
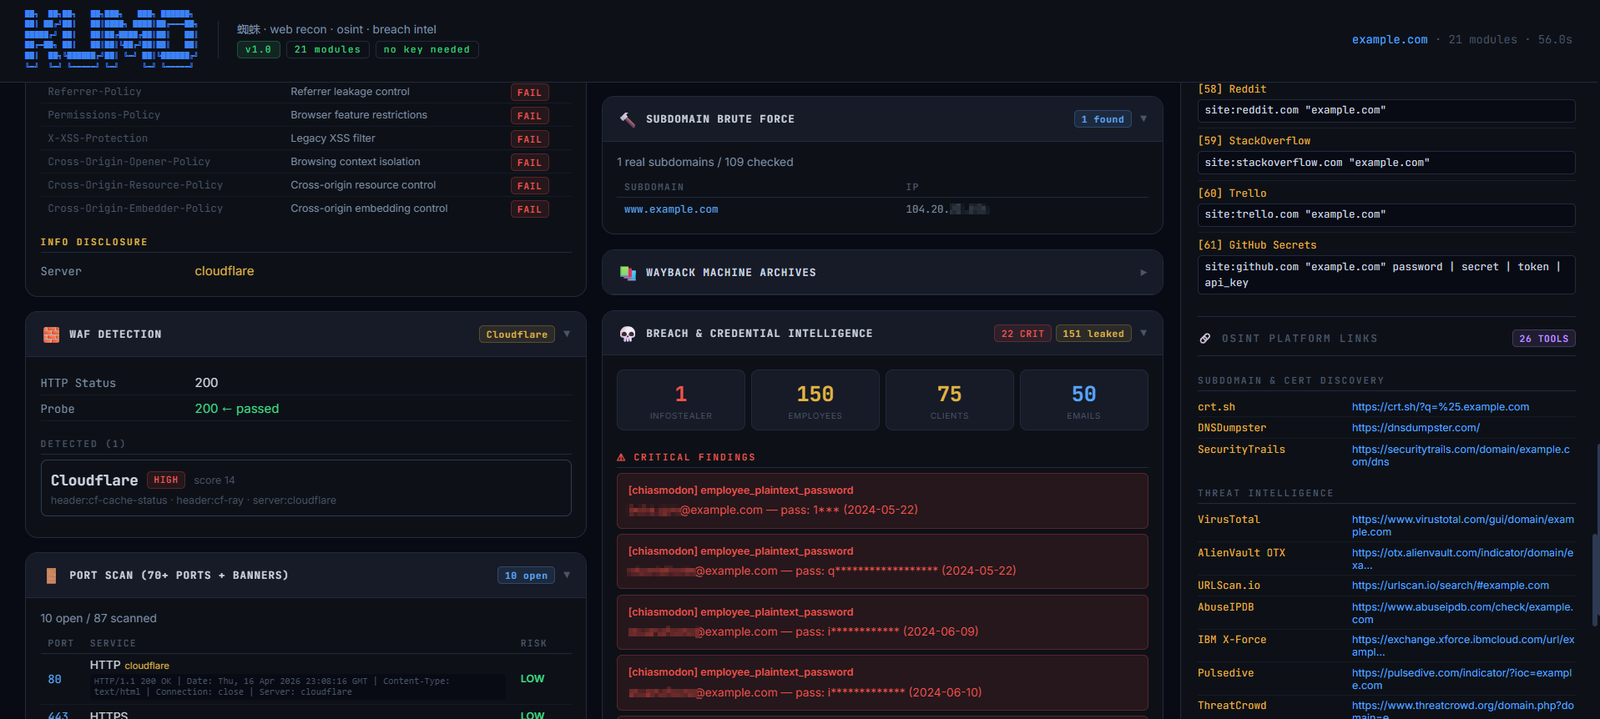
KUMO-Domain-Recon-Tool
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
dns-analysisinformation-gatheringosint+8
48
karim852/kumo-domain-recon-toolDomain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 trickest/resolvers
The most exhaustive list of reliable DNS resolvers.
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
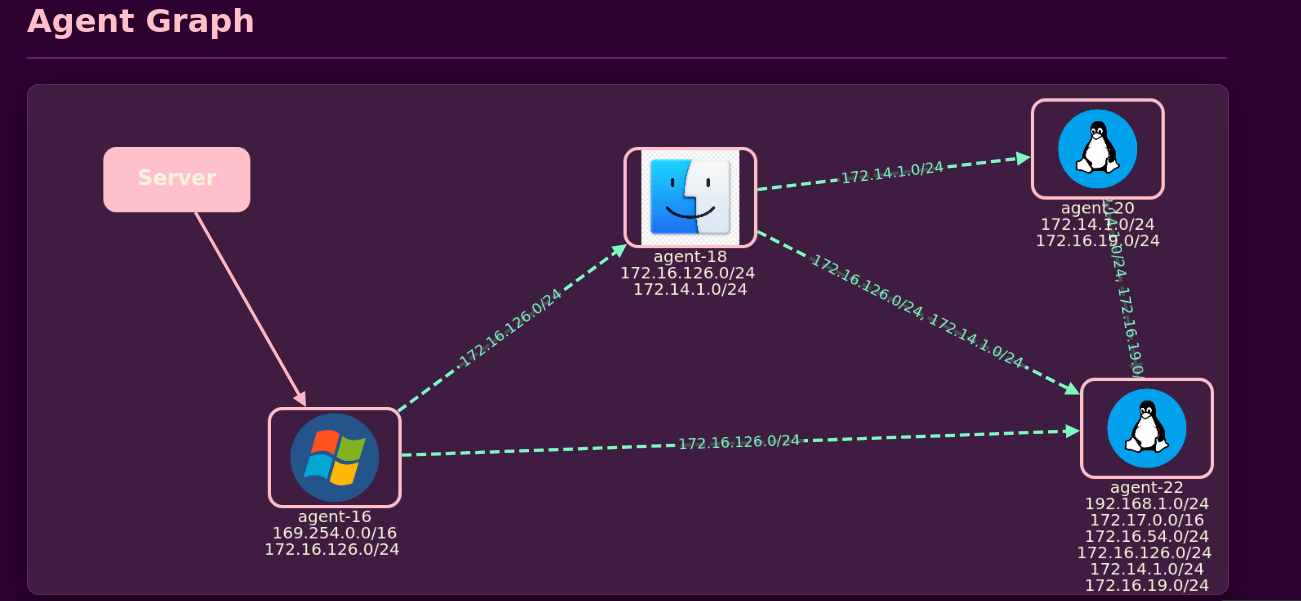 blue0x1/rosemary
Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
 1n3/powerexfil
A collection of data exfiltration scripts for Red Team assessments.
 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 cyber-note/cve-2026-34835-black-box-analysis
A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…
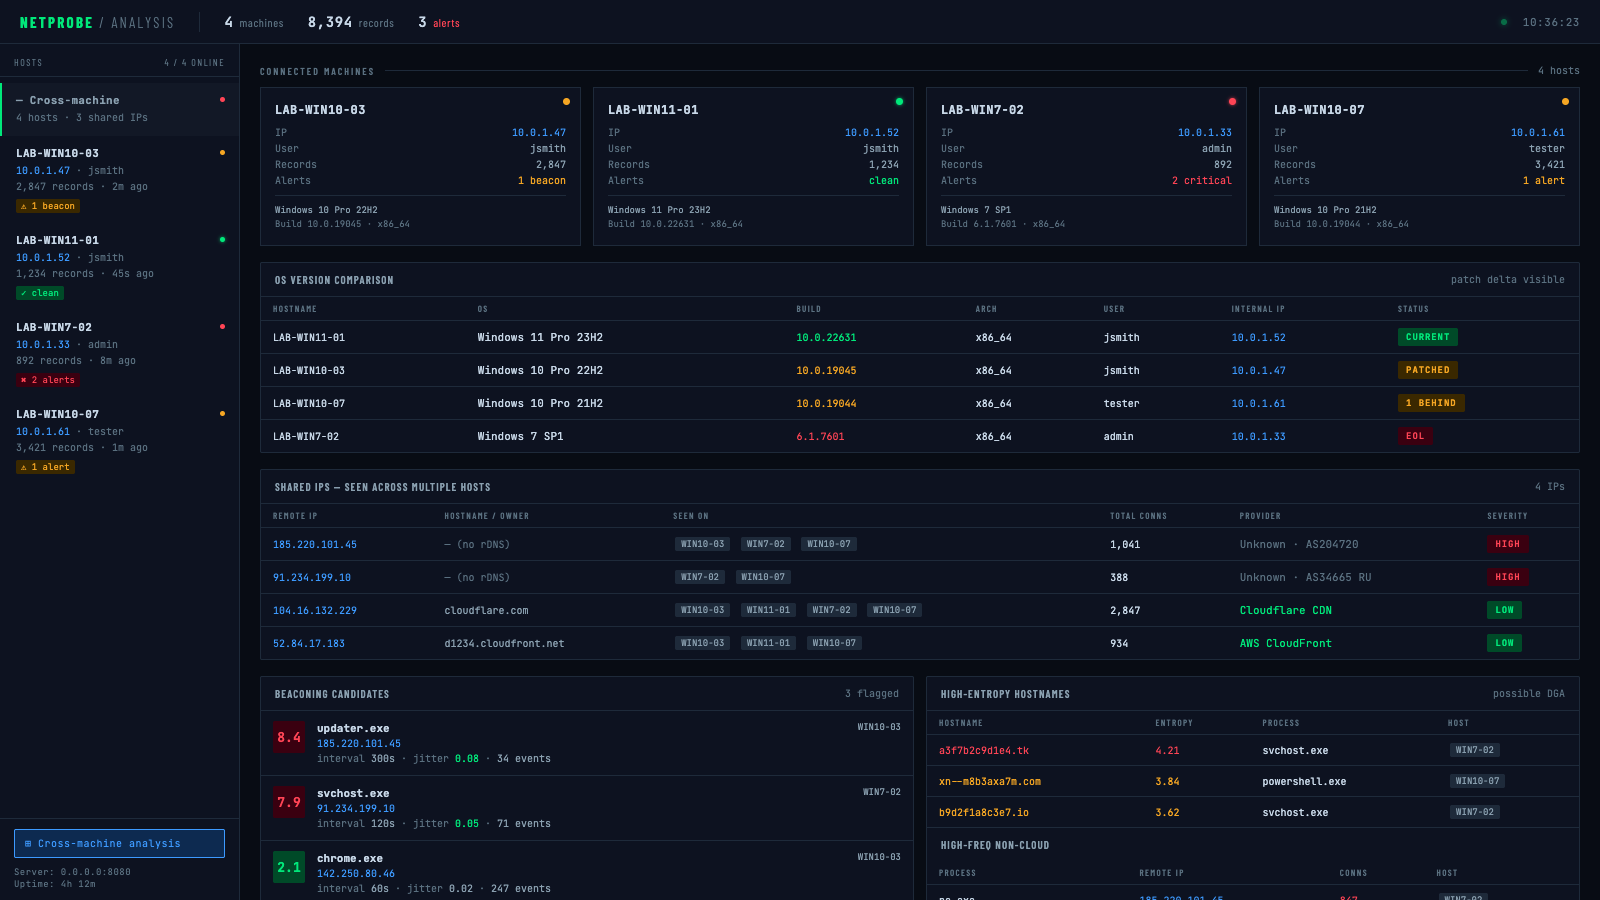
 hackinglz/gibson
Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity
 brannondorsey/dns-rebind-toolkit
A front-end JavaScript toolkit for creating DNS rebinding attacks.
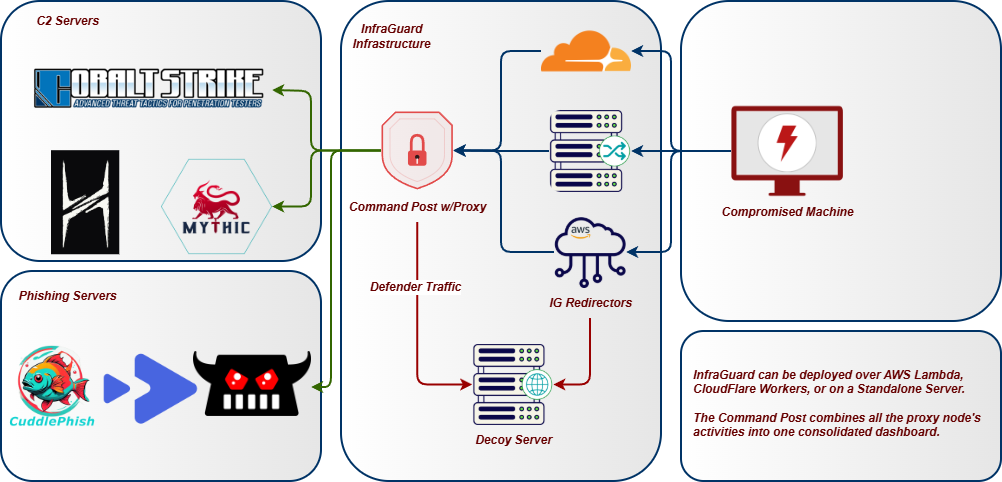 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
 wddadk/offensive-osint-tools
Curated list of OSINT tools for offensive security, covering email harvesting, subdomain enumeration, threat intelligence, and social engineering for…
 ginjachris/pentmenu
A bash script for recon and DOS attacks
 brannondorsey/whonow
A "malicious" DNS server for executing DNS Rebinding attacks on the fly (public instance running on rebind.network:53)
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
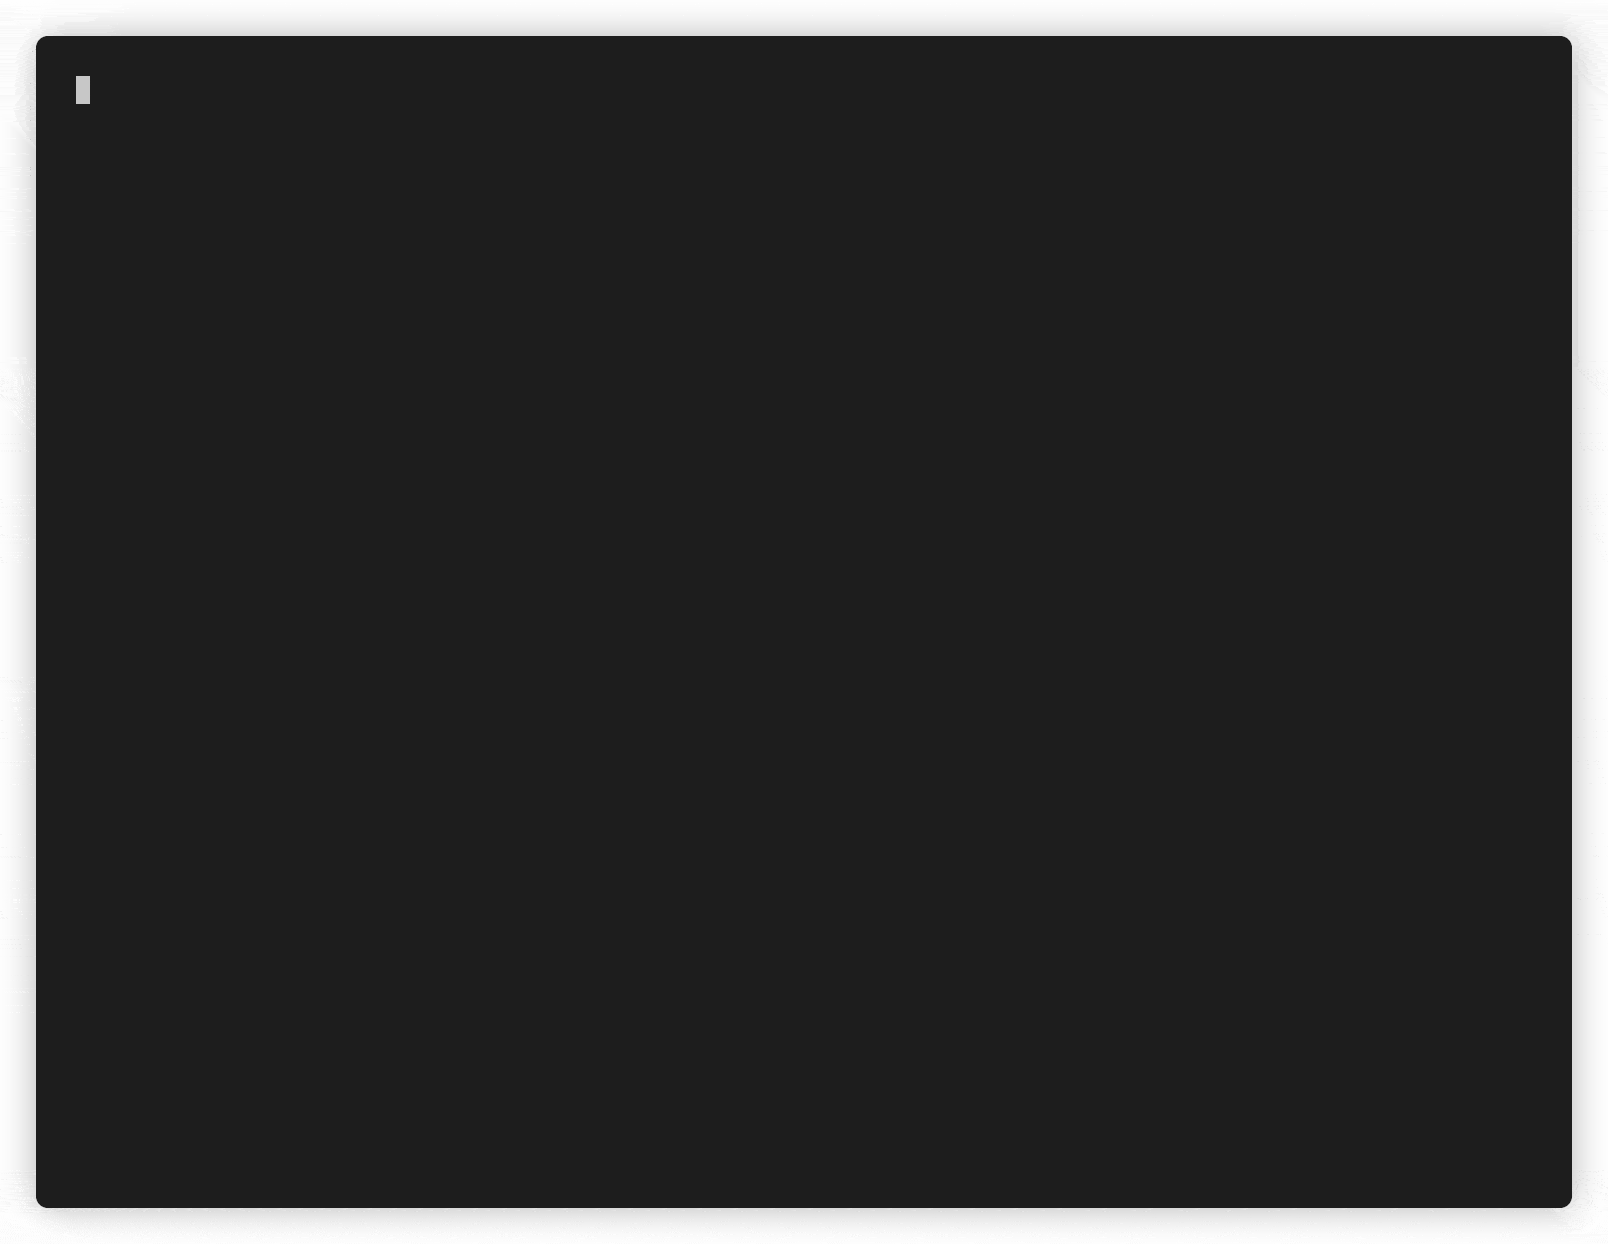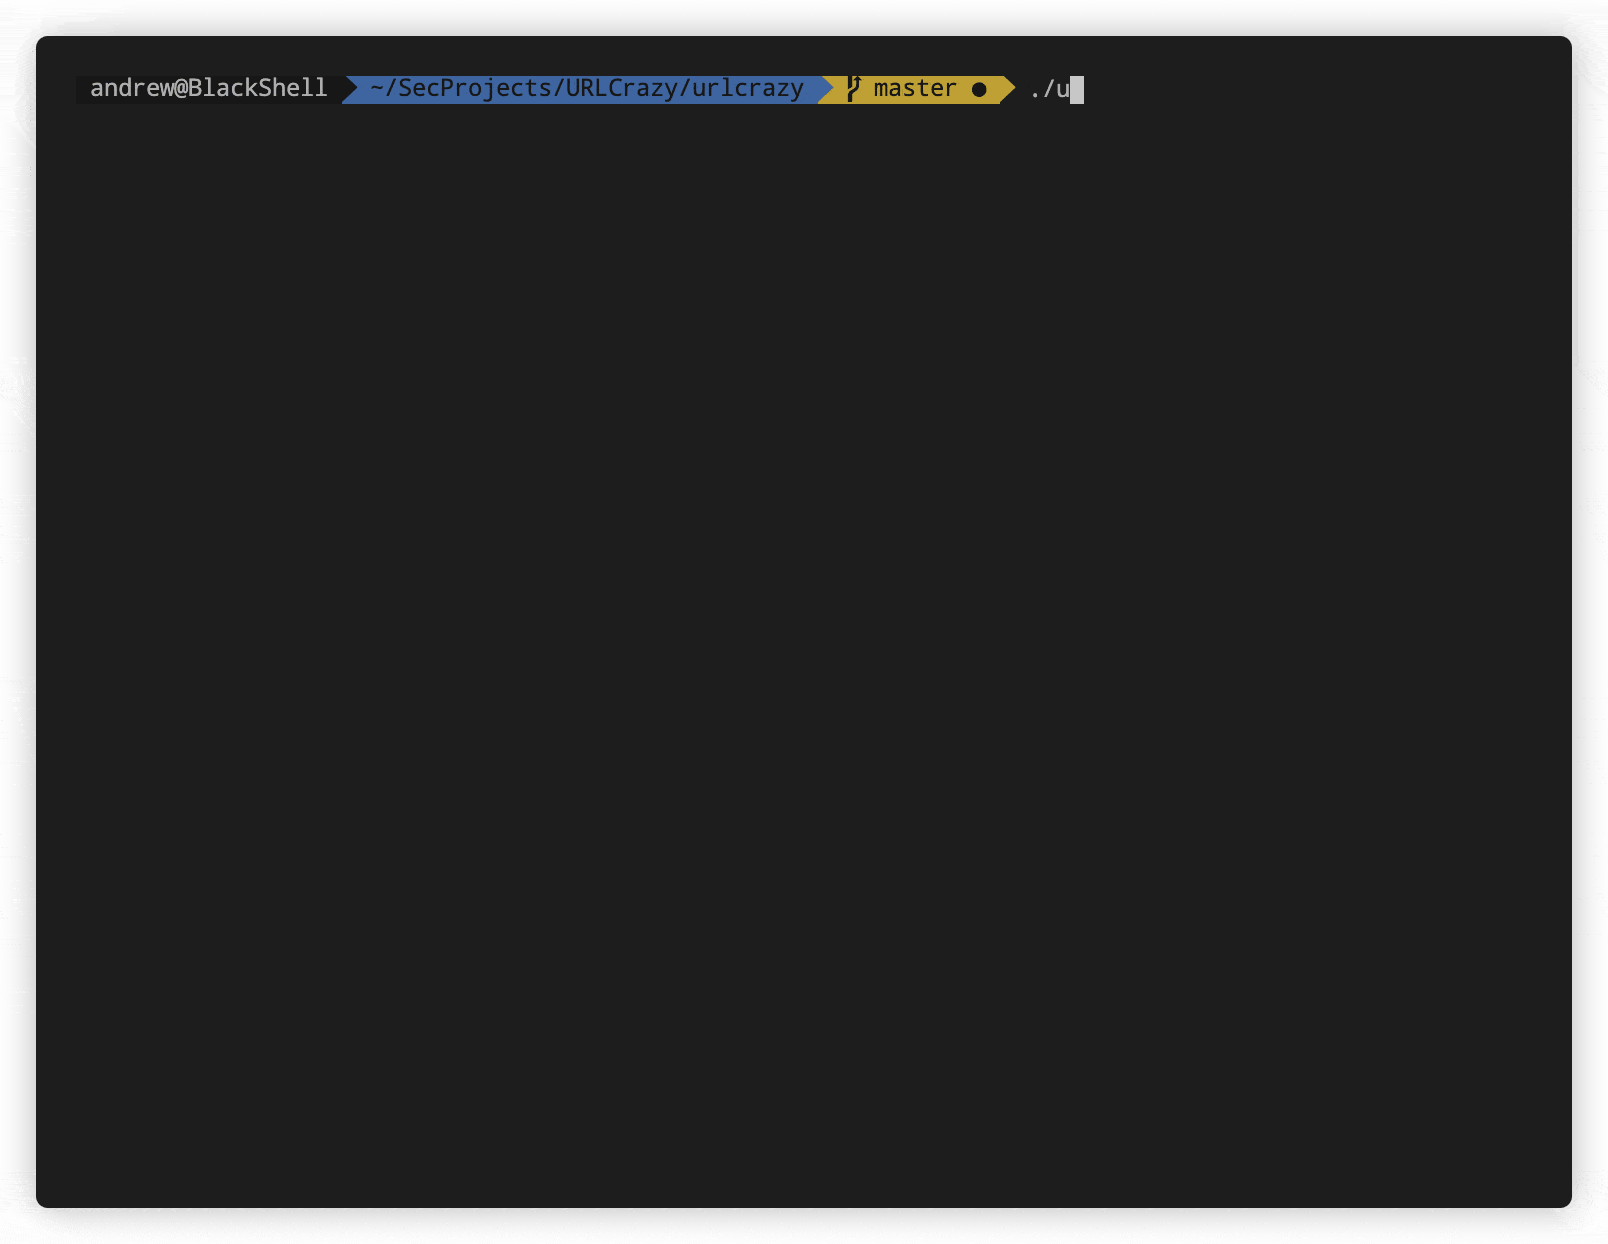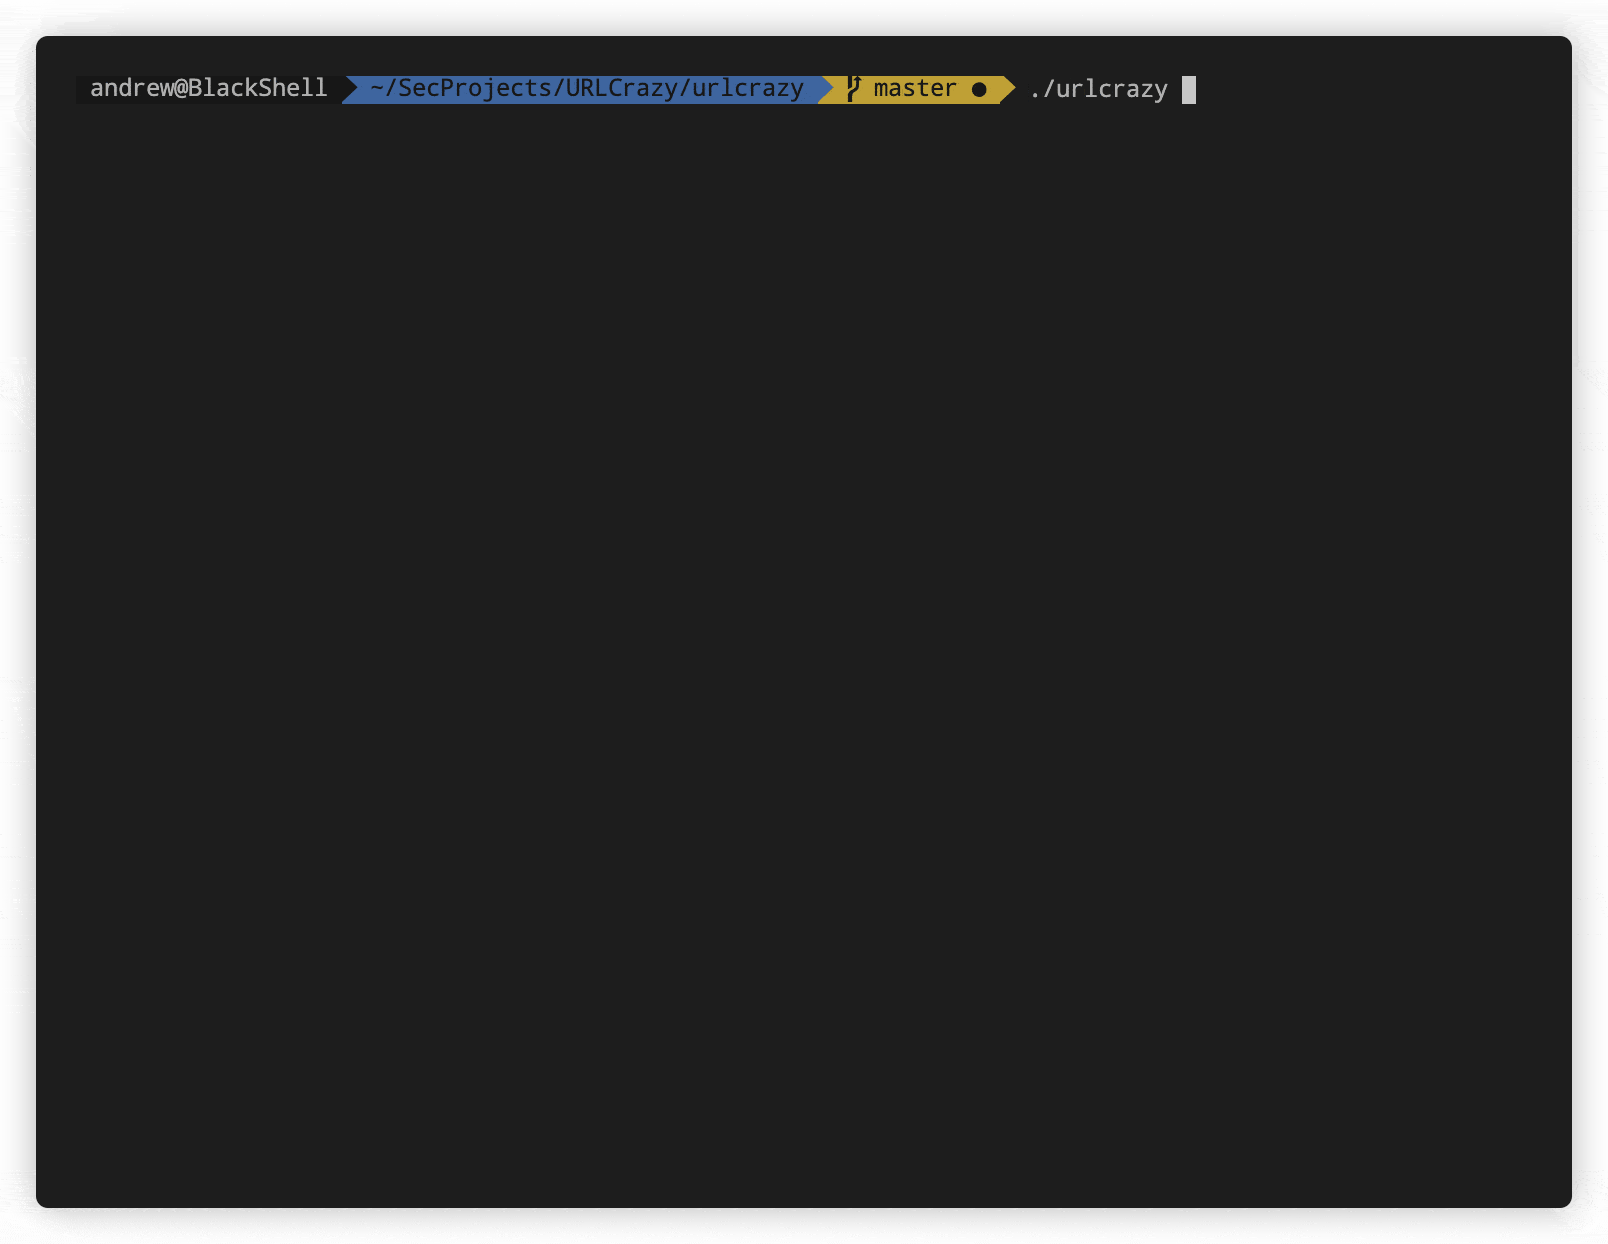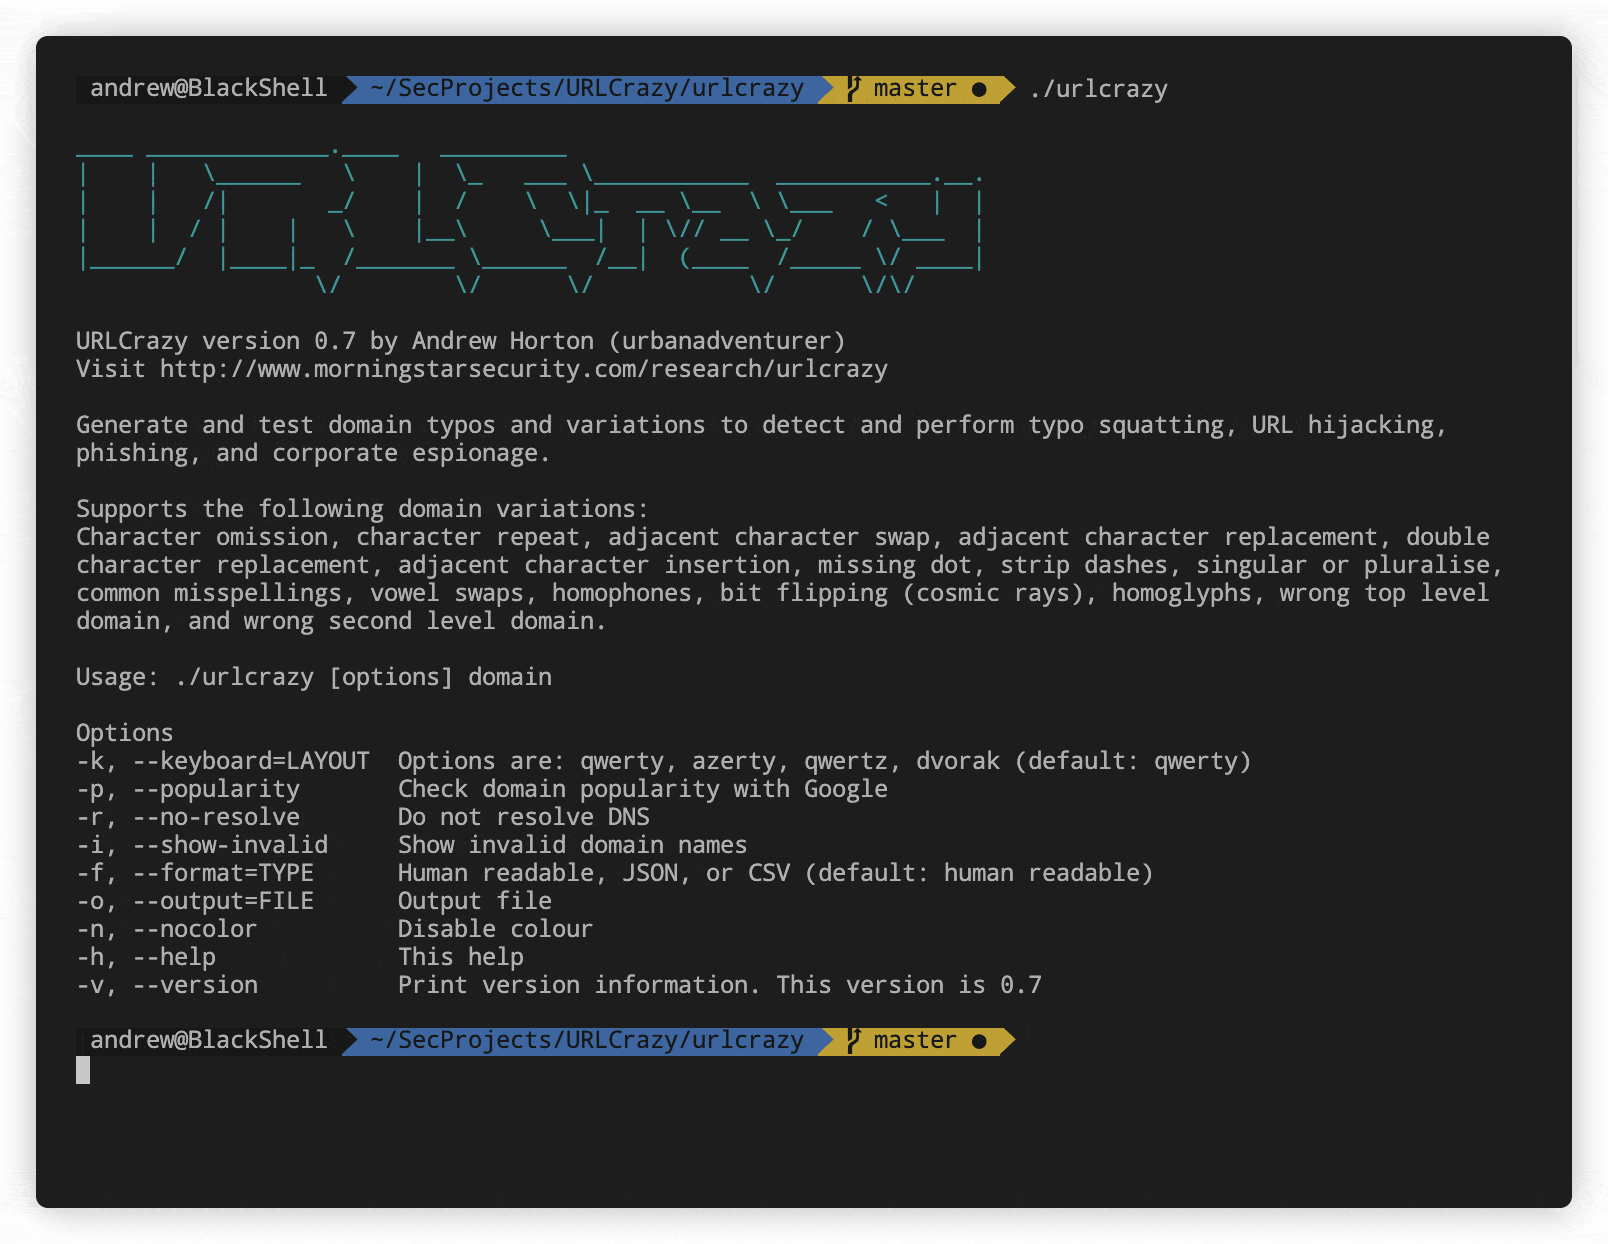 urbanadventurer/urlcrazy
Generate and test domain typos and variations to detect and perform typo squatting, URL hijacking, phishing, and corporate espionage.
 tasooshi/exfilkit
Data exfiltration utility for testing detection capabilities
 redteampentesting/pretender
Your MitM sidekick for relaying attacks featuring DHCPv6 DNS takeover as well as mDNS, LLMNR and NetBIOS-NS spoofing.