

spiderfoot
 smicallef/spiderfoot
Automates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
dns-analysisemail-harvestinginformation-gathering+9
24.1k
smicallef/spiderfootAutomates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 shmilylty/oneforall
Multi-source subdomain enumeration tool with 50+ collection modules, DNS brute-force, passive DNS analysis, certificate transparency, search engine…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 1n3/powerexfil
A collection of data exfiltration scripts for Red Team assessments.
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 escape-technologies/awesome-attack-surface-management
A curated collection of tools, techniques, frameworks, and learning resources focused on Attack Surface Management (ASM).
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 takeshixx/ip-https-tools
Tools for the IP over HTTPS (IP-HTTPS) Tunneling Protocol
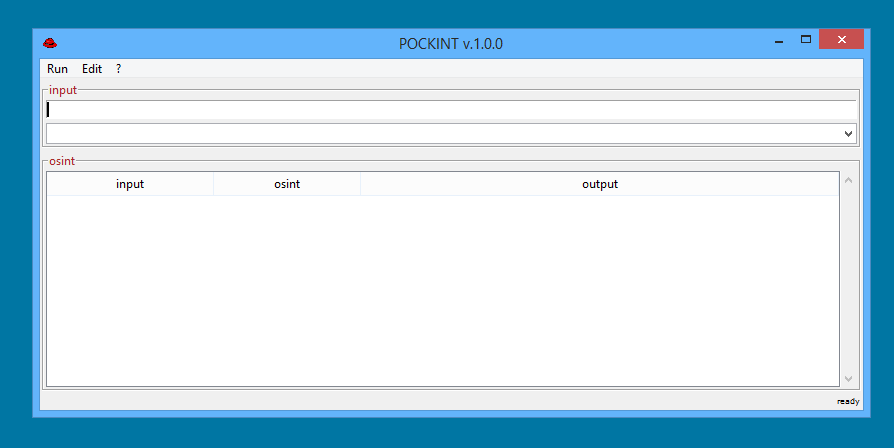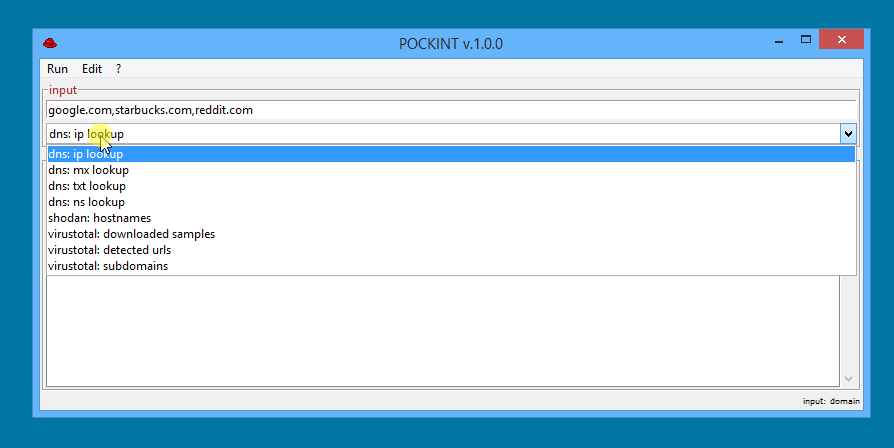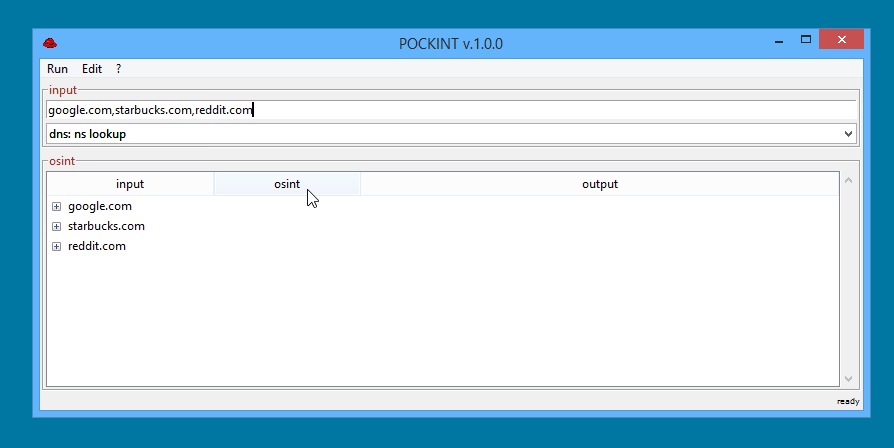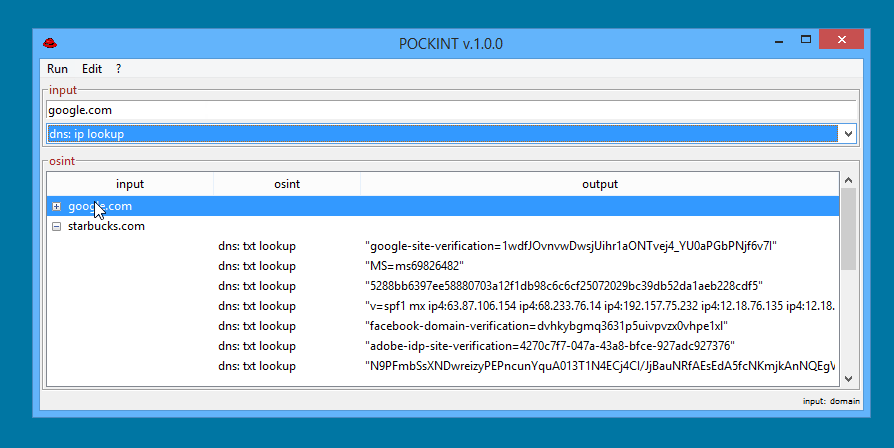 edoardogerosa/pockint
A portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️
 fevar54/cve-2026-33634-scanner
Scanner de IOCs del ataque de cadena de suministro TeamPCP (CVE-2026-33634).
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit