

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
43 results
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

digital-forensicsdisk-forensicsforensics+4
5.1k5 days ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

debuggersdigital-forensicsdisk-forensics+7
252 months ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.0k7h 34m ago
OSXAuditor preview

OSXAuditor

GitHubjipegit/osxauditor

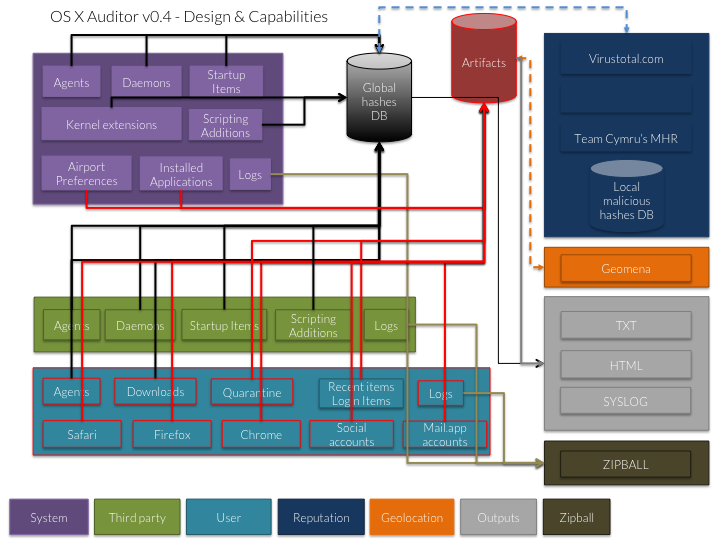
OS X Auditor is a free Mac OS X computer forensics tool

digital-forensicsdisk-forensicsforensics+4
3.1k6 years ago
bulk_extractor preview

bulk_extractor

GitHubsimsong/bulk_extractor

This is the development tree. Production downloads are at:

data-recoverydigital-forensicsdisk-forensics+9
1.4k1 month ago
dissect preview

dissect

GitHubfox-it/dissect

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…


data-recoverydigital-forensicsdisk-forensics+5
1.2k7 months ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.3k10h 18m ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k19h 15m ago
cyberchef-recipes preview

cyberchef-recipes

GitHubmattnotmax/cyberchef-recipes

A list of cyber-chef recipes and curated links

curated-resourcesdigital-forensicsdisk-forensics+8
2.2k2 years ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k1 day ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
ctfdigital-forensicsdisk-forensics+6
60016 days ago
sift preview

sift

GitHubteamdfir/sift

SIFT

cloud-securitydigital-forensicsdisk-forensics+3
5502 years ago
forensictools preview

forensictools

GitHubcristianzsh/forensictools

Collection of forensic tools

binary-analysisdata-recoverydigital-forensics+7
7051 month ago
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

digital-forensicsdisk-forensicsforensics+6
4885 years ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

digital-forensicsdisk-forensicsforensics+3
5215 years ago
Skadi preview

Skadi

GitHuborlikoski/skadi

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
curated-resourcesdigital-forensicsdisk-forensics+9
5203 years ago
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

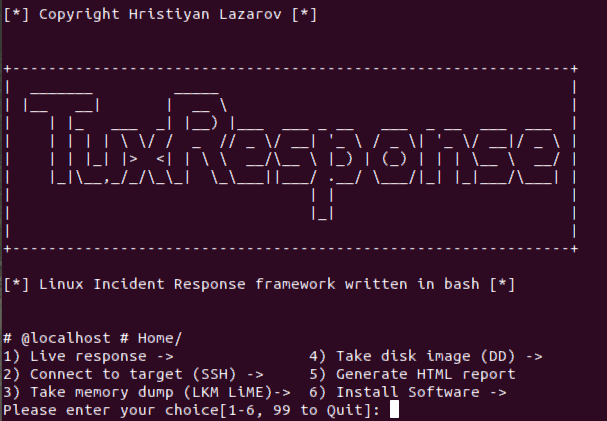
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
digital-forensicsdisk-forensicsforensics+5
915 months ago
ATMMalScan preview

ATMMalScan

GitHubfboldewin/atmmalscan

Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…

digital-forensicsdisk-forensicsincident-response+2
575 years ago
Previous123Next
