
RecoverPy
 pablolec/recoverpy
Interactively find and recover deleted or :point_right: overwritten :point_left: files from your terminal
data-recoverydigital-forensicsdisk-forensics+1
1.8k
pablolec/recoverpyInteractively find and recover deleted or :point_right: overwritten :point_left: files from your terminal
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
 libyal/libewf
C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
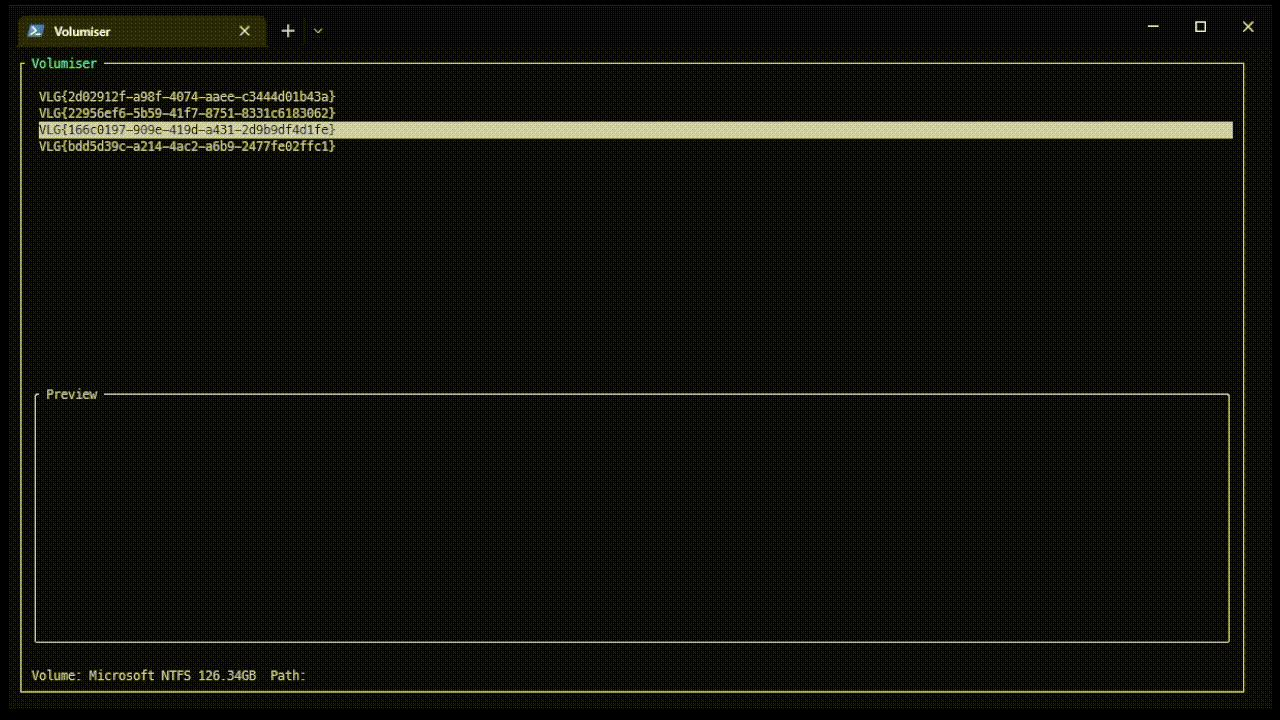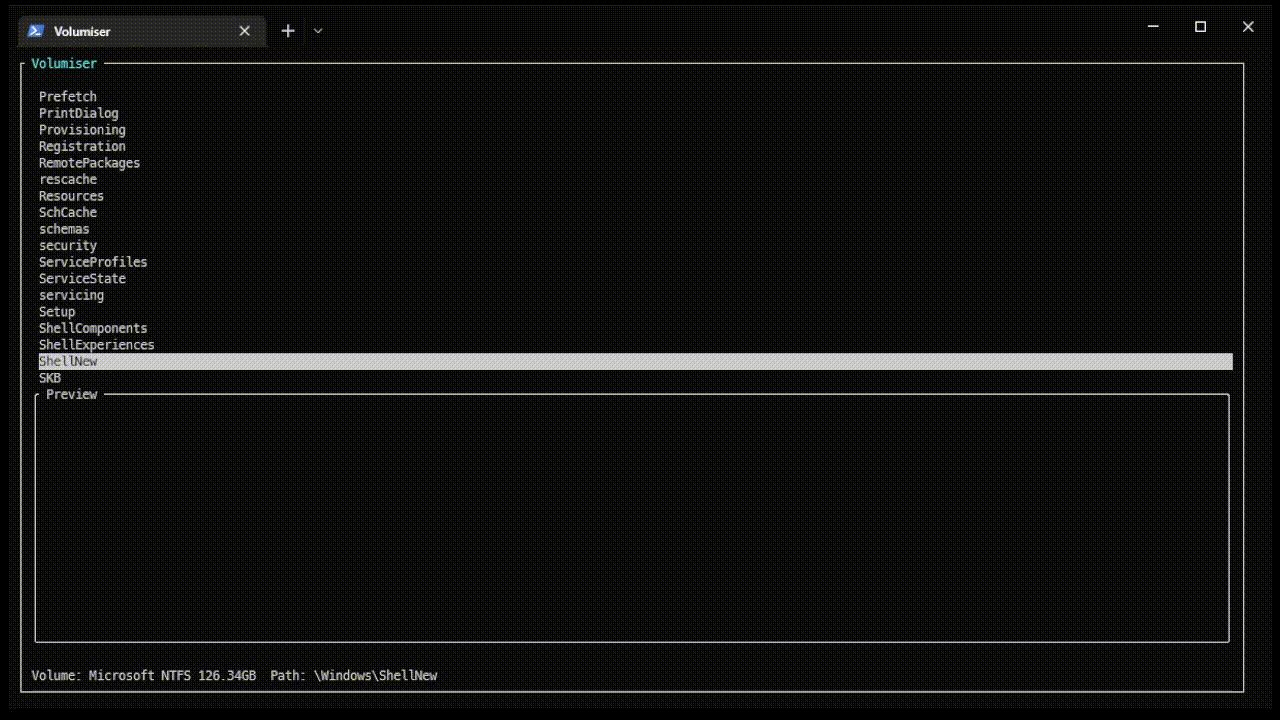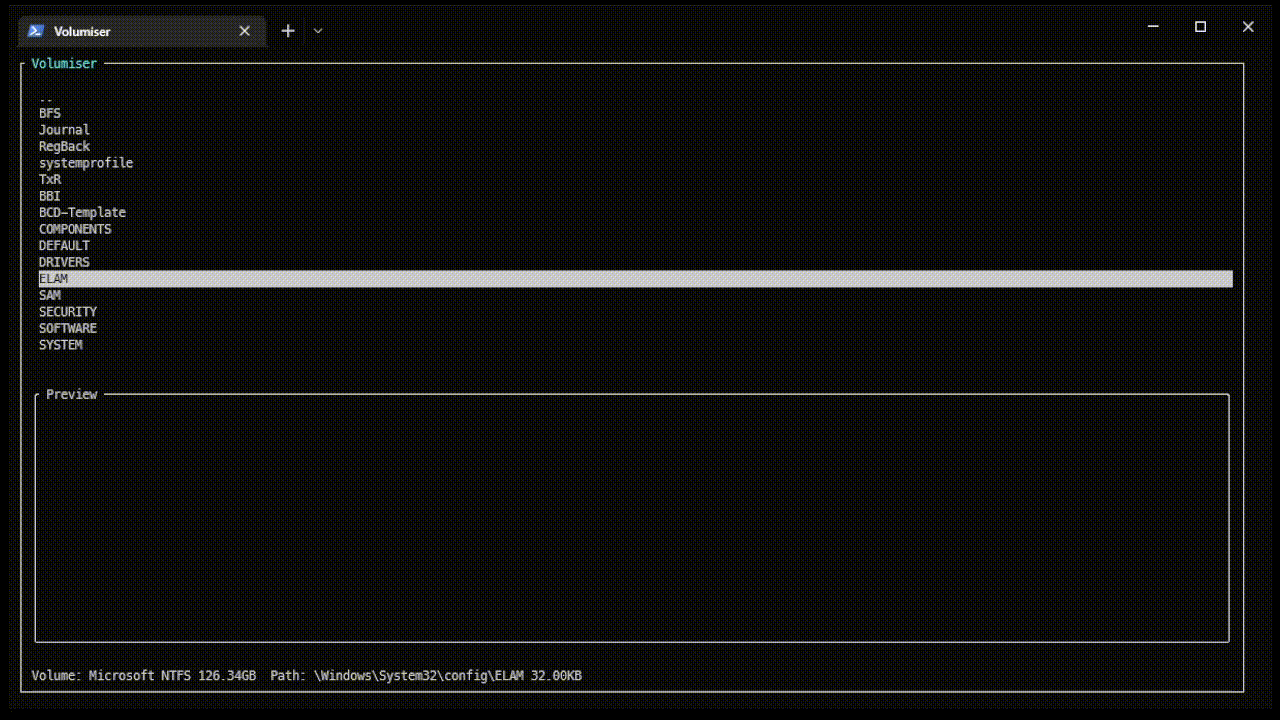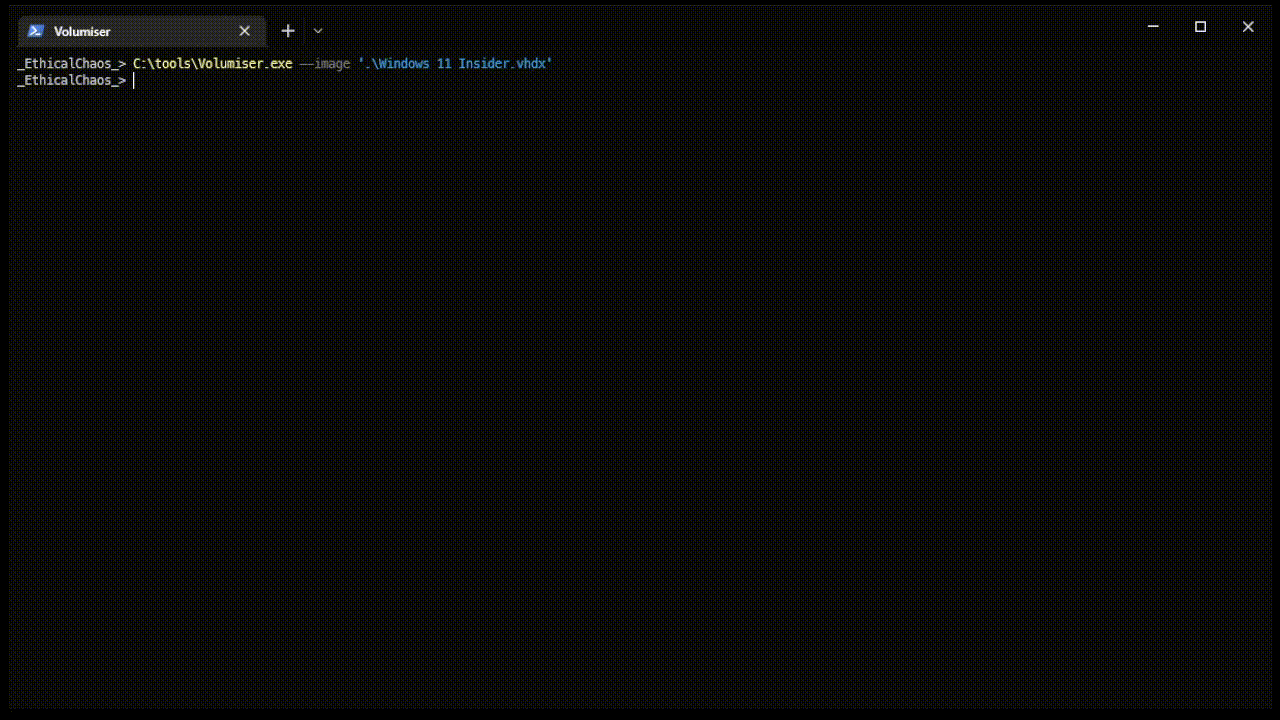 ccob/volumiser
CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 cherojeong/extundelete
Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 ericzimmerman/kapefiles
This repository serves as a place for community created Targets and Modules for use with KAPE.
 lazza/recuperabit
A tool for forensic file system reconstruction.
 jschicht/rawcopy
Commandline low level file extractor for NTFS