

Loki
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k
neo23x0/lokiIOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
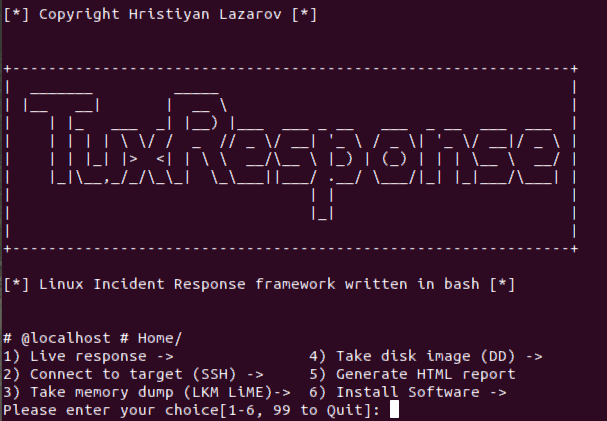 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 cgsecurity/testdisk
Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
 ericzimmerman/kapefiles
This repository serves as a place for community created Targets and Modules for use with KAPE.
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 lazza/recuperabit
A tool for forensic file system reconstruction.
 libyal/libewf
C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…