Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

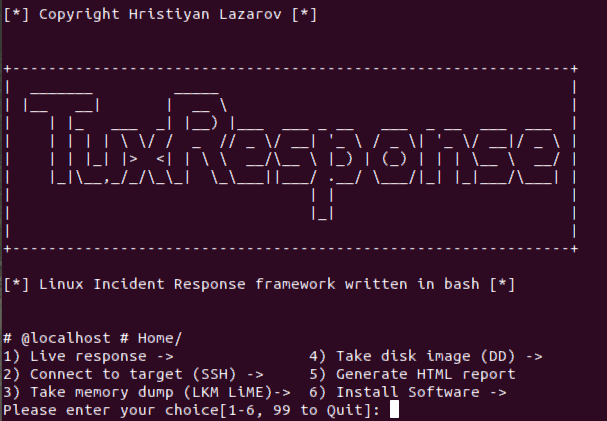
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

Digital Forensics Intelligence Framework

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…

Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.

This repository serves as a place for community created Targets and Modules for use with KAPE.

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…

C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…

Forensics tool for NTFS (parser, mft, bitlocker, deleted files)

A tool for forensic file system reconstruction.

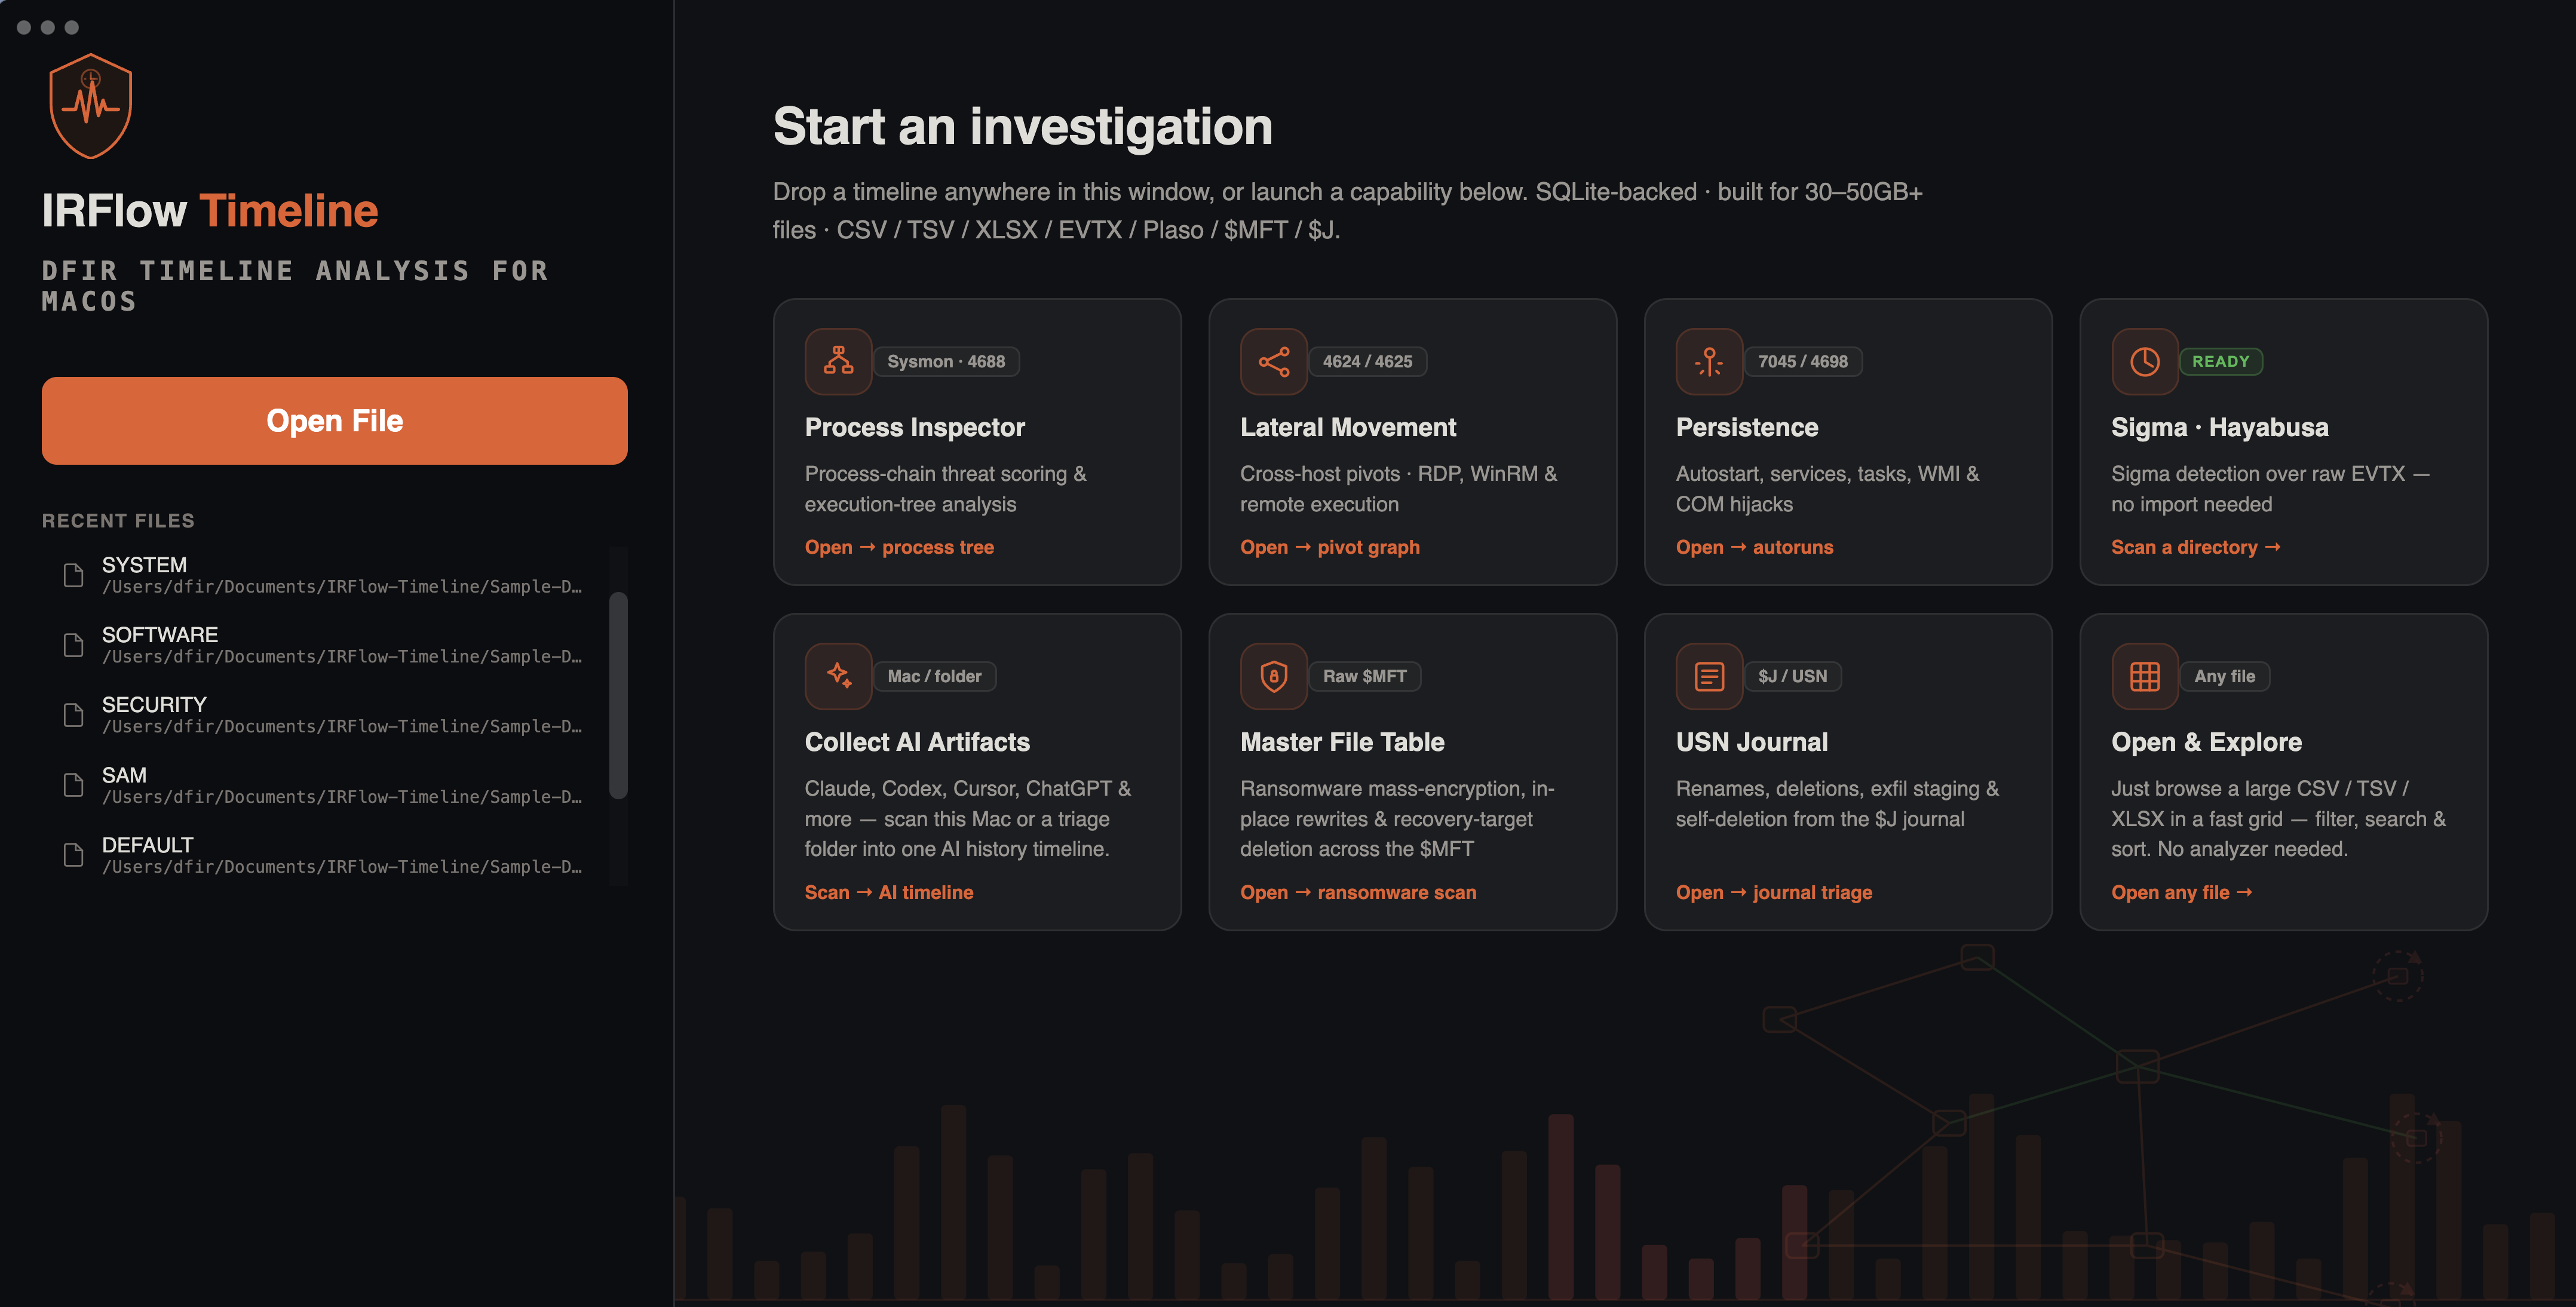
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

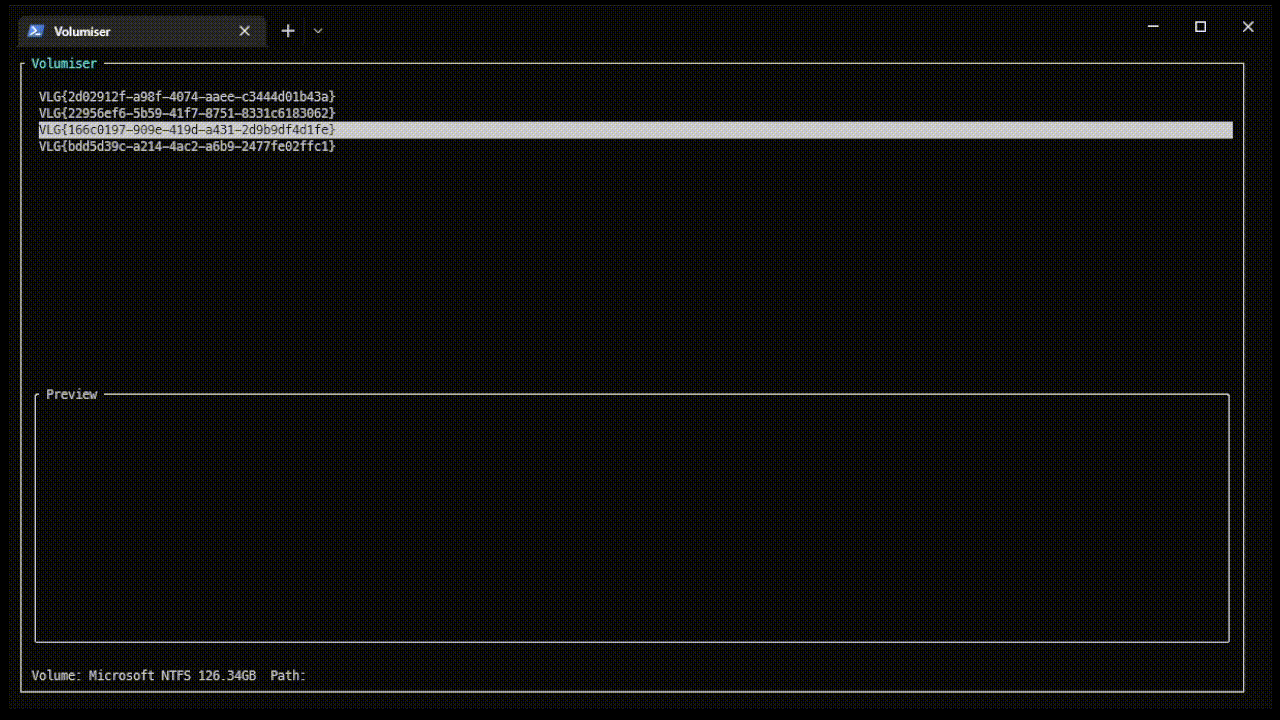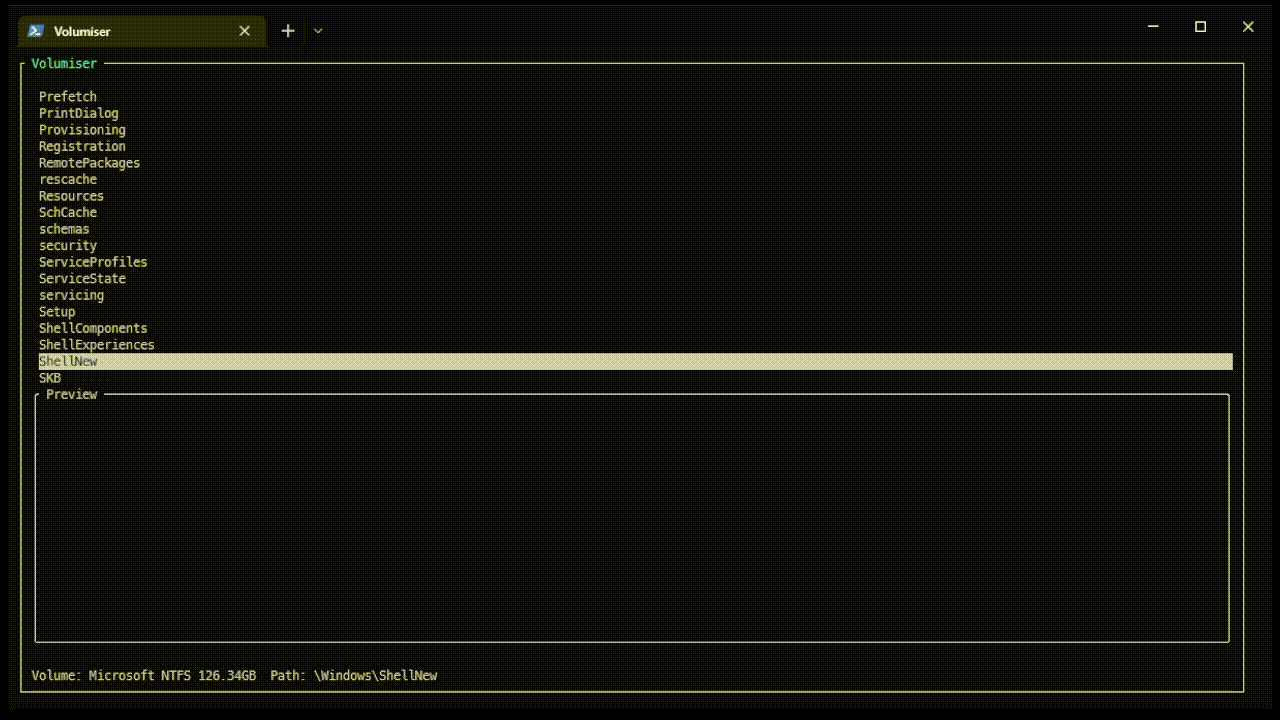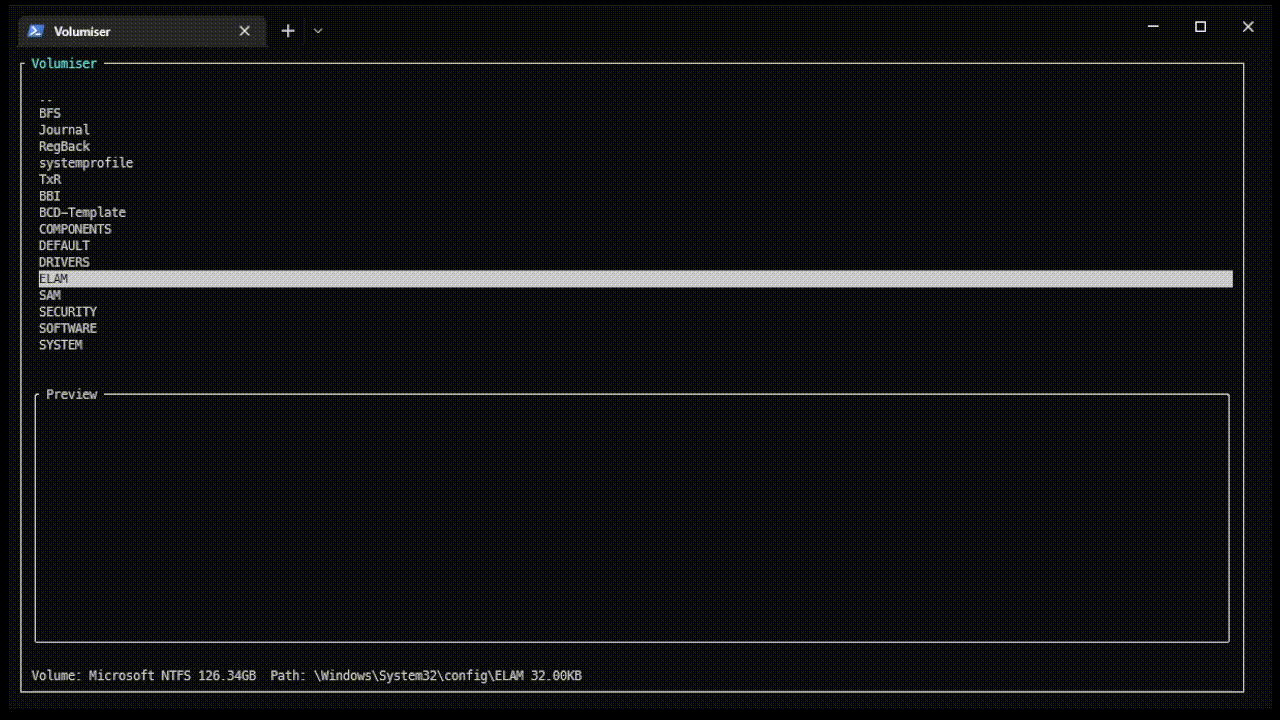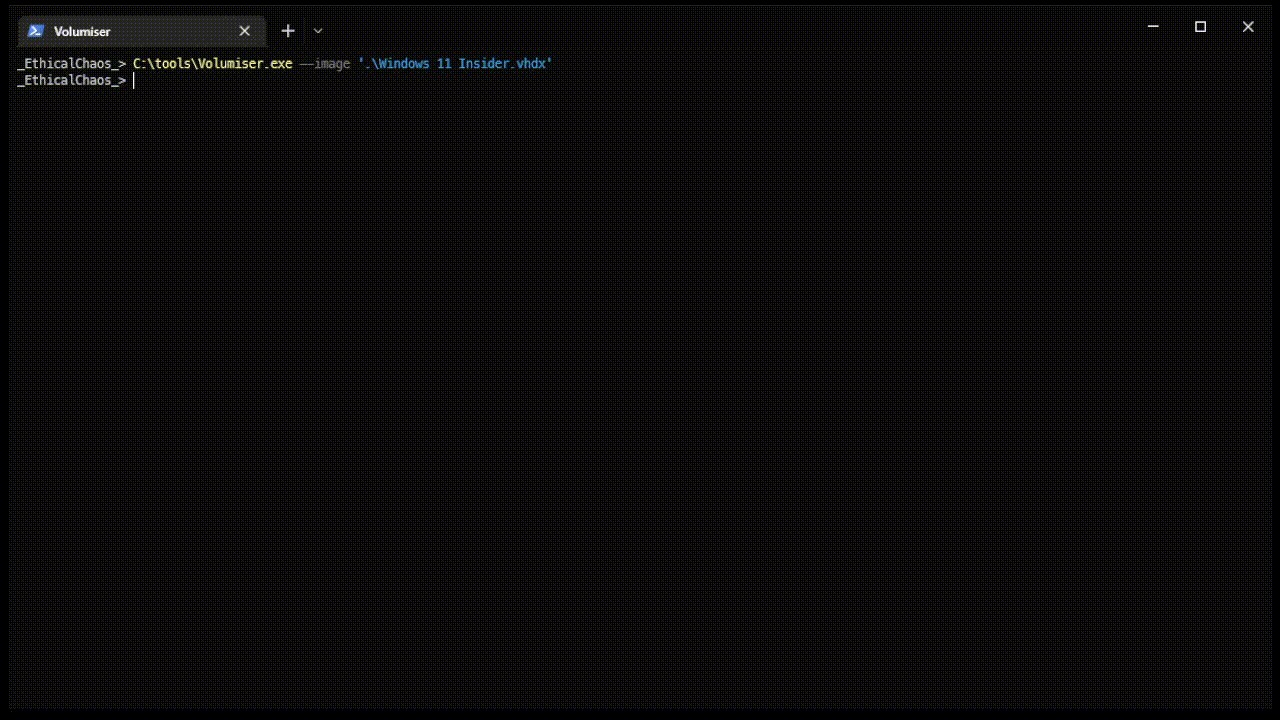
CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…