
tscopy
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
data-recoverydigital-forensicsdisk-forensics+2
103
trustedsec/tscopyPython tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
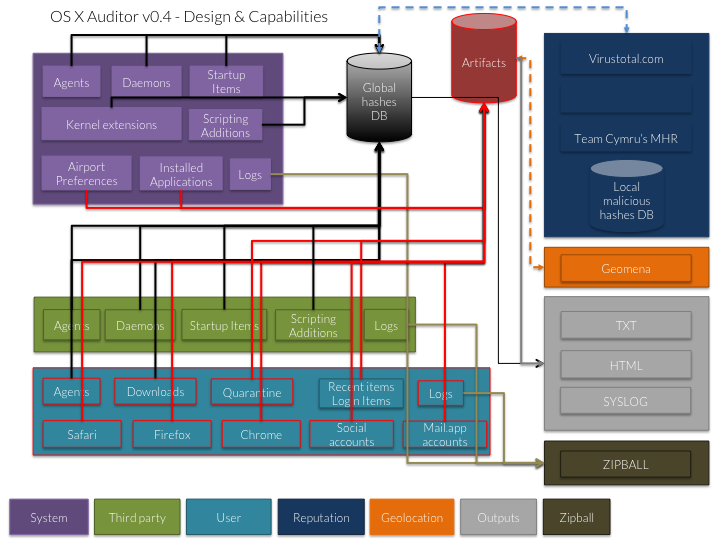 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
 dmtrkovalenko/ffs
F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
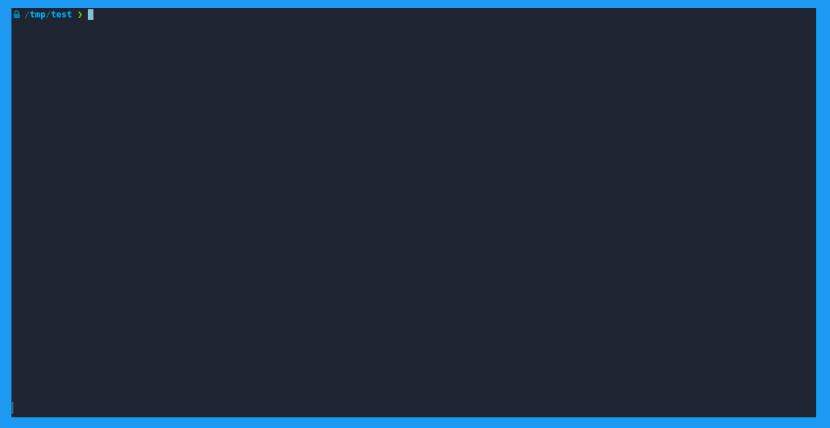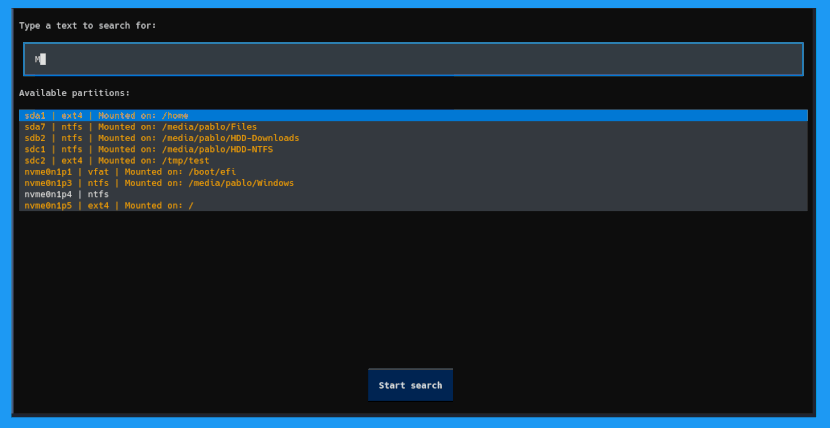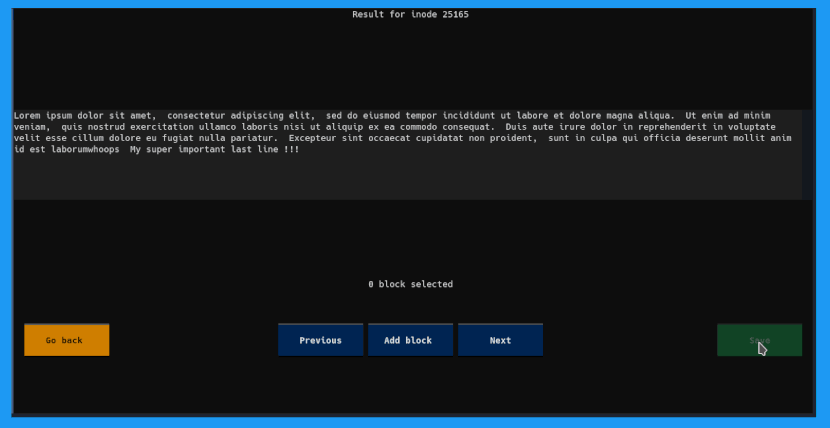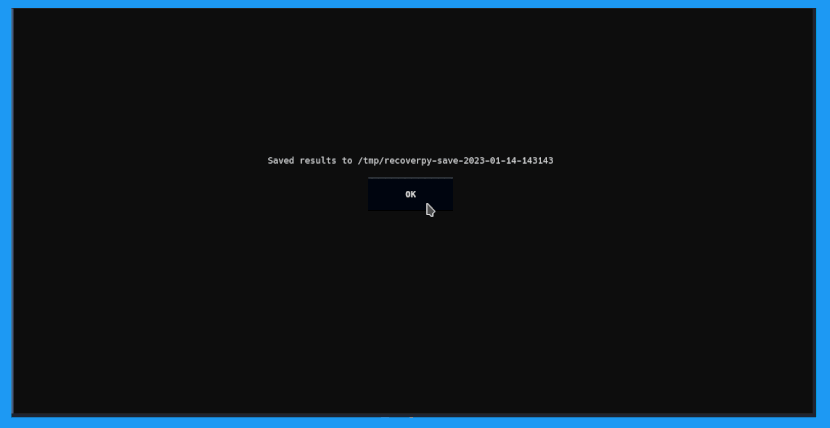 pablolec/recoverpy
Interactively find and recover deleted or :point_right: overwritten :point_left: files from your terminal
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 lazza/recuperabit
A tool for forensic file system reconstruction.
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 jschicht/extractusnjrnl
Tool to extract the $UsnJrnl from an NTFS volume
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.