

DFIR-LABS
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
ctfdigital-forensicsdisk-forensics+6
azr43lkn1ght/dfir-labsHands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
 libyal/libfsntfs
Library and tools to access the Windows New Technology File System (NTFS)
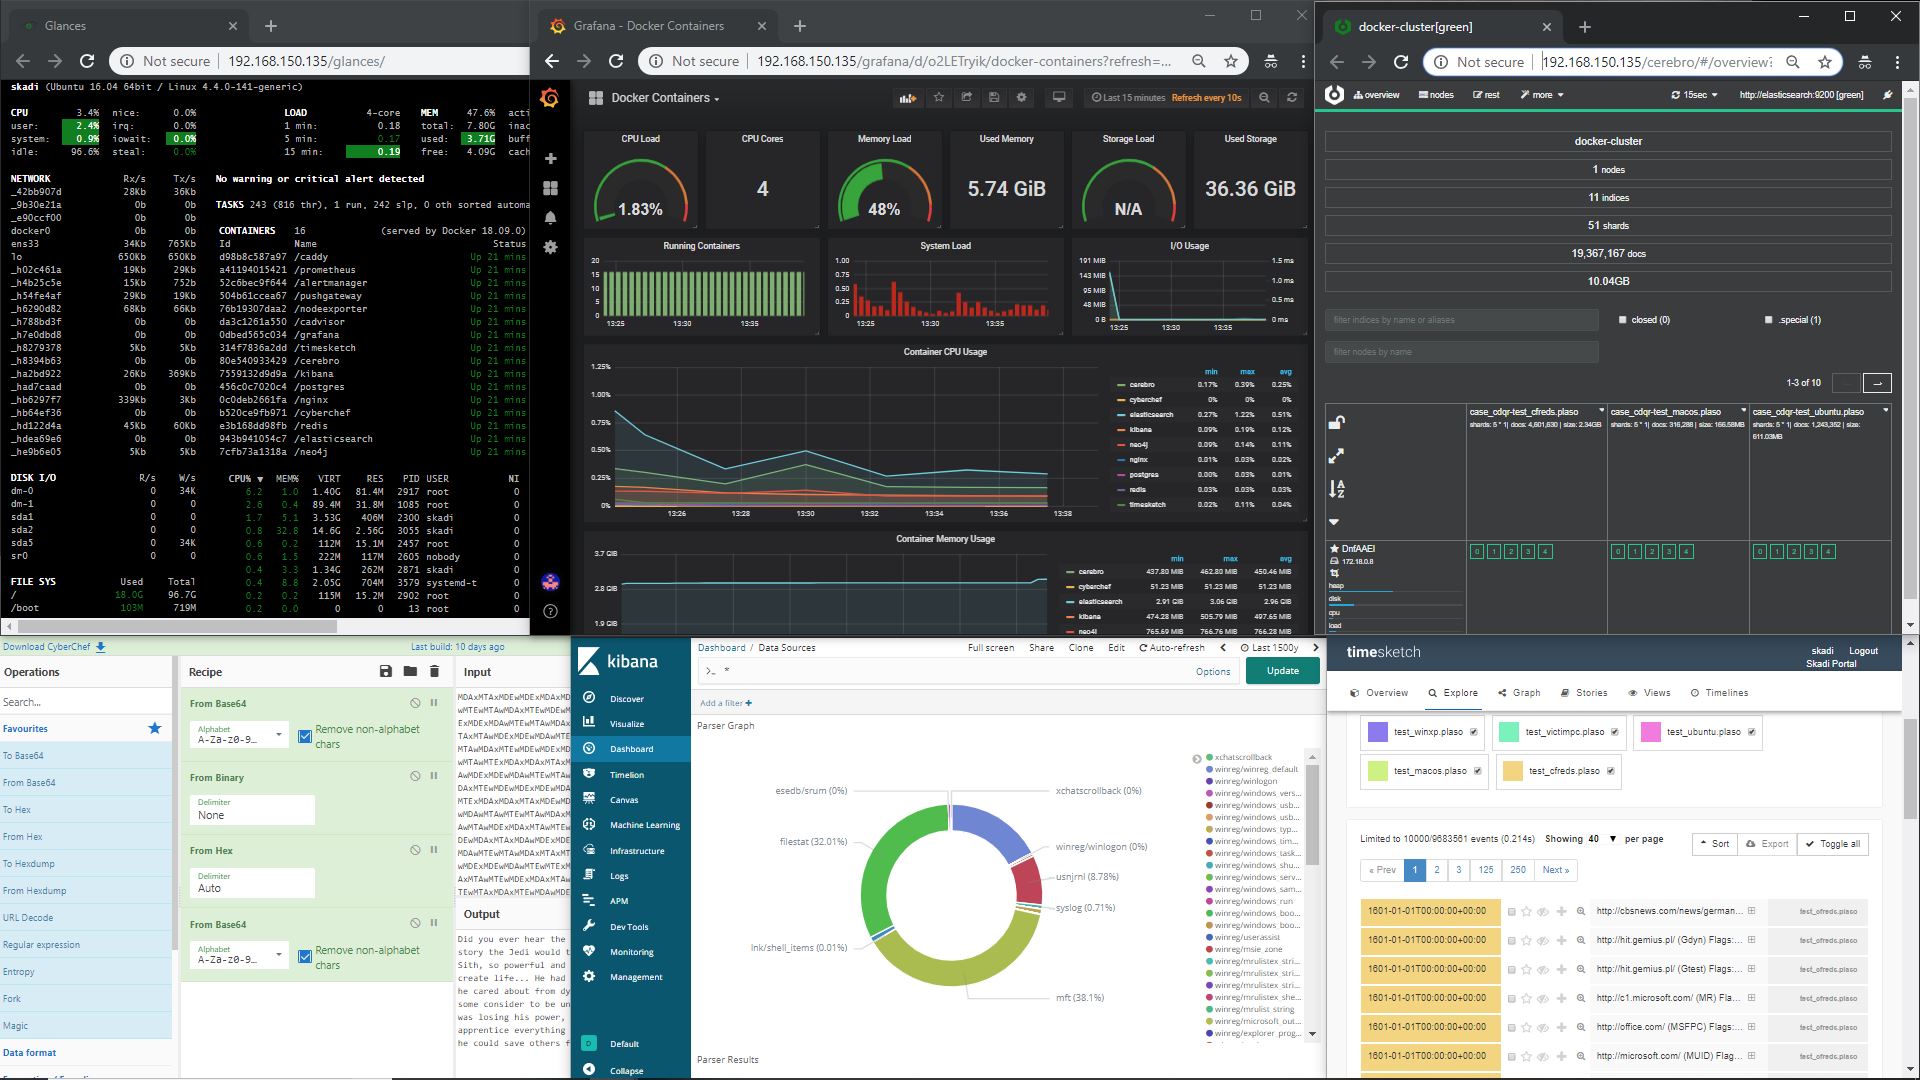 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 libyal/libvmdk
Library and tools to access the VMware Virtual Disk (VMDK) format
 libyal/libvhdi
Library and tools to access the Virtual Hard Disk (VHD) image format
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
 jschicht/extractusnjrnl
Tool to extract the $UsnJrnl from an NTFS volume
 libyal/libqcow
Library and tools to access the QEMU Copy-On-Write (QCOW) image format

 4n6ist/usn_analytics
It's not just UsnJrnl (USN Journal Records/Change Journal Records) parser.
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 gnu-mirror-unofficial/ddrescue
Copies data from damaged or failing storage devices, handles read errors, and performs efficient rescue operations to recover as much data as…