
Archived
dfir-toolkit
 dfir-dd/dfir-toolkit
CLI tools for forensic investigation of Windows artifacts
digital-forensicsdisk-forensicsforensics+2
dfir-dd/dfir-toolkitCLI tools for forensic investigation of Windows artifacts
 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X

 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
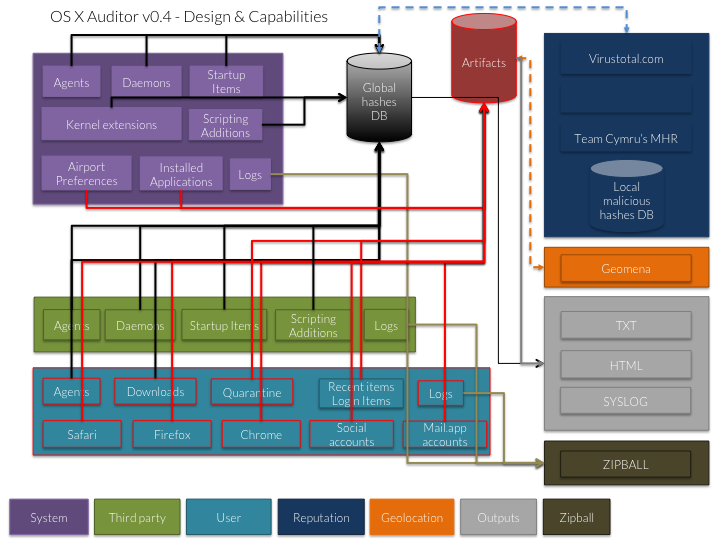 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 cristianzsh/forensictools
Collection of forensic tools
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
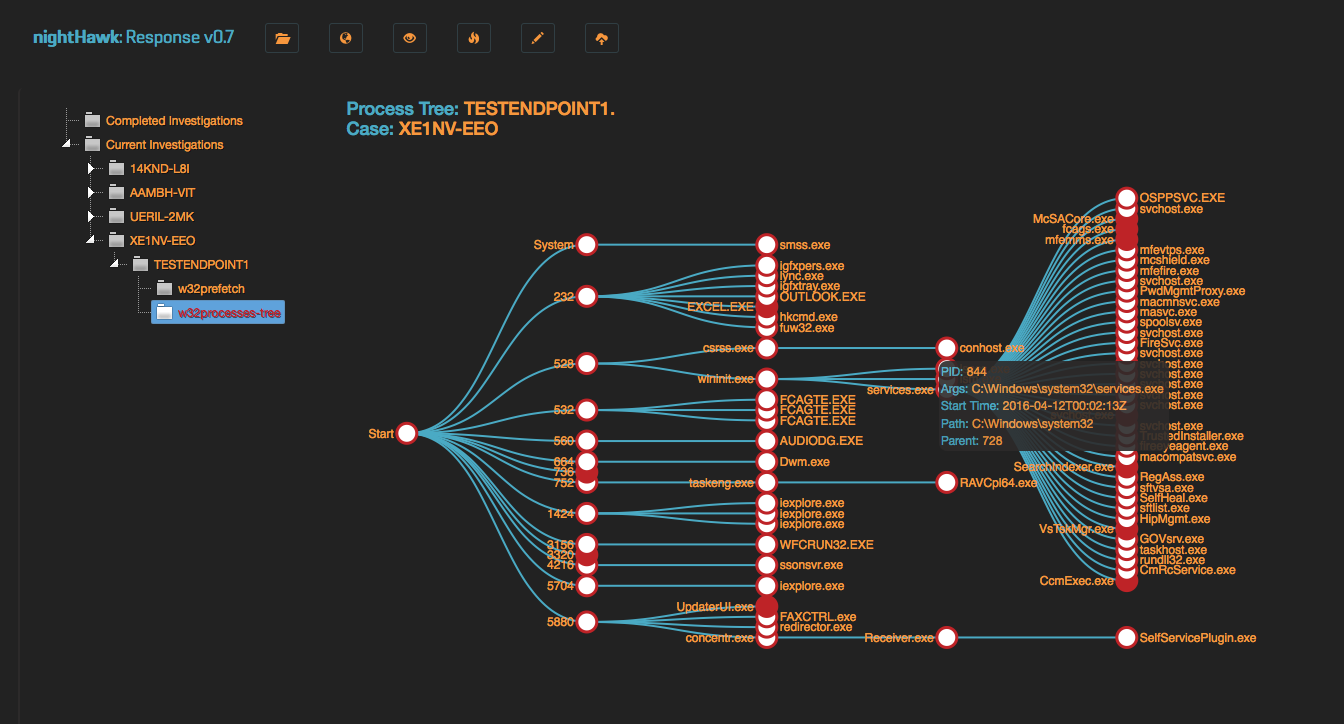 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.

 jschicht/rawcopy
Commandline low level file extractor for NTFS
 jschicht/extractusnjrnl
Tool to extract the $UsnJrnl from an NTFS volume

 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 4n6ist/usn_analytics
It's not just UsnJrnl (USN Journal Records/Change Journal Records) parser.
 synacktiv/veeam-velociraptor
Proof-of-concept Velociraptor artifacts pack to showcase a remote Veeam forensics pipeline.