
DFIR-LABS
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
ctfdigital-forensicsdisk-forensics+6
671
azr43lkn1ght/dfir-labsHands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 libyal/libewf
C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…

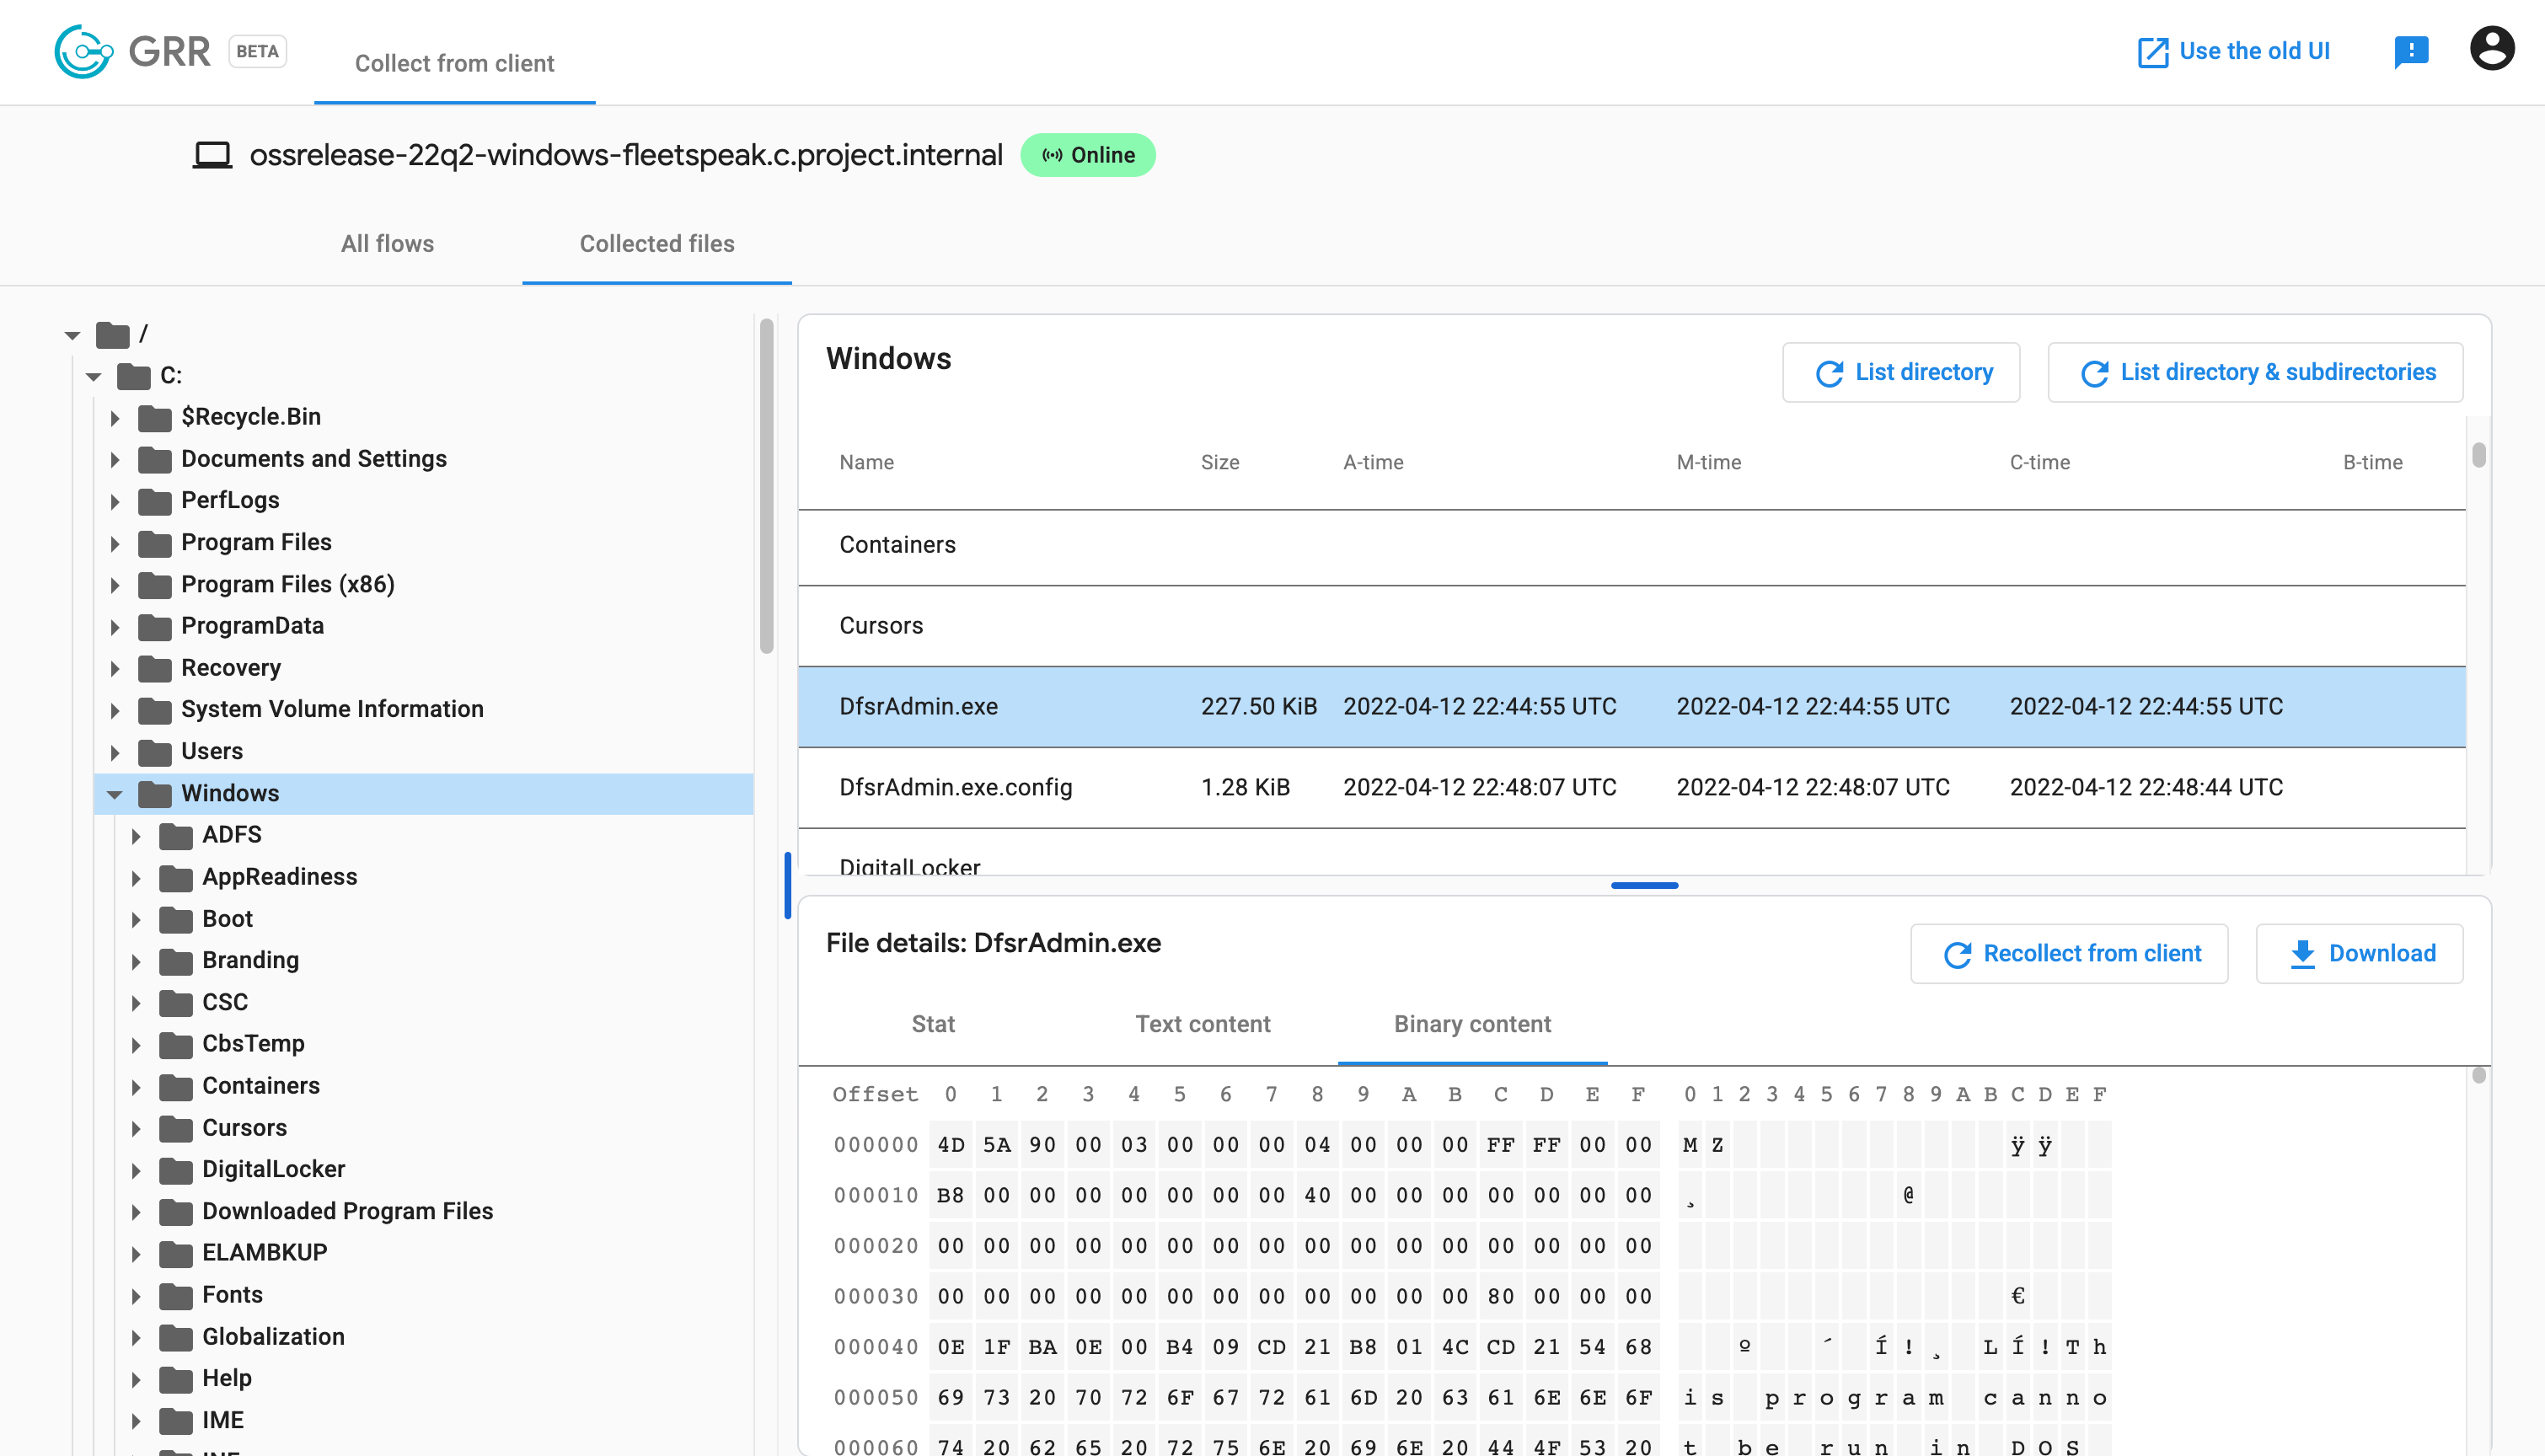 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 cgsecurity/testdisk
Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
 ericzimmerman/kapefiles
This repository serves as a place for community created Targets and Modules for use with KAPE.
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 cristianzsh/forensictools
Collection of forensic tools
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
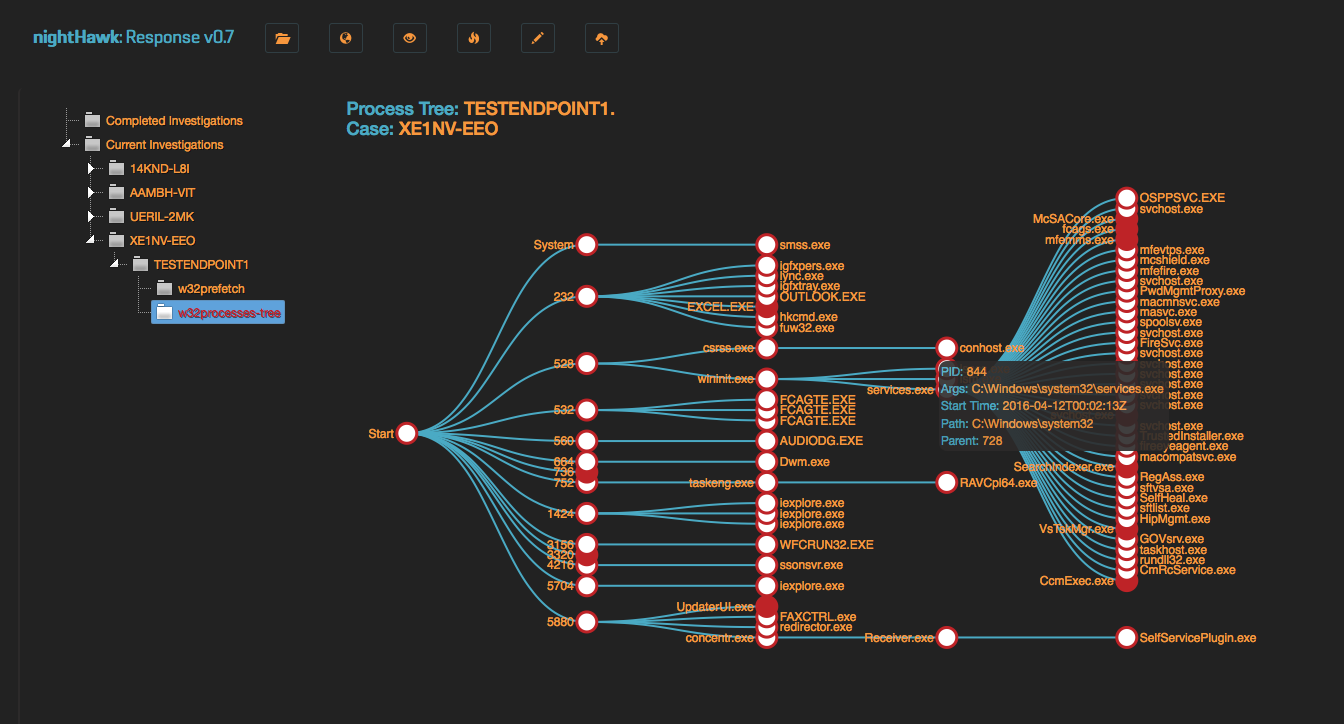 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 jschicht/rawcopy
Commandline low level file extractor for NTFS
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads