
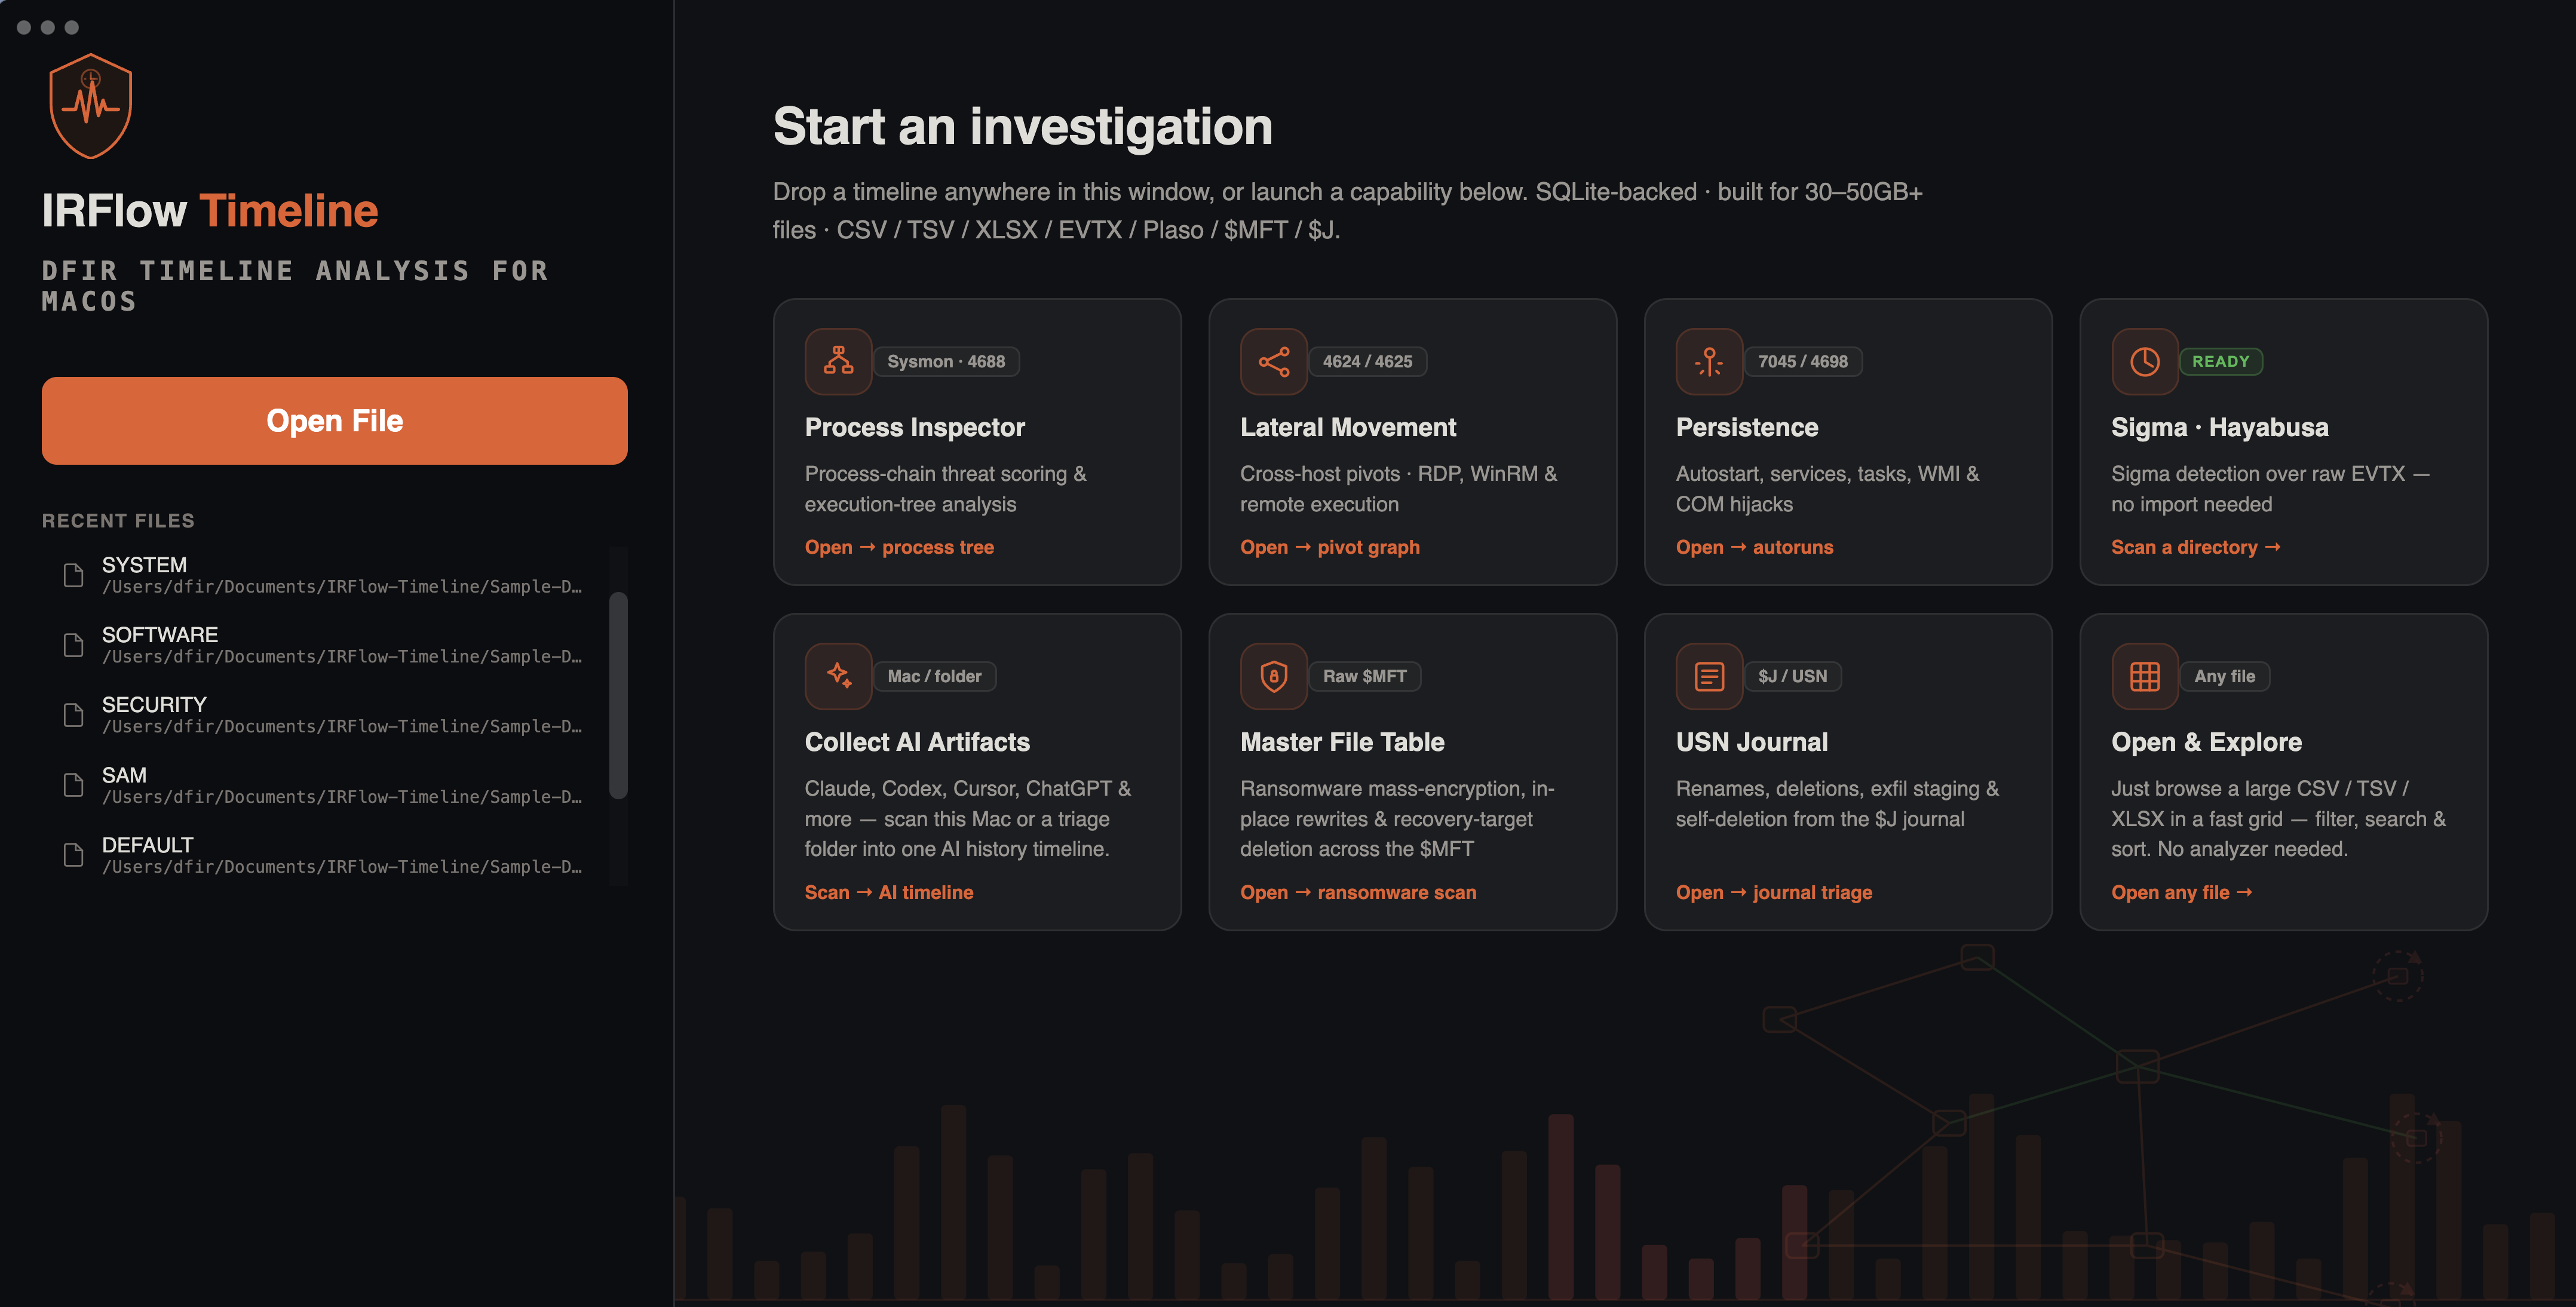
irflow-timeline
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
digital-forensicsdisk-forensicsforensics+7
304
r3nzsec/irflow-timelineDFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 theevidencehunter/forensix
Digital Forensics Intelligence Framework

 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X