timesketch
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k
google/timesketchCollaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
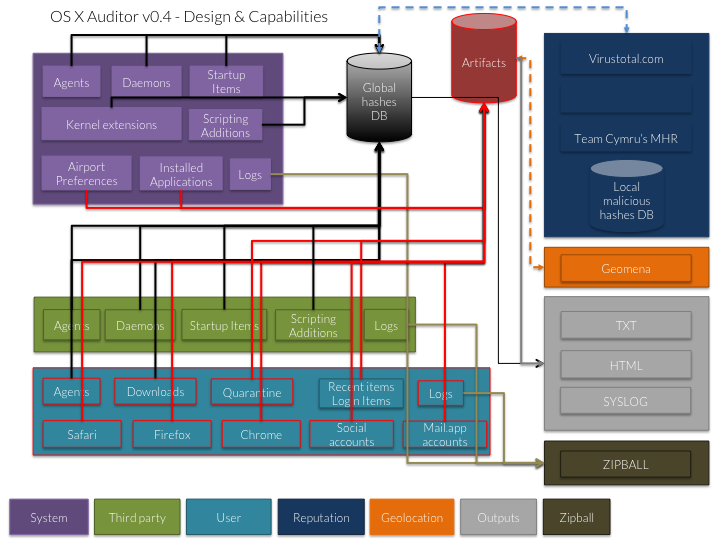 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links

 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
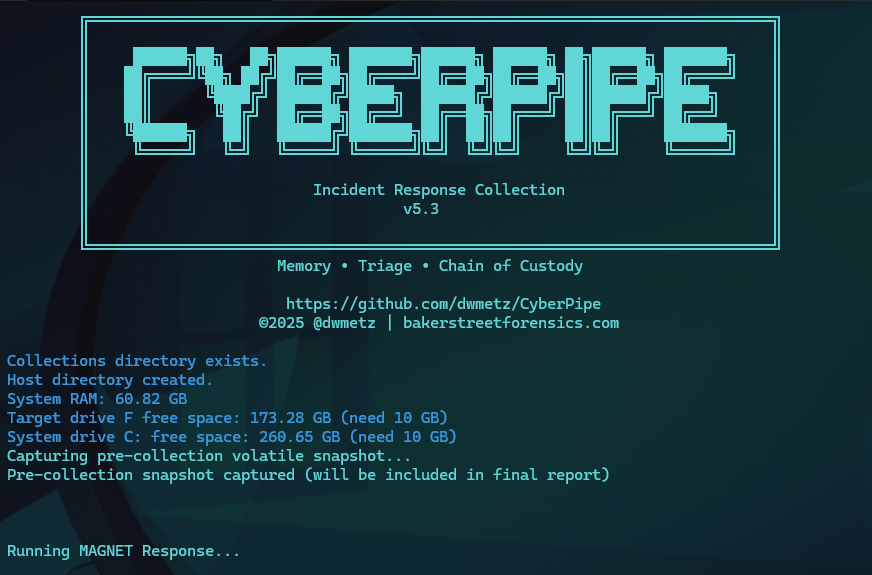 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
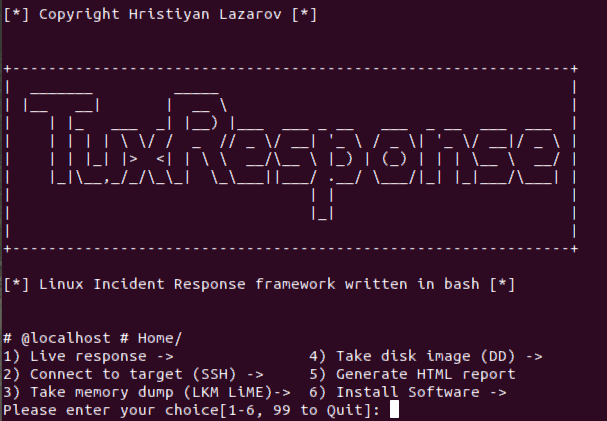 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

 radkawar/aws-firmware-dump
Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…

 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X