
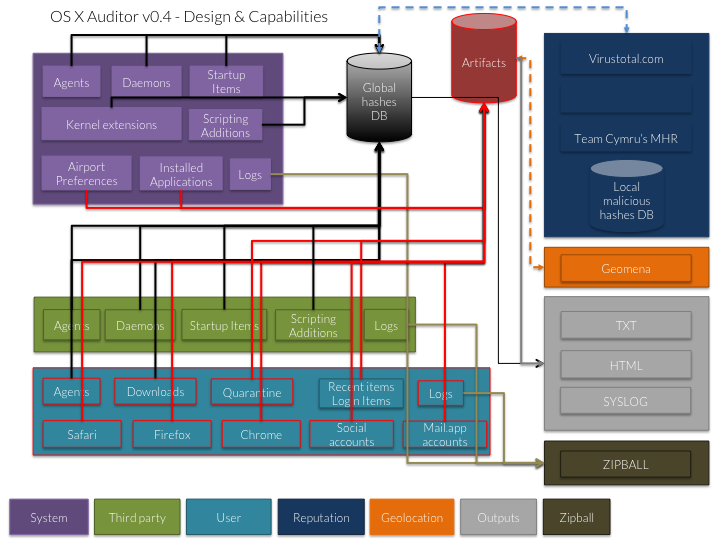
OSXAuditor
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
digital-forensicsdisk-forensicsforensics+4
jipegit/osxauditorOS X Auditor is a free Mac OS X computer forensics tool
 jschicht/extractusnjrnl
Tool to extract the $UsnJrnl from an NTFS volume
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 theevidencehunter/forensix
Digital Forensics Intelligence Framework

 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 cgsecurity/testdisk
Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
 ericzimmerman/kapefiles
This repository serves as a place for community created Targets and Modules for use with KAPE.
 cherojeong/extundelete
Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 libyal/libewf
C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…