Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
74 results
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
819

4 months ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

digital-forensicsdisk-forensicsforensics+7
37229 days ago
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

digital-forensicsdisk-forensicsforensics+6
4885 years ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

digital-forensicsdisk-forensicsforensics+3
5175 years ago
libfsntfs preview

libfsntfs

GitHublibyal/libfsntfs

Library and tools to access the Windows New Technology File System (NTFS)

data-recoverydigital-forensicsdisk-forensics+1
23914 days ago
analyzeMFT preview

analyzeMFT

GitHubrowingdude/analyzemft

analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.

data-recoverydigital-forensicsdisk-forensics+1
5341 year ago
Skadi preview

Skadi

GitHuborlikoski/skadi

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

curated-resourcesdigital-forensicsdisk-forensics+9
5203 years ago
Volumiser preview

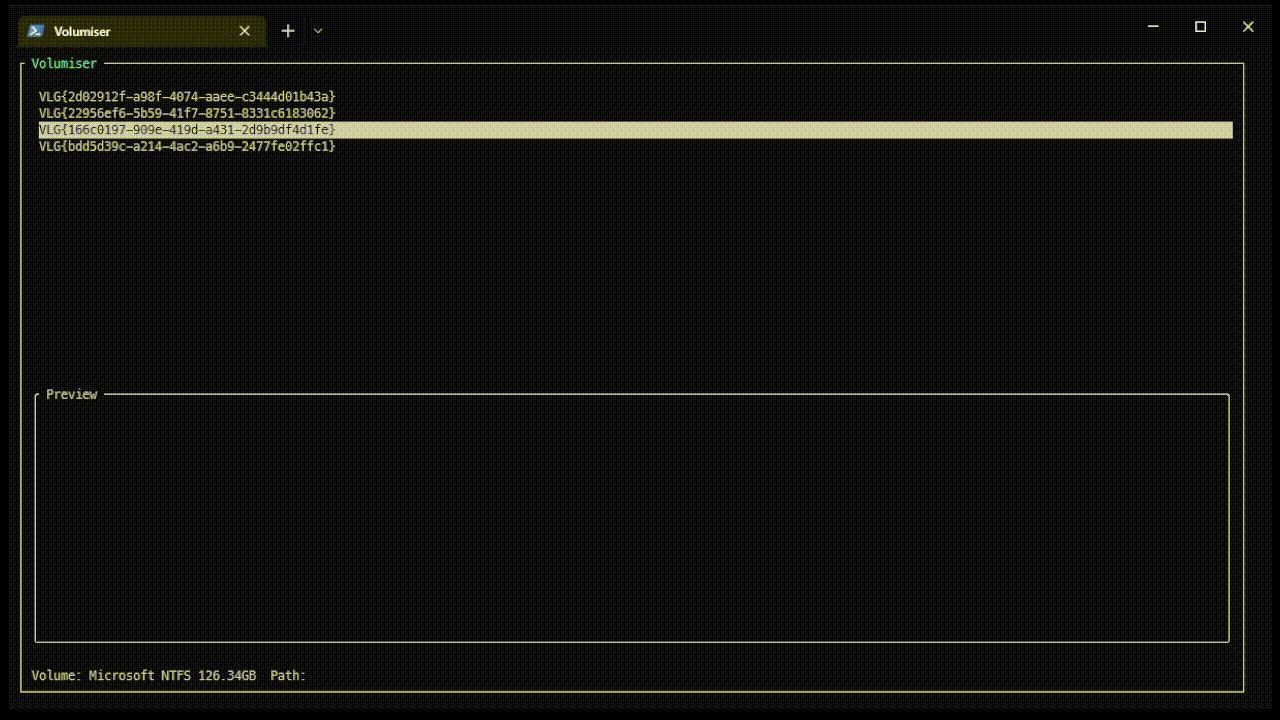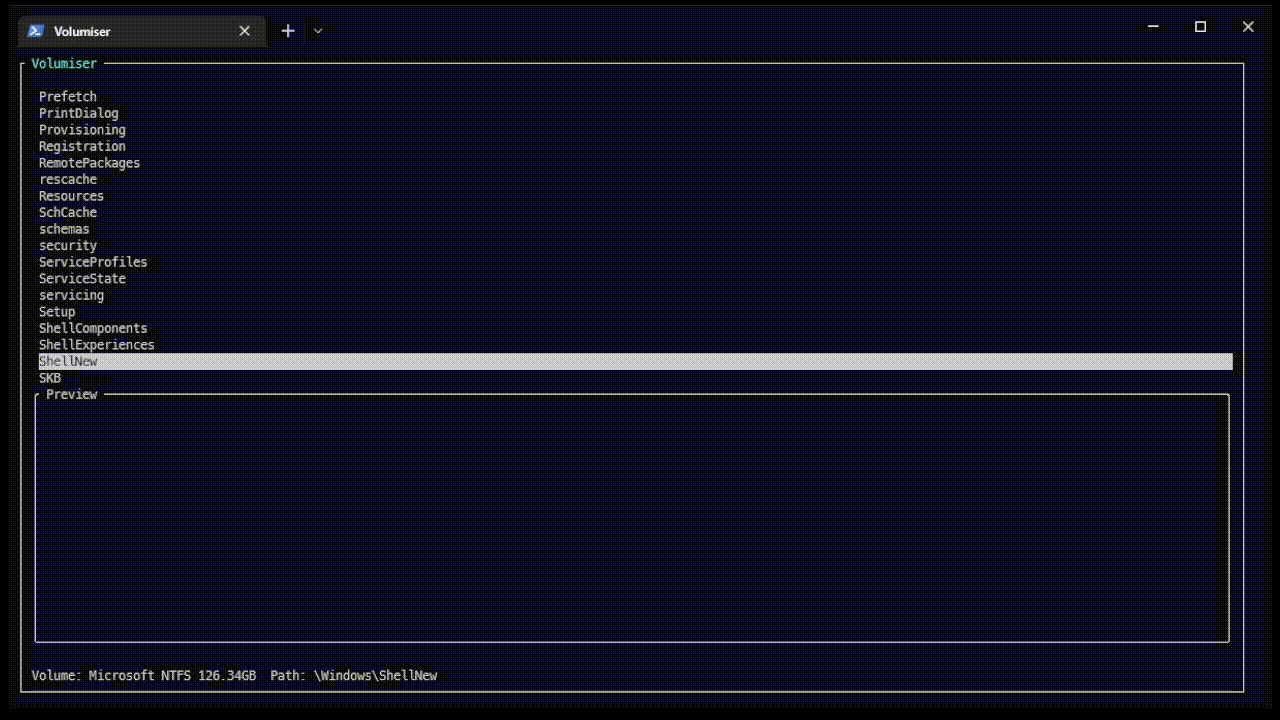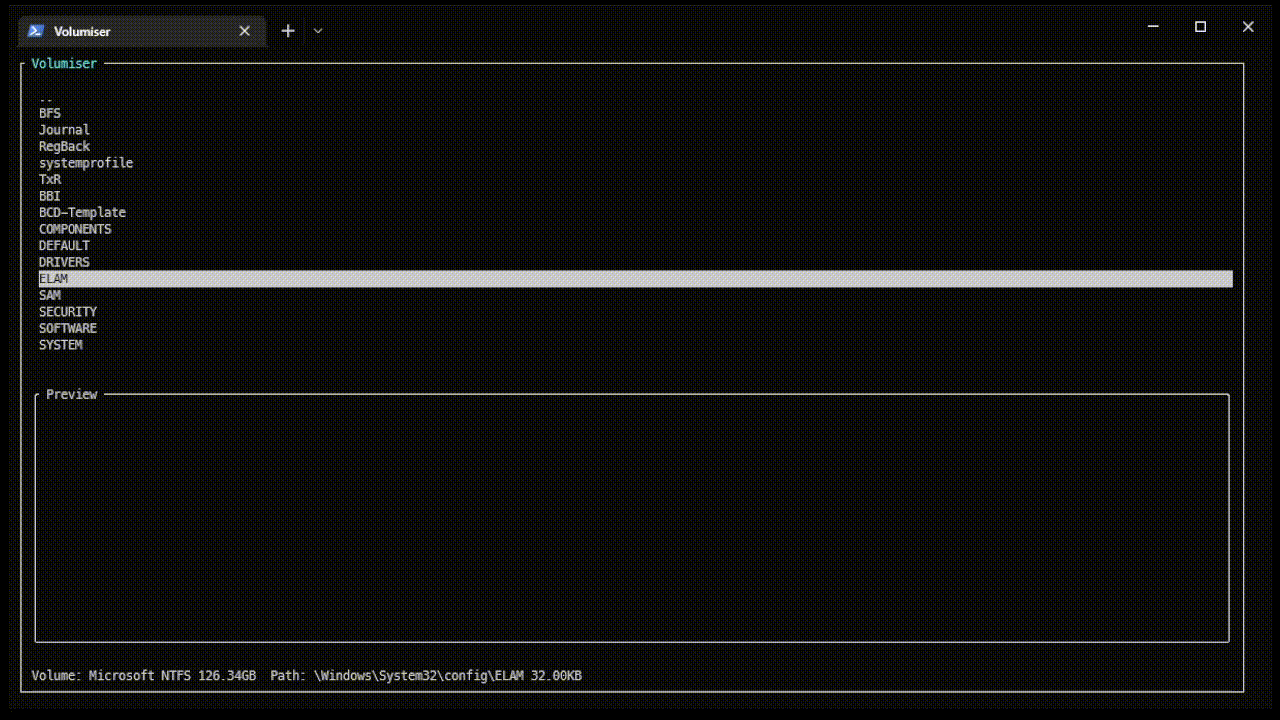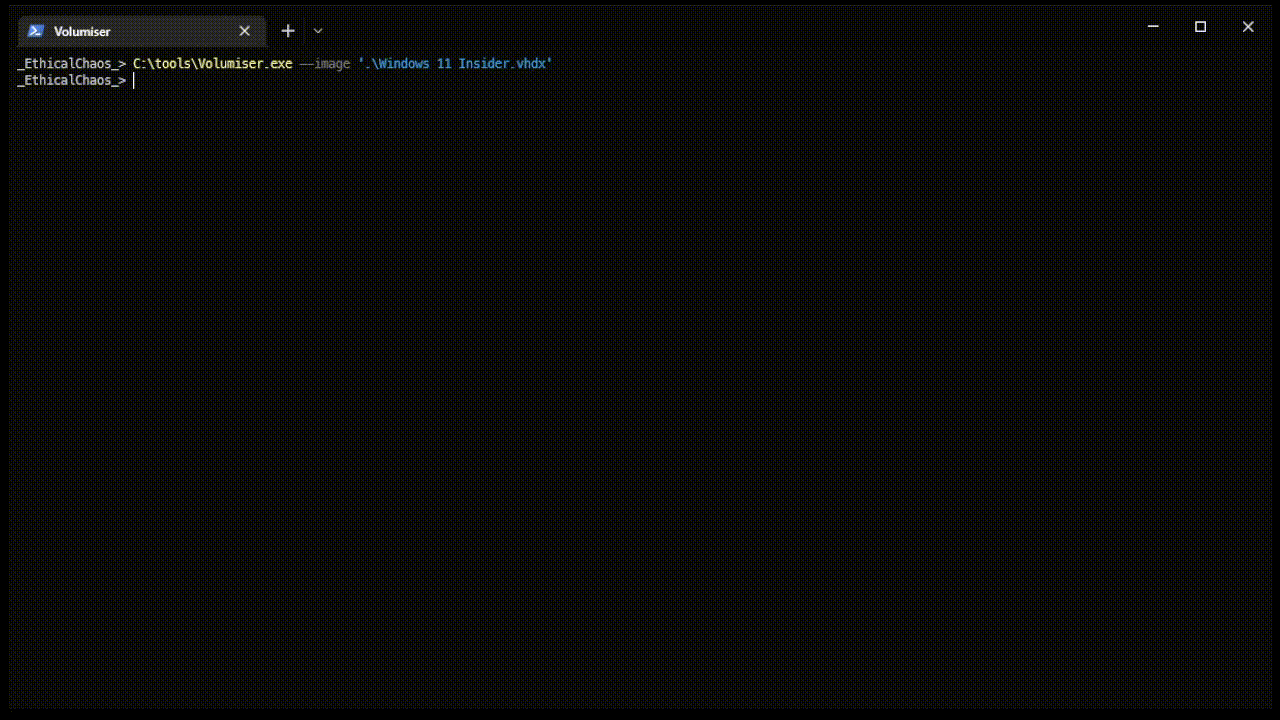
Volumiser

GitHubccob/volumiser

CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…

command-and-controldata-exfiltrationdigital-forensics+3
4361 year ago
libvmdk preview

libvmdk

GitHublibyal/libvmdk

Library and tools to access the VMware Virtual Disk (VMDK) format

data-recoverydigital-forensicsdisk-forensics
18714 days ago
libvhdi preview

libvhdi

GitHublibyal/libvhdi

Library and tools to access the Virtual Hard Disk (VHD) image format

data-recoverydigital-forensicsdisk-forensics+1
14814 days ago
CyberPipe preview

CyberPipe

GitHubdwmetz/cyberpipe

An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.

digital-forensicsdisk-forensicsforensics+2
34710 months ago
foremost preview

foremost

GitHubkorczis/foremost

File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…

data-recoverydigital-forensicsdisk-forensics+2
3809 years ago
fatcat preview

fatcat

GitHubgregwar/fatcat

FAT filesystems explore, extract, repair, and forensic tool

data-recoverydigital-forensicsdisk-forensics+1
3281 year ago
libvshadow preview

libvshadow

GitHublibyal/libvshadow

Library and tools to access the Volume Shadow Snapshot (VSS) format

data-recoverydigital-forensicsdisk-forensics+2
11913 days ago
UnderlayCopy preview

UnderlayCopy

GitHubkfallahi/underlaycopy

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads

data-recoverydigital-forensicsdisk-forensics+3
25411 months ago
tscopy preview

tscopy

GitHubtrustedsec/tscopy

Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…

data-recoverydigital-forensicsdisk-forensics+2
1034 years ago
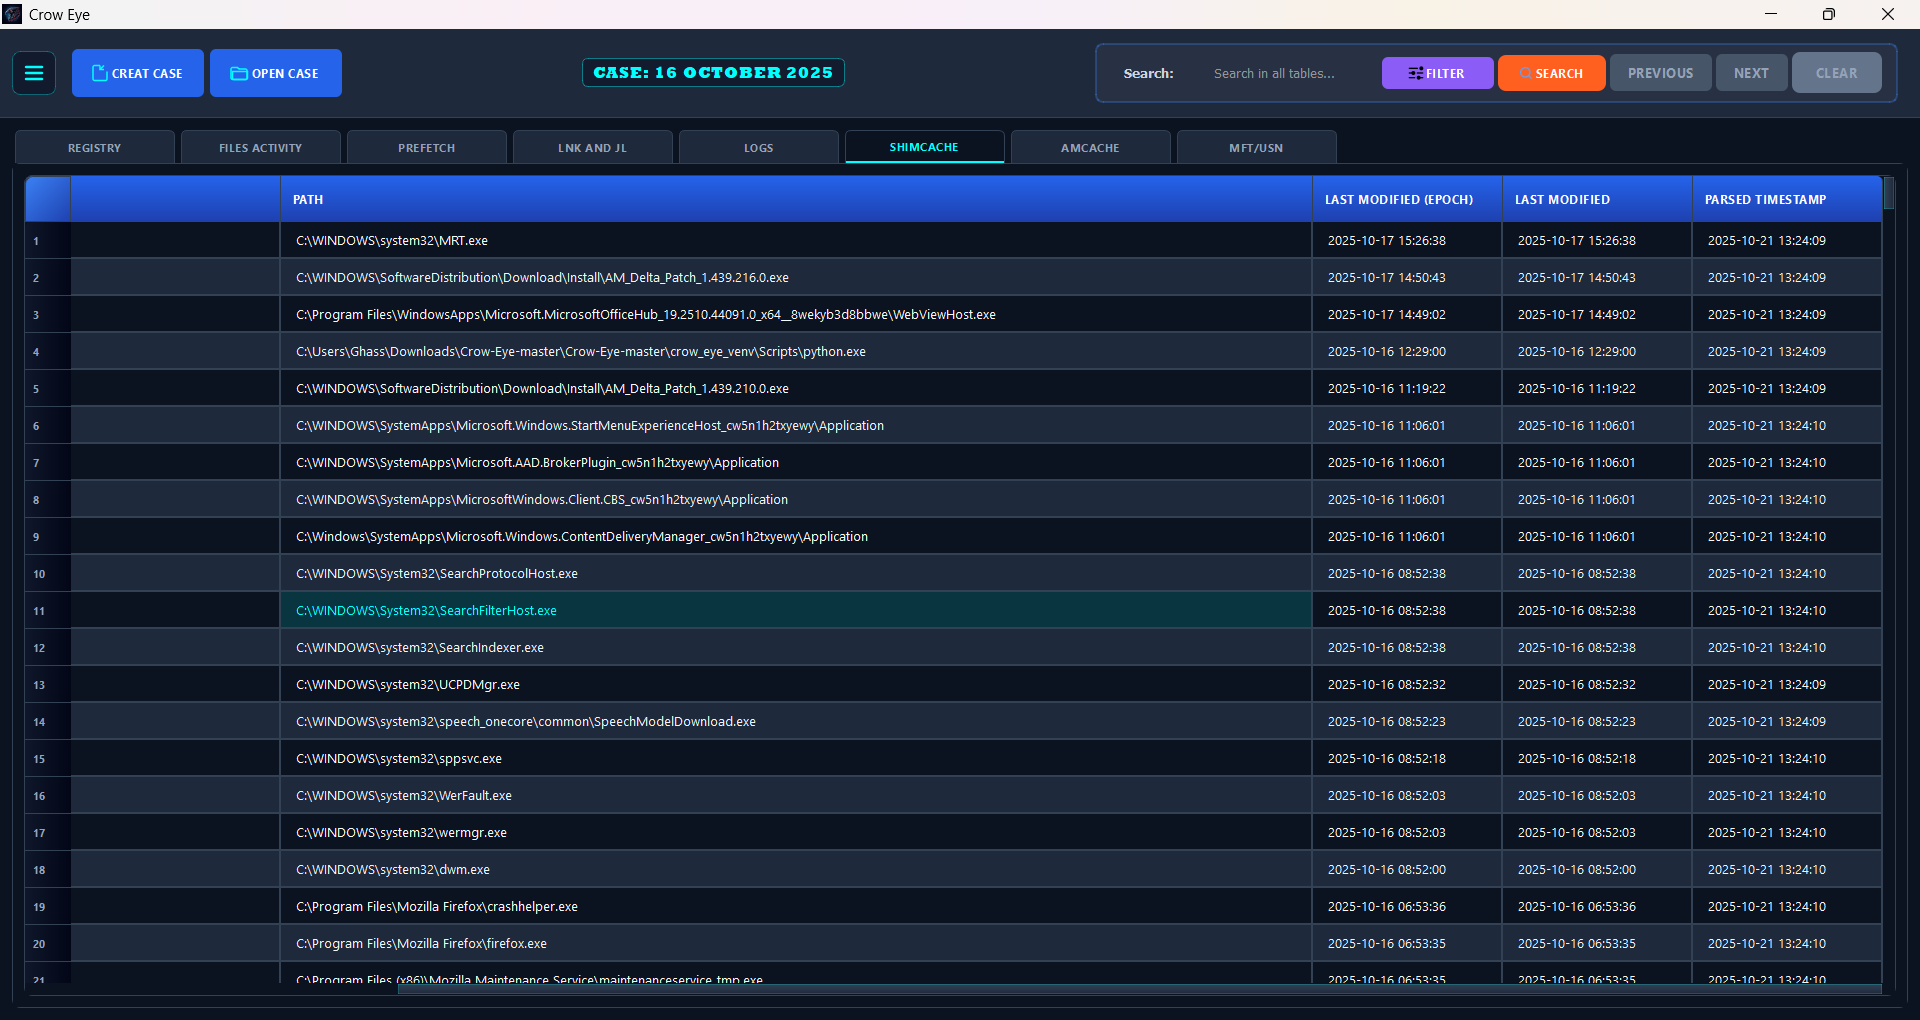
Crow-Eye preview

Crow-Eye

GitHubghassan-elsman/crow-eye

Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…

defensive-toolsdigital-forensicsdisk-forensics+3
11413h 5m ago
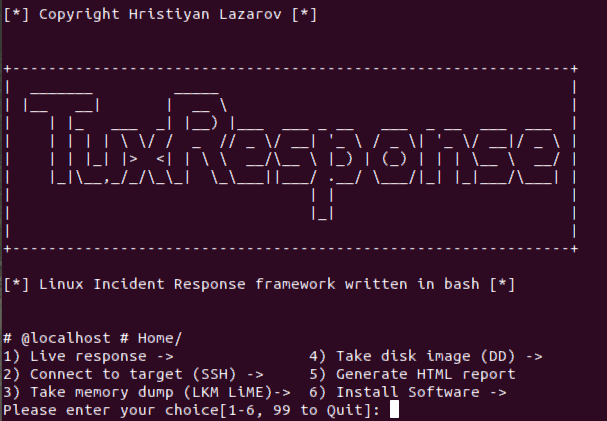
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

digital-forensicsdisk-forensicsforensics+5
915 months ago
Previous12345Next