
dissect
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
data-recoverydigital-forensicsdisk-forensics+5
1.2k
fox-it/dissectDissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
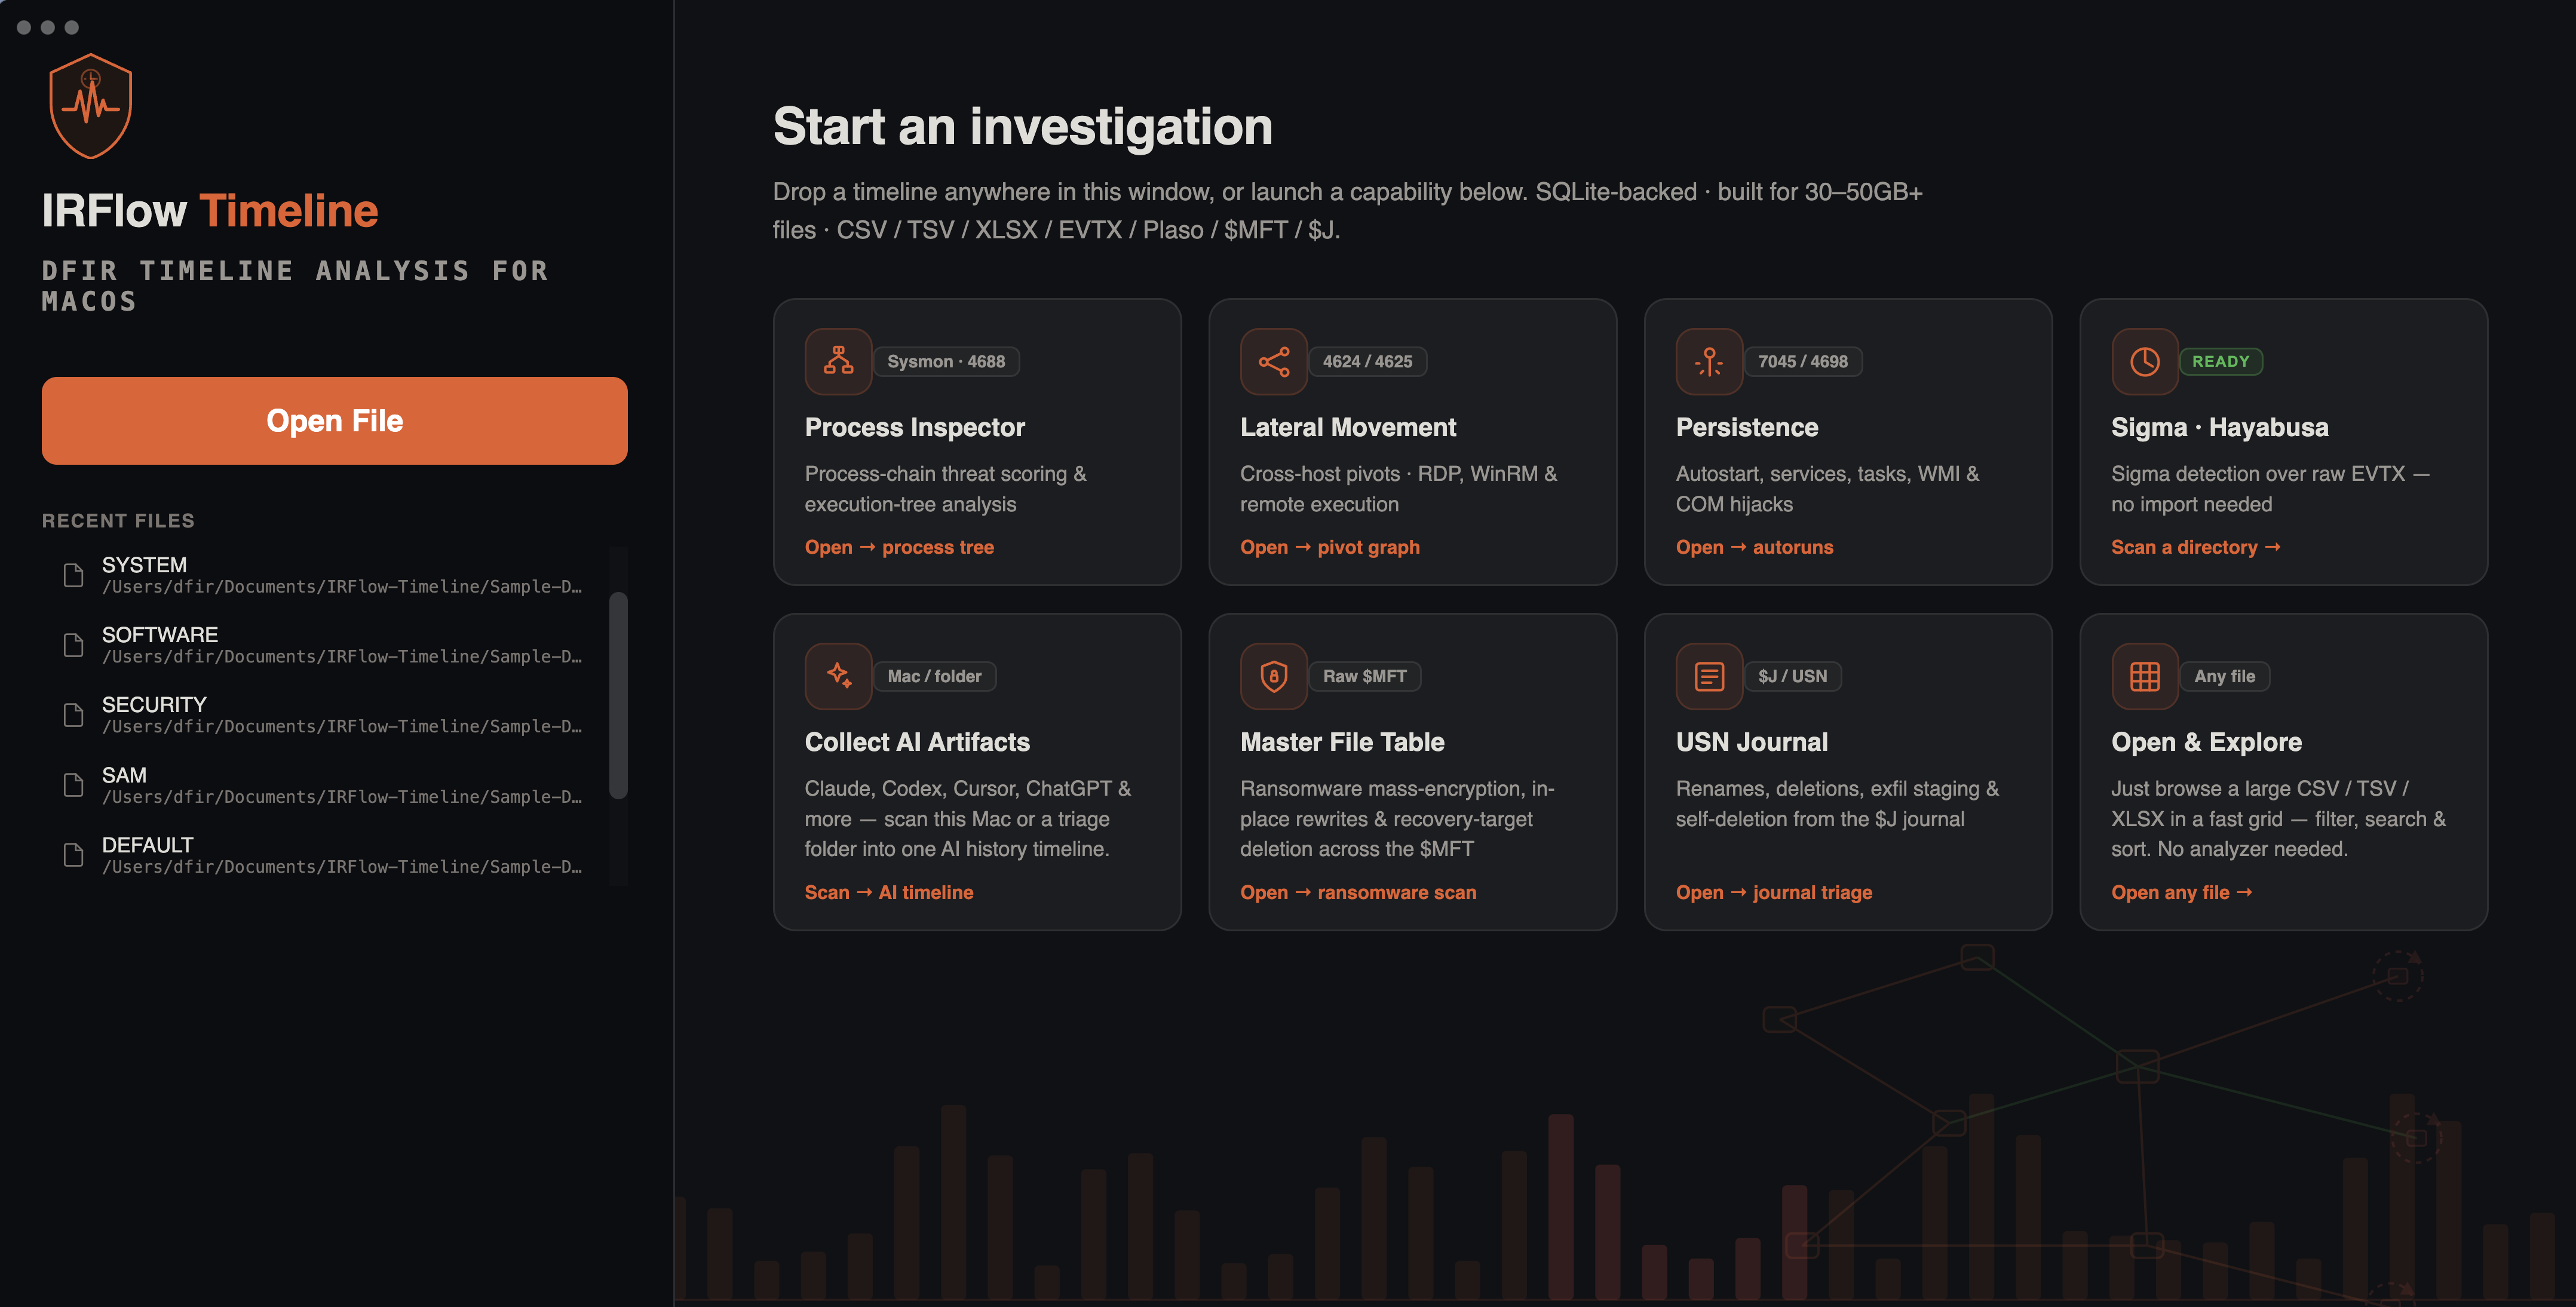 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 libyal/libewf
C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
 libyal/libfsntfs
Library and tools to access the Windows New Technology File System (NTFS)
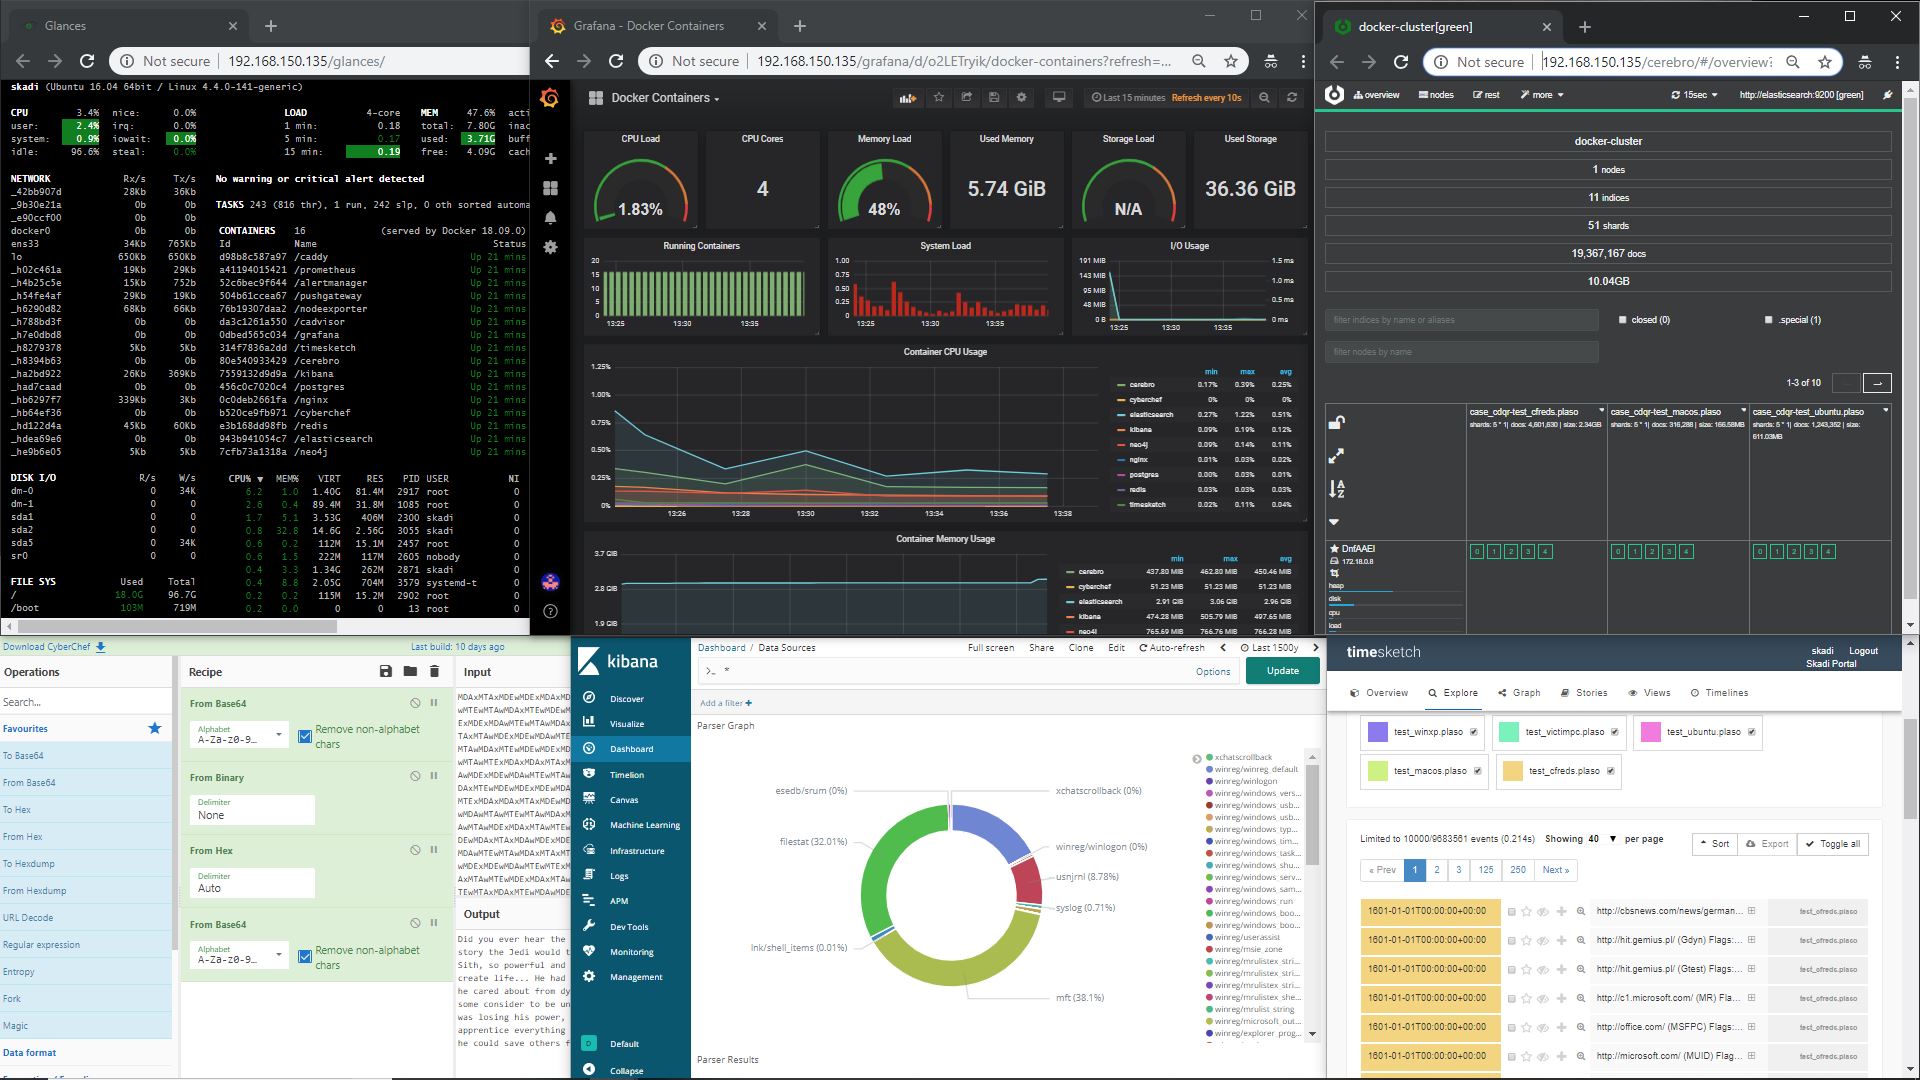 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
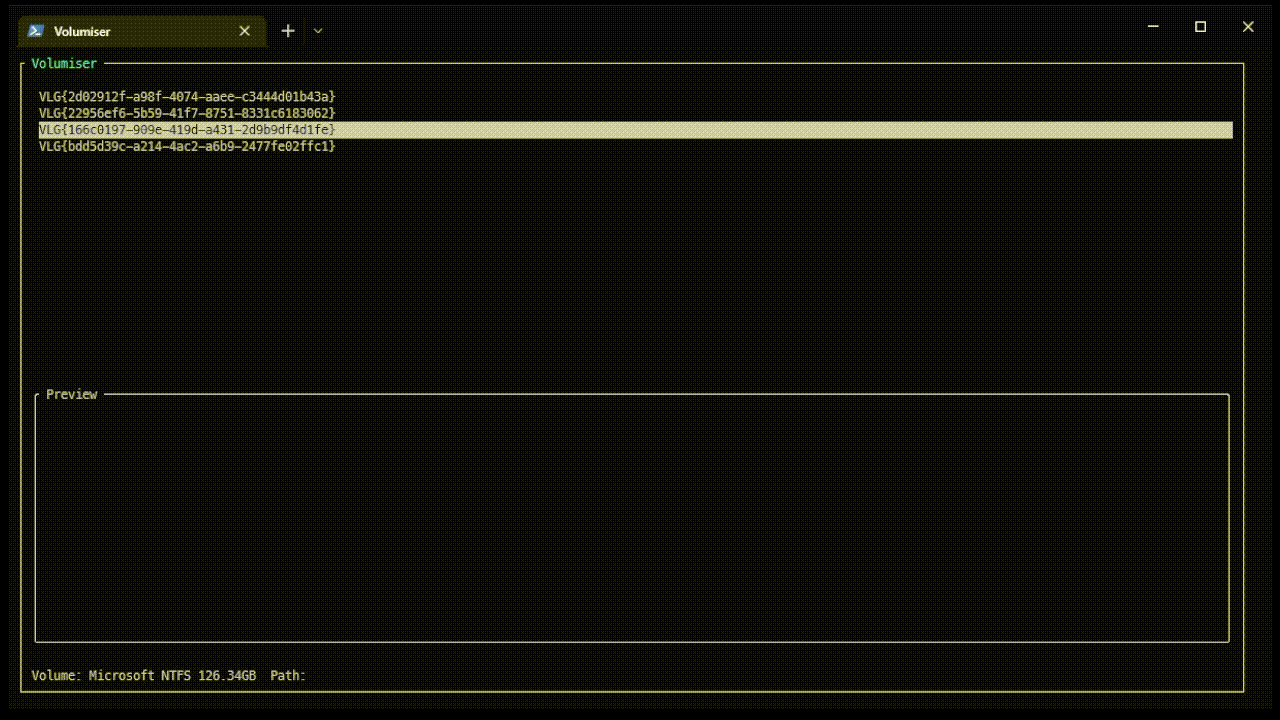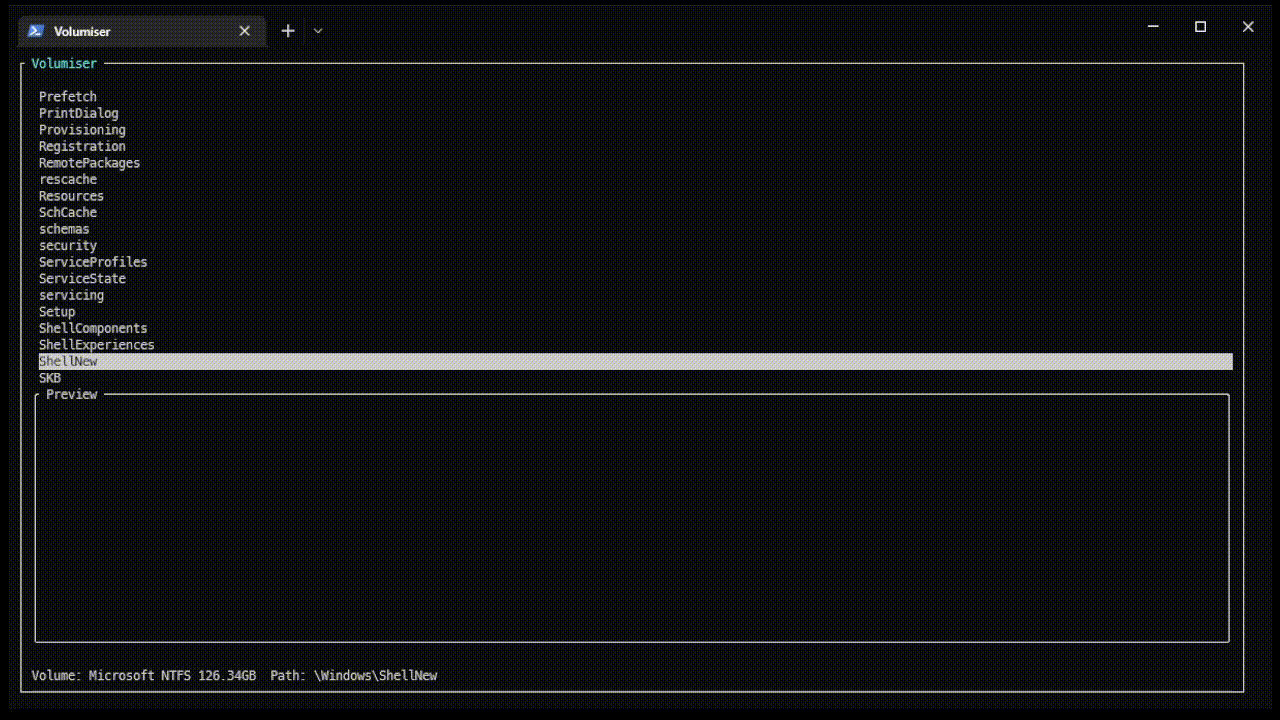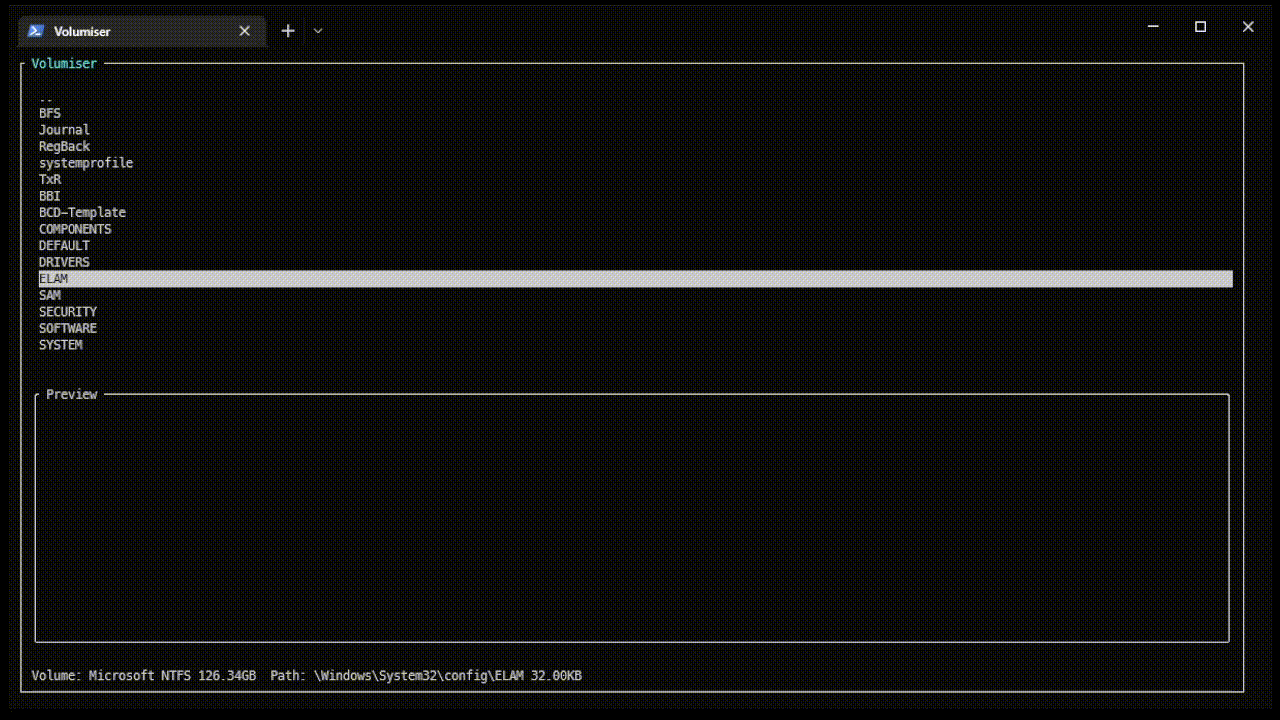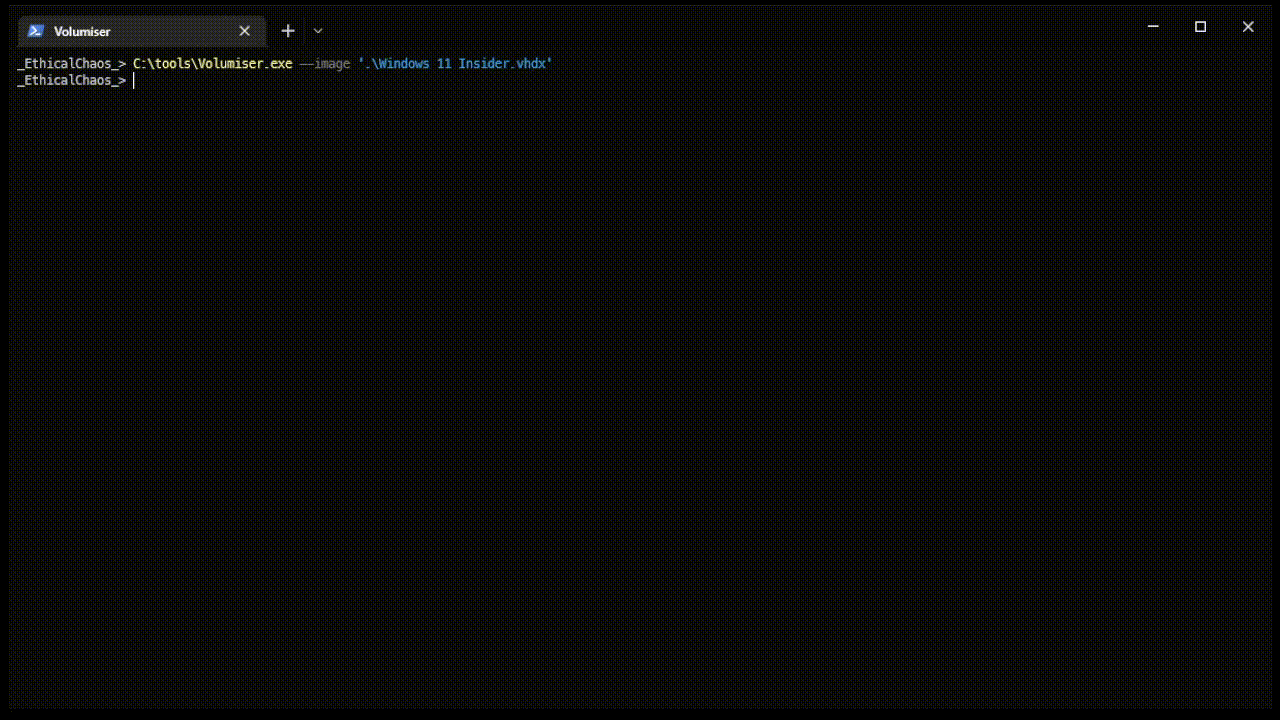 ccob/volumiser
CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 libyal/libvmdk
Library and tools to access the VMware Virtual Disk (VMDK) format
 libyal/libvhdi
Library and tools to access the Virtual Hard Disk (VHD) image format
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
 dmtrkovalenko/ffs
F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
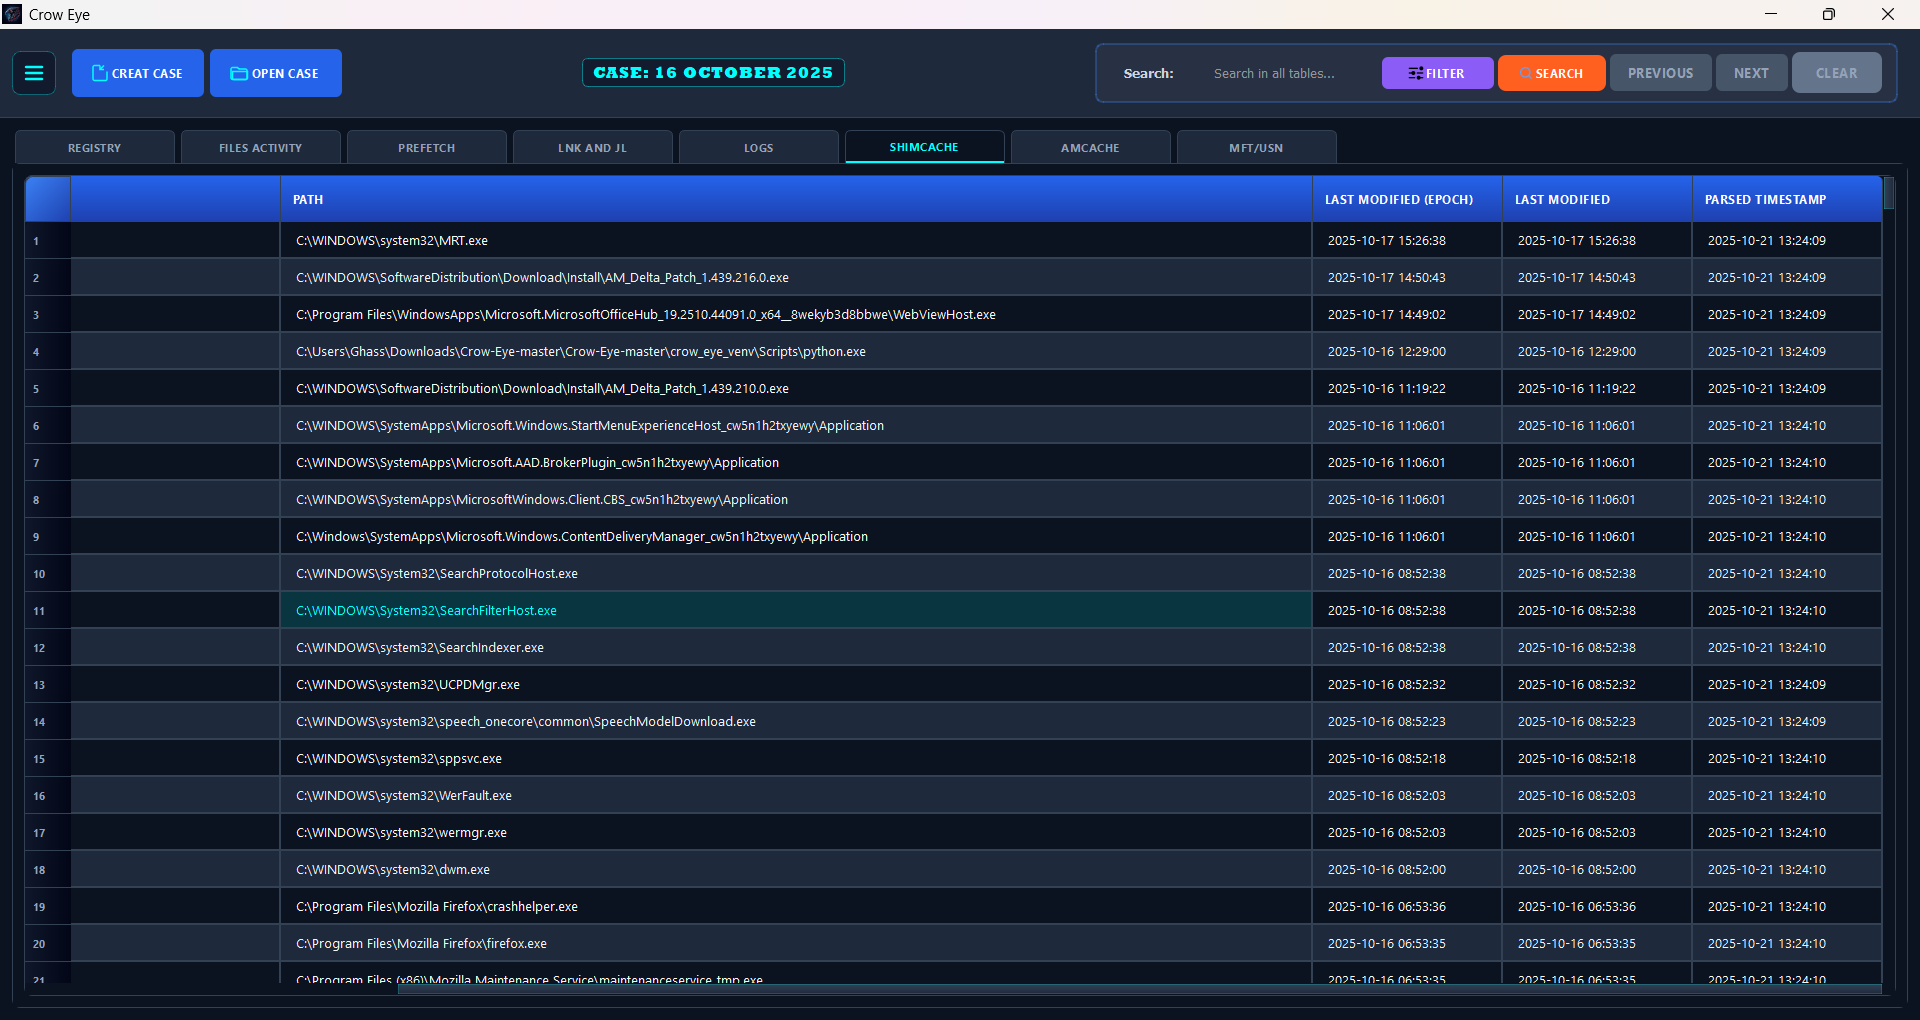 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…