Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

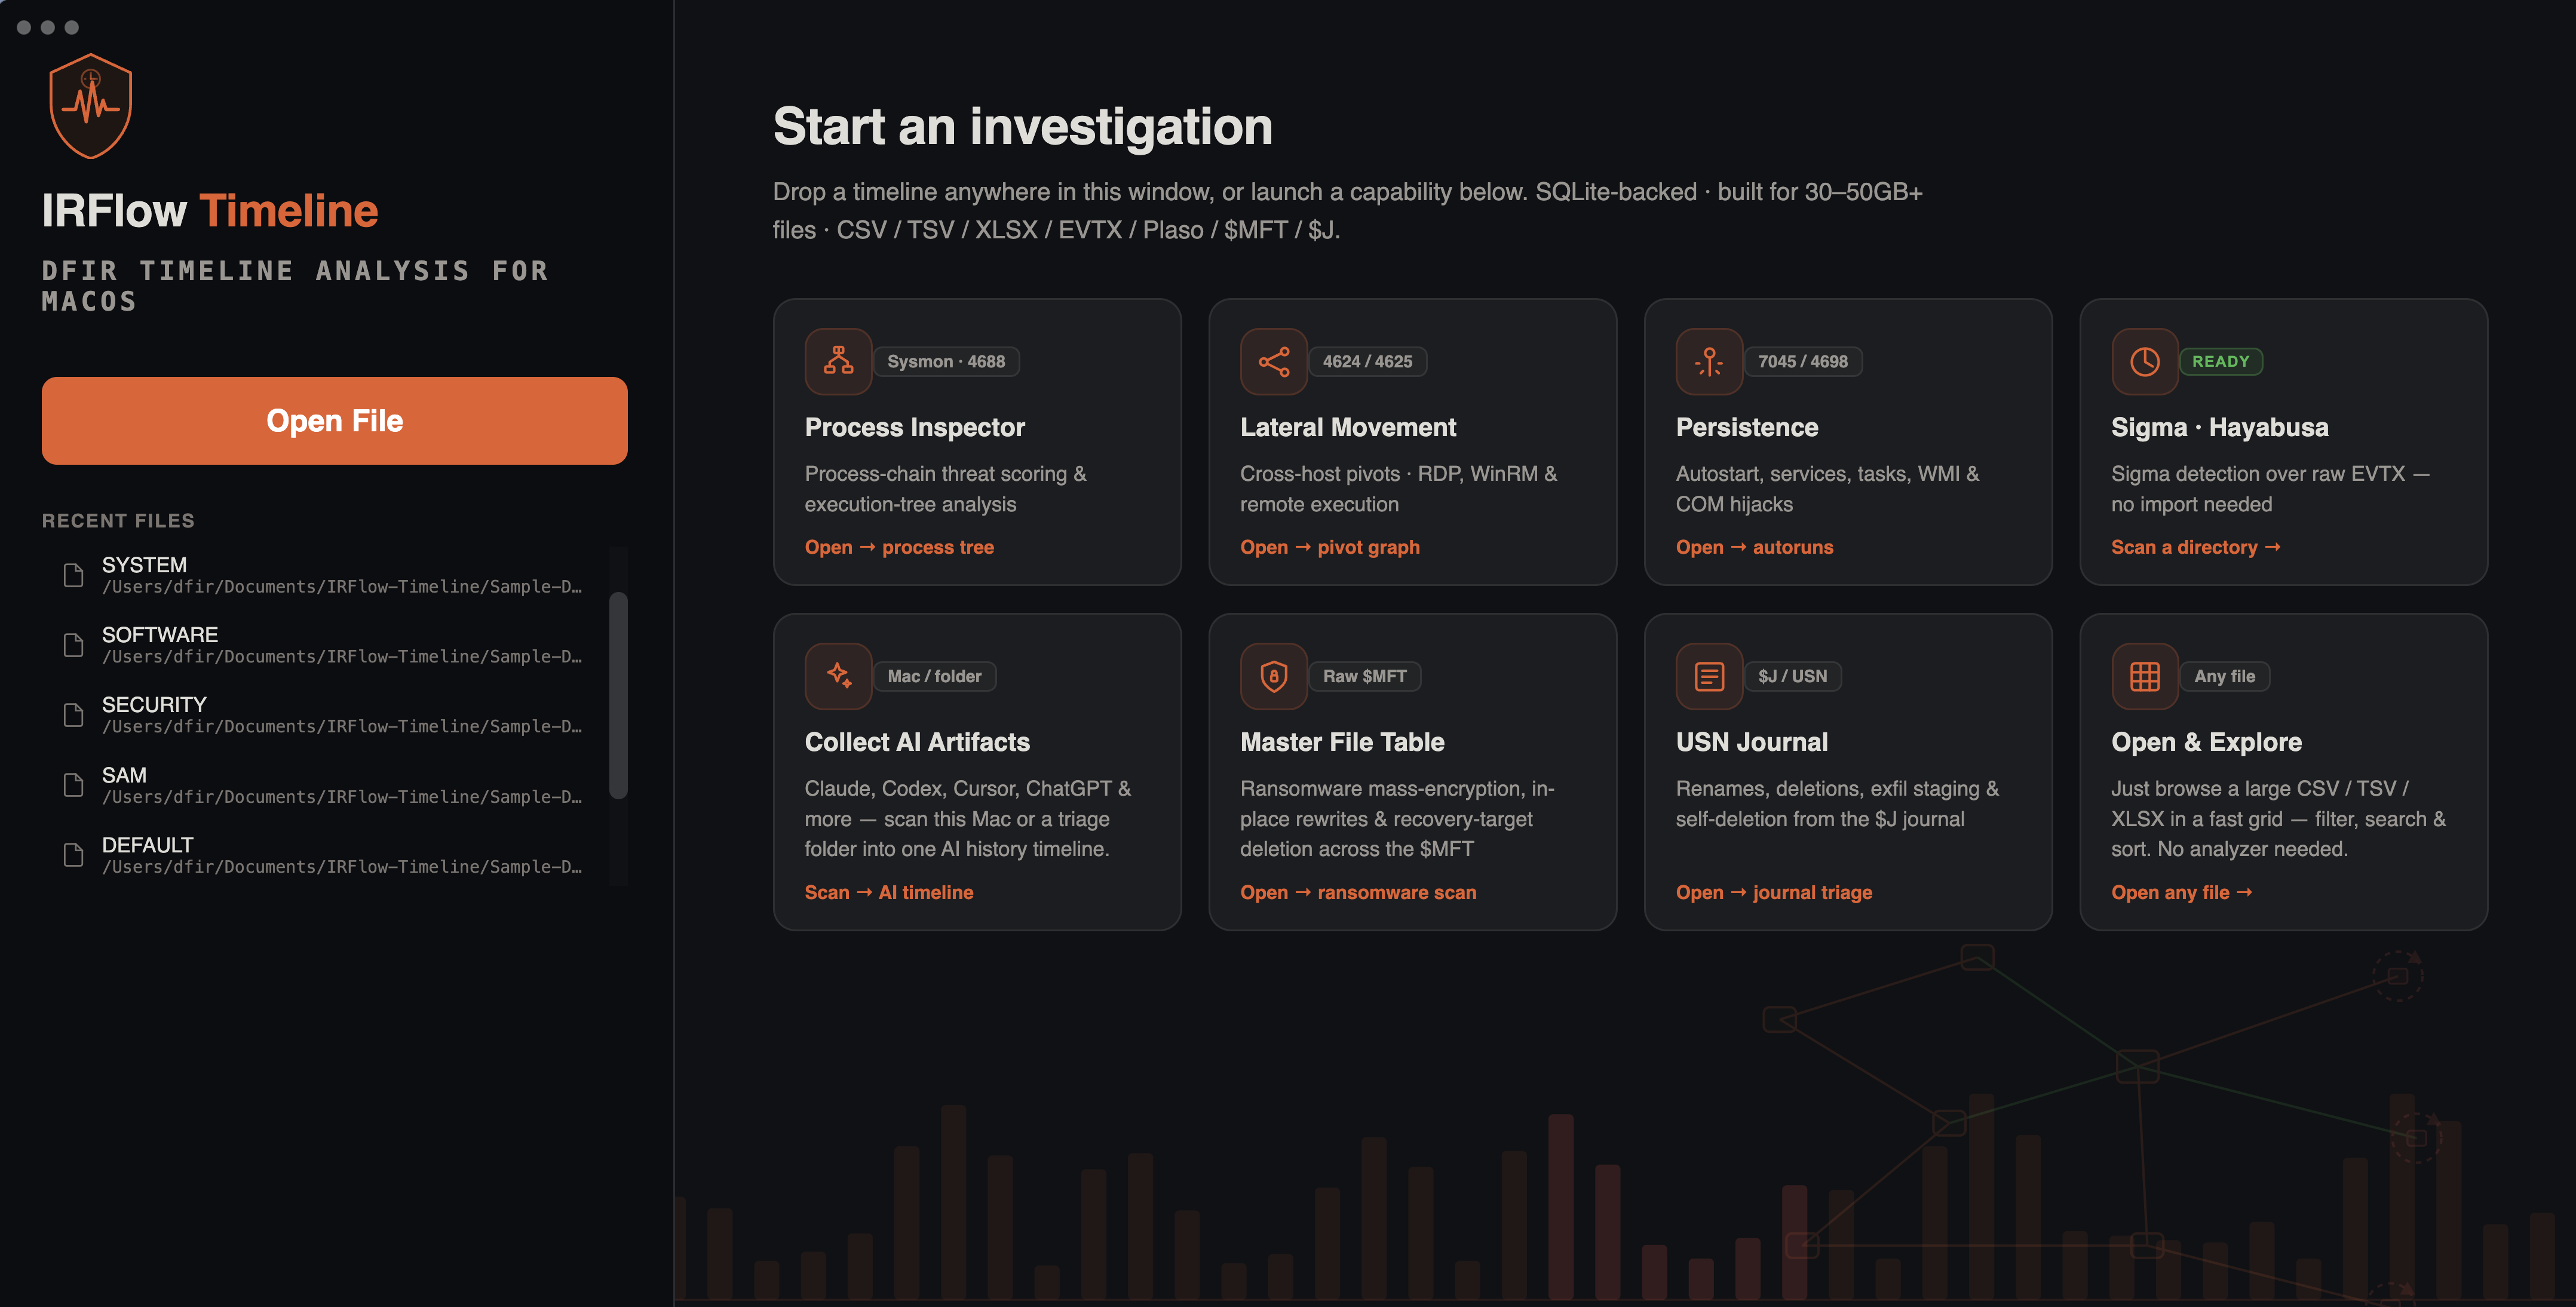
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…

Library and tools to access the Windows New Technology File System (NTFS)

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…

FAT filesystems explore, extract, repair, and forensic tool

Library and tools to access the VMware Virtual Disk (VMDK) format

Library and tools to access the Virtual Hard Disk (VHD) image format

An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.

File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…

Library and tools to access the Volume Shadow Snapshot (VSS) format

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads

Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…

F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry

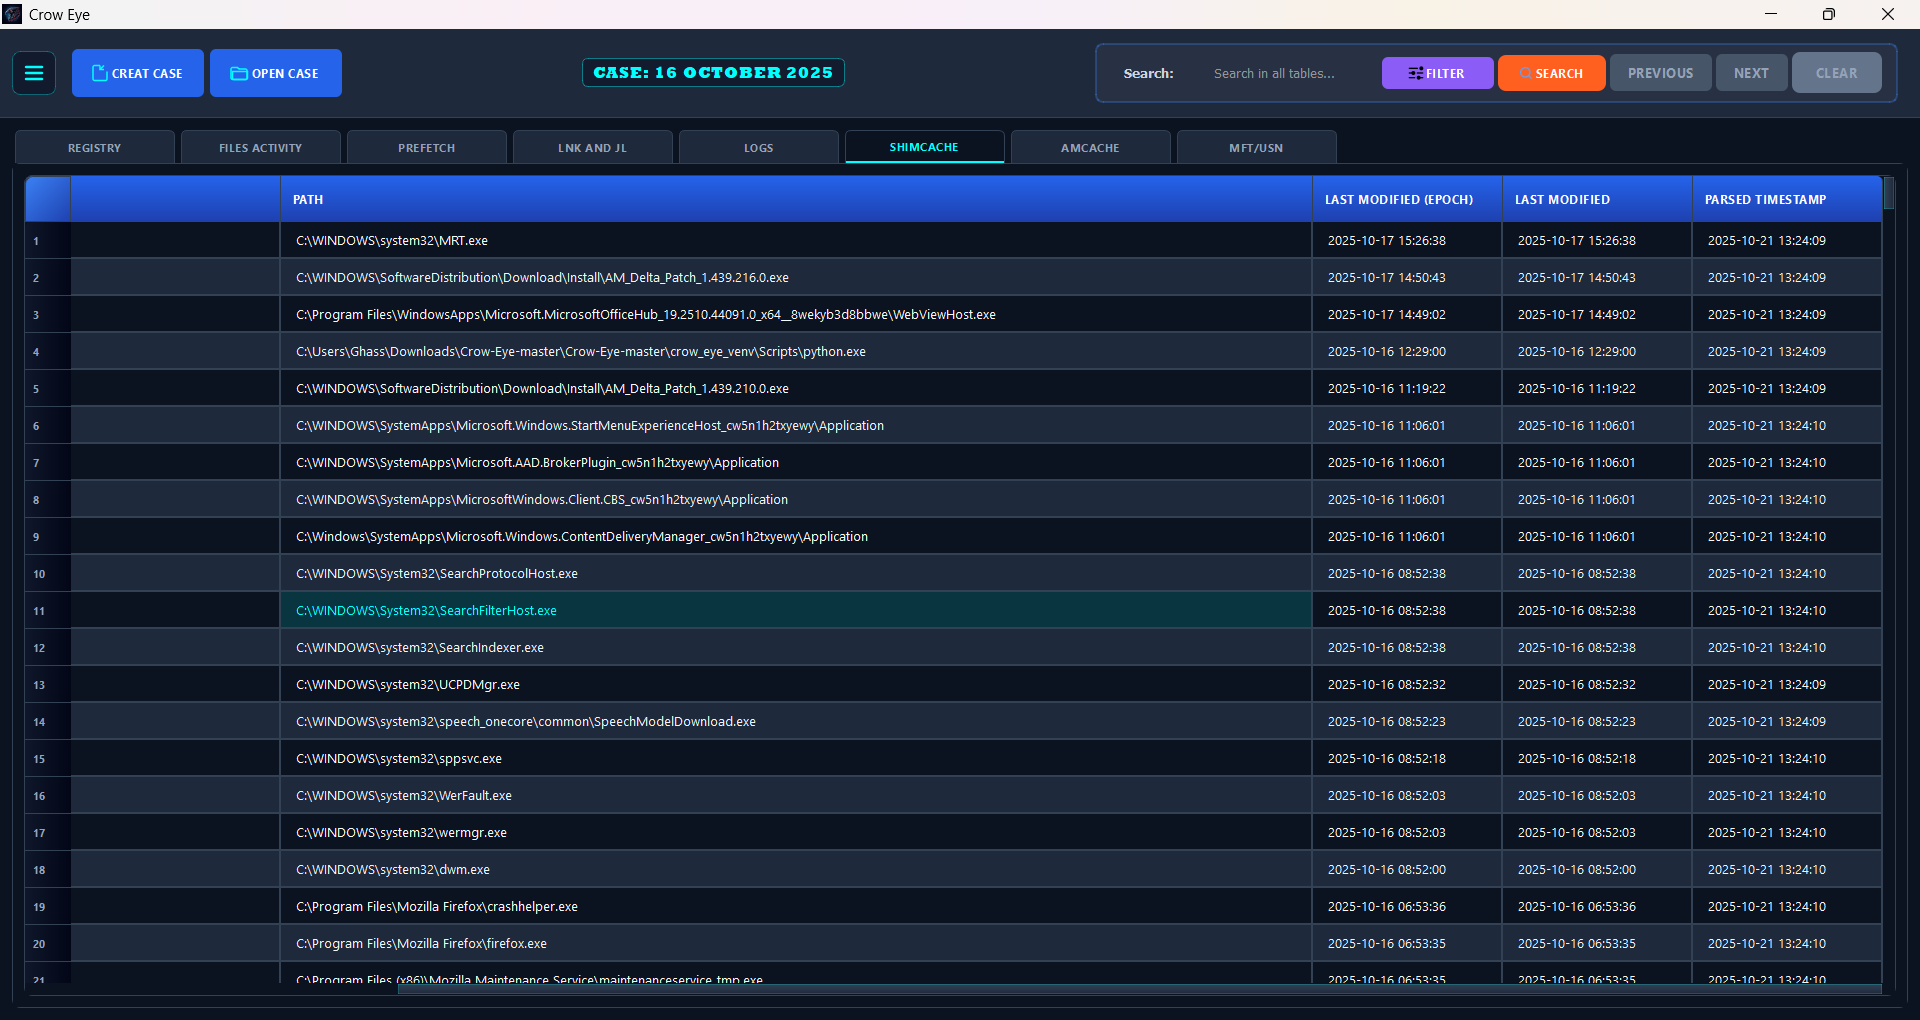
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…