

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
73 results
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

android-securitydigital-forensicsdisk-forensics+7
14.9k
11h 42m ago
sleuthkit preview

sleuthkit

GitHubsleuthkit/sleuthkit

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

data-recoverydigital-forensicsdisk-forensics+3
3.2k12h 14m ago
digital-forensics-lab preview

digital-forensics-lab

GitHubfrankwxu/digital-forensics-lab

Free hands-on digital forensics labs for students and faculty

ai-securityctfdigital-forensics+9
3.0k12h 28m ago
plaso preview

plaso

GitHublog2timeline/plaso

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…


data-recoverydigital-forensicsdisk-forensics+5
2.2k15h 41m ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.3k21h 18m ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…


data-recoverydigital-forensicsdisk-forensics+9
3.0k1 day ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k2 days ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

digital-forensicsdisk-forensicsforensics+4
5.1k2 days ago
libewf preview

libewf

GitHublibyal/libewf

C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…

data-recoverydigital-forensicsdisk-forensics+1
3173 days ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k3 days ago
libvshadow preview

libvshadow

GitHublibyal/libvshadow

Library and tools to access the Volume Shadow Snapshot (VSS) format
data-recoverydigital-forensicsdisk-forensics+2
1193 days ago
libvmdk preview

libvmdk

GitHublibyal/libvmdk

Library and tools to access the VMware Virtual Disk (VMDK) format
data-recoverydigital-forensicsdisk-forensics
1873 days ago
libvhdi preview

libvhdi

GitHublibyal/libvhdi

Library and tools to access the Virtual Hard Disk (VHD) image format

data-recoverydigital-forensicsdisk-forensics+1
1473 days ago
libfsntfs preview

libfsntfs

GitHublibyal/libfsntfs

Library and tools to access the Windows New Technology File System (NTFS)

data-recoverydigital-forensicsdisk-forensics+1
2384 days ago
flare-floss preview

flare-floss

GitHubmandiant/flare-floss

FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.

ai-assisted-reversingbinary-analysisdigital-forensics+8
4.2k5 days ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

ctfdigital-forensicsdisk-forensics+6
5937 days ago
KapeFiles preview

KapeFiles

GitHubericzimmerman/kapefiles

This repository serves as a place for community created Targets and Modules for use with KAPE.
digital-forensicsdisk-forensicsforensics+2
88110 days ago
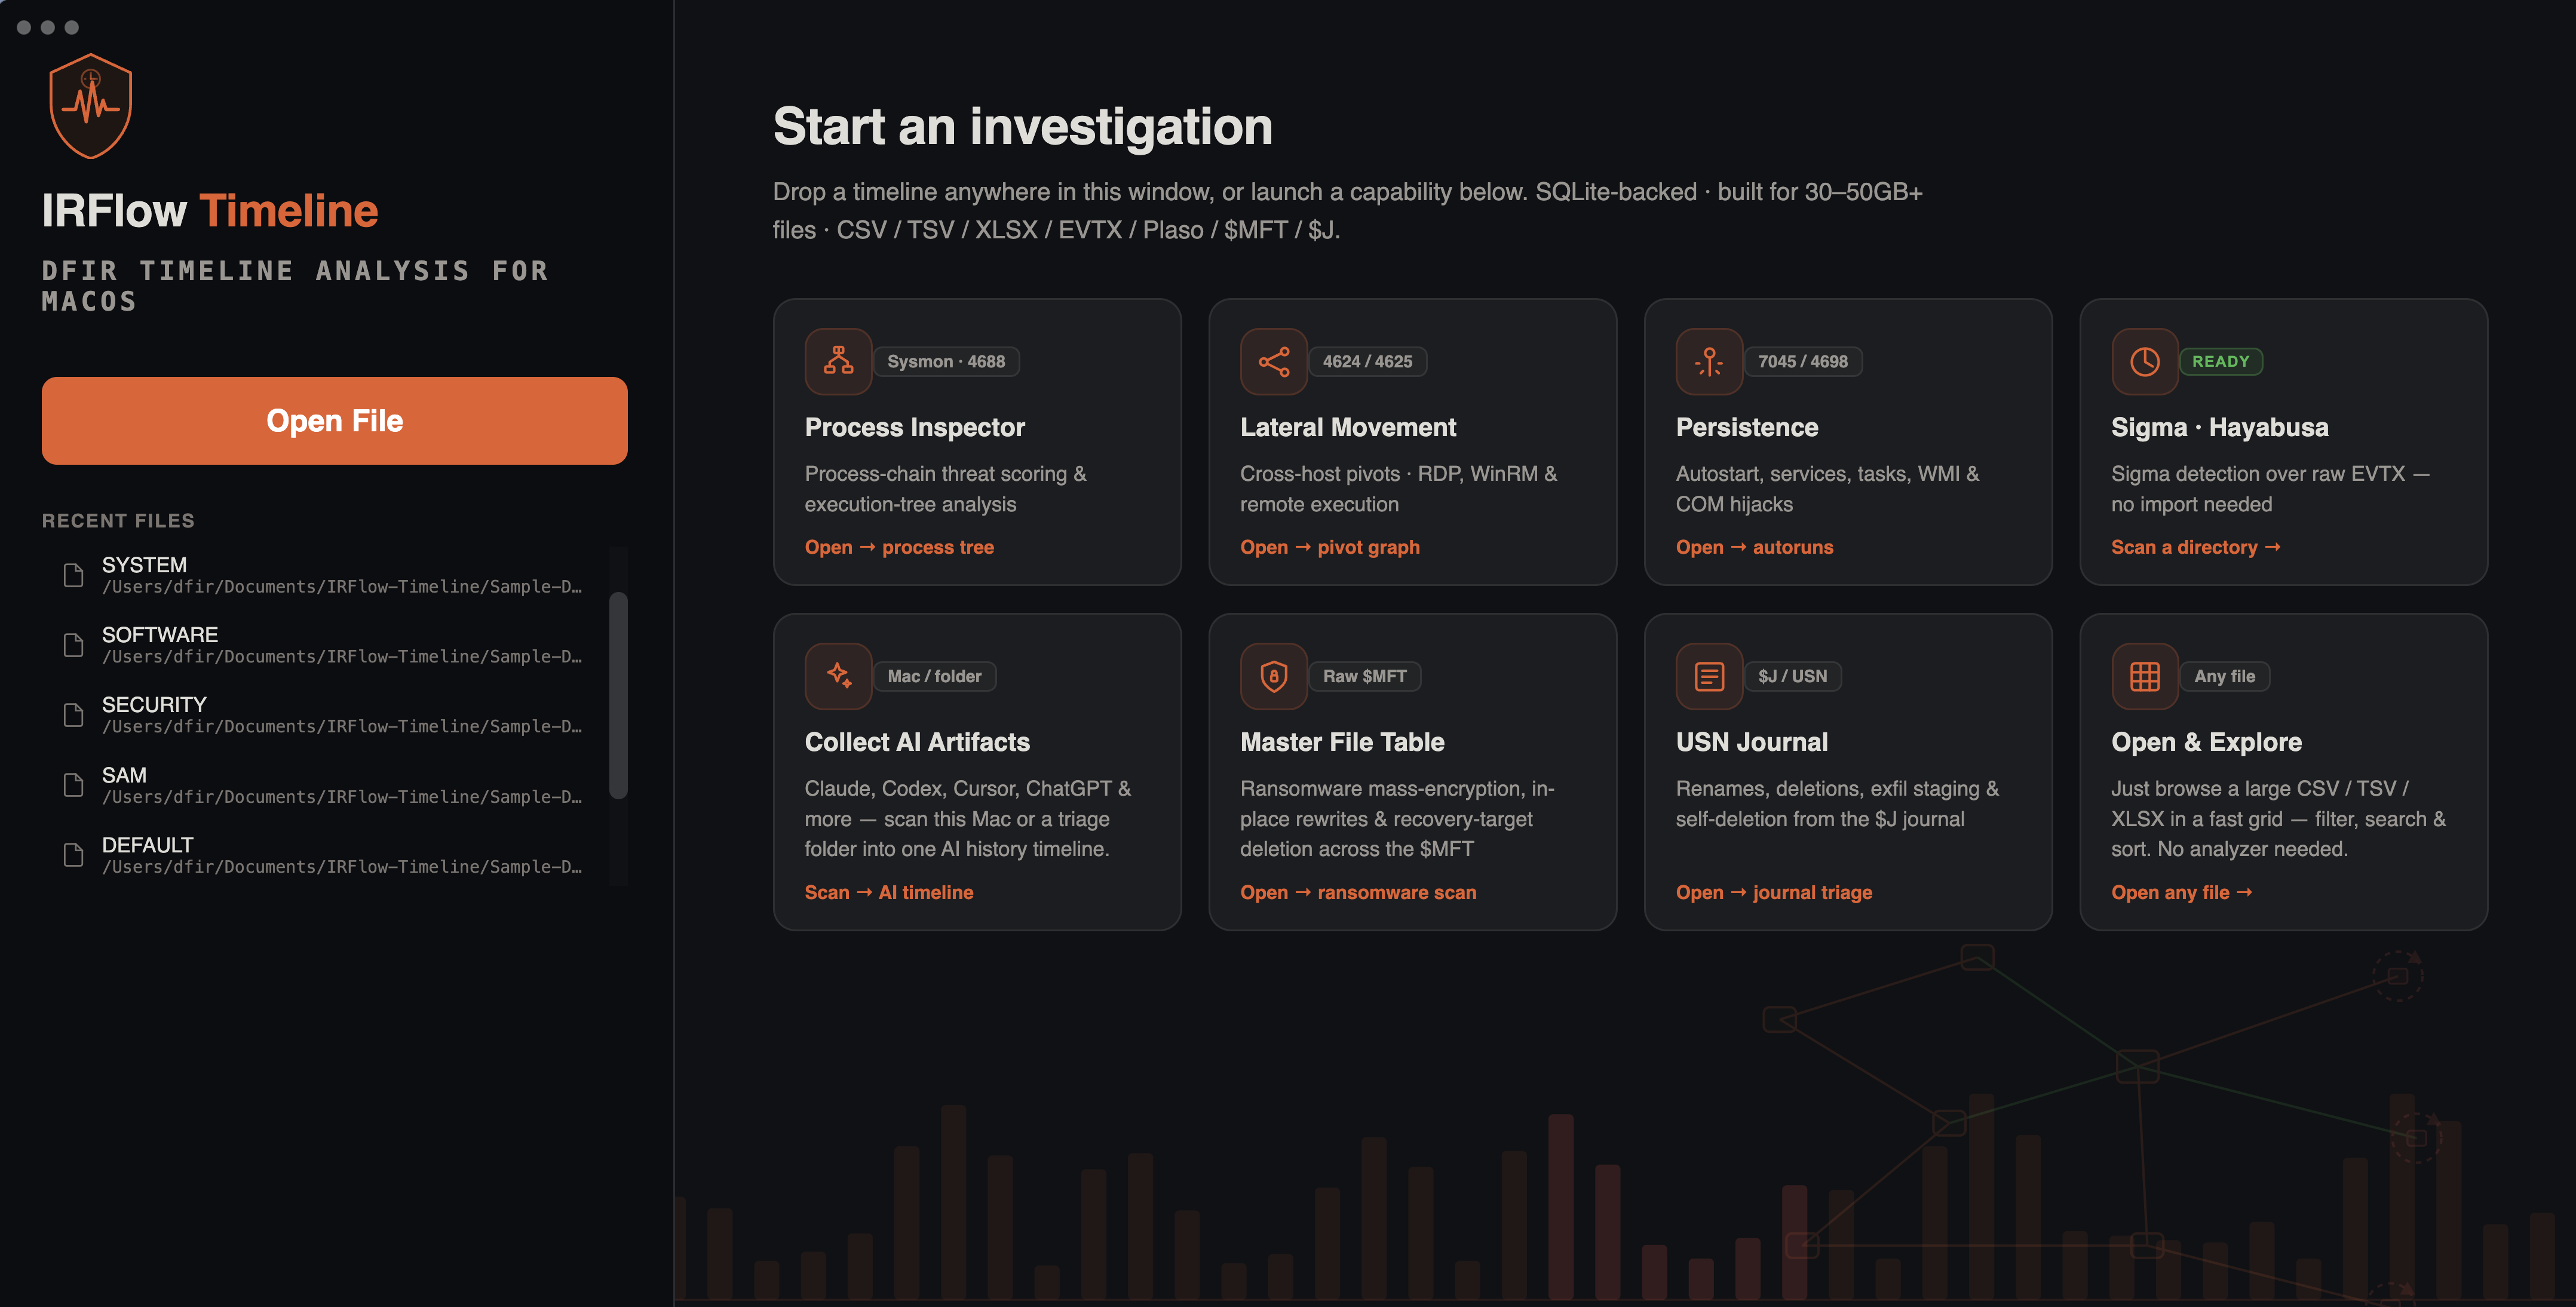
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

digital-forensicsdisk-forensicsforensics+7
37019 days ago
Previous12345Next