

IPED
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
sepinf-inc/ipedIPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.

 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
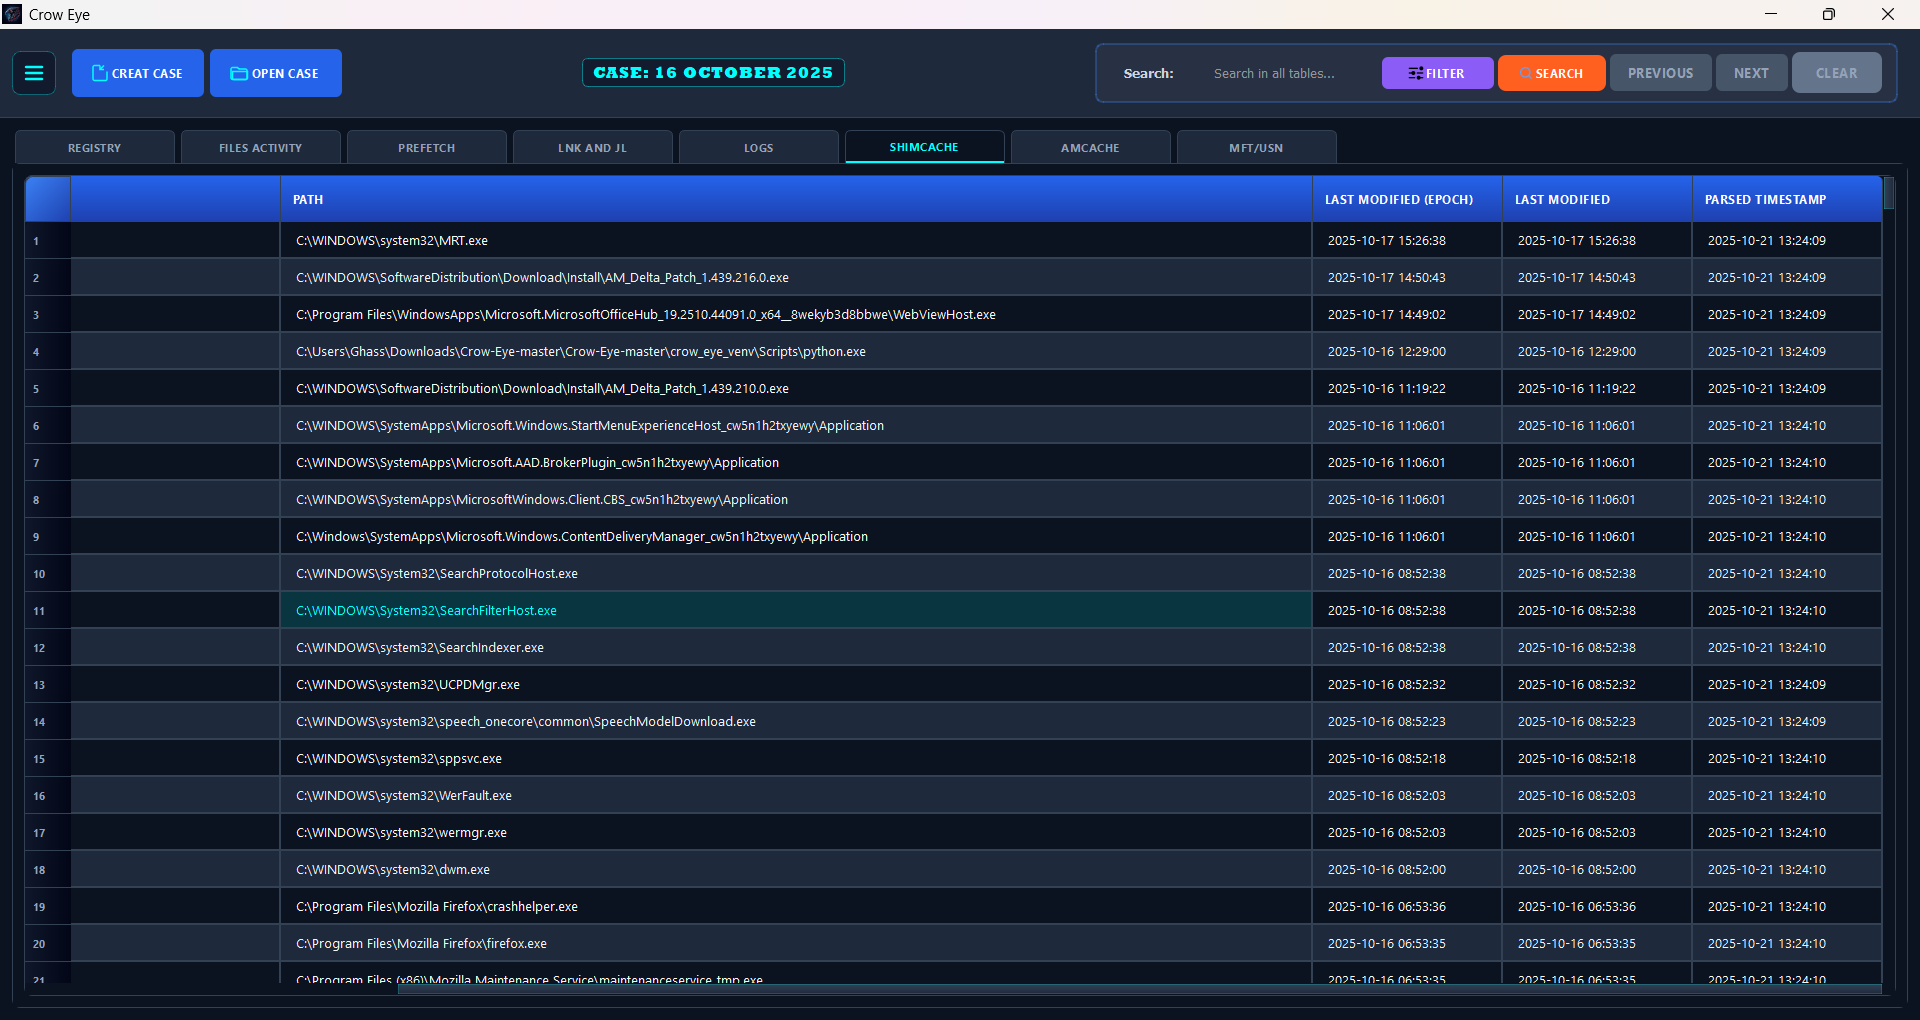 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
 radkawar/aws-firmware-dump
Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 cristianzsh/forensictools
Collection of forensic tools
 lazza/recuperabit
A tool for forensic file system reconstruction.