
foremost
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
data-recoverydigital-forensicsdisk-forensics+2
378
korczis/foremostFile carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 libyal/libqcow
Library and tools to access the QEMU Copy-On-Write (QCOW) image format
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 jschicht/logfileparser
Parser for $LogFile on NTFS
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
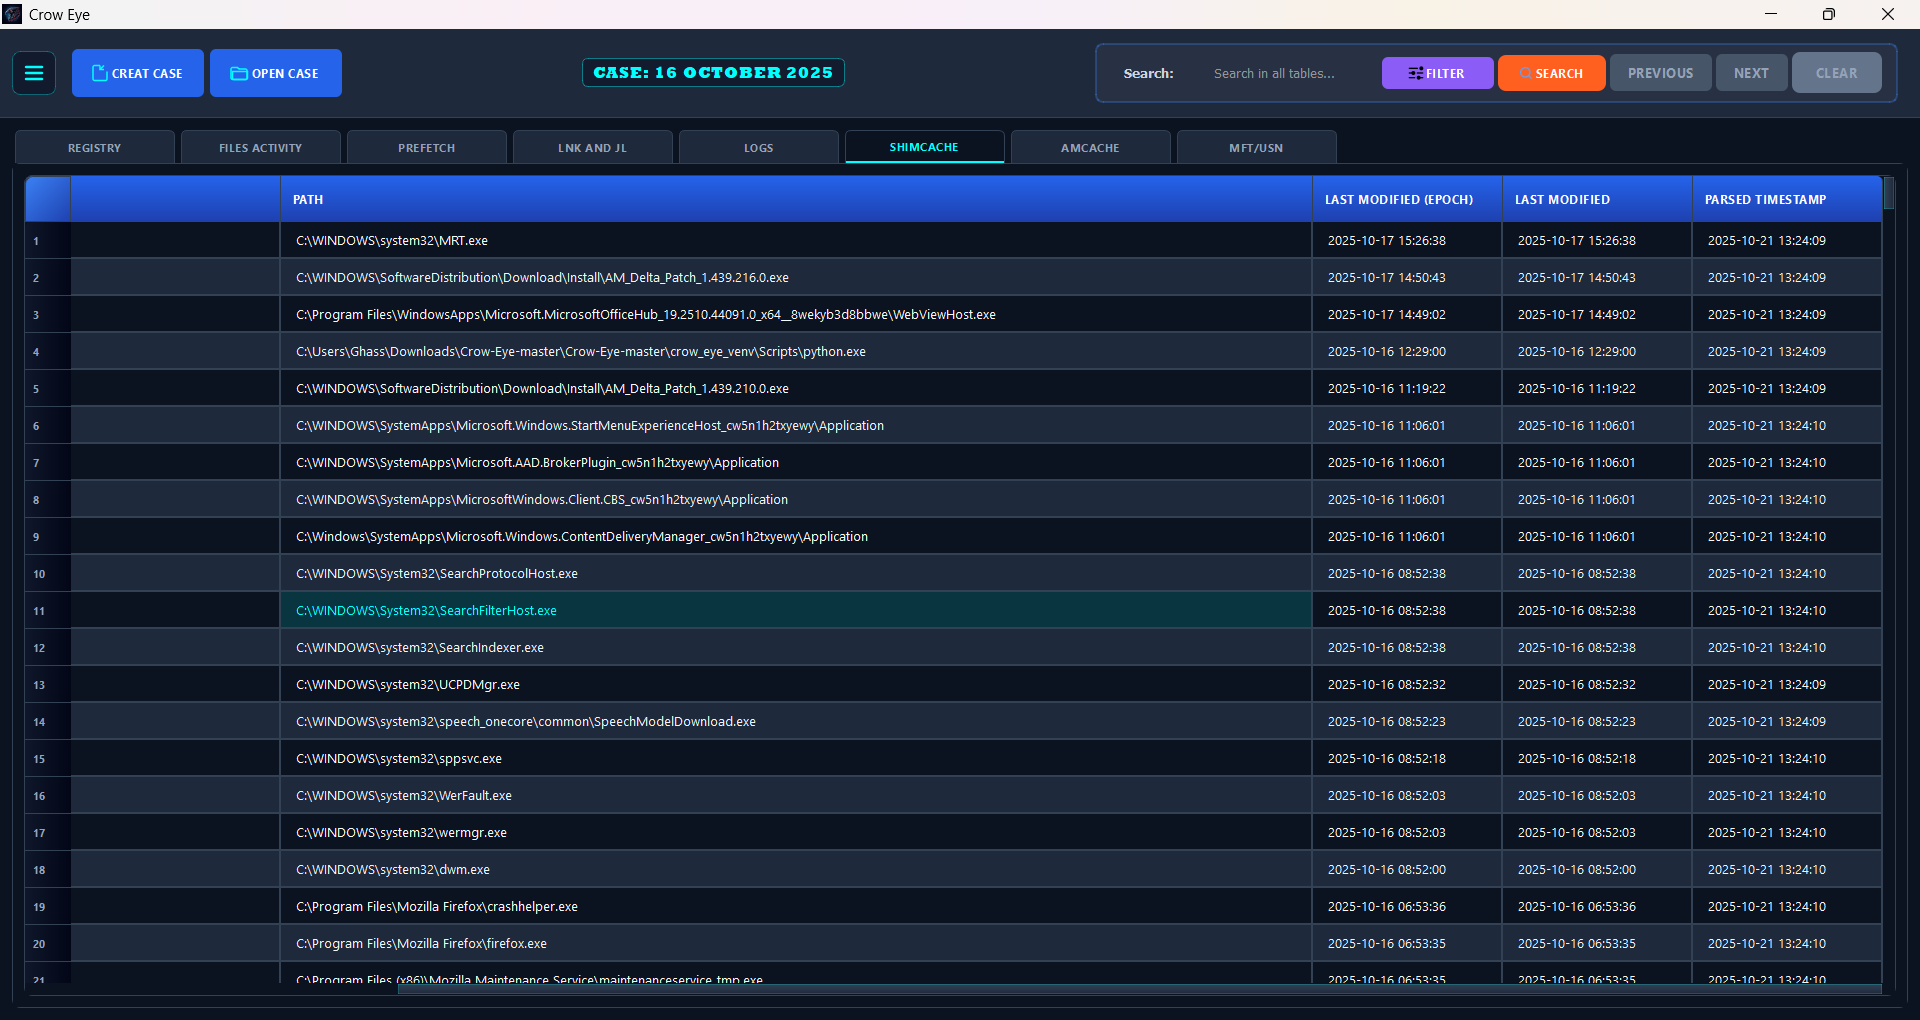 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
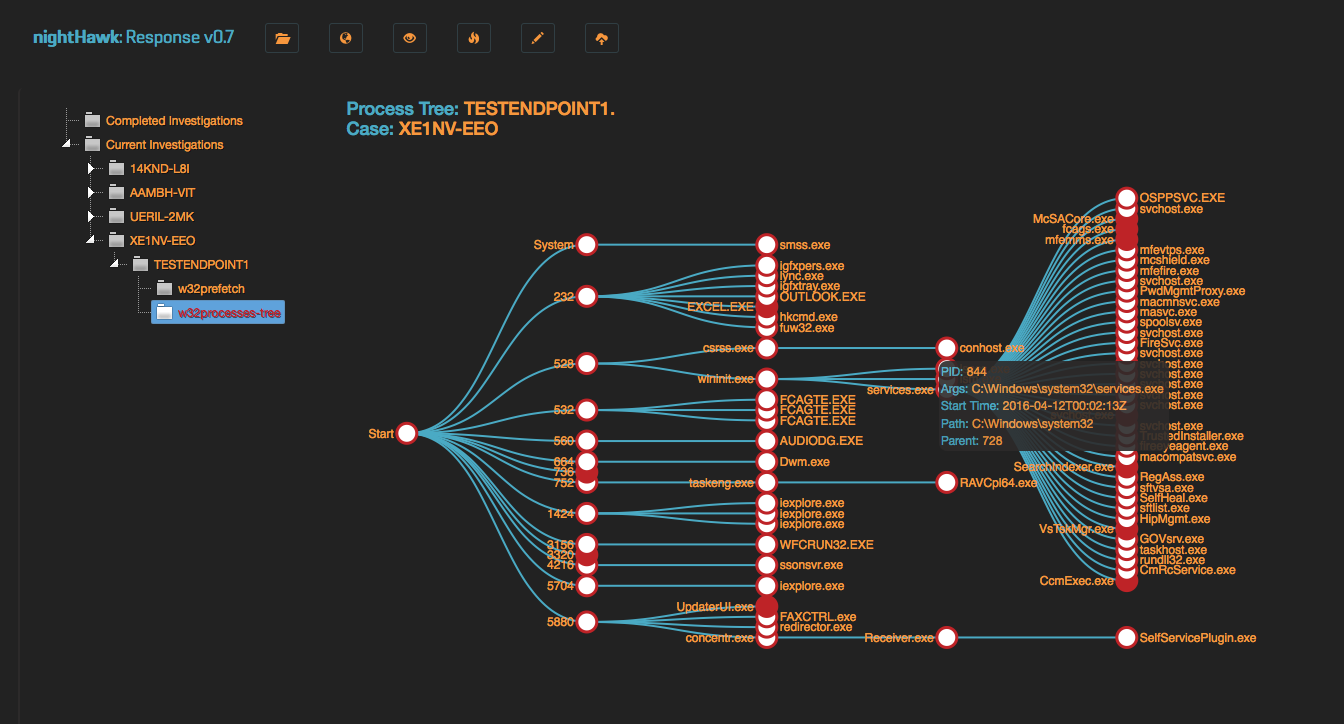 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
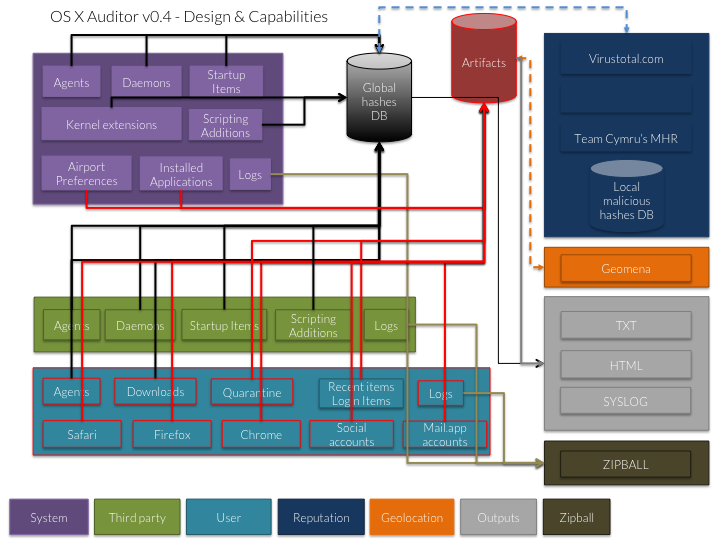 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
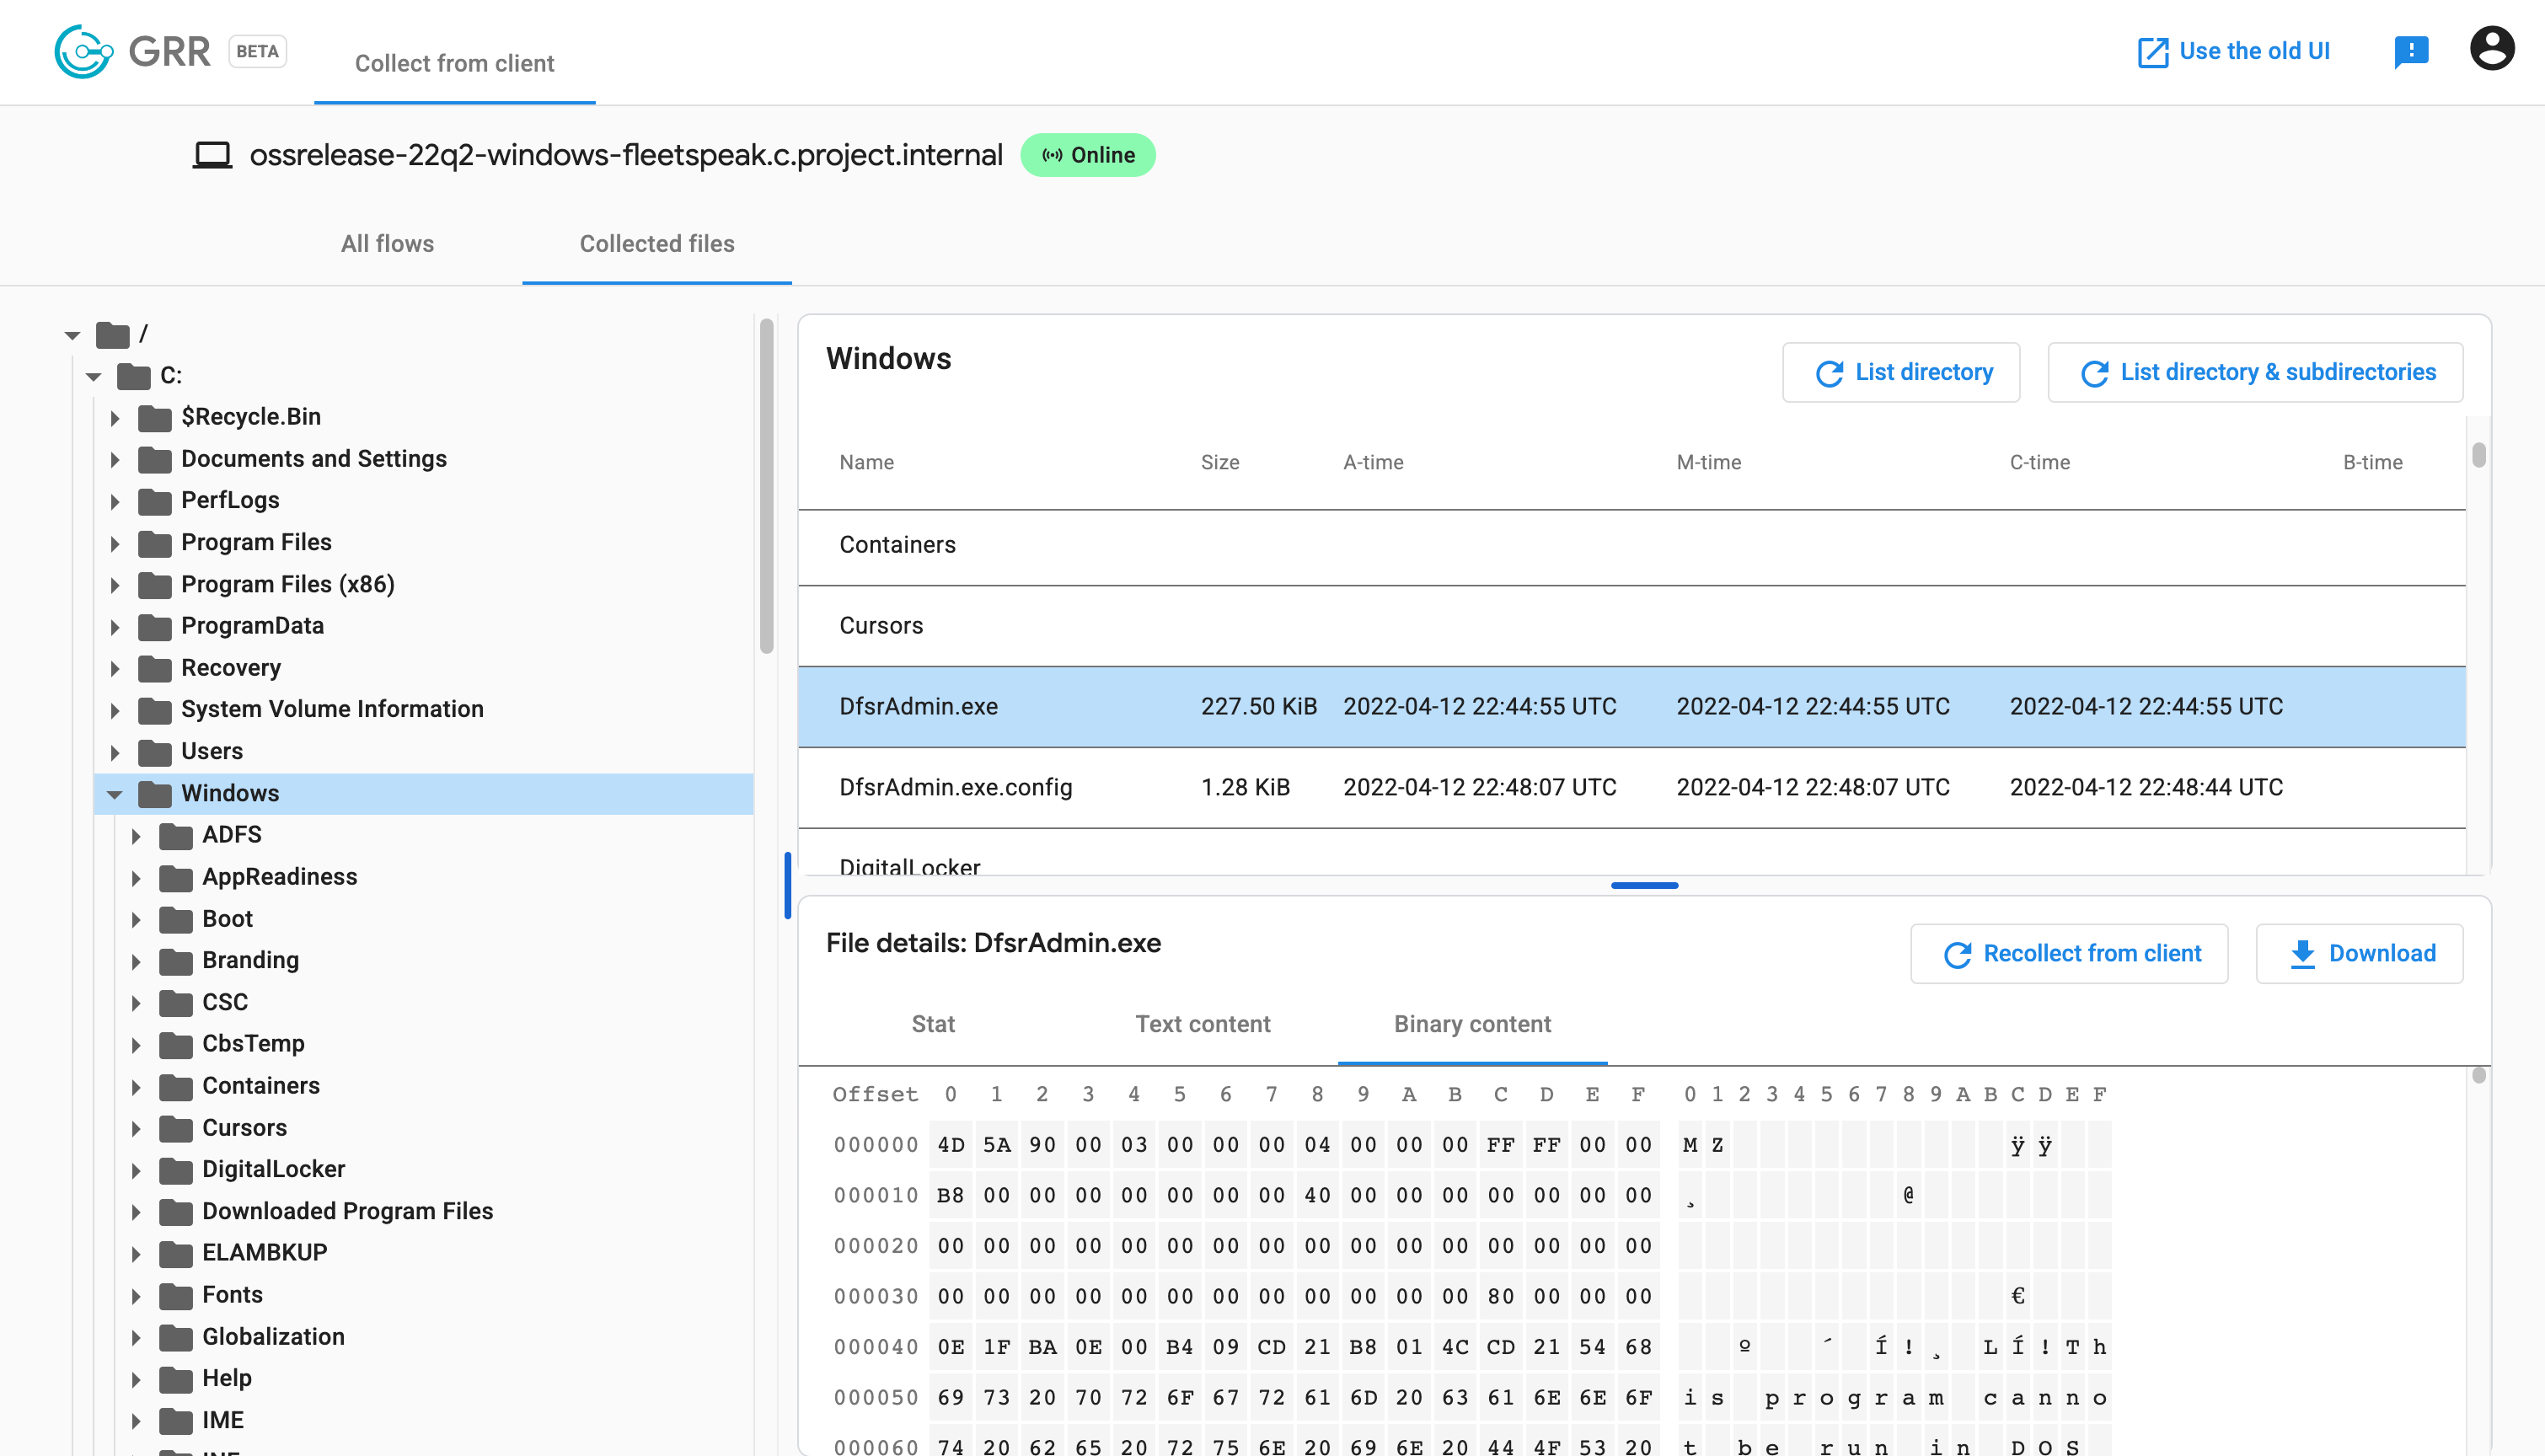 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
 jschicht/extractusnjrnl
Tool to extract the $UsnJrnl from an NTFS volume
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X