
bulk_extractor
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
data-recoverydigital-forensicsdisk-forensics+9
1.4k
simsong/bulk_extractorThis is the development tree. Production downloads are at:
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
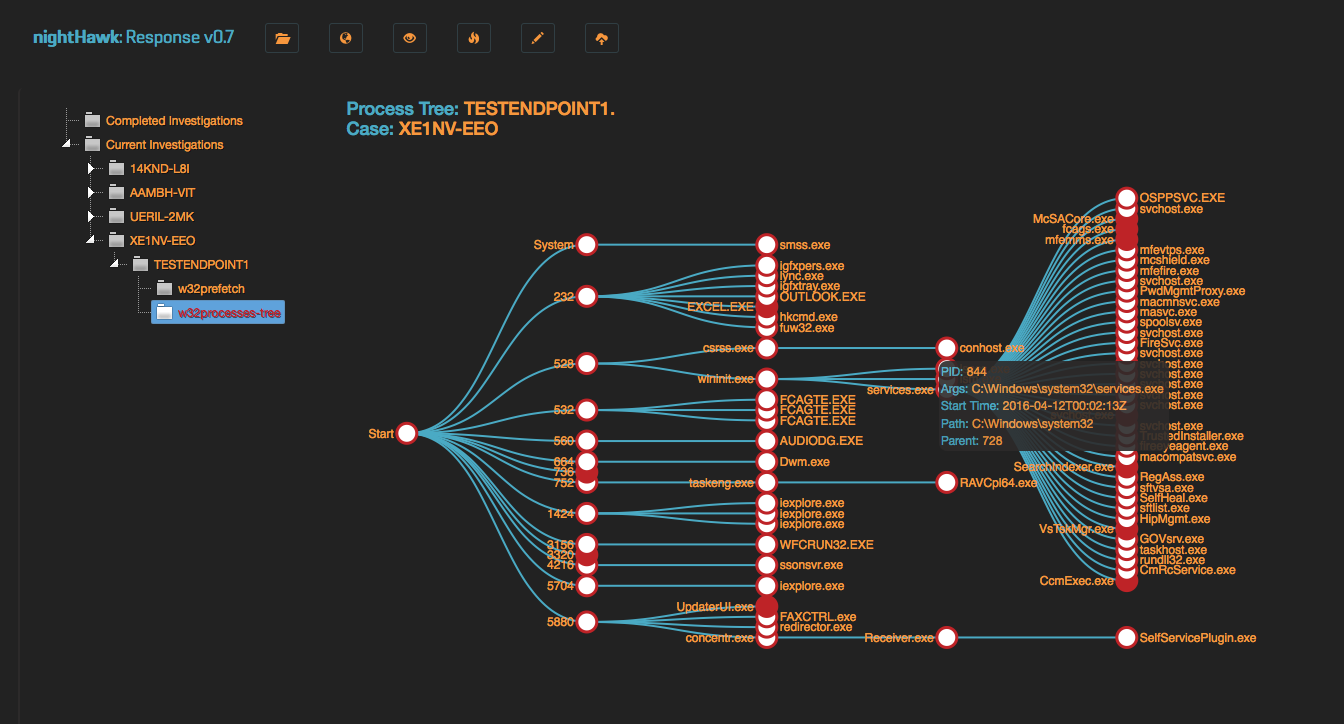 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
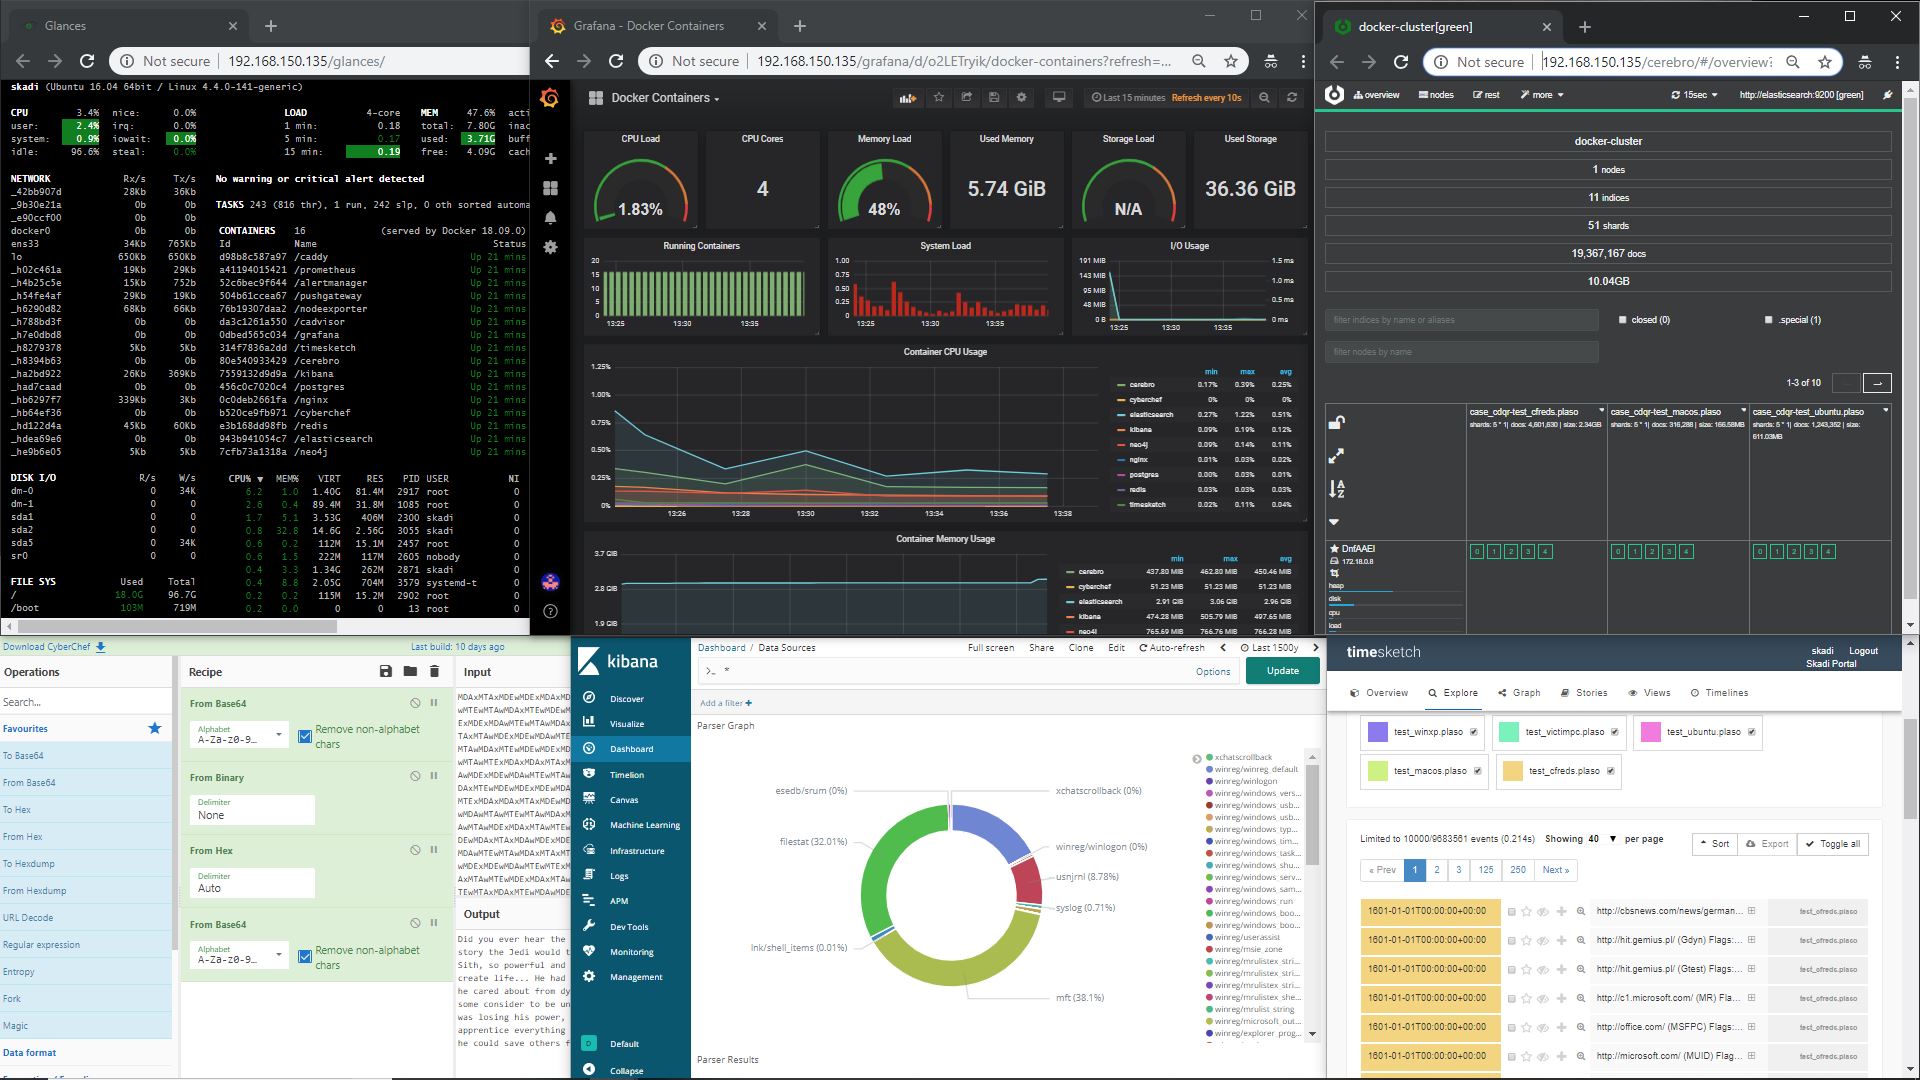 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X