


 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…

 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
 lazza/recuperabit
A tool for forensic file system reconstruction.
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 dmtrkovalenko/ffs
F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
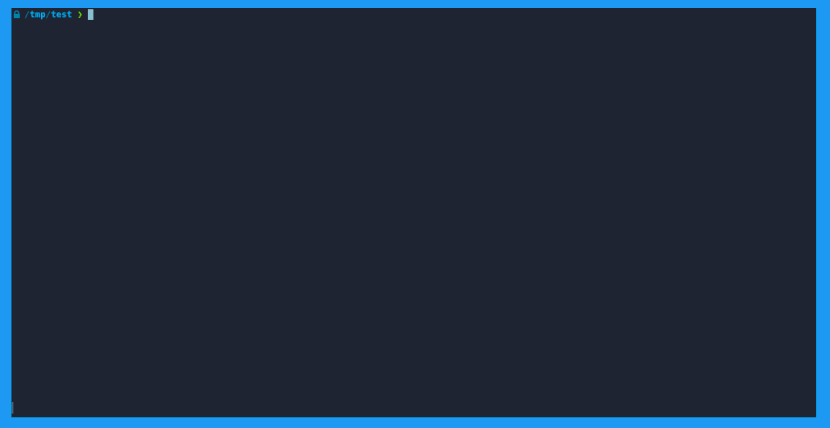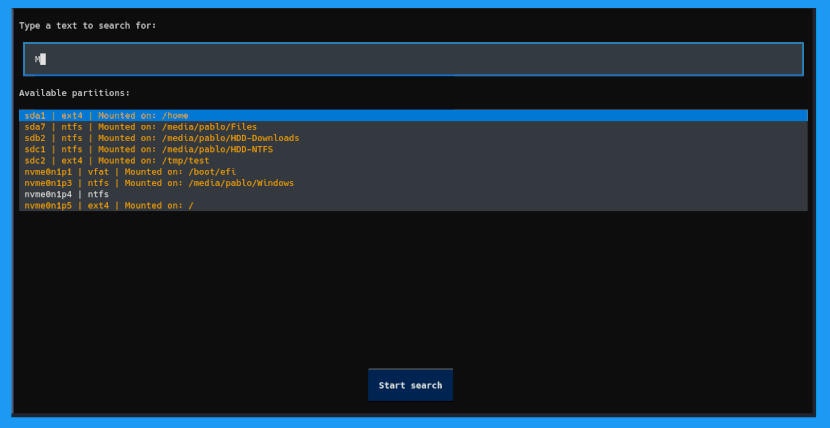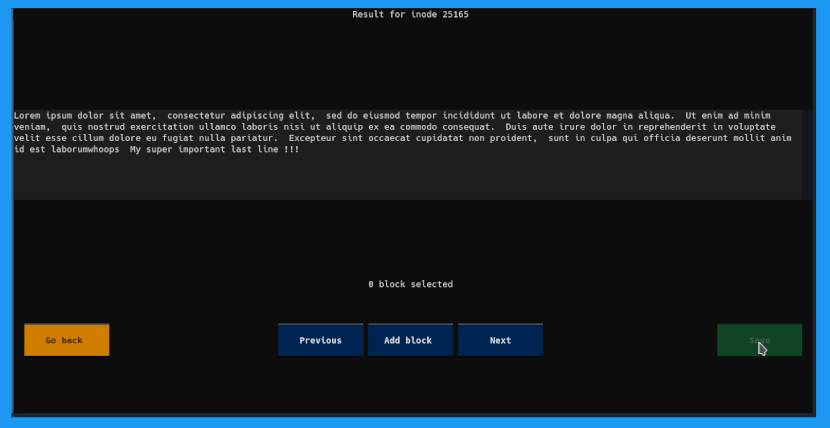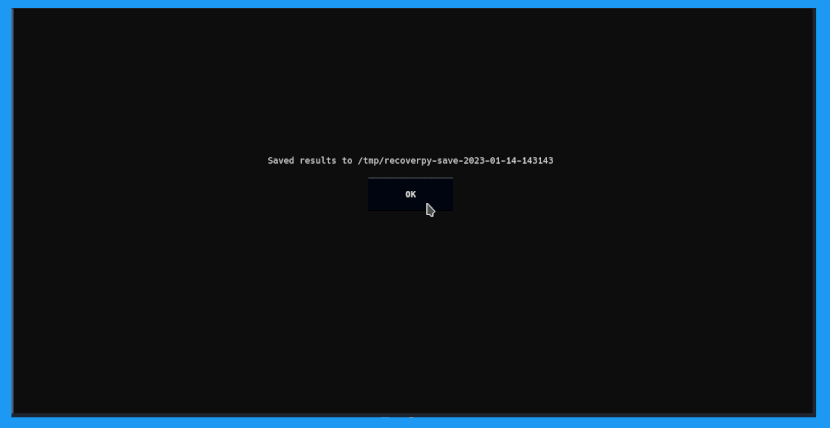 pablolec/recoverpy
Interactively find and recover deleted or :point_right: overwritten :point_left: files from your terminal
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…