
interrogate
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
binary-analysiscryptographydata-recovery+4
78
carmaa/interrogateInterrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 circl/factual-rules-generator
Generates YARA rules from installed software on a running OS to baseline known software and find similar installations across digital forensic…
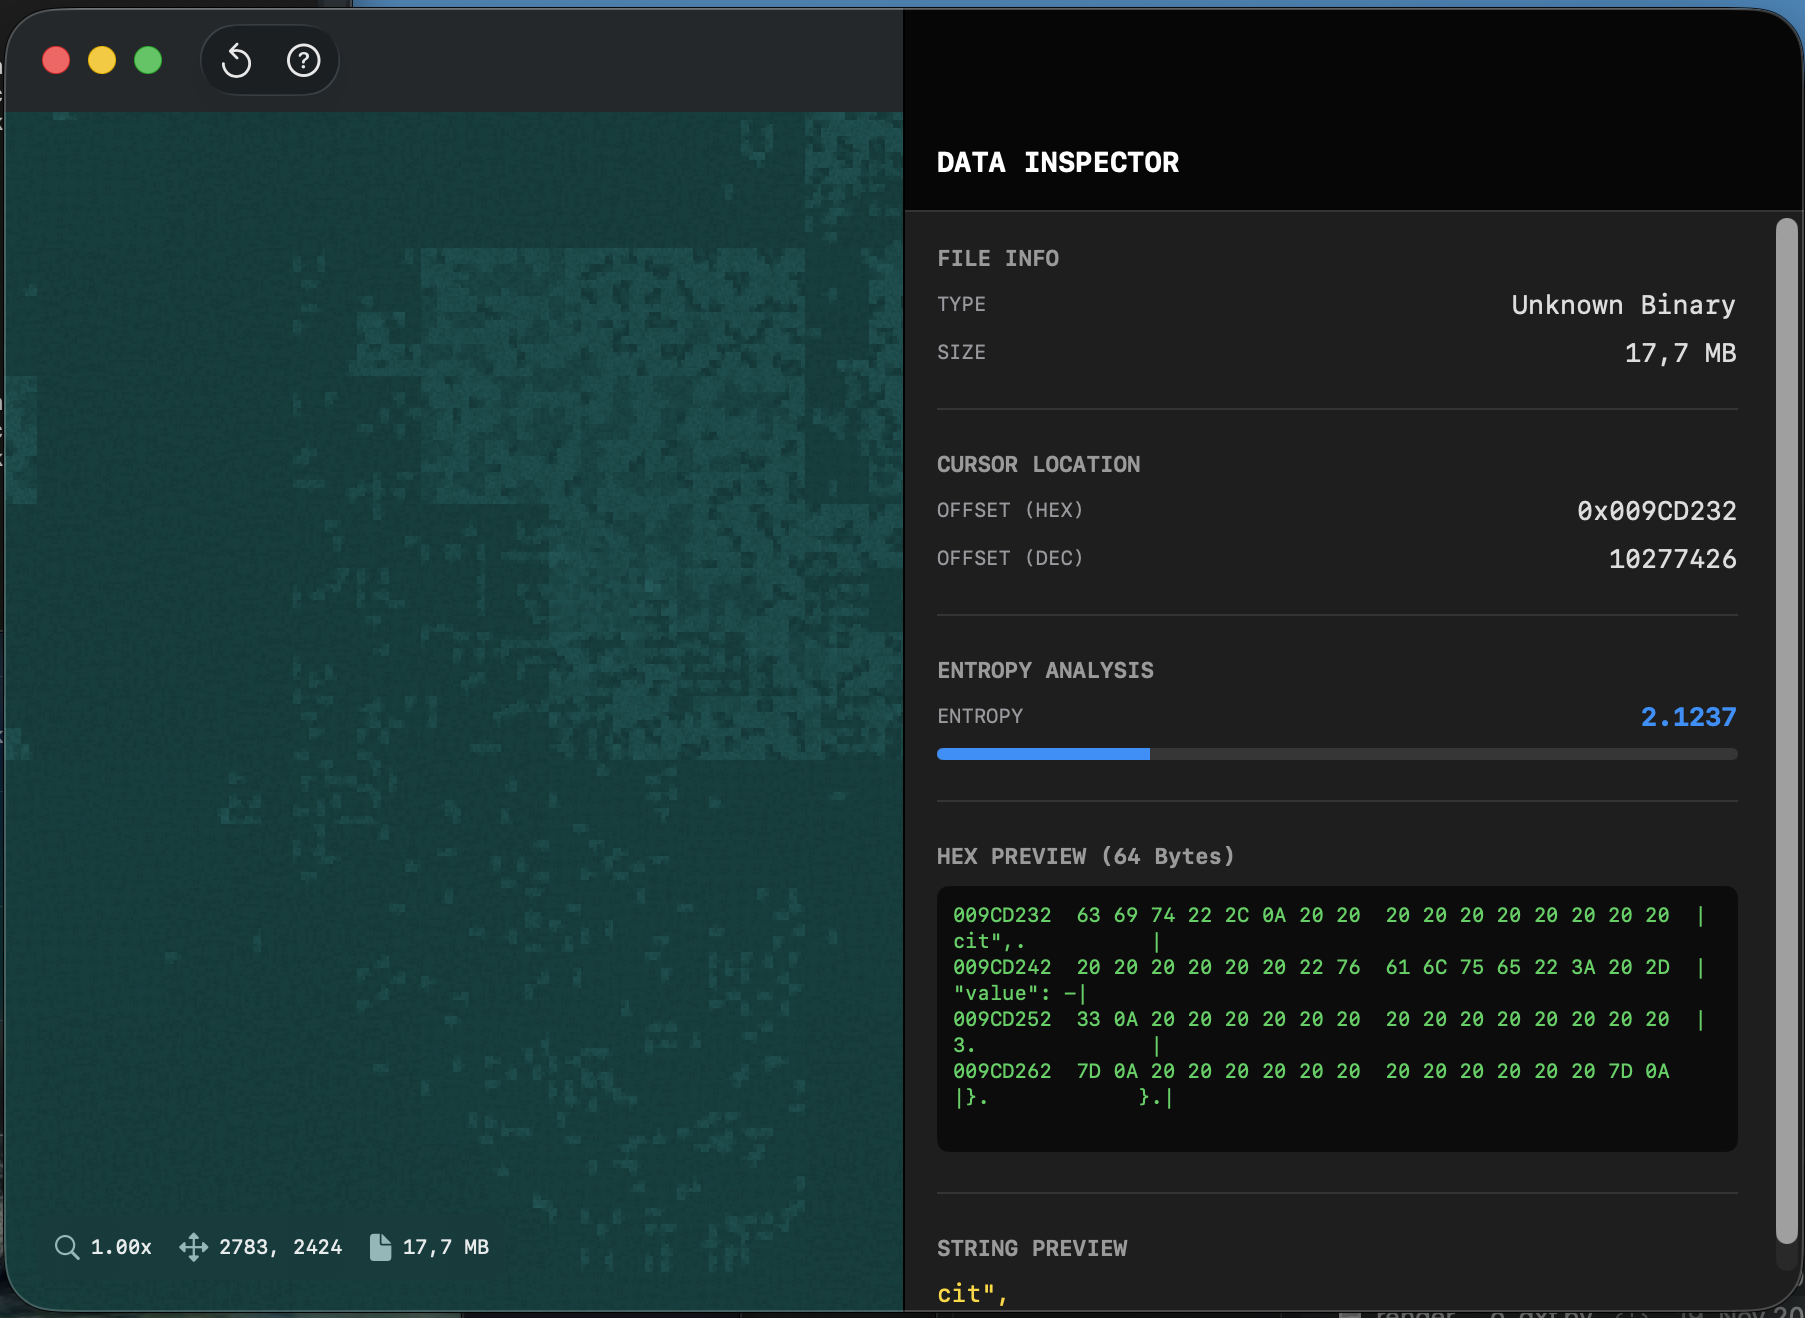 farukalpay/neurocore
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
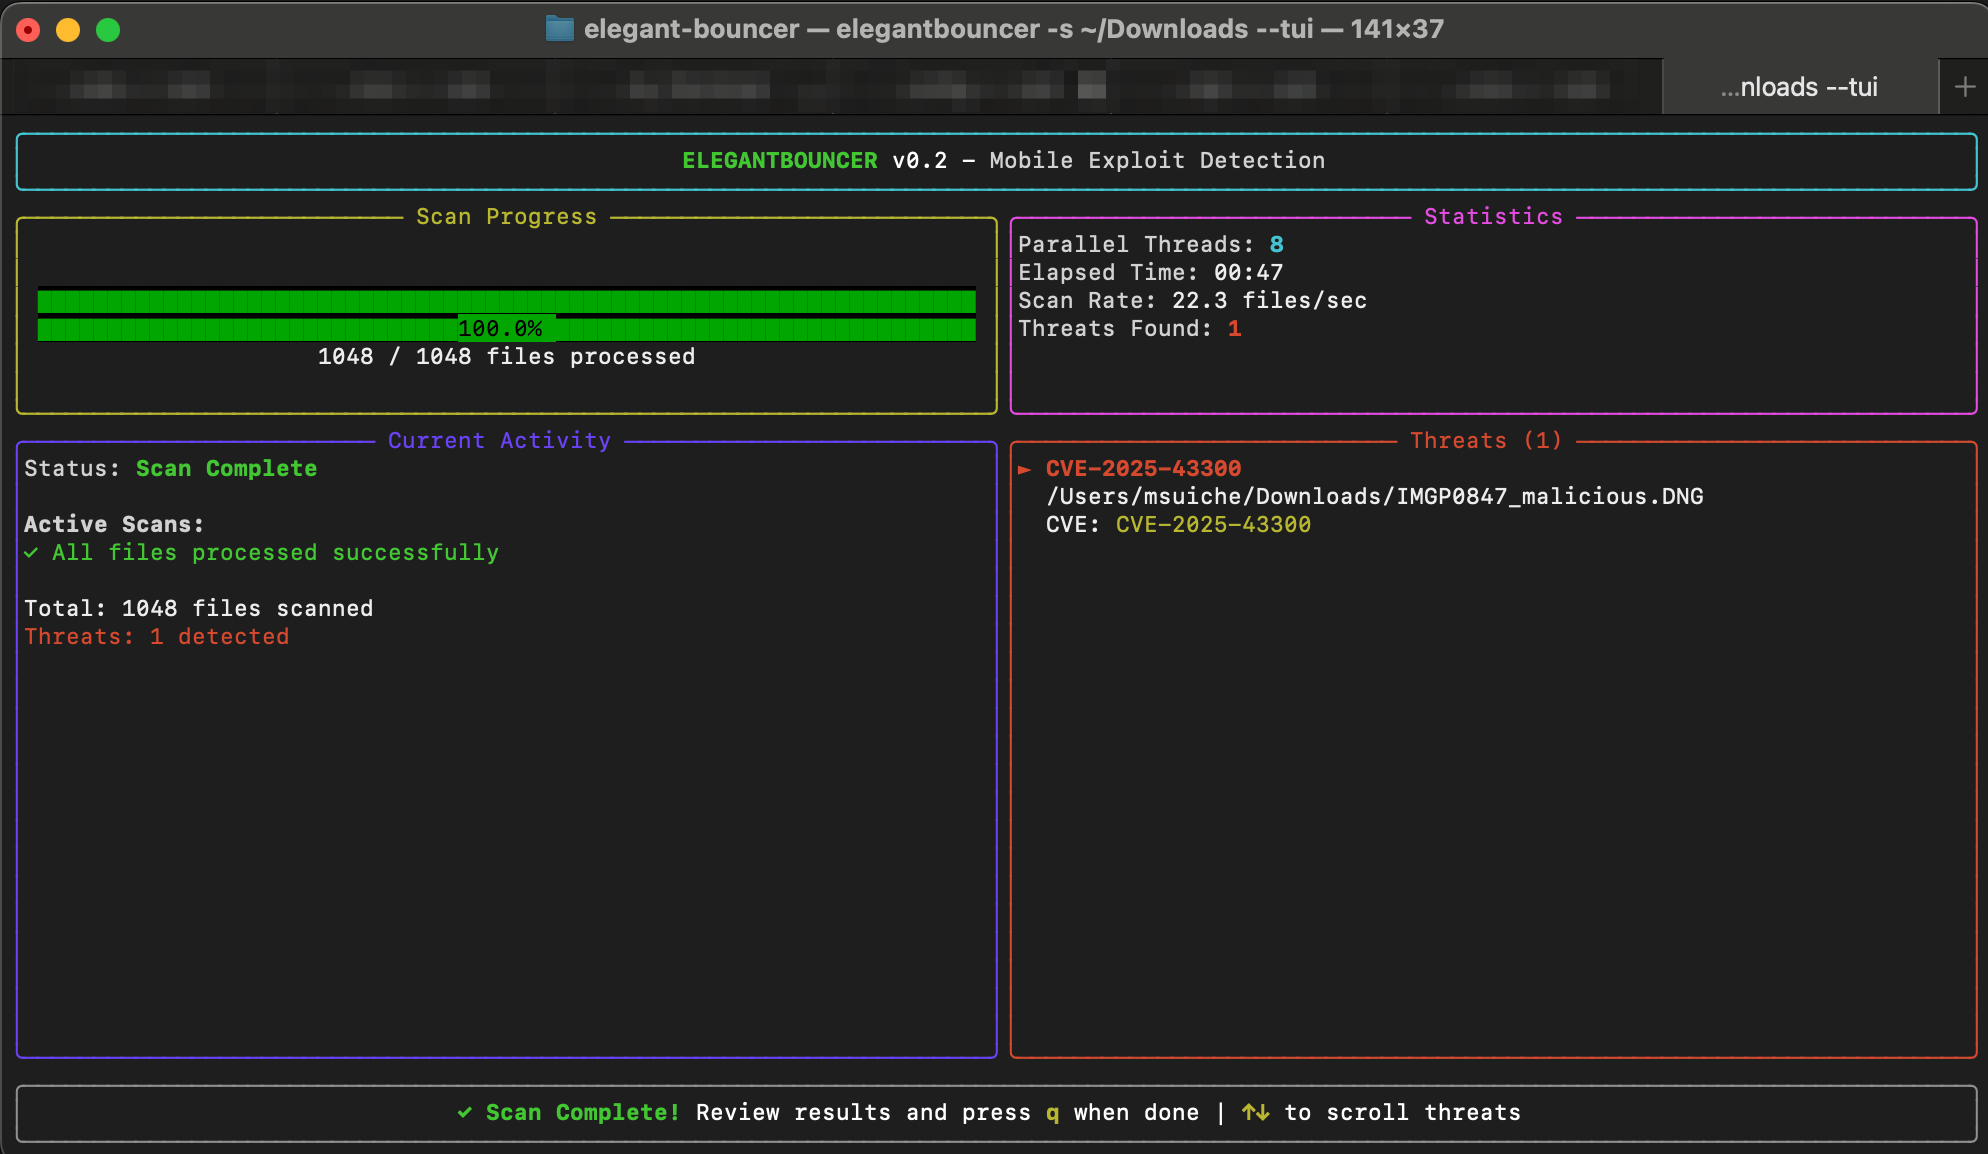 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 realitynet/ios_triage
Bash script to extract data from a "chekcra1ned" iOS device
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 jeffssh/cve-2021-30860
Collection of materials relating to FORCEDENTRY
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…