

ztewaste
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
android-securitydata-exfiltrationdigital-forensics+6
4
joshatticus/ztewasteExtract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.

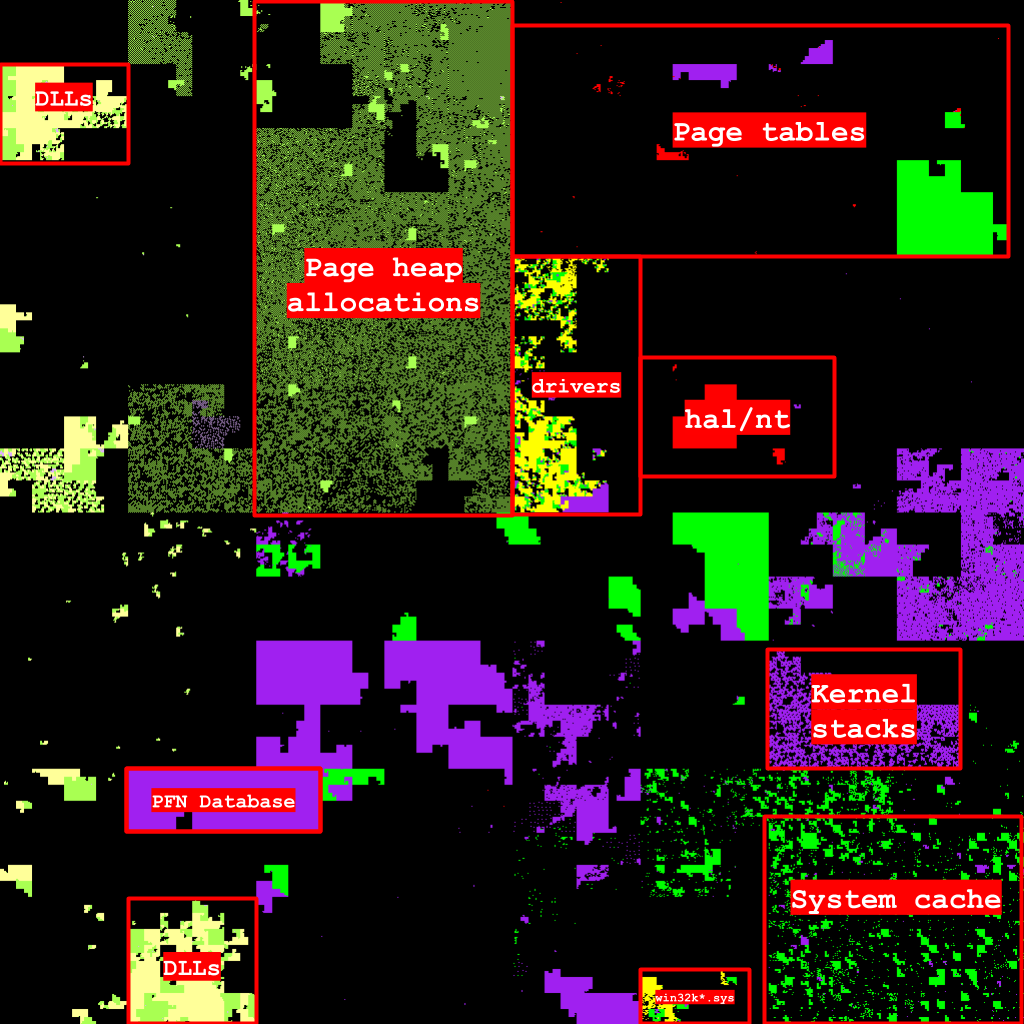 0vercl0k/clairvoyance
Visualize the virtual address space of a Windows process on a Hilbert curve.
 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
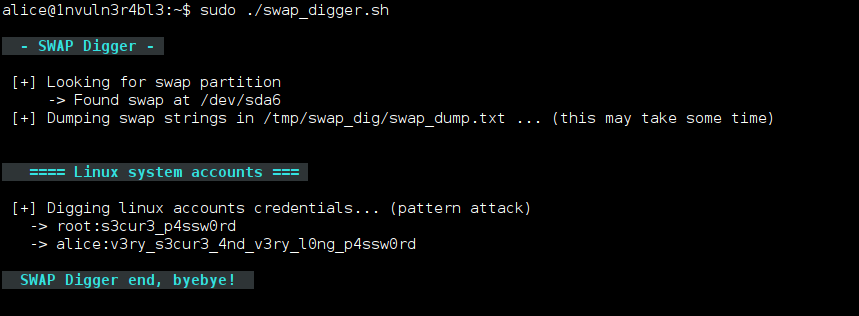 sevagas/swap_digger
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…
 guibacellar/tex
Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
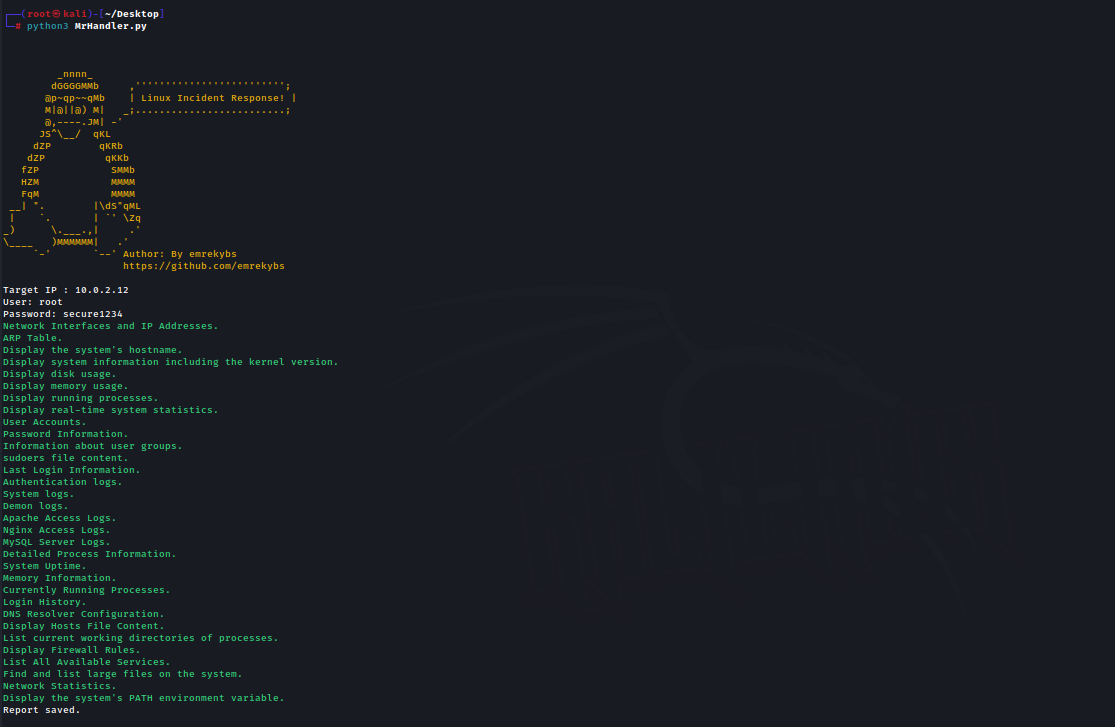 emrekybs/mrhandler
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
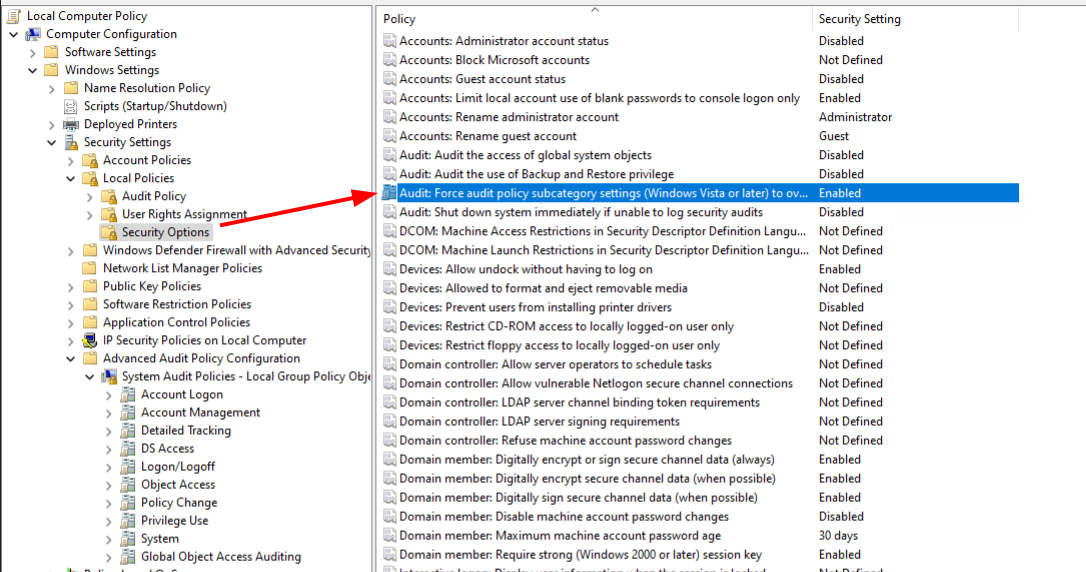 nextronsystems/evtx-baseline
A repository hosting example goodware evtx logs containing sample software installation and basic user interaction
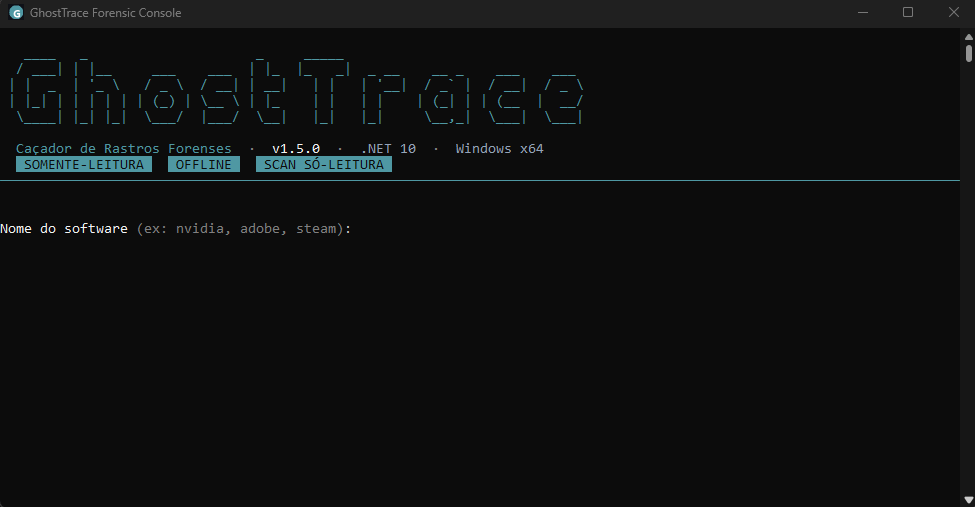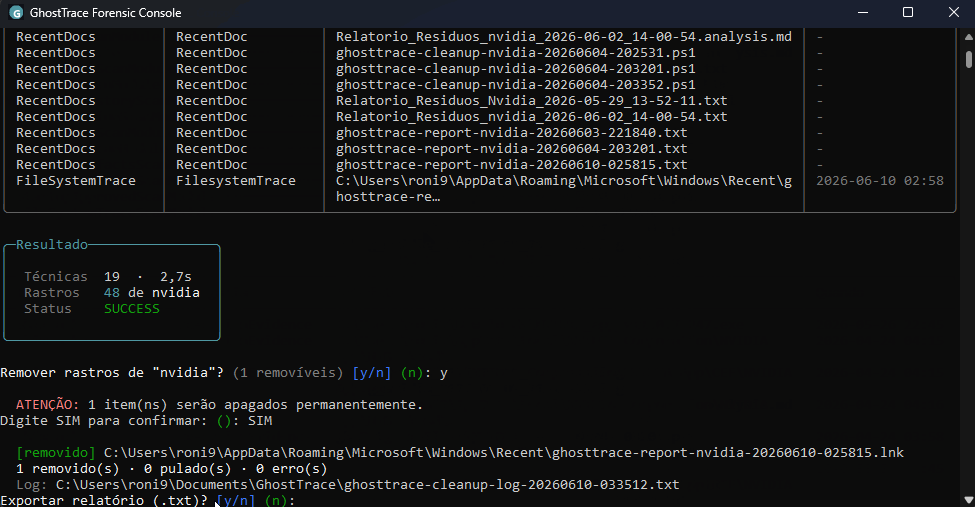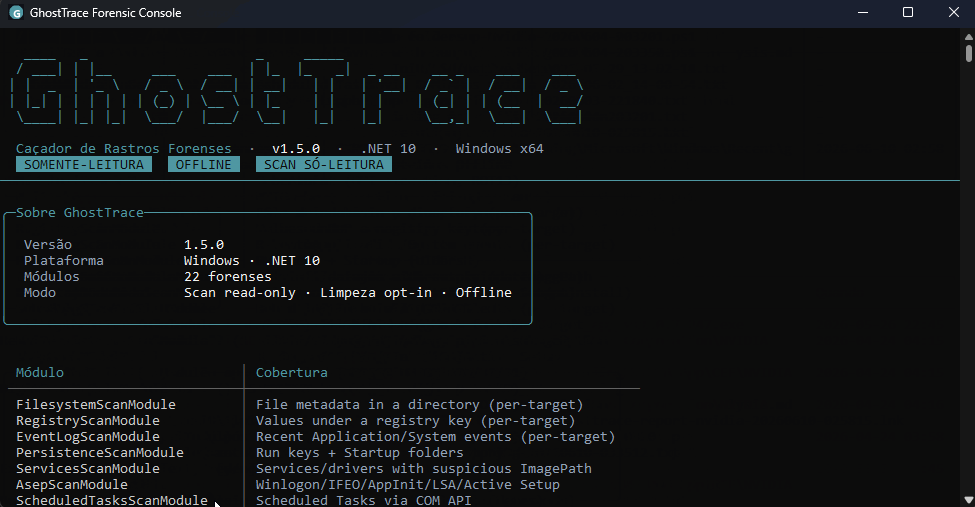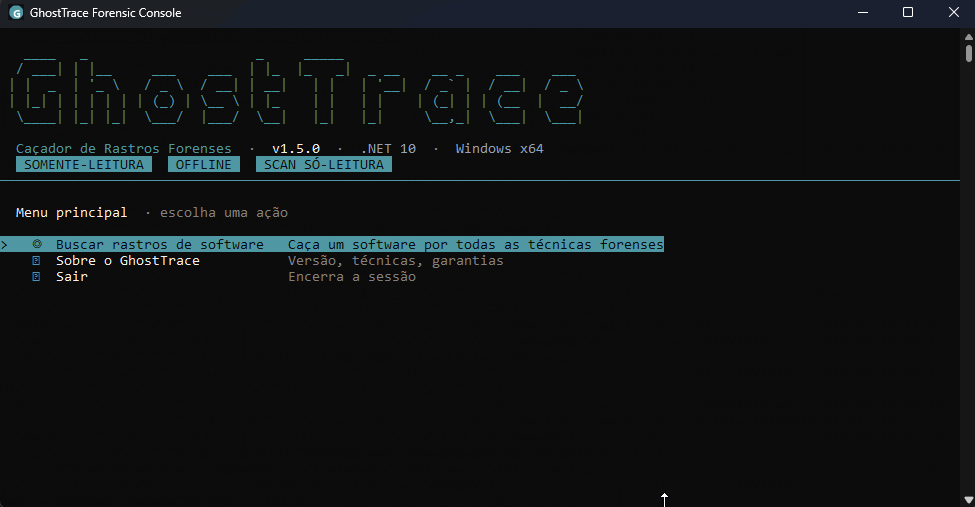 devzinh/ghosttrace
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 guillaumemeyer/watermarks-remover
A privacy-first app that strips AI watermarks from content you own.
 nongiach/sudo_inject
[Linux] Two Privilege Escalation techniques abusing sudo token
 alessandroz/lazagneforensic
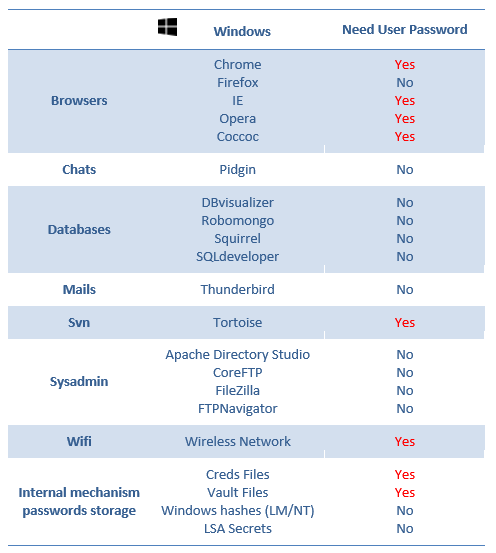
Windows passwords decryption from dump files