

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.2k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
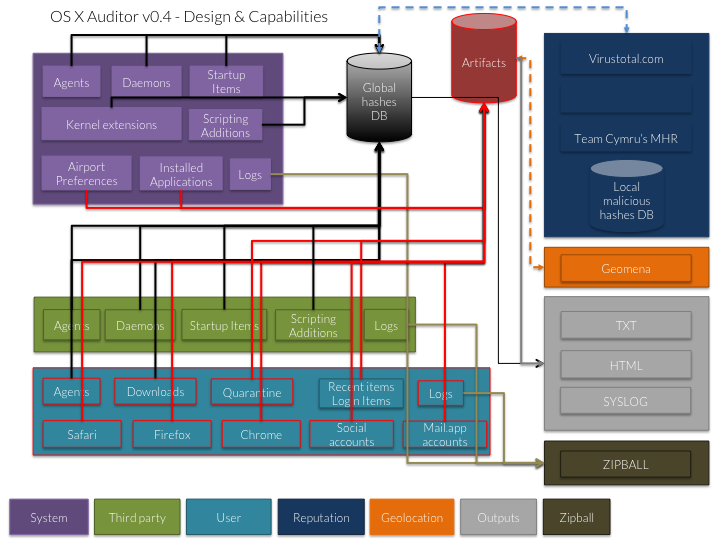 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
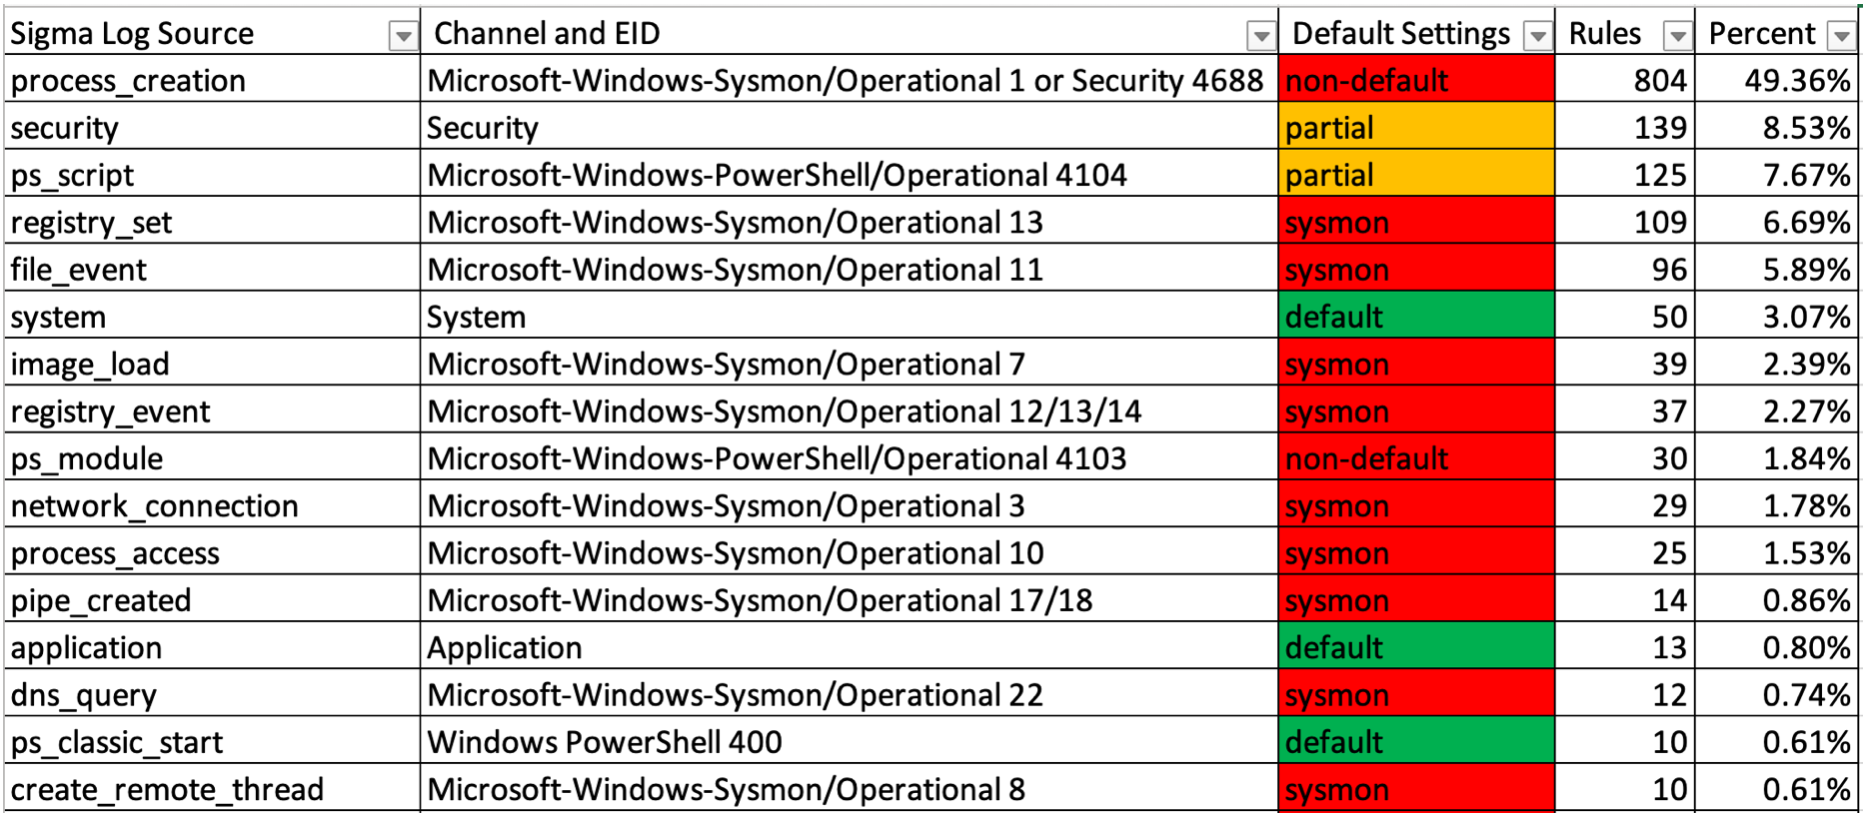 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 chainguard-dev/osquery-defense-kit
Production-ready detection & response queries for osquery
 korben00/no-gdid
Read, understand and silence the Windows GDID device identifier (the ID that tracked a hacker through a VPN). Verified on a real Win11 VM. Honest: it…
 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.