
ParanoiDF
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
data-recoverydigital-forensicsencryption-decryption-tools+6
112
patrickdw123/paranoidfParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
 opensourcesec/cirtkit
Tools for the Computer Incident Response Team :computer:
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 themittenmac/truetree
A command line tool for pstree-like output on macOS with additional pid capturing capabilities
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing
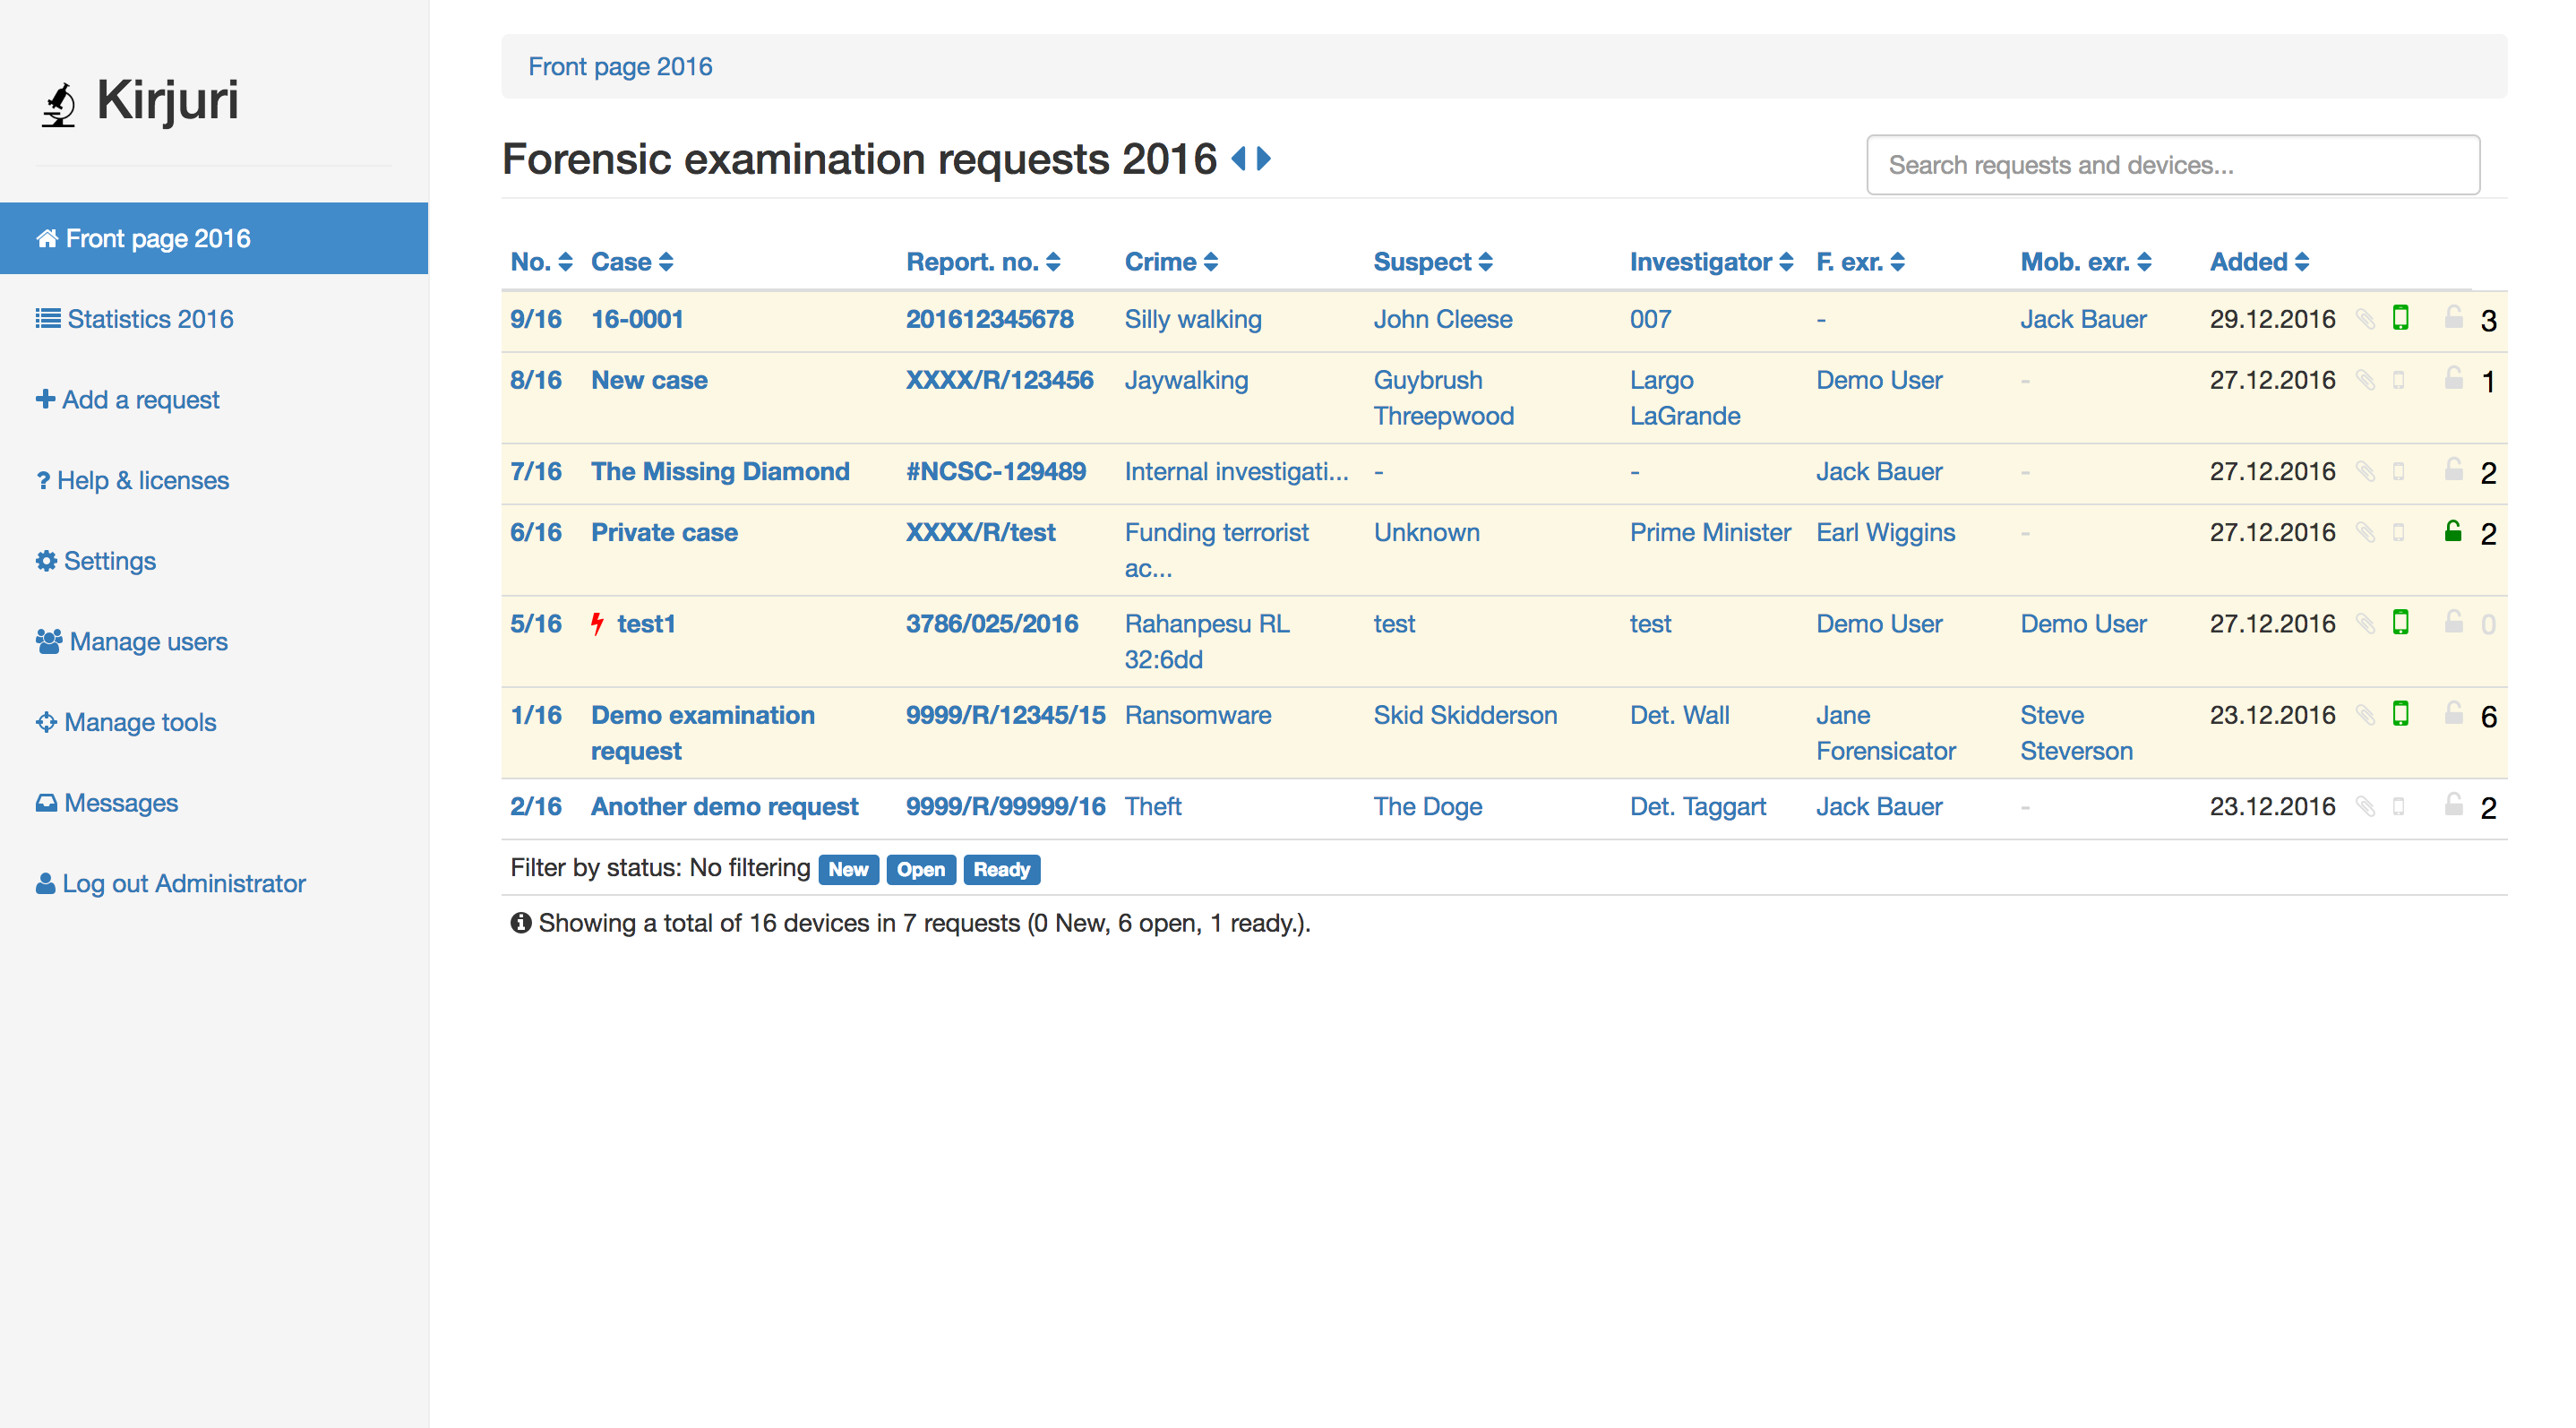 anttikurittu/kirjuri
Kirjuri is a web application for managing cases and physical forensic evidence items.
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework