
Archived
pyrebox
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
binary-analysisdebuggersdigital-forensics+5
1.7k
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 synacktiv/sharker
A simple, reliable and reasonably fast network capture analyzer.
 robindavid/lsb-steganography
Python program to steganography files into images using the Least Significant Bit.
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
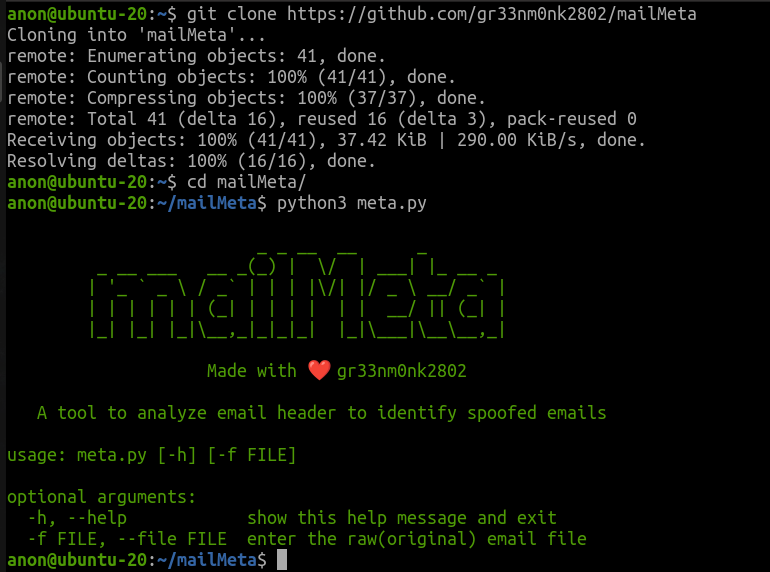 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
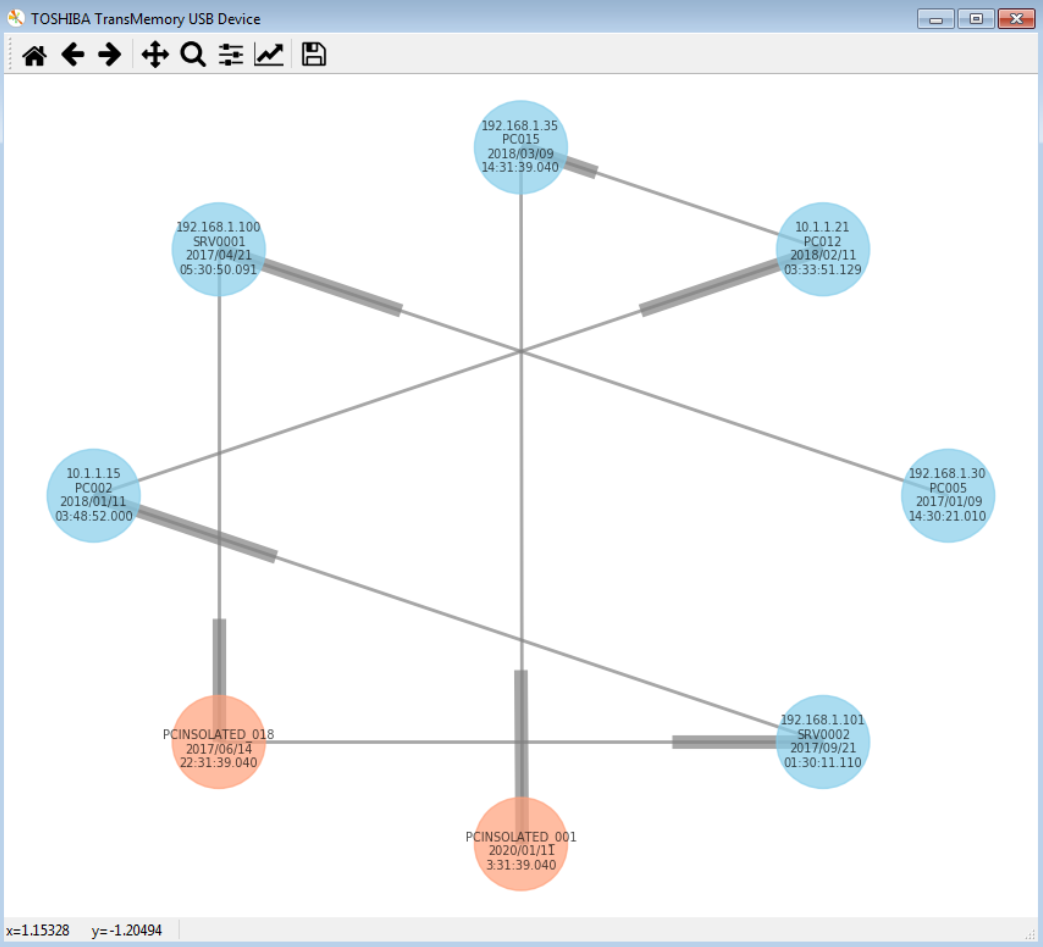 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…