
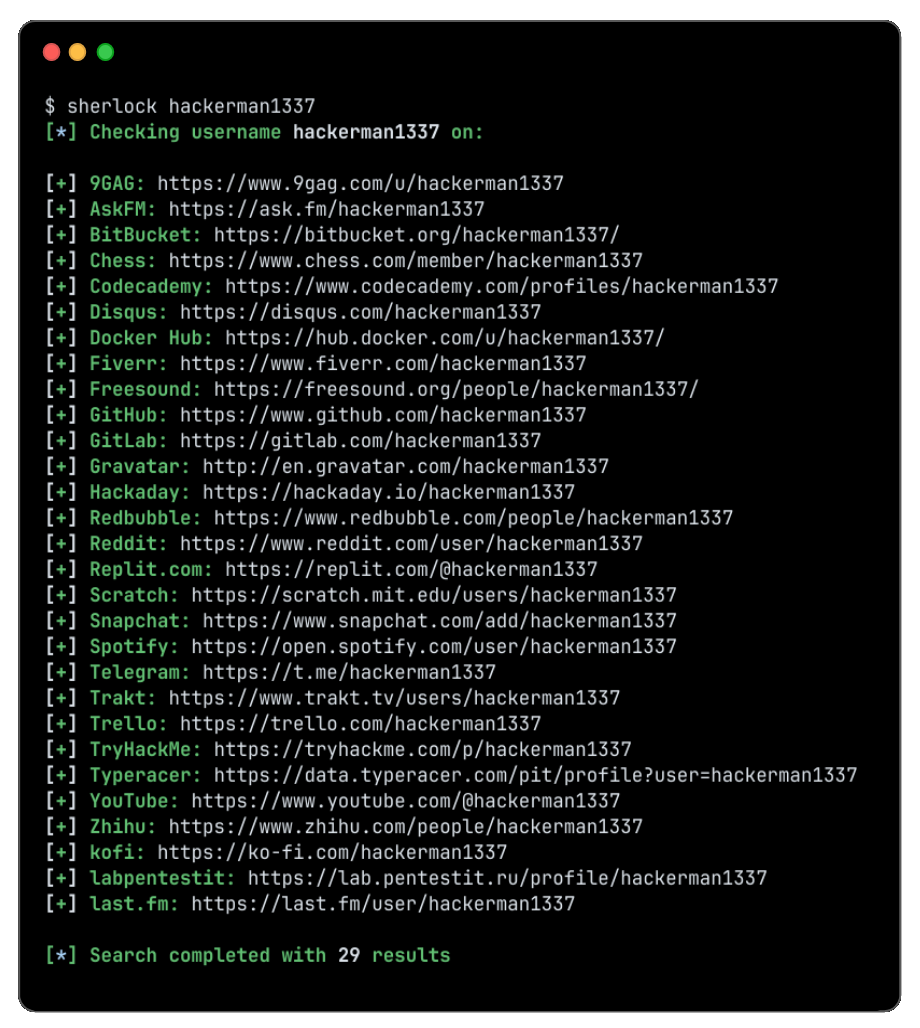
sherlock
 sherlock-project/sherlock
Hunt down social media accounts by username across social networks
digital-forensicsemail-harvestingforensics+11
93.8k14 days ago
sherlock-project/sherlockHunt down social media accounts by username across social networks
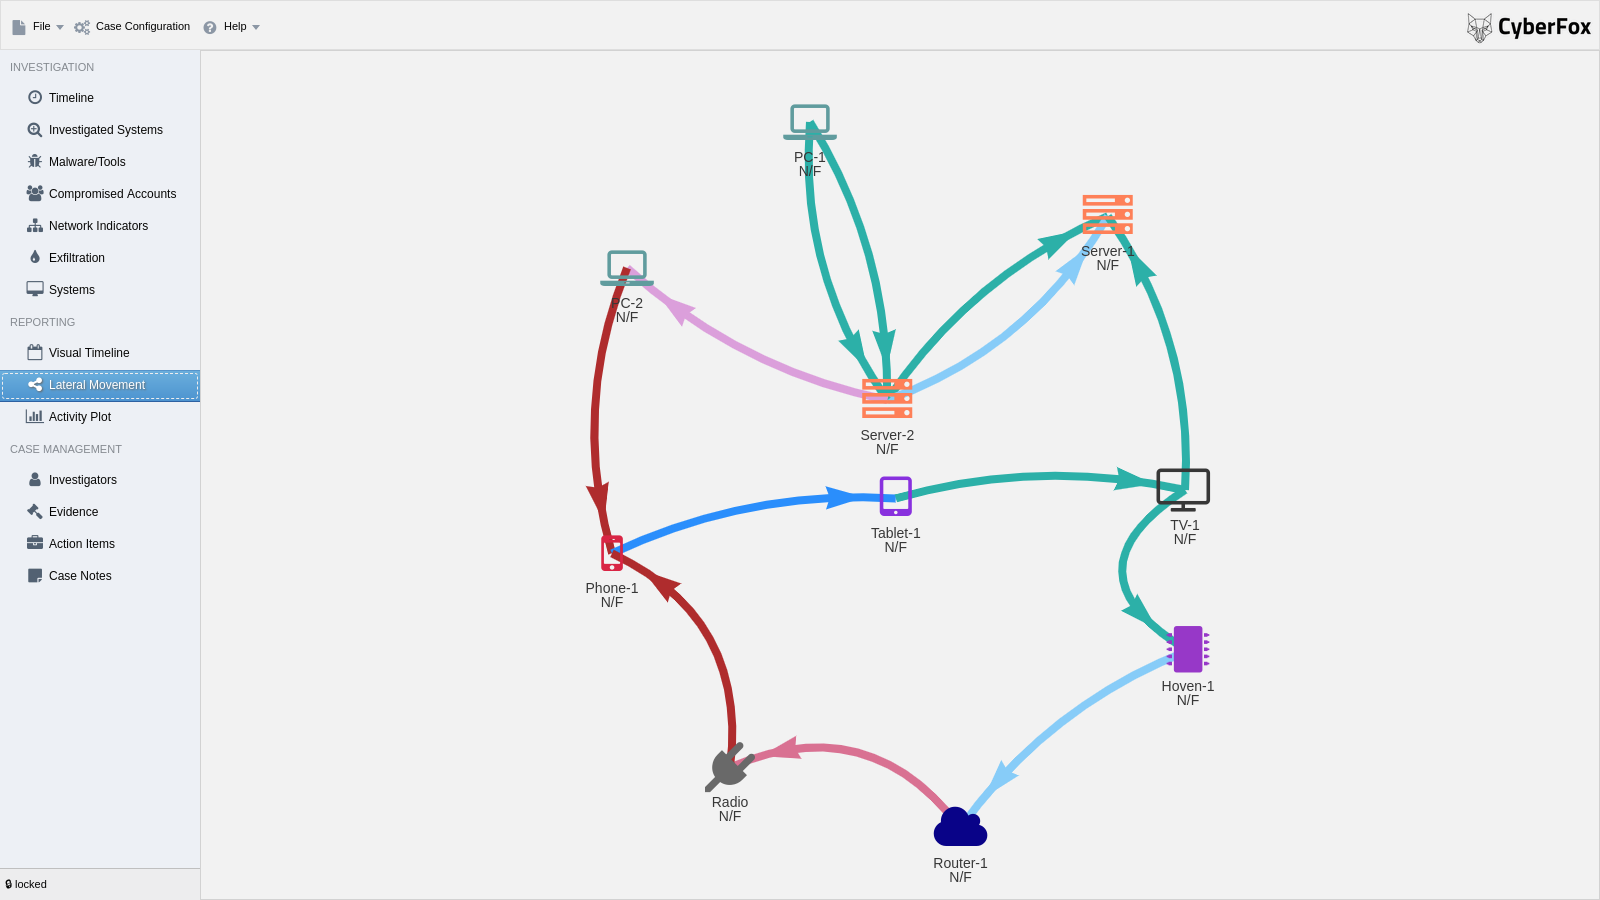 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
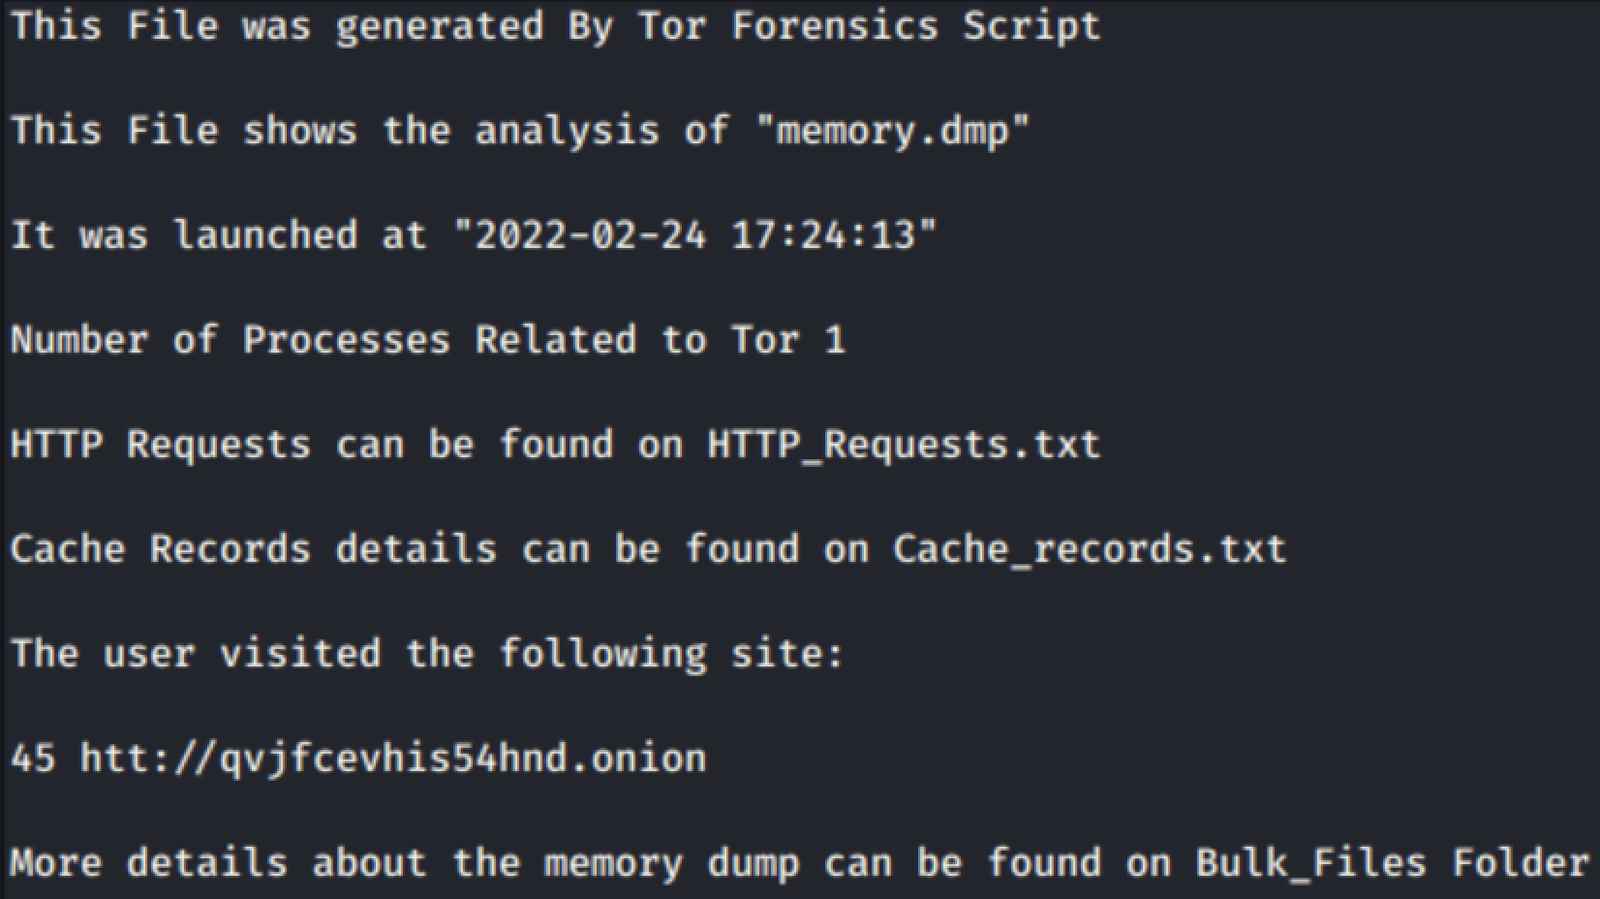 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
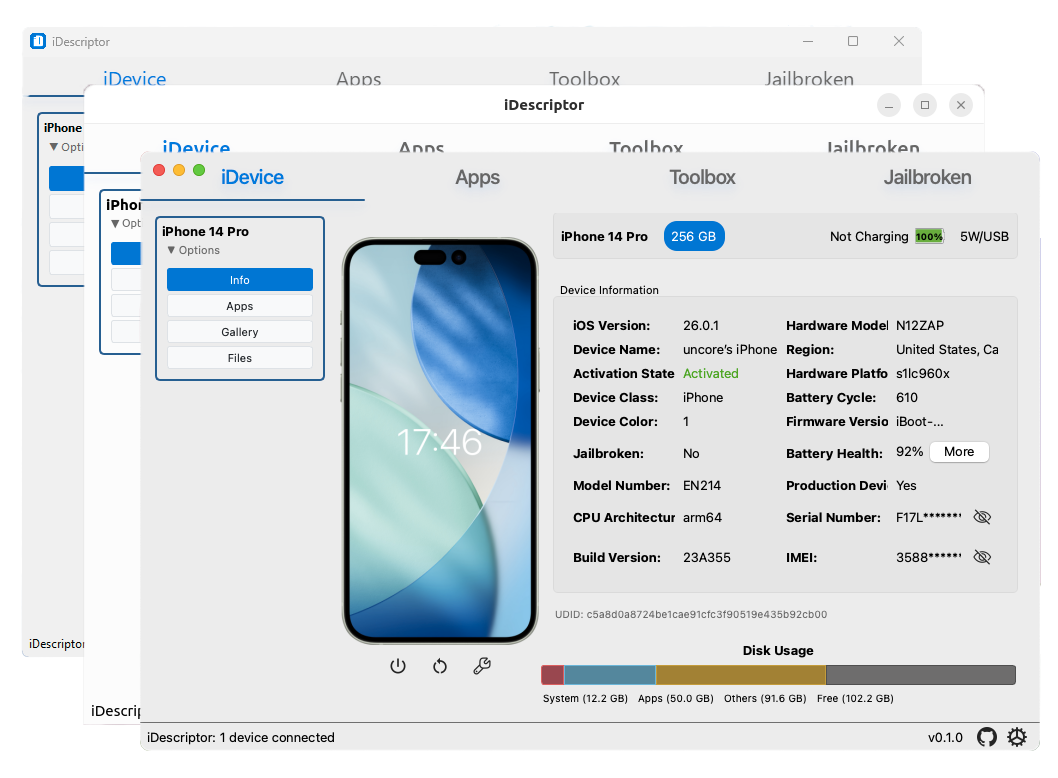 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
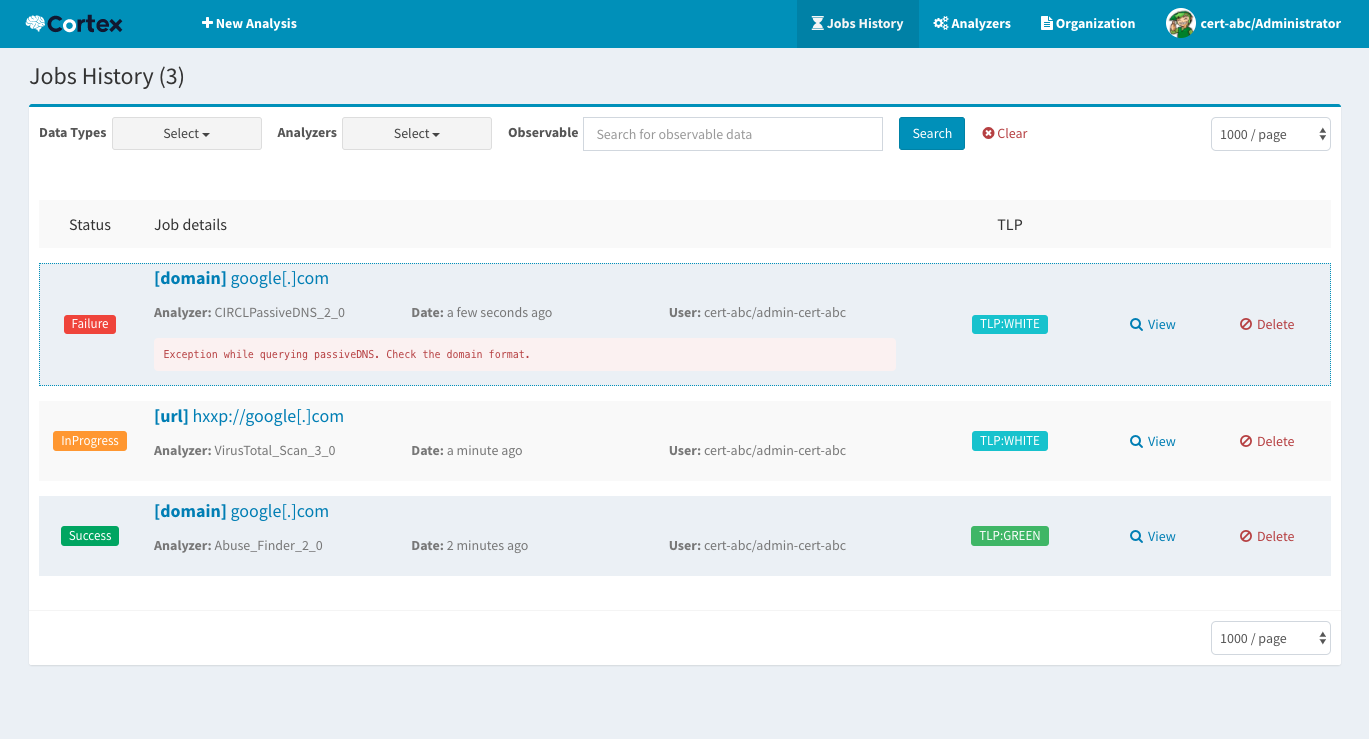 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 mr-r3b00t/crime-mapper
A tool for mapping cyber crime
 paul-tew/lifer
Windows link file (shortcuts) examiner

 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.

 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 andrewrathbun/dfirartifactmuseum
The goal of this repo is to archive artifacts from all versions of various OS's and categorizing them by type. This will help with artifact…
 spieglt/whatfiles
Log what files are accessed by any Linux process