Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
14 results
ParrotSec-Linux-Hardening-Project preview

ParrotSec-Linux-Hardening-Project

GitLabxe1phix/parrotlinux-public-kiosk-project

Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…

configuration-auditingdigital-forensicsforensics+3
3
1 month ago
Linpmem preview

Linpmem

GitHubvelocidex/linpmem

Linux kernel driver for physical memory acquisition, enabling read access to any physical address including reserved memory and memory holes, with…

digital-forensicsforensicsincident-response+1
1061 year ago
cve-2026-31431 preview

cve-2026-31431

GitHubvasyapokemon/cve-2026-31431

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…

curated-resourcesdigital-forensicseducation+8
4 months ago
mquire preview

mquire

GitHubtrailofbits/mquire

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.

binary-analysisdigital-forensicseducation+8
18512 days ago
copyfail-dfir preview

copyfail-dfir

GitHubledlight33/copyfail-dfir

Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.

digital-forensicseducationincident-response+2
14 months ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

binary-analysiscontainer-escapedata-recovery+7
101 month ago
LiME preview

LiME

GitHubjtsylve/lime

Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.

digital-forensicsforensicsincident-response+2
2.0k5 months ago
fim-ebpf preview

fim-ebpf

GitHubharshavmb/fim-ebpf

A lightweight eBPF program to monitor file creation and modification events on Linux. This tool leverages eBPF (Extended Berkeley Packet Filter) to…

defensive-toolsdigital-forensicsforensics+1
78 months ago
Persistnux preview

Persistnux

GitHubgo-lanz/persistnux

Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…

container-escapedigital-forensicseducation+7
32 months ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

debuggersdigital-forensicsdisk-forensics+7
252 months ago
kdmp-parser preview

kdmp-parser

GitHub0vercl0k/kdmp-parser

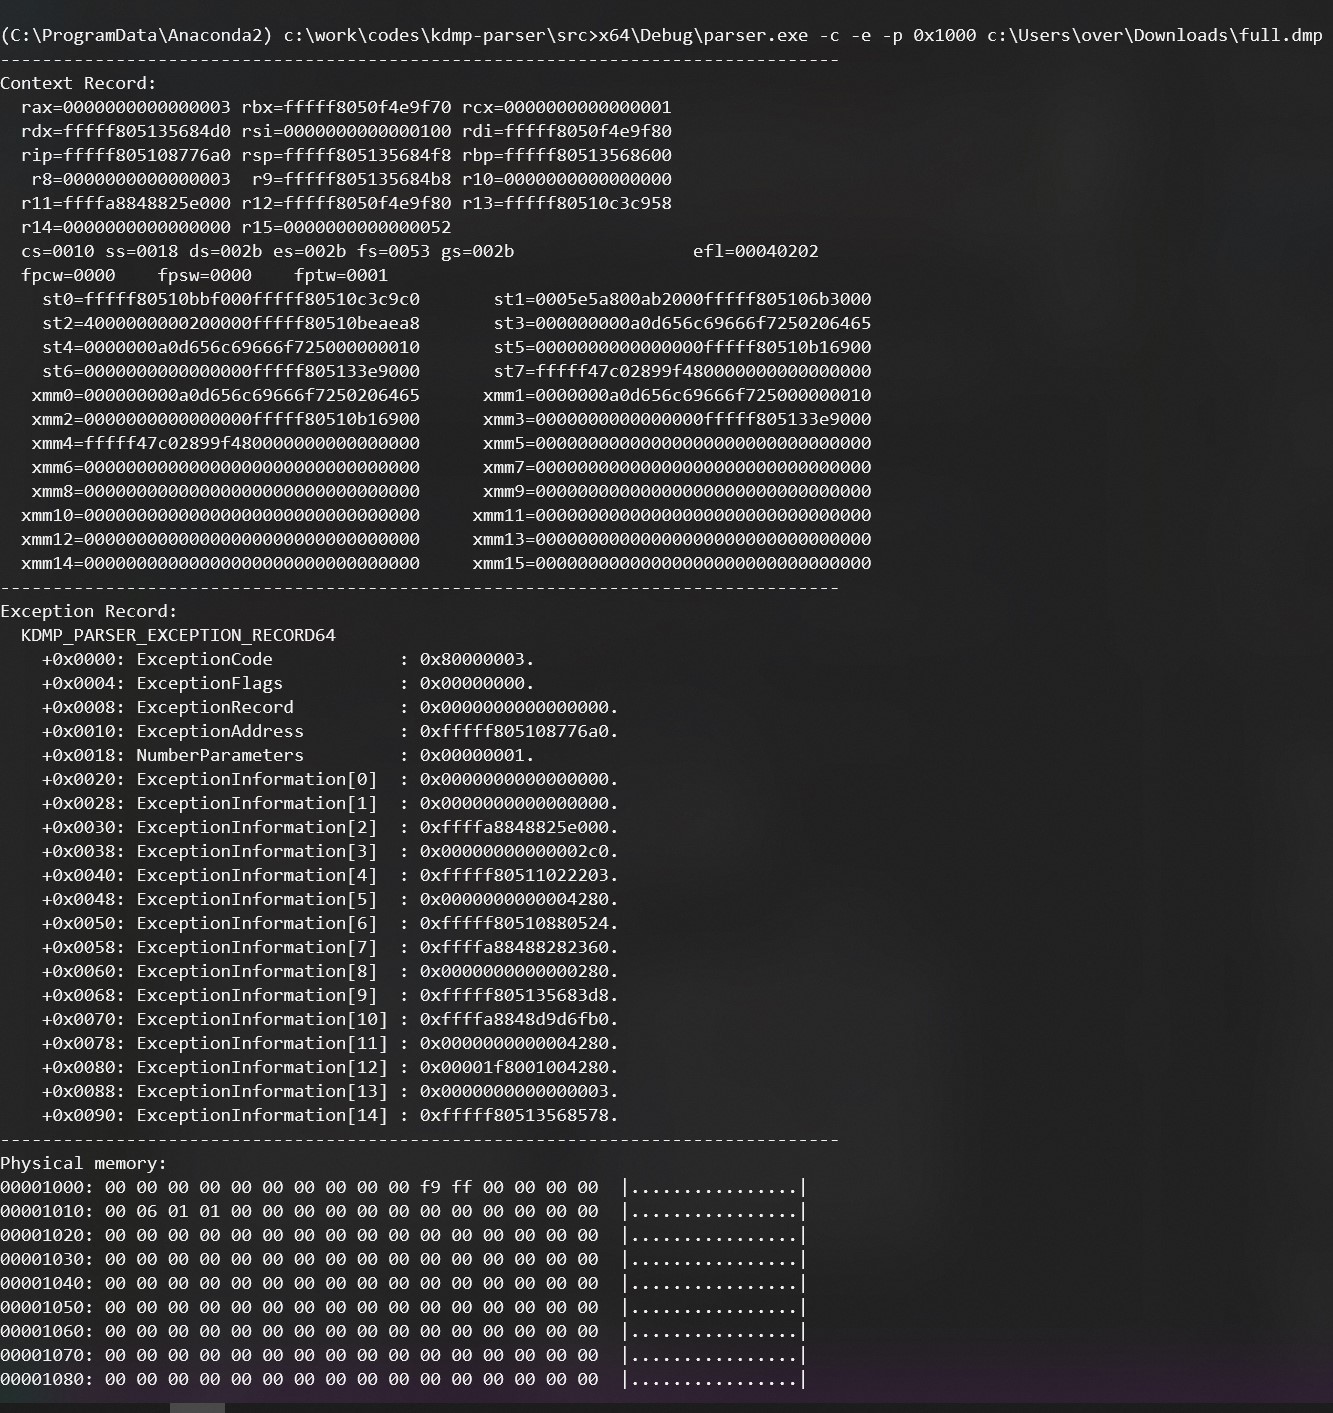
A Windows kernel dump C++ parser library with Python 3 bindings.

digital-forensicsforensicsincident-response+1
21511 months ago
security-baseline-ubuntu preview

security-baseline-ubuntu

GitHubeugexo/security-baseline-ubuntu

Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, custom AppArmor/Firejail 0.9.80, Rootless Docker,…

configuration-auditingdata-recoverydigital-forensics+6
85 days ago
dumpscan preview
Archived

dumpscan

GitHubdaddycocoaman/dumpscan

Finding secrets in kernel and user memory

cryptographydigital-forensicsencryption-decryption-tools+4
1183 years ago
clairvoyance preview

clairvoyance

GitHub0vercl0k/clairvoyance

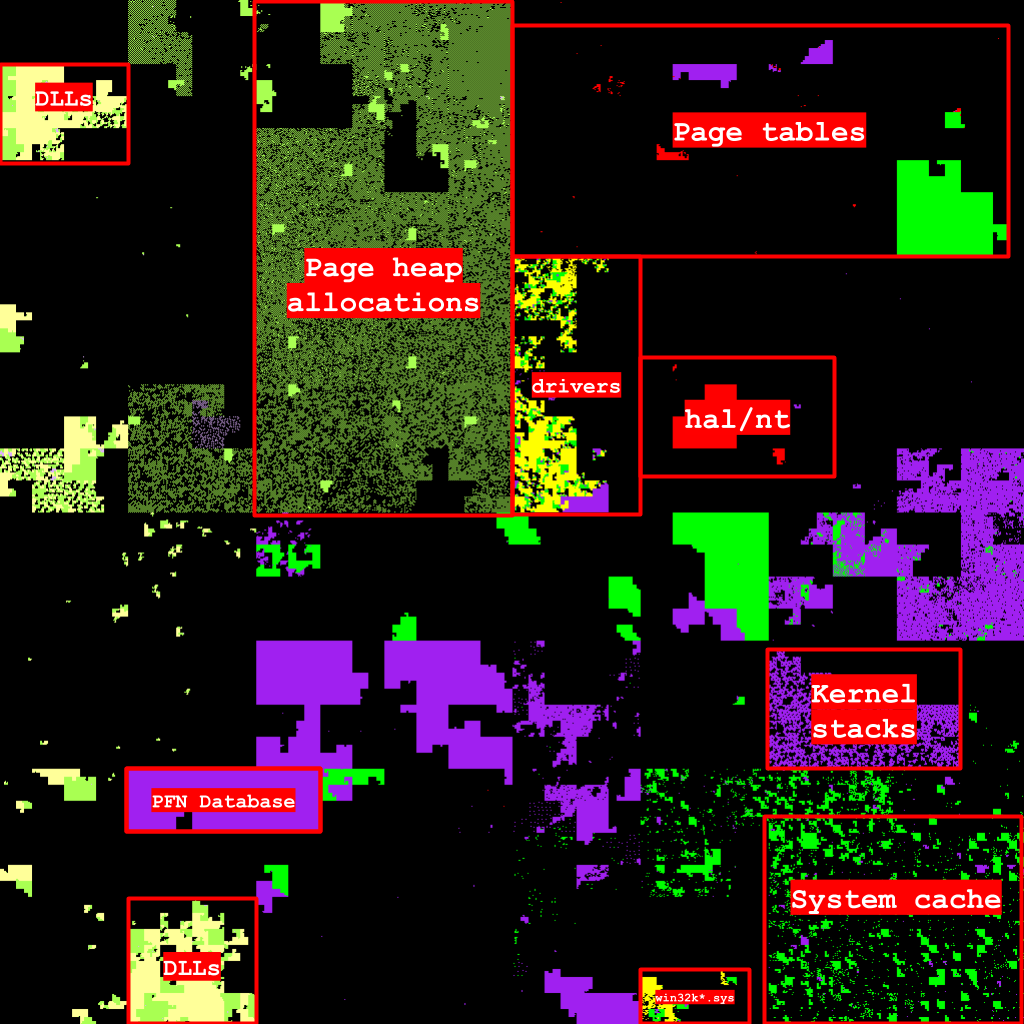
Visualize the virtual address space of a Windows process on a Hilbert curve.

digital-forensicsforensicsmemory-forensics
3115 years ago