
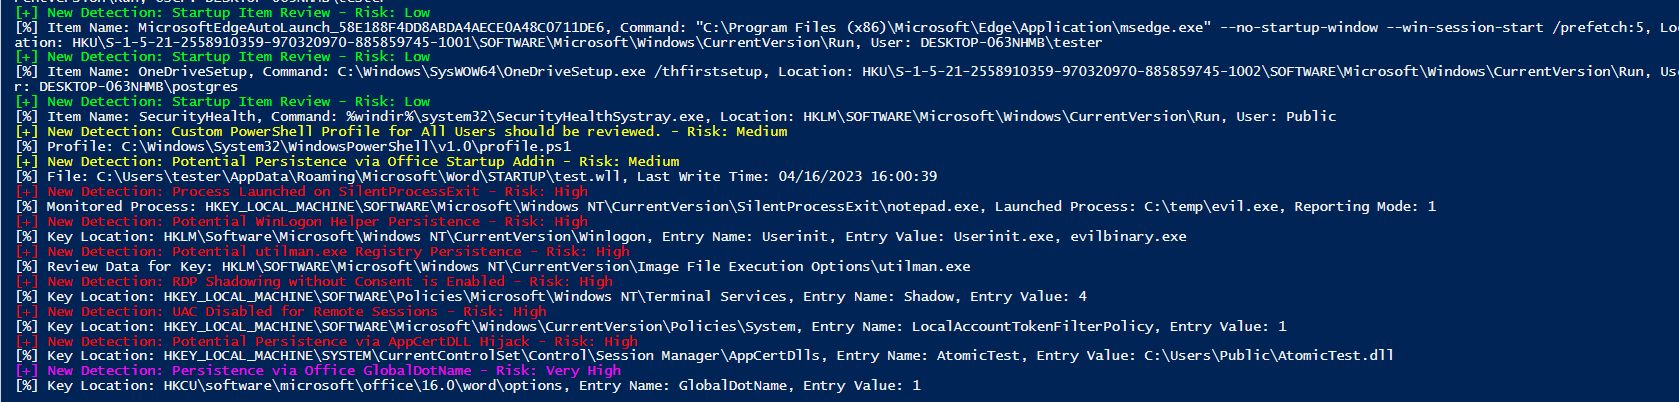
Trawler
 joeavanzato/trawler
PowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
defensive-toolsdigital-forensicsforensics+2
340
joeavanzato/trawlerPowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
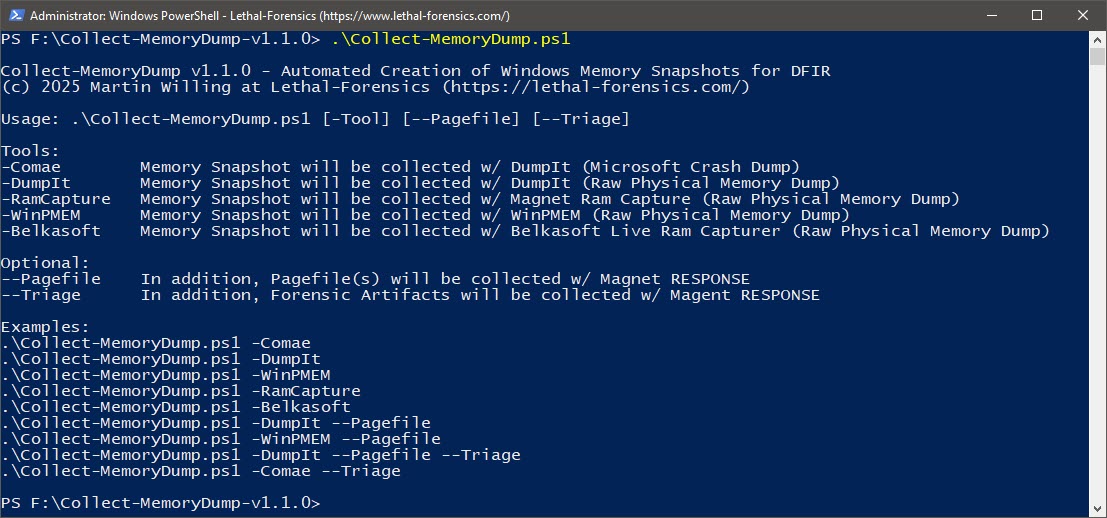 lethal-forensics/collect-memorydump
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…
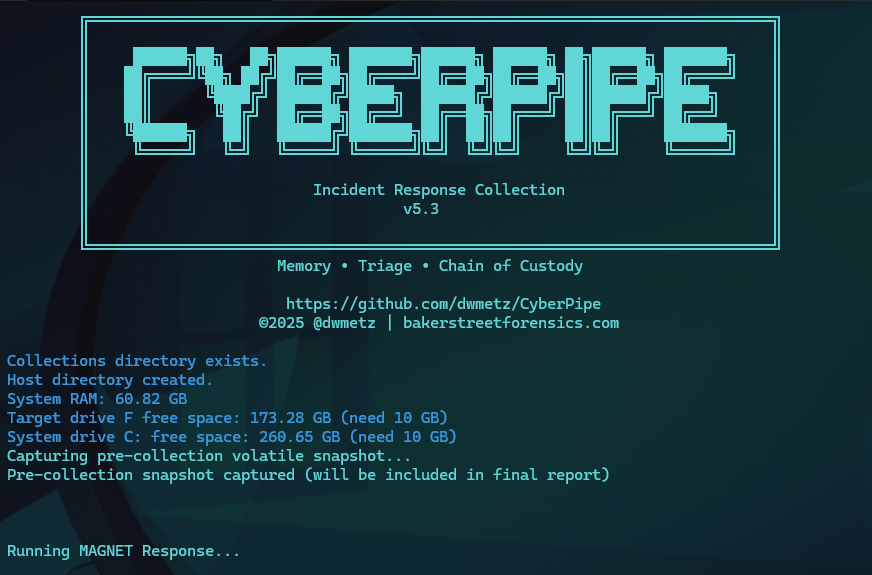 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
 mingchen-script/cve-2020-1472-visualizer
PowerShell script to scan Windows Event Logs for CVE-2020-1472 indicators (events 5827-5831), export to CSV, and generate Excel pivot tables for…
 bjbakker1984/yellowkey-mitigation
PowerShell script that automates the WinRE mitigation workflow for CVE-2026-45585, with verification steps and conditional commit to avoid…
 soteria-security/hafnium-ioc
A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865
 zach115th/toolshellfinder
Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…