

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
40 results
androidqf preview

androidqf

GitHubmvt-project/androidqf

androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
3257h 36m ago
excelpeek preview

excelpeek

GitHubslaughterjames/excelpeek

Static analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
digital-forensicsforensicsmalware-analysis+1
384 years ago
Persistnux preview

Persistnux

GitHubgo-lanz/persistnux

Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
container-escapedigital-forensicseducation+7
32 months ago
dwarf2json preview

dwarf2json

GitHubvolatilityfoundation/dwarf2json

convert ELF/DWARF symbol and type information into vol3's intermediate JSON

binary-analysisdigital-forensicsmemory-forensics+2
1601 year ago
androidqf preview

androidqf

GitHubbotherder/androidqf

Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
android-securitydigital-forensicsforensics+2
3118 months ago
email-header-analyzer preview

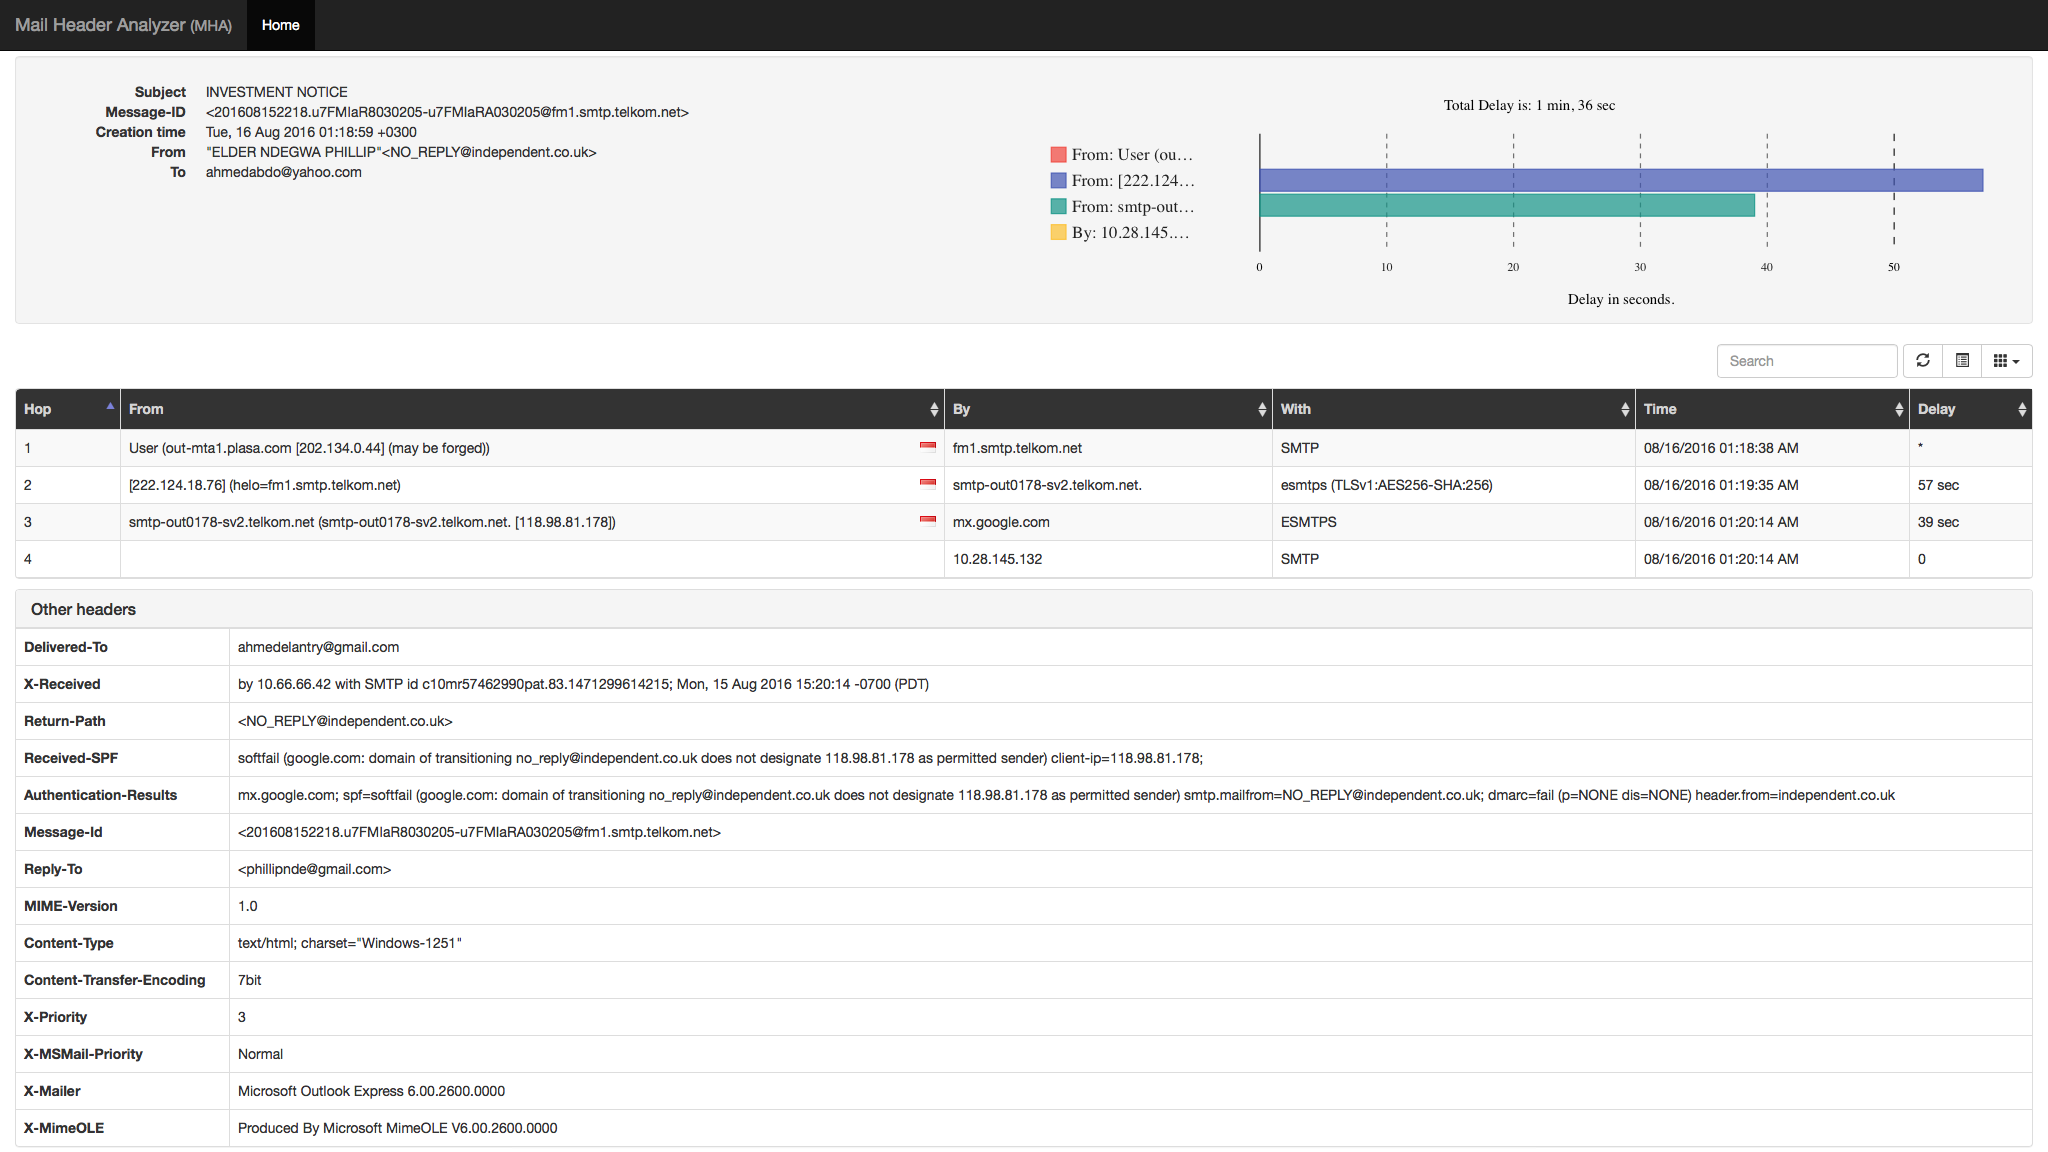
email-header-analyzer

GitHubcyberdefenders/email-header-analyzer

E-Mail Header Analyzer

digital-forensicsemail-securityforensics+2
7006 years ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

database-securitydigital-forensicsdisk-forensics+8
856 months ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.3k1 day ago
whatsapp-media-decrypt preview

whatsapp-media-decrypt

GitHubddz/whatsapp-media-decrypt

Decrypt WhatsApp encrypted media files (images, videos, audio, documents) using media keys extracted from iOS ChatStorage.sqlite or Android…
digital-forensicsencryption-decryption-toolsforensics+1
1.0k6 years ago
YellowKey-Bitlocker-CVE-2026-45585 preview

YellowKey-Bitlocker-CVE-2026-45585

GitHubneccie/yellowkey-bitlocker-cve-2026-45585

Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.
data-recoverydigital-forensicsencryption-decryption-tools+1
1 month ago
ShadowNet preview

ShadowNet

GitHubantisurveillanceagency/shadownet

ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…

anti-botdigital-forensicsforensics+9
1612 days ago
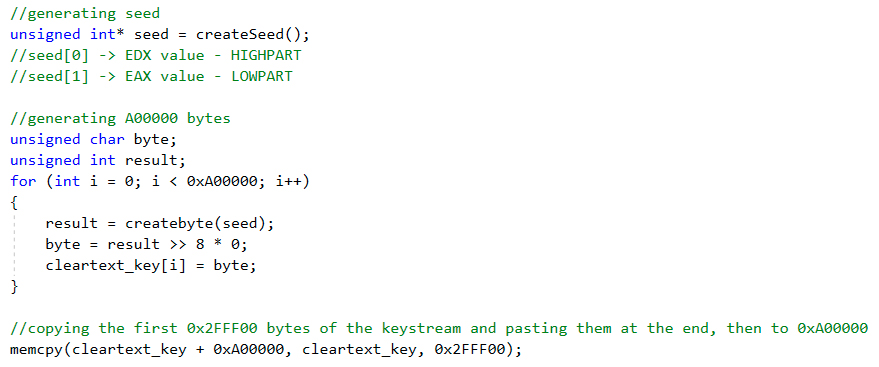
gocropalypse preview

gocropalypse

GitHubnotaswe/gocropalypse

CVE-2023-21036 detection in Go
data-recoverydigital-forensicsforensics+2
13 years ago
HiveV5_keystream_decryptor preview

HiveV5_keystream_decryptor

GitHubreecdeep/hivev5_keystream_decryptor

bad stuffs by bad guys

binary-analysiscryptographydata-recovery+4
494 years ago
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

You didn't think I'd go and leave the blue team out, right?
curated-resourcesdigital-forensicseducation+5
1.8k15 days ago
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
1964 days ago
misp-wireshark preview

misp-wireshark

GitHubmisp/misp-wireshark

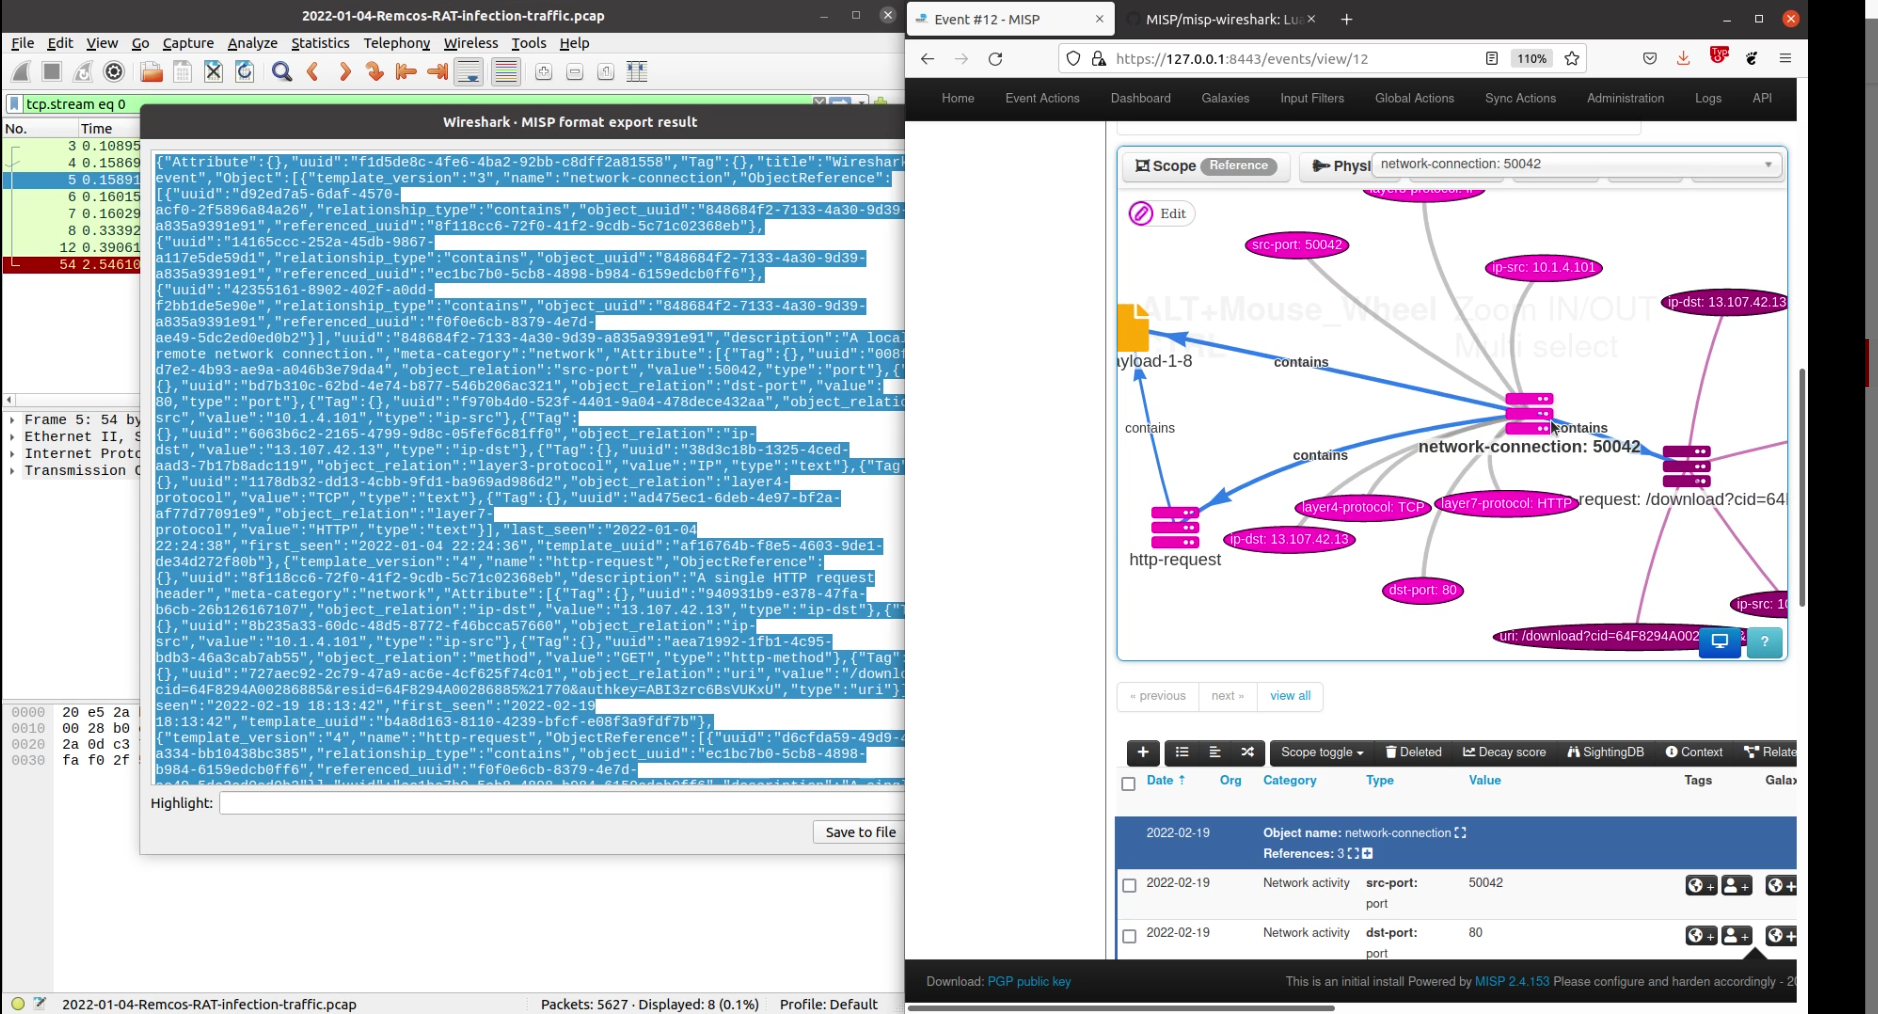
Lua plugin to extract data from Wireshark and convert it into MISP format
digital-forensicsforensicsnetwork-forensics+2
502 years ago
envocabulary preview

envocabulary

GitHubsreckoskocilic/envocabulary

Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…

configuration-auditingdigital-forensicsforensics+3
39 days ago
rinhit preview

rinhit

GitLabtoxy4ny/rinhit

Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…

bluetooth-securitydigital-forensicsinformation-gathering+6
1 month ago
Previous123Next