
netlas-cookbook
 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
curated-resourcesdigital-forensicseducation+9
889
netlas-io/netlas-cookbookThe goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
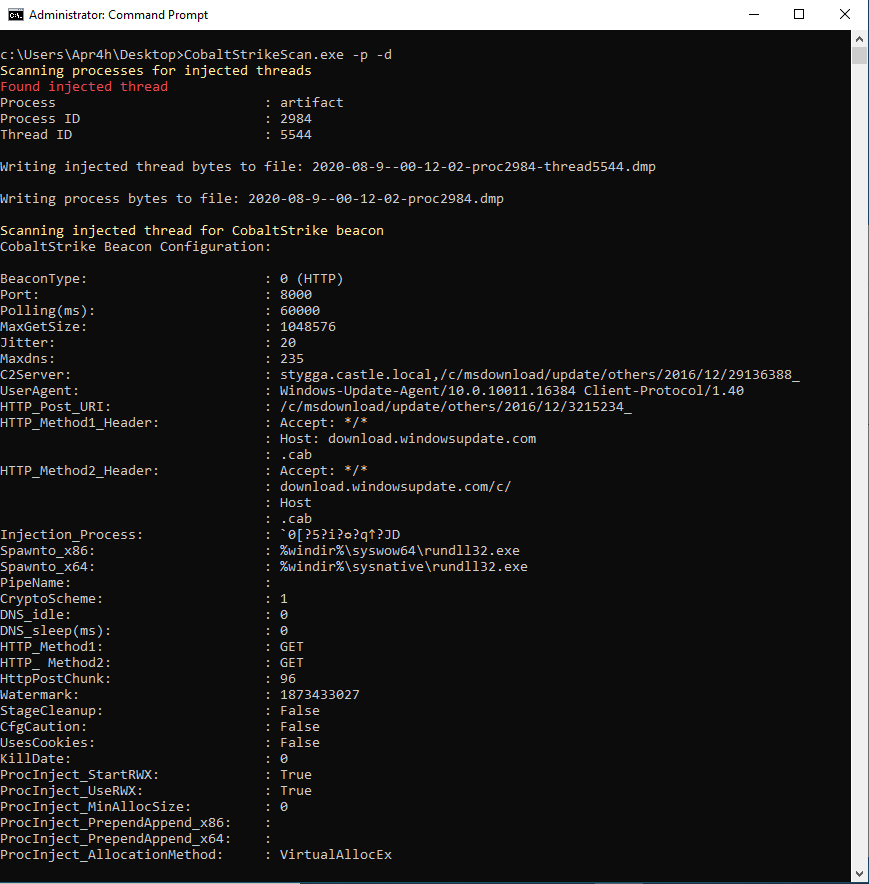 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 simsong/tcpflow
TCP/IP packet demultiplexer. Download from:
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 mindcrypt/covertchannels-steganography
A list of covert channels and steganography/steganalysis resources (books, papers & tools)
 rails/rails-forensics-cve-2026-66066
Forensic toolkit and agent skills for investigating Rails Active Storage/libvips CVE-2026-66066: detects crafted blob indicators, exposure windows,…
 knight0x07/bibi-windows-wiper-analysis
Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
 clark-prog/blackout-public
Blackout — The Official Blackout Public FAFO Repo.
 mukul975/anthropic-cybersecurity-skills
817 structured cybersecurity skills for AI agents · Mapped to 6 frameworks: MITRE ATT&CK, NIST CSF 2.0, MITRE ATLAS, D3FEND, NIST AI RMF & MITRE F3…
 google/turbinia
Automation and Scaling of Digital Forensics Tools
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 zblurx/dploot
Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…