
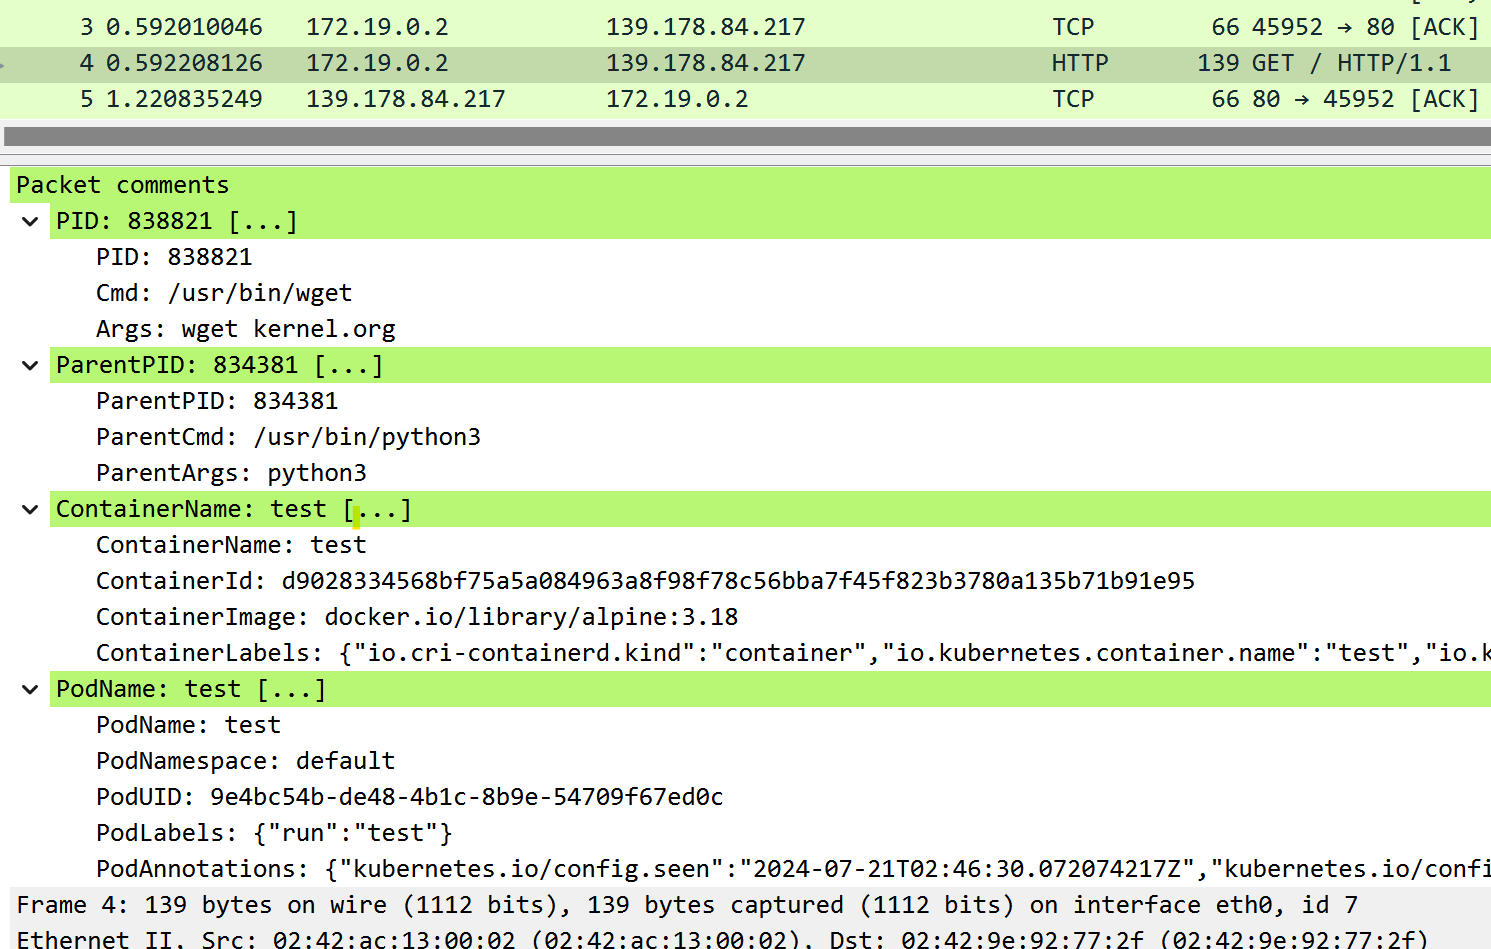
ptcpdump
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
cloud-securitycontainer-securitydigital-forensics+5
1.3k
mozillazg/ptcpdumpeBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
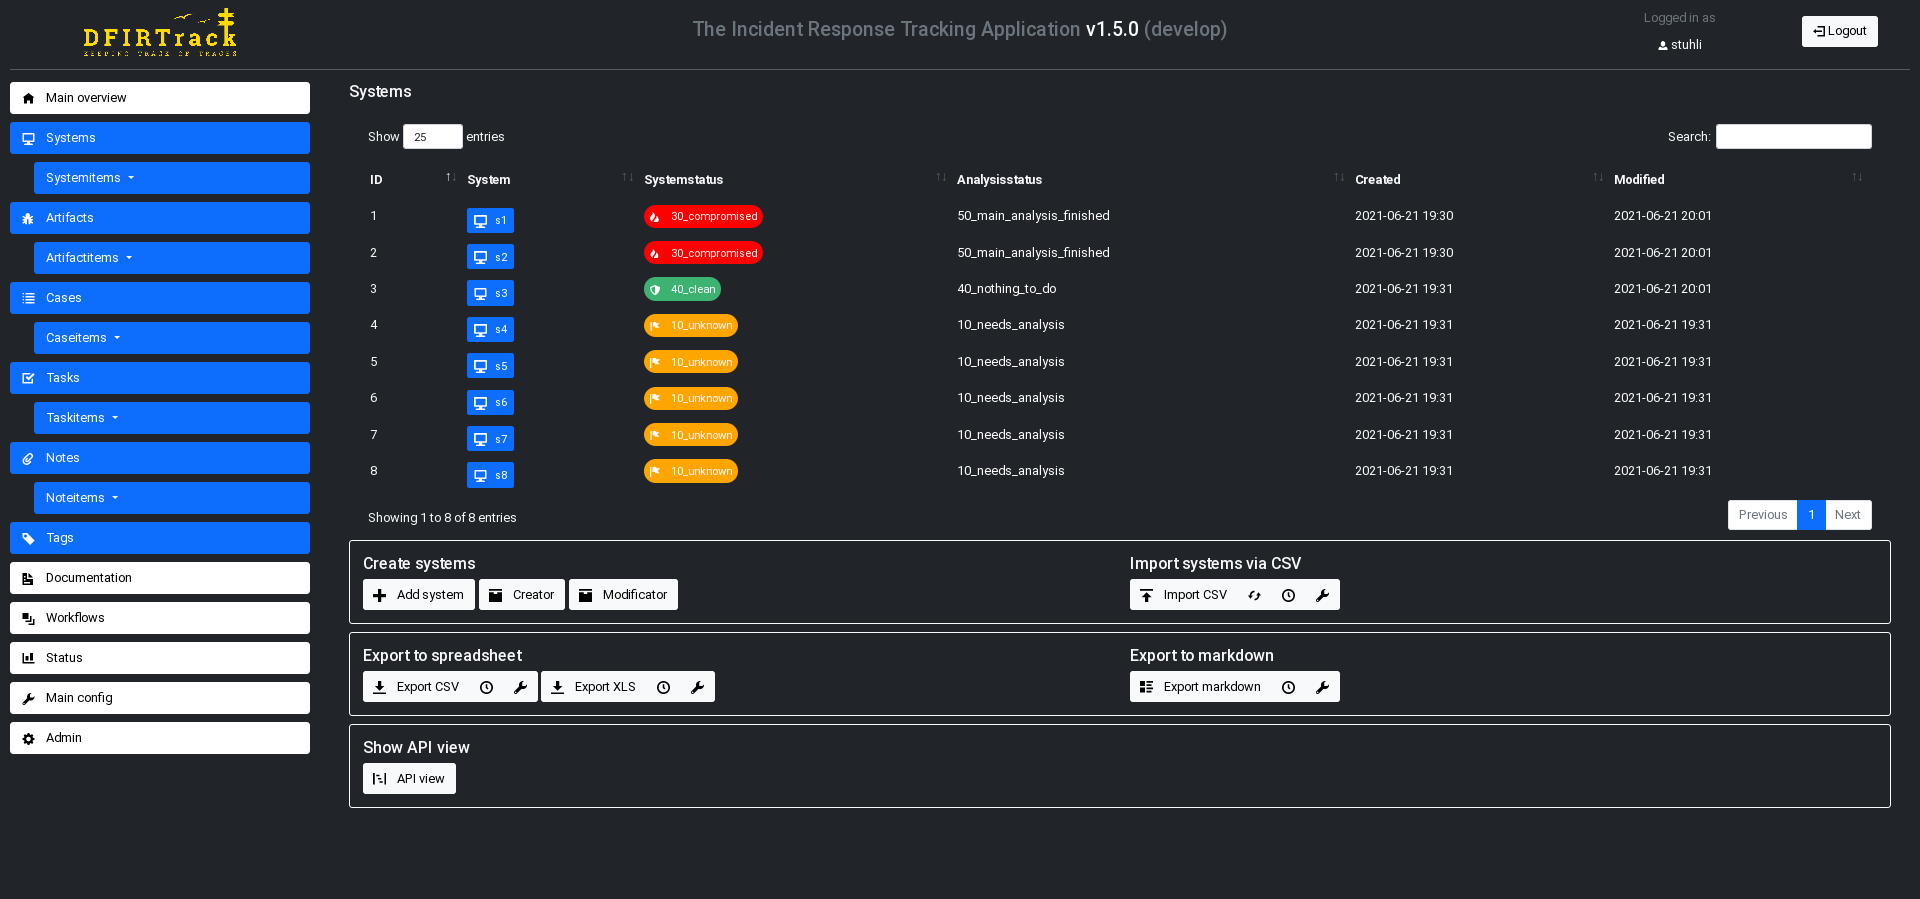 dfirtrack/dfirtrack
System-based incident response tracking application for managing large-scale DFIR cases, with import/export, task workflows, and artifact tracking…
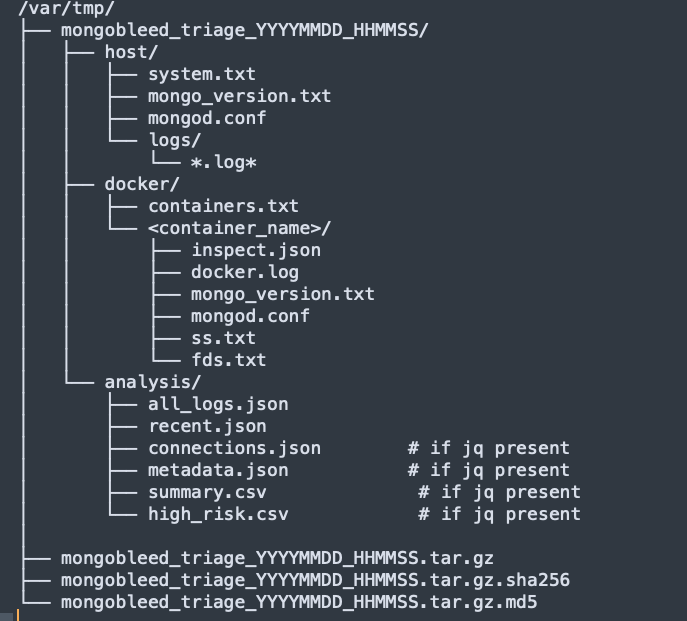 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
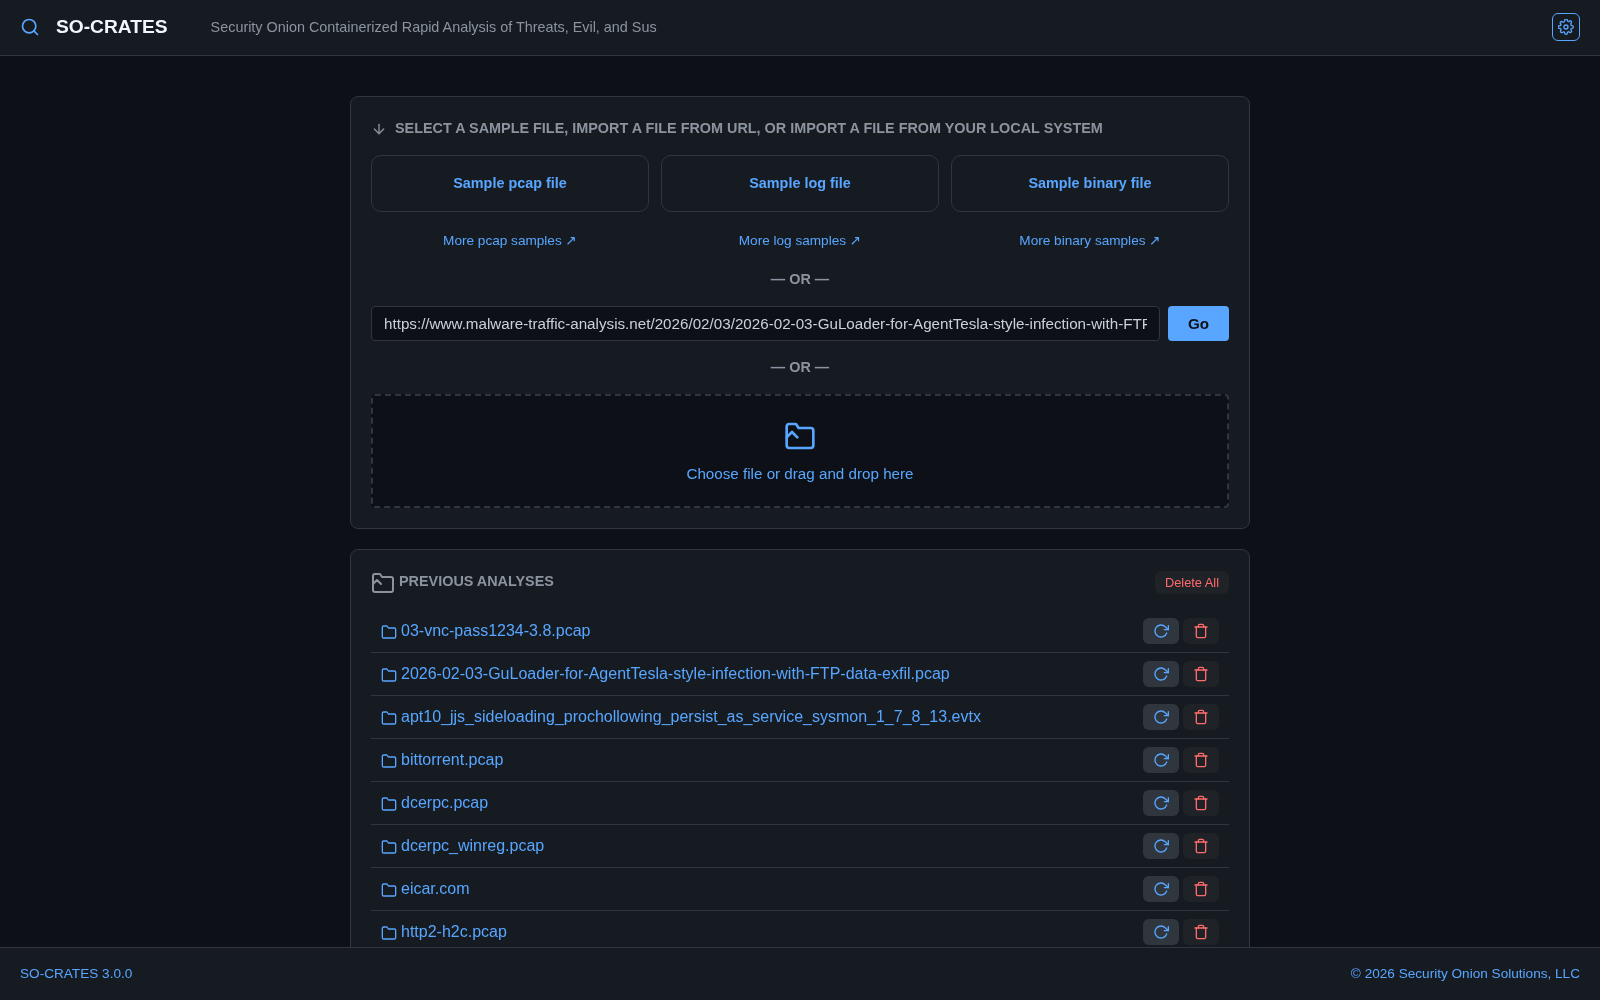 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 cado-security/varc
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
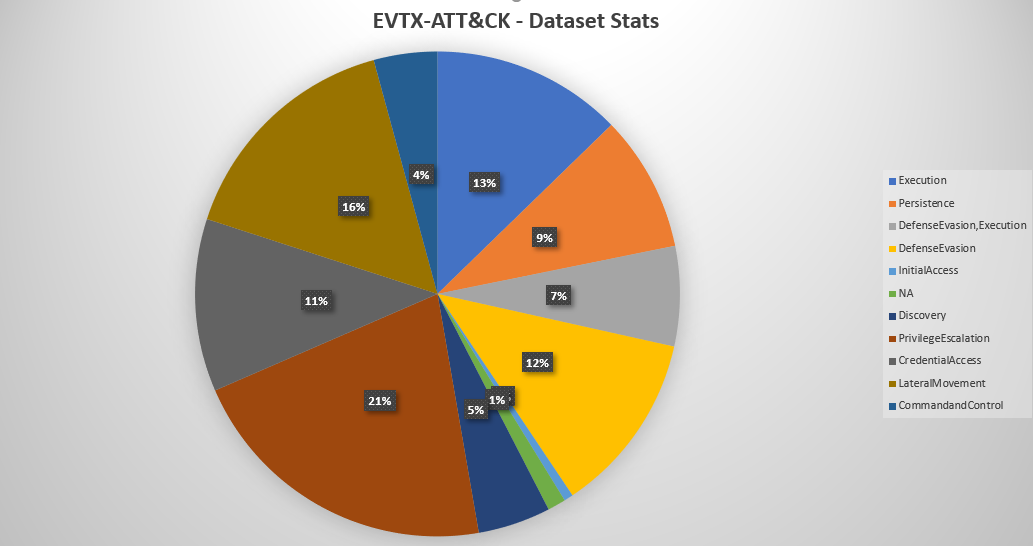 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
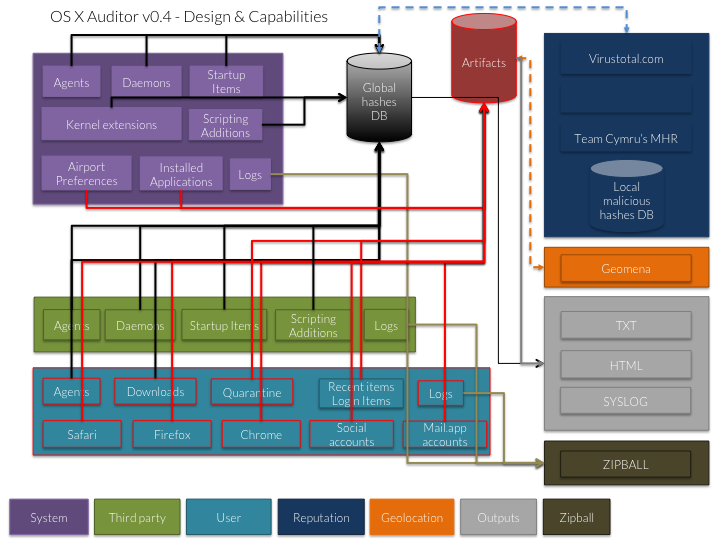 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool