CVE-2021-36934-DLL-Hijacking-DFIR-Investigation

DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…

DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…

Detection and restoration of Windows Snipping Tool PNG captures vulnerable to CVE-2023-28303

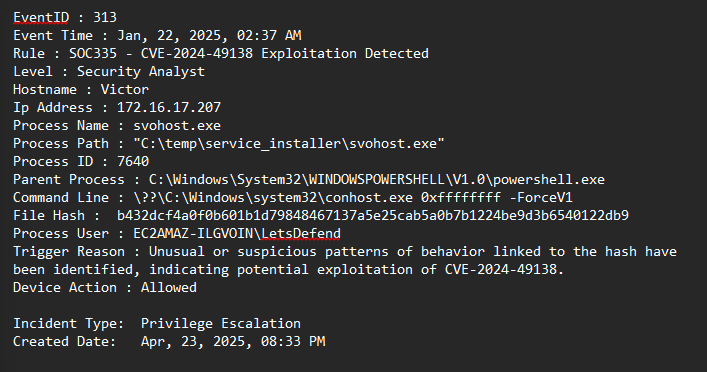
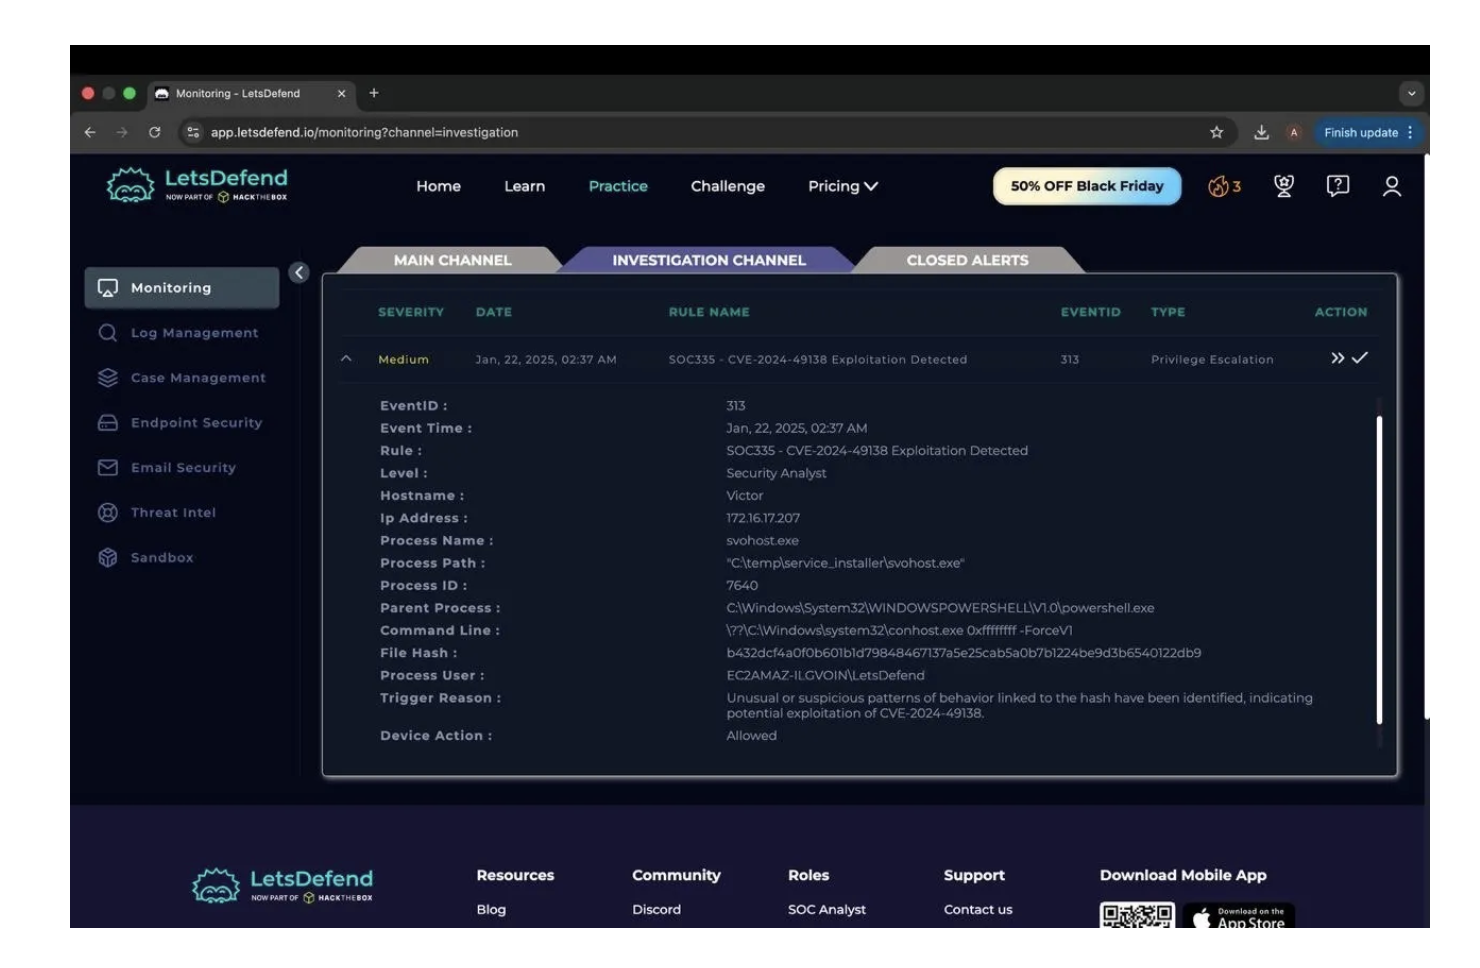
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.

Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771

Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

Demostracion educativa de mitigacion de CVE-2026-68820: Use-After-Free en afd.sys de Windows.

Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)

X-Ways Acropalypse extension detects CVE-2023-21036 in common images

A proof-of-concept for (CVE-2023-38840) that extracts plaintext master passwords from a locked Bitwarden vault.

This repository is to demonstrate and practice my forensic/vulnerability analysis skills by reproducing a web-related CVE in a safe environment.

Original PoC for CVE-2023-32784

SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…

Retrieves the master password from Keepass memory dump, using a hint of bruteforce.

A lightweight CLI tool to detect and reconstruct cropped images vulnerable to Acropalypse (CVE-2023-21036 and CVE-2023-28303) written in Python.

Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…

Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)

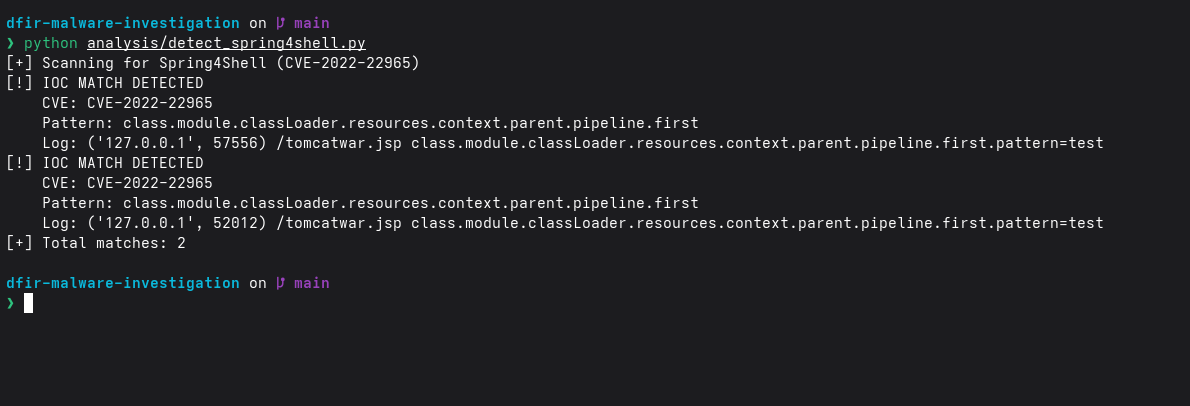
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.