

mailMeta
 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
digital-forensicsemail-securityforensics+2
1765 years ago
gr33nm0nk2802/mailmetaAn forensics tool to help aid in the investigation of spoofed emails based off the email headers.
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 osintnet/osintnet-public
OsintNET is a browser-based OSINT platform for domain intelligence, website risk scanning, SERP discovery, image intelligence and AI image detection.
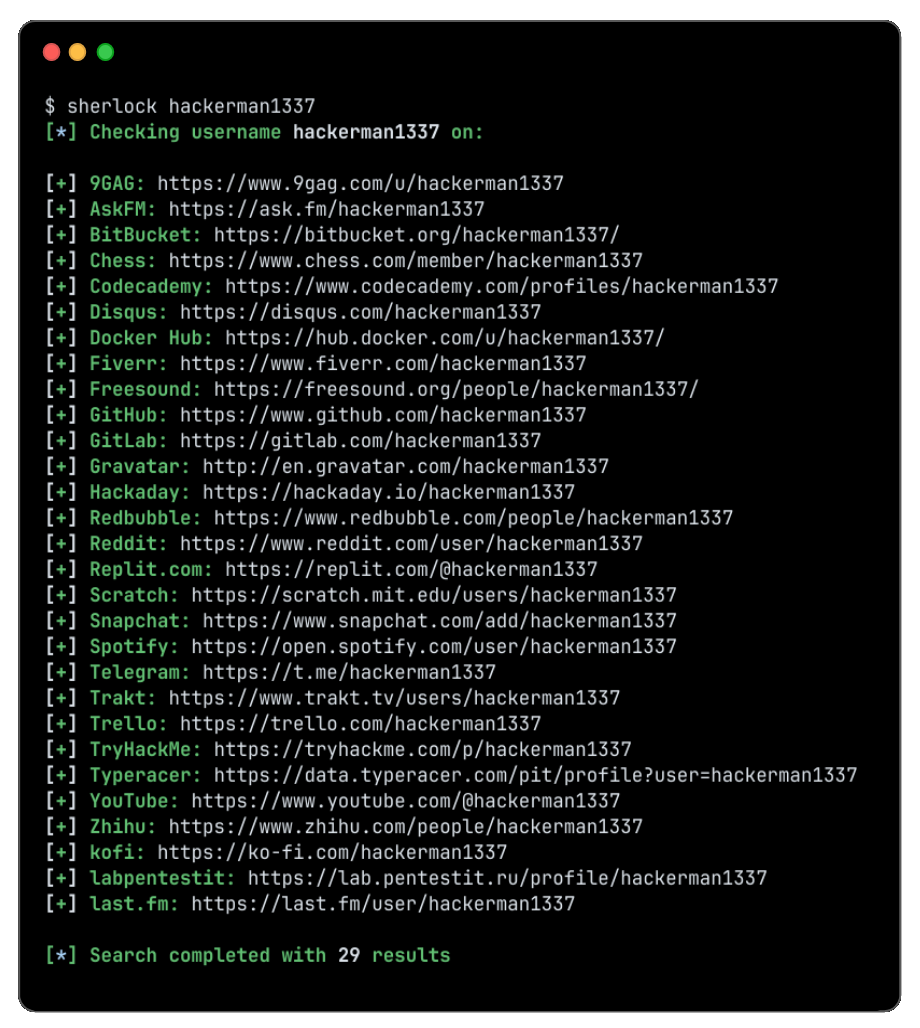 sherlock-project/sherlock
Hunt down social media accounts by username across social networks
 adulau/the-art-of-pivoting
The Art of Pivoting - Techniques for Intelligence Analysts to Discover New Relationships in a Complex World
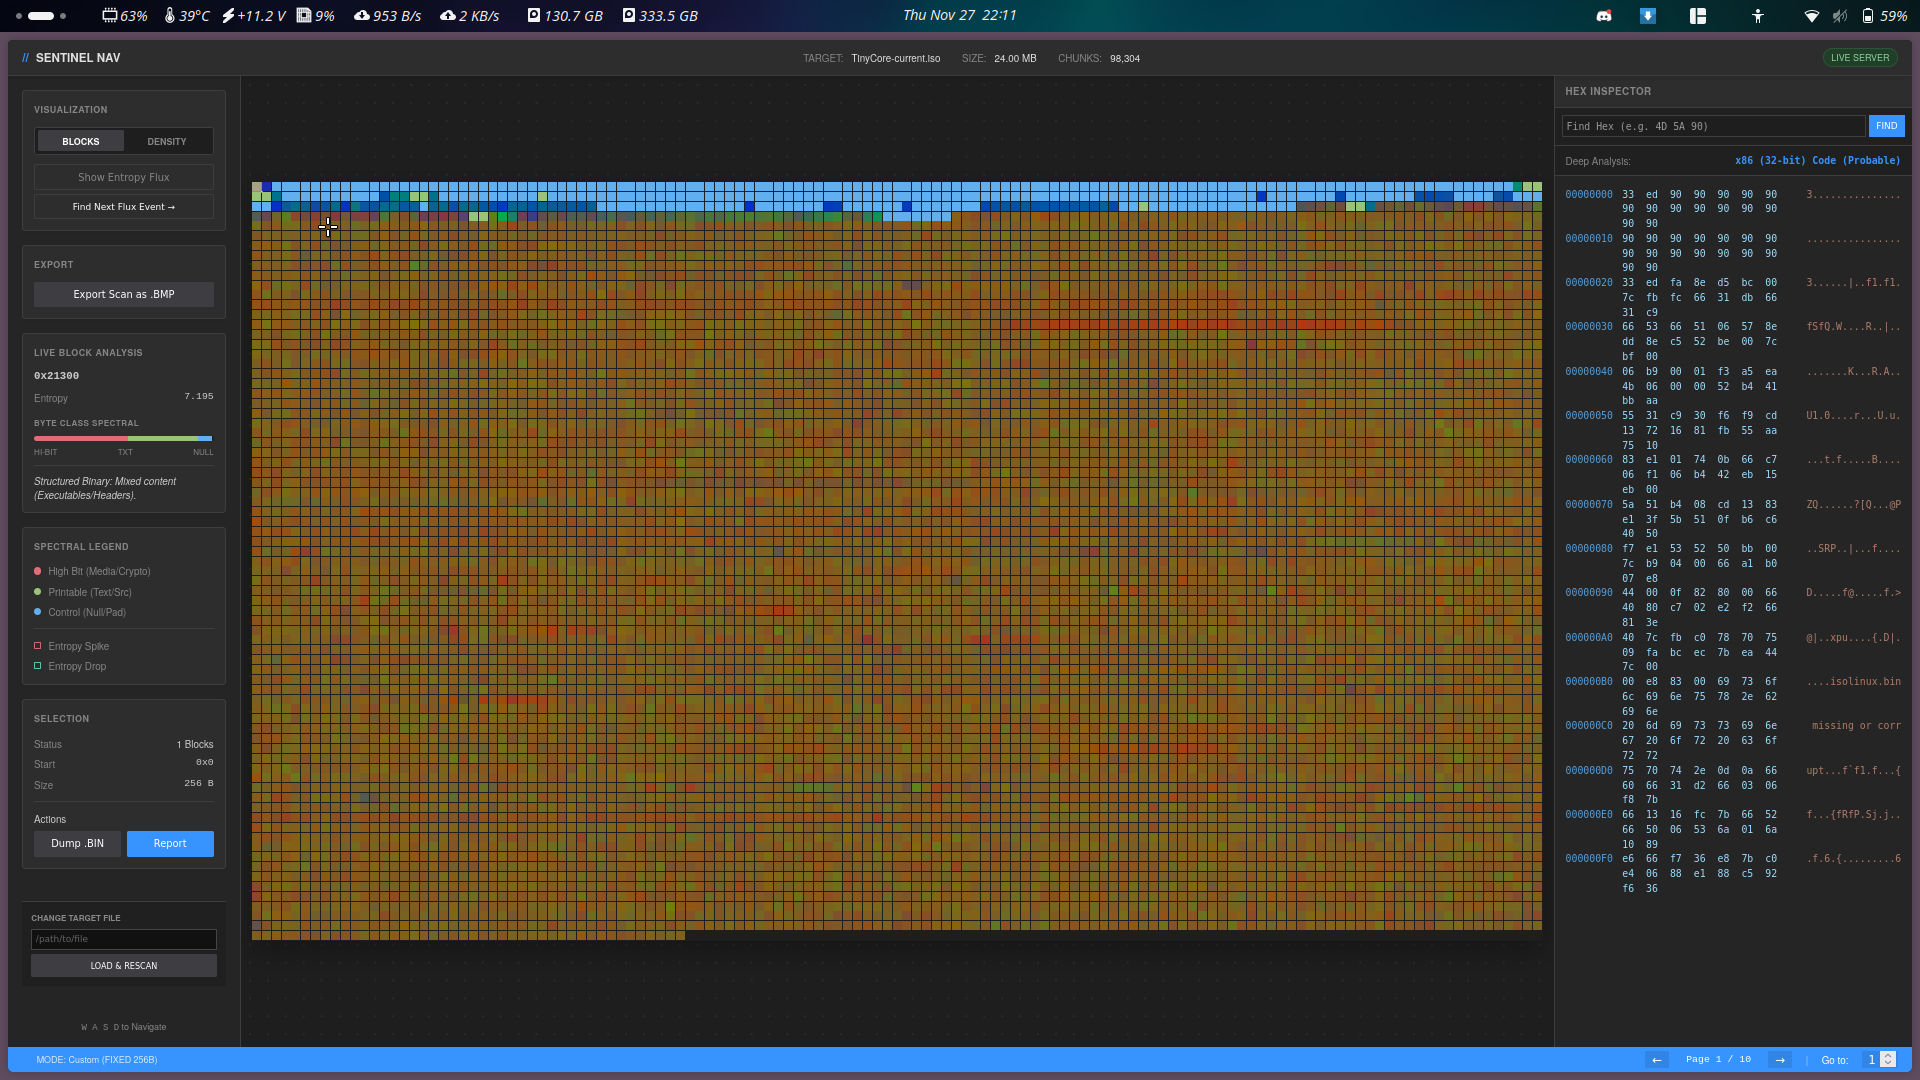 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
 farghlymal/config-extractors
Extracts and decrypts malware configuration data from captured samples, automating C2 endpoint discovery, credential extraction, and indicator triage…
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
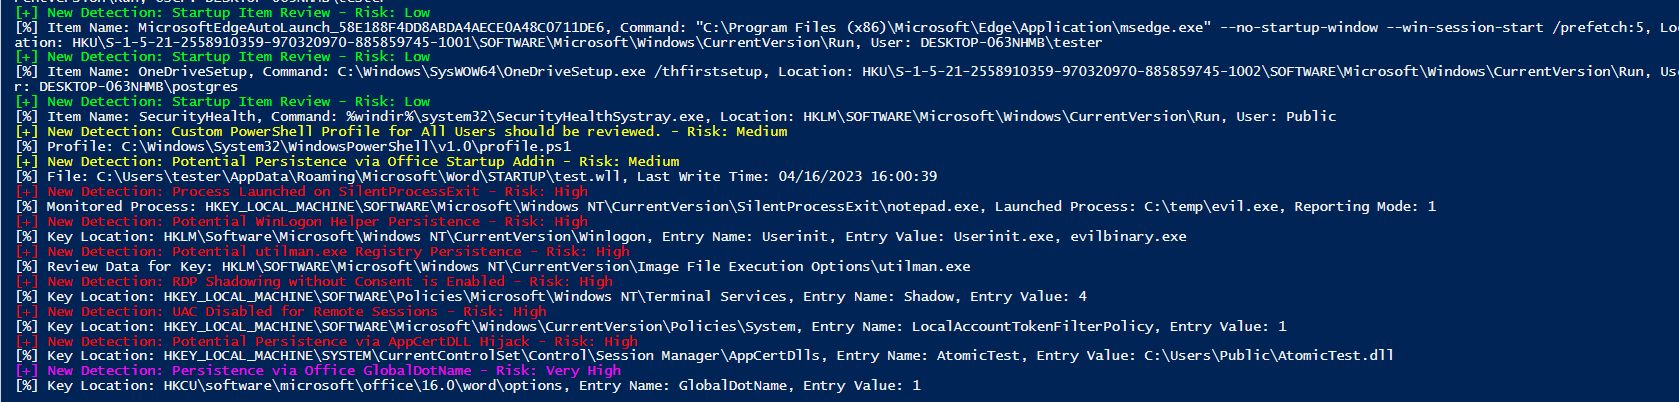 joeavanzato/trawler
PowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
 itres-labs/cve-2025-31702
Repository with tools, exploits, and material associated with the analysis and discovery process of CVE-2025-31702 and other related security issues.
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 jas502n/010-editor-template
Binary template repository for 010 Editor, providing .bt scripts for parsing executables, filesystem images, registry hives, and forensic artifacts…
 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…