prefetch-hash-cracker

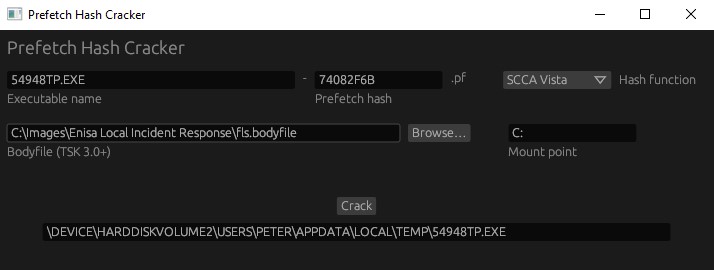
Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…

Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…

Extract Windows credentials directly from VM memory snapshots and virtual disks

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

Curated collection of indicators of compromise extracted from real-world malware investigations, including hashes, domains, and IPs for threat…

Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…

Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…


FWT is a security analysis and file monitoring tool that utilizes Sysmon events.