
MacOSThreatTrack
 ab2pentest/macosthreattrack
Bash tool used for proactive detection of malicious activity on macOS systems.
digital-forensicsincident-responseinformation-gathering+1
40
ab2pentest/macosthreattrackBash tool used for proactive detection of malicious activity on macOS systems.
 t0pcyber/hawk
Powershell Based tool for gathering information related to O365 intrusions and potential Breaches
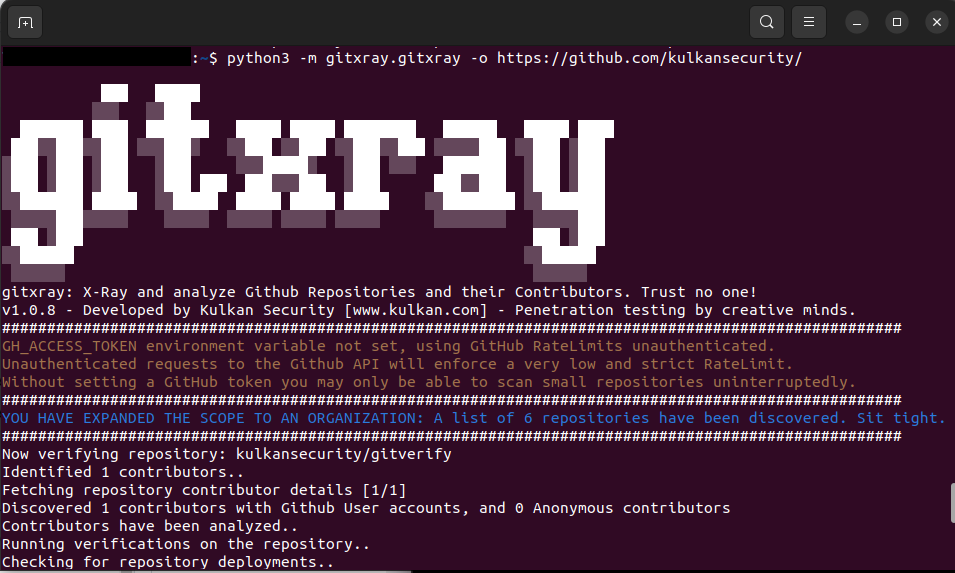 kulkansecurity/gitxray
A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.
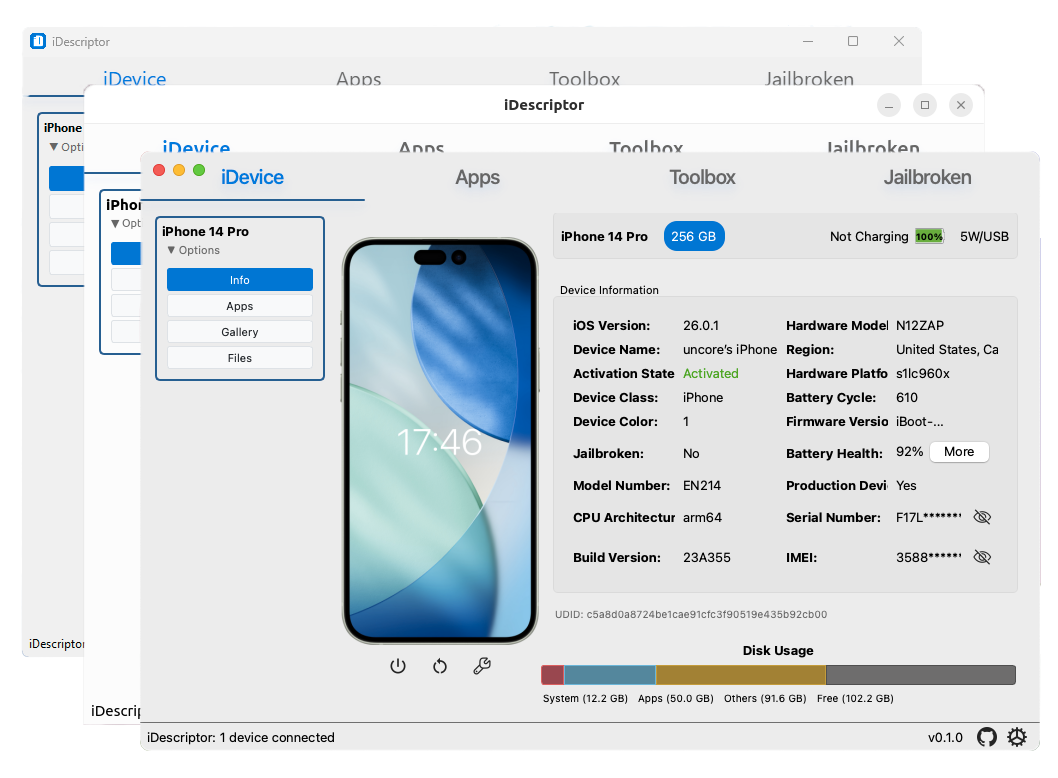 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
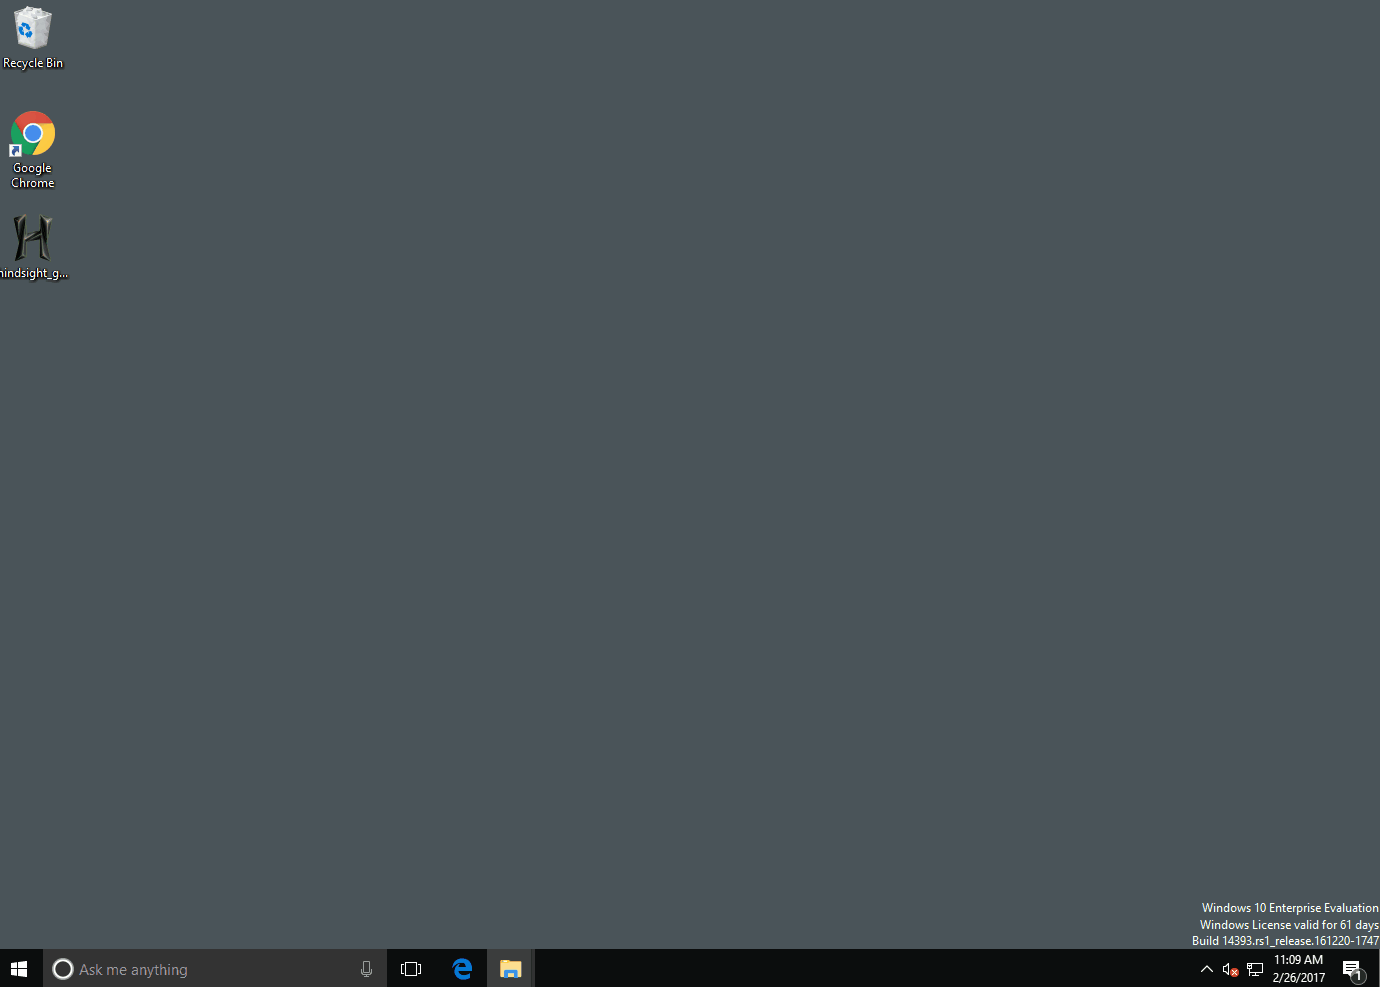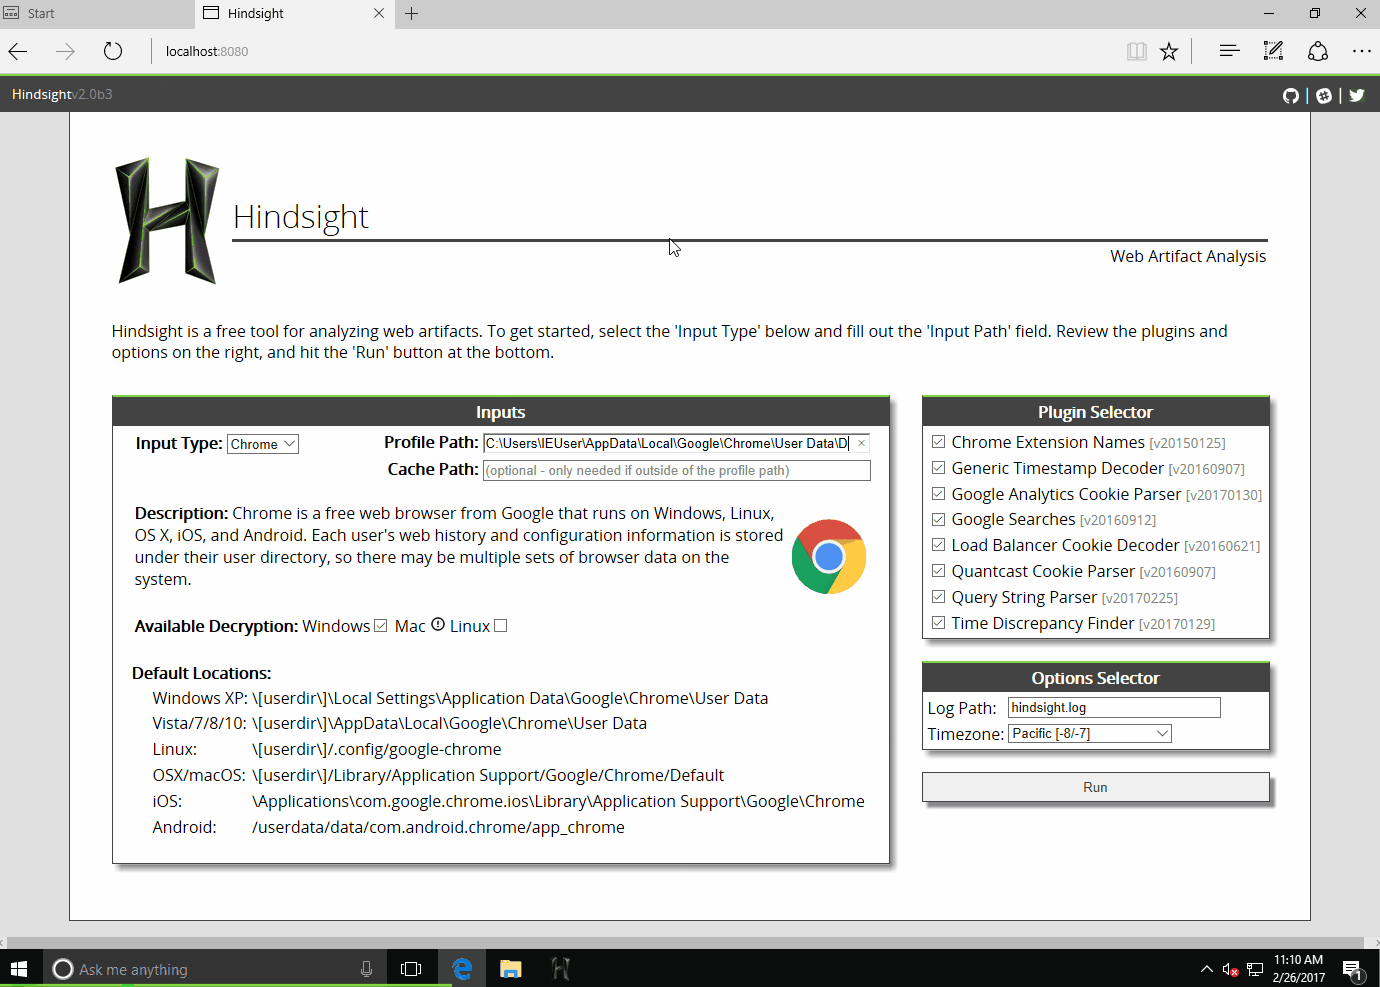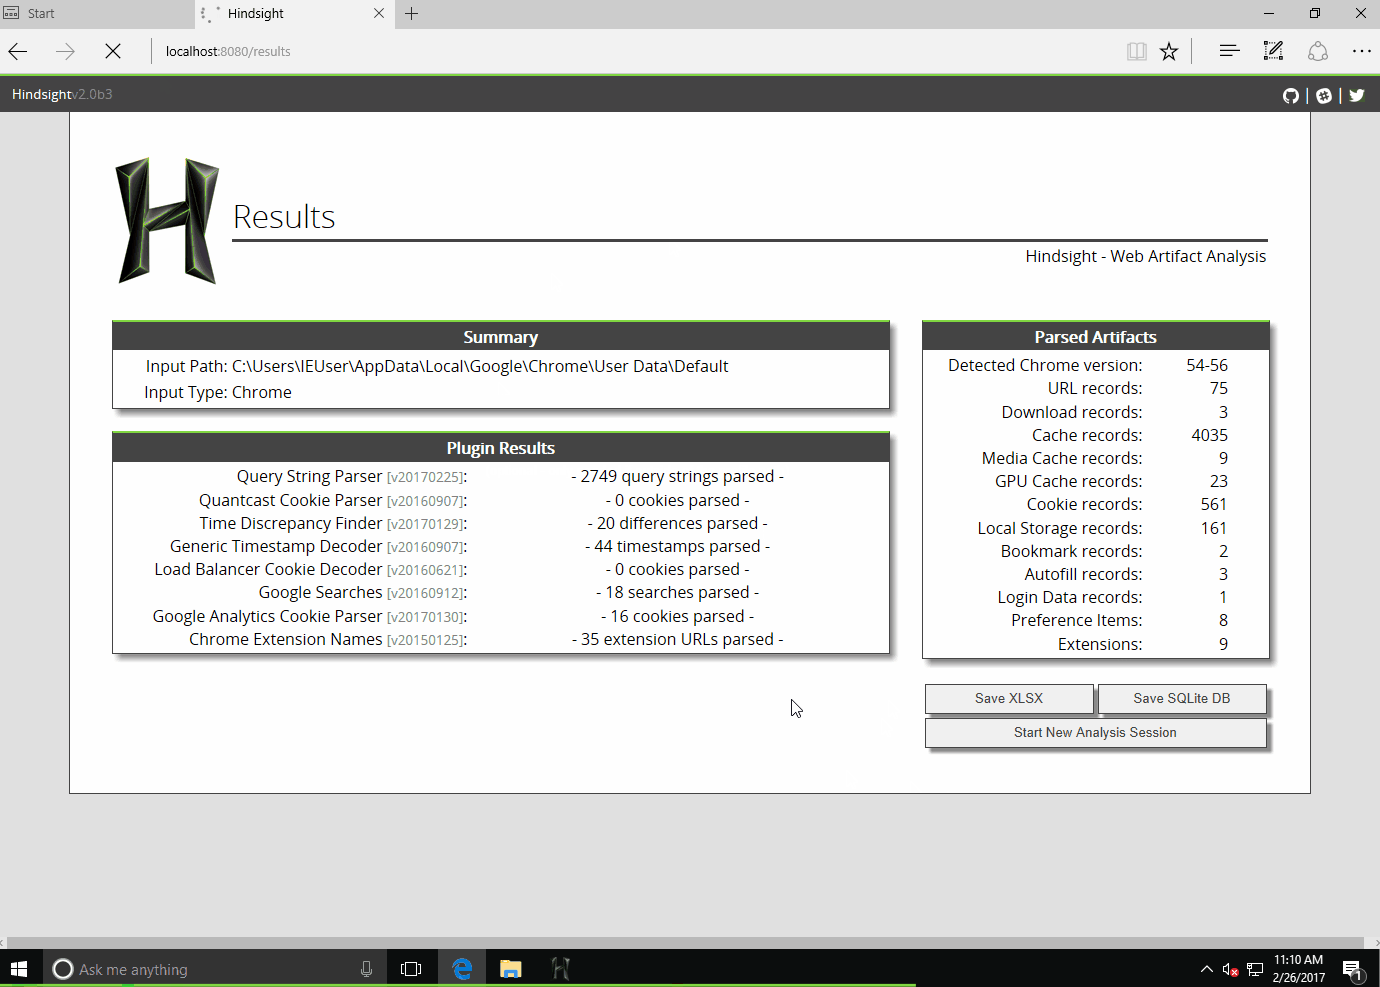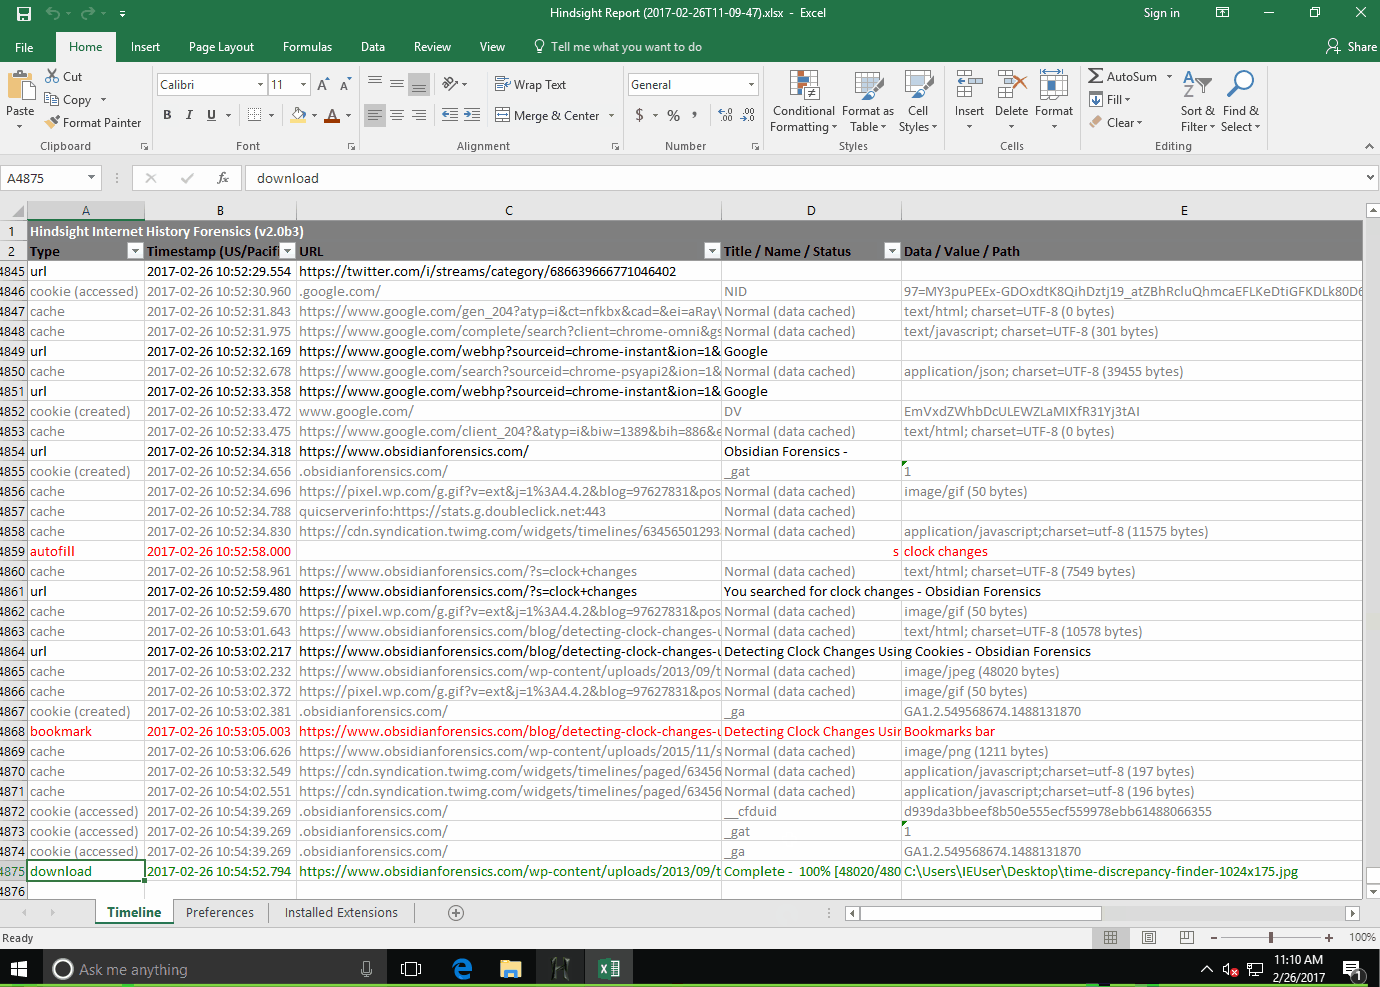 ryandfir/hindsight
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 guibacellar/tex
Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…
 mr-r3b00t/crime-mapper
A tool for mapping cyber crime
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems
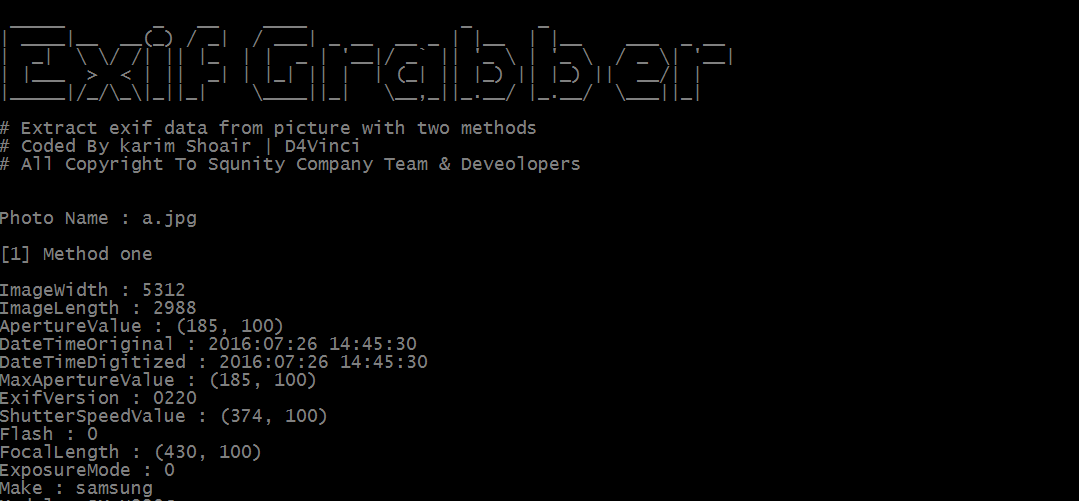 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
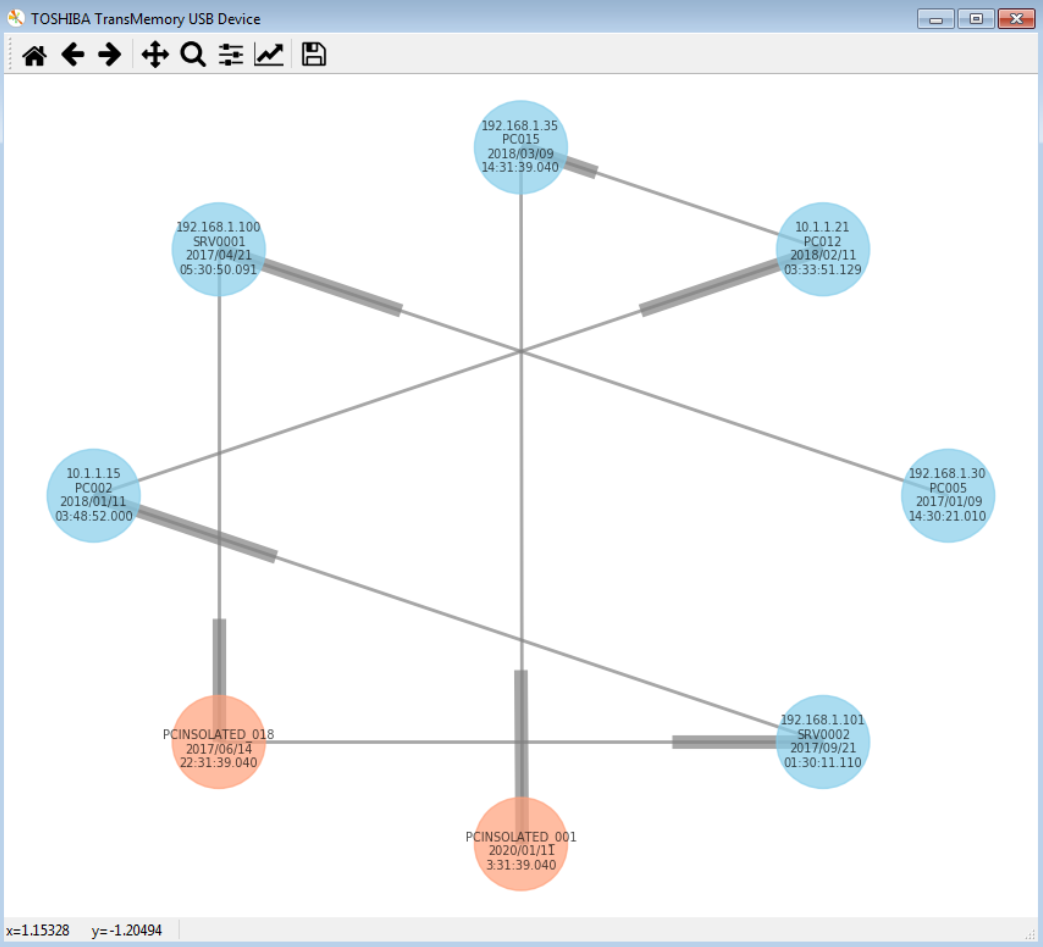 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 nccgroup/metadataplus
A tool to use novel locations to extract metadata from Office documents.
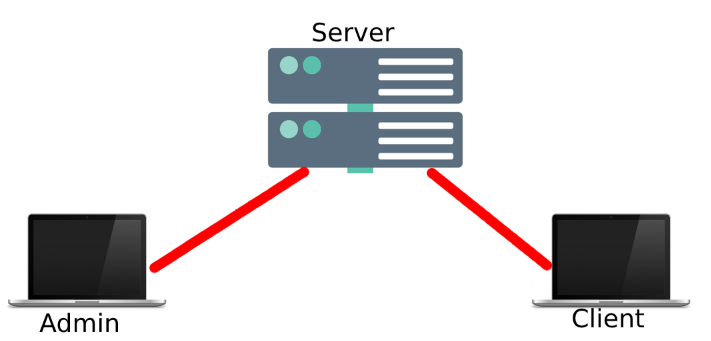 letsdefendio/simple-live-data-collection
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.