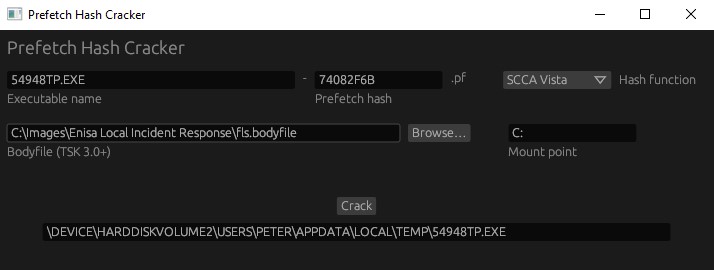
prefetch-hash-cracker

Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…
digital-forensicsforensicsincident-response+1
78
Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…

Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…

Automated forensic script hunting for cve-2019-19781

Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management

Forensics artefact collection tool for systems running Microsoft Windows