

ADRecon
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
980
adrecon/adreconPowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 omriher/captipper
Malicious HTTP traffic explorer
 nox-project/nox-framework
High-performance OSINT/CTI framework for automated identity pivoting and risk analysis across 120+ sources.
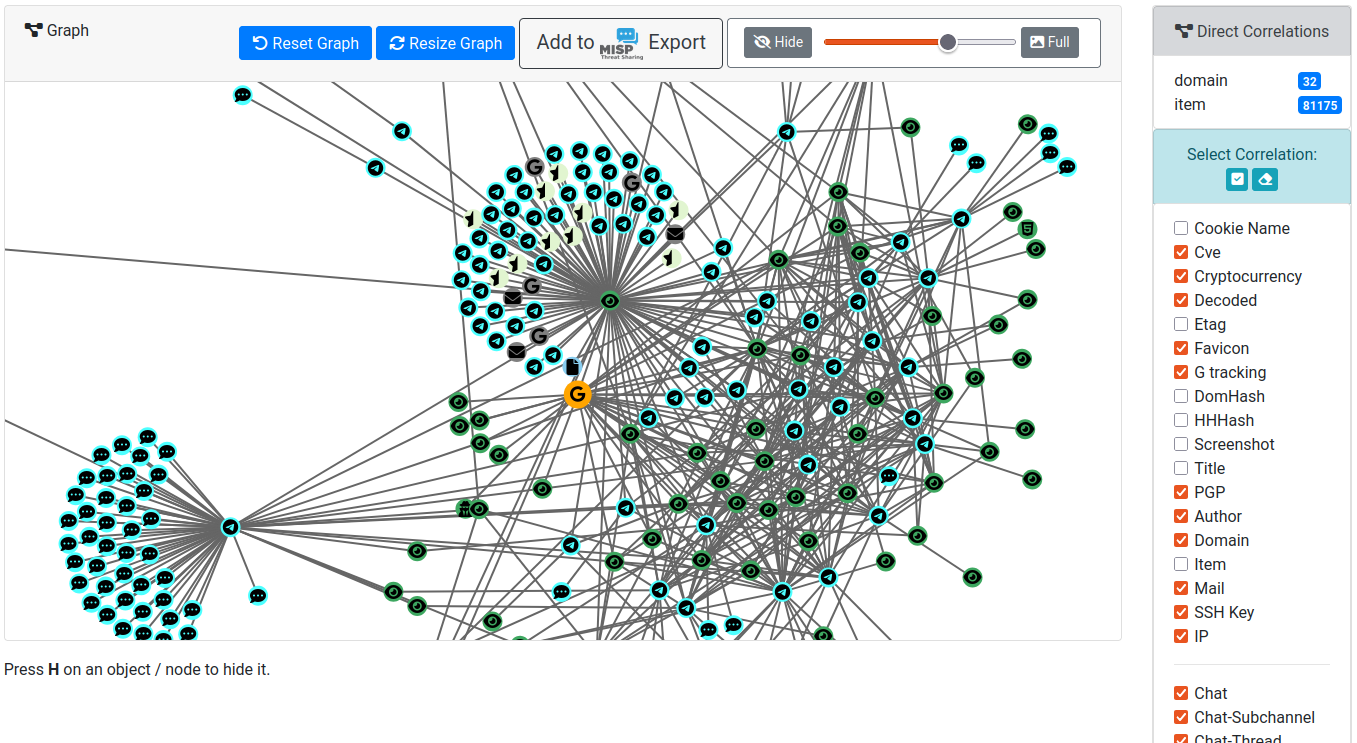 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
 nowsecure/android-forensics
Open source Android Forensics app and framework
