
autopsy
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
data-recoverydigital-forensicsdisk-forensics+3
3.3k
sleuthkit/autopsyAutopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 cado-security/dfir_resources_revil_kaseya
Resources for DFIR Professionals Responding to the REvil Ransomware Kaseya Supply Chain Attack
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 eyesecurity/wp2shell-compromise-scanner-plugin
Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
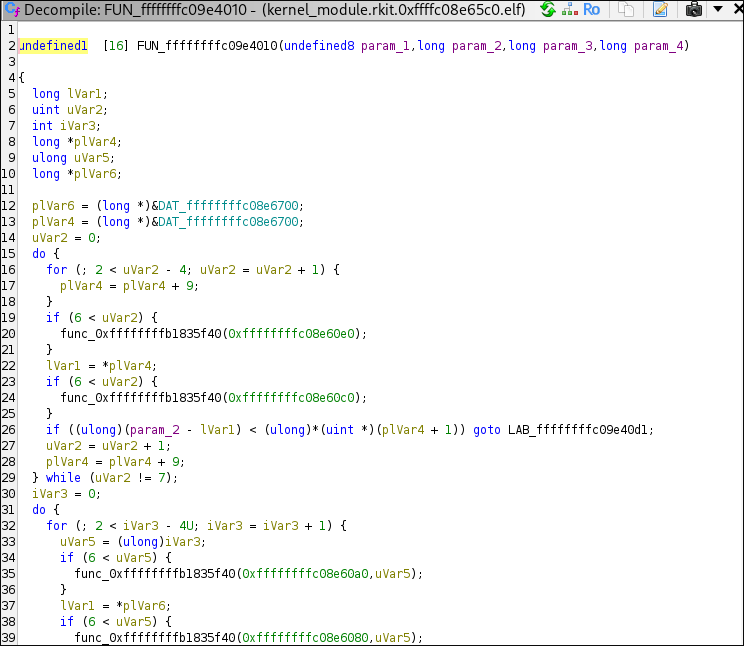 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 bitcoin/bitcoin
Full-node Bitcoin client that validates transactions and blocks on the peer-to-peer network, with integrated wallet, cryptographic security, and…
 otrf/security-datasets
Re-play Security Events
 mthcht/threathunting-keywords
Awesome list of keywords and artifacts for Threat Hunting sessions

 packetlss/android-locdump
android location service cache dumper
 corelight/log-add-http-post-bodies
Add POST body excerpt to Bro's HTTP log
 ares-sys/uefi_bootkit_softlanding
First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).