
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
338 results
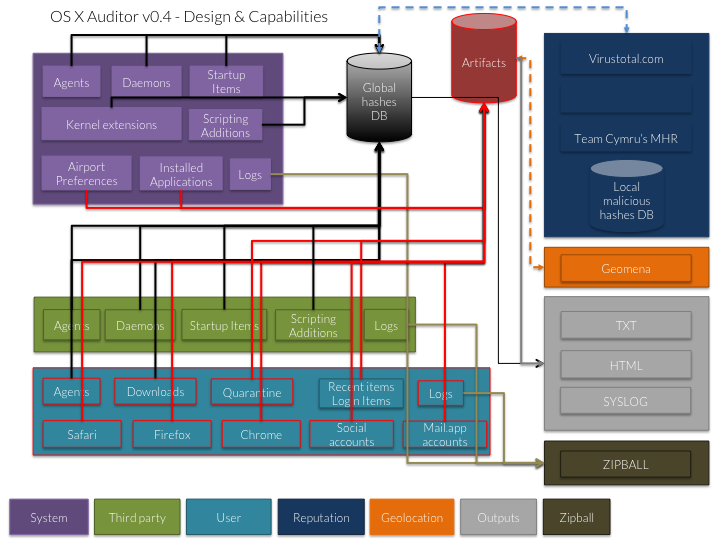
OSXAuditor preview

OSXAuditor

GitHubjipegit/osxauditor

OS X Auditor is a free Mac OS X computer forensics tool
digital-forensicsdisk-forensicsforensics+4
3.1k
6 years ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
digital-forensicsforensicsnetwork-forensics+3
1024 years ago
CVE-2023-32784-kdbxpassdmp preview

CVE-2023-32784-kdbxpassdmp

GitHubamperclock/cve-2023-32784-kdbxpassdmp

Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
digital-forensicsexploitationforensics+3
3 months ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

ctfdigital-forensicsdisk-forensics+6
5859 months ago
pdfresurrect preview

pdfresurrect

GitHubenferex/pdfresurrect

Analyze and help extract older "hidden" versions of a pdf from the current pdf.
data-recoverydigital-forensicsstatic-analysis
1054 years ago
CVE-2025-48708 preview

CVE-2025-48708

GitHubb1tbreaker/cve-2025-48708

Lack of argument sanitization leading to password leakage in Ghostscript PDF versions up to 10.05.0.
data-exfiltrationdigital-forensicsexploitation+3
51 year ago
CVE-2024-3400-Checker preview

CVE-2024-3400-Checker

GitHubterminaljunki3/cve-2024-3400-checker

Check to see if your Palo Alto firewall has been compromised by running script againt support bundle.
digital-forensicsforensicsincident-response+3
2 years ago
cve-2023-32784 preview

cve-2023-32784

GitHubmister-turtle/cve-2023-32784

Extracts KeePass master passwords from memory dumps of unlocked databases, outputting potential characters by position, a passphrase, and a…

digital-forensicsexploitationforensics+3
42 years ago
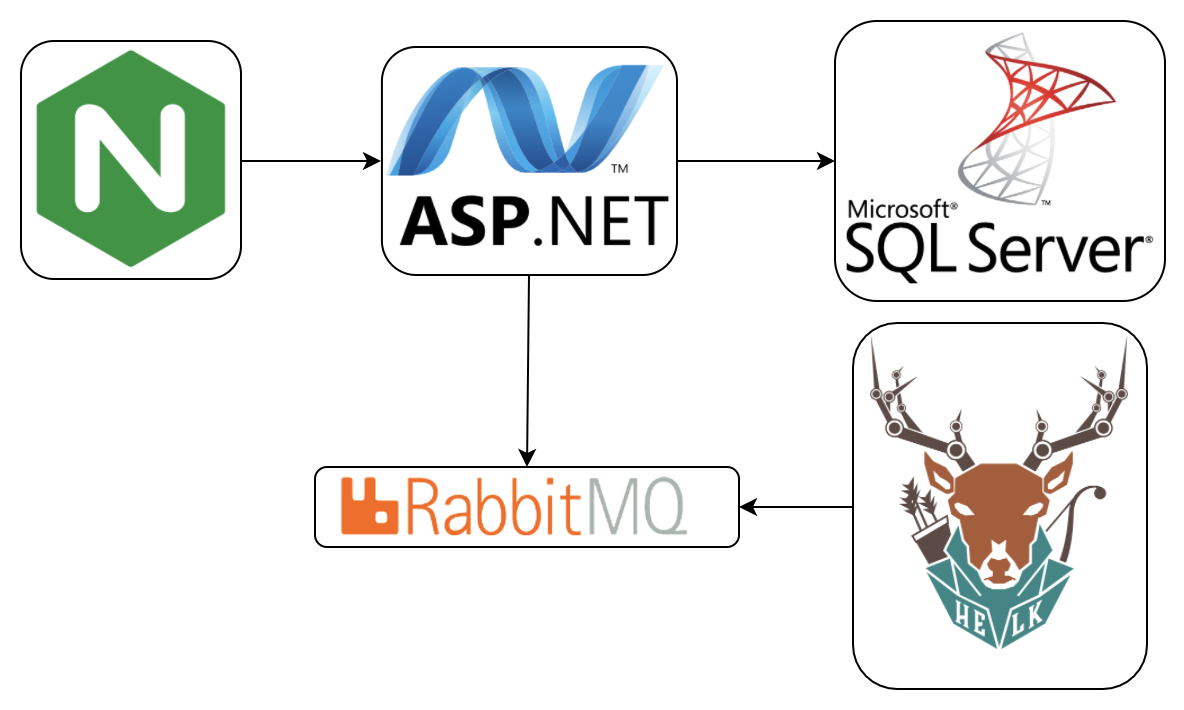
dfir-orc preview

dfir-orc

GitHubdfir-orc/dfir-orc

Forensics artefact collection tool for systems running Microsoft Windows
defensive-toolsdigital-forensicsforensics+2
4471 month ago
ACE preview

ACE

GitHubinvoke-ir/ace

Automated, Collection, and Enrichment Platform
digital-forensicsforensicsincident-response+2
3258 years ago
ESFang preview

ESFang

GitHubwithsecurelabs/esfang

ESF modular ingestion tool for development and research.

digital-forensicsforensicsincident-response+1
384 years ago
py_certificate_extractor preview

py_certificate_extractor

GitHubpassword123456/py_certificate_extractor

Extracts and exports certificate information from digitally signed PE files using Python and pefile, enabling forensic analysis of code-signing…
code-analysisdigital-forensicsmalware-analysis+1
3 years ago
fim-ebpf preview

fim-ebpf

GitHubharshavmb/fim-ebpf

A lightweight eBPF program to monitor file creation and modification events on Linux. This tool leverages eBPF (Extended Berkeley Packet Filter) to…
defensive-toolsdigital-forensicsforensics+1
78 months ago
MEAT preview

MEAT

GitHubjfarley248/meat

This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
data-recoverydigital-forensicsforensics+2
1696 years ago
ATMMalScan preview

ATMMalScan

GitHubfboldewin/atmmalscan

Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
digital-forensicsdisk-forensicsincident-response+2
575 years ago
AIL-framework preview

AIL-framework

GitHubcircl/ail-framework

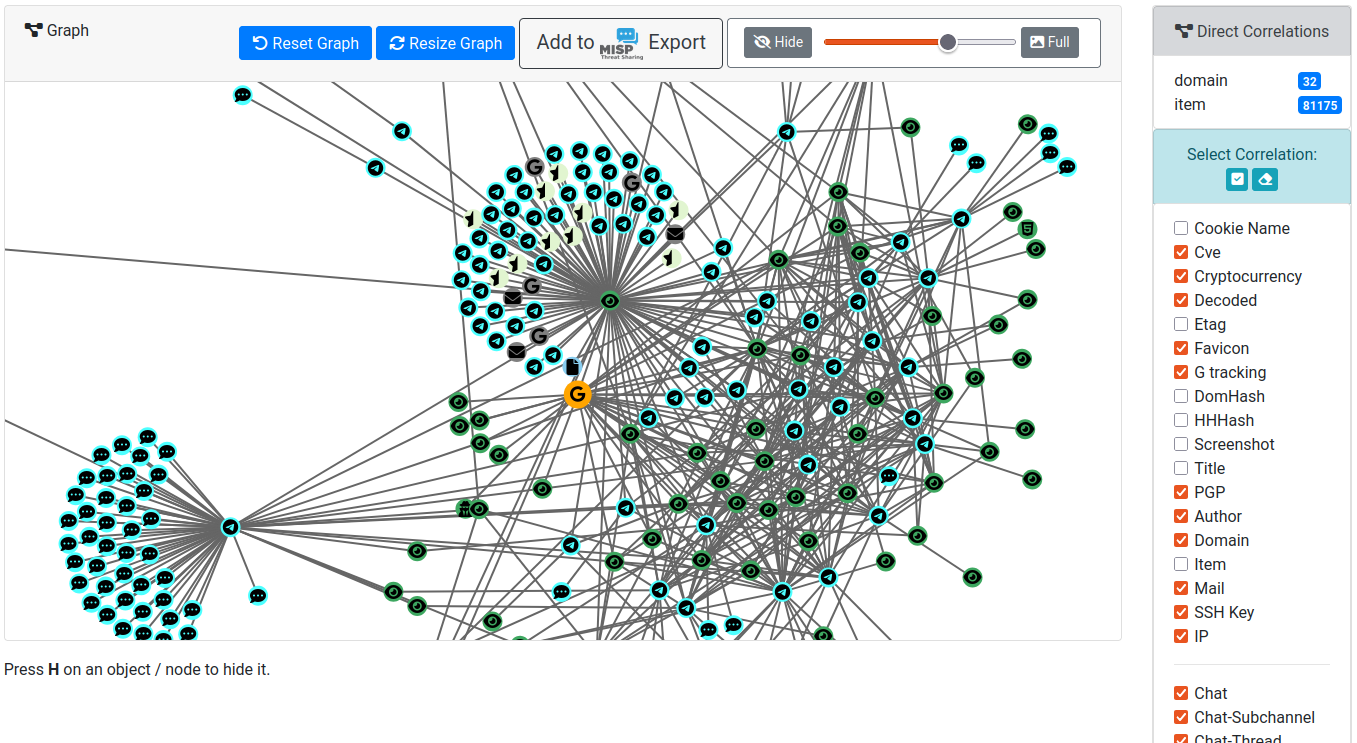
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
crawlerdata-exfiltrationdigital-forensics+8
1.4k29 days ago
copyfail-dfir preview

copyfail-dfir

GitHubledlight33/copyfail-dfir

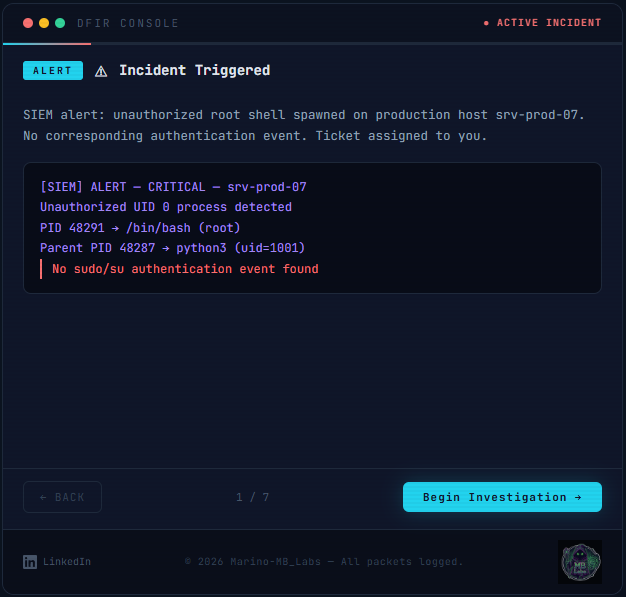
Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.
digital-forensicseducationincident-response+2
14 months ago
iDescriptor preview

iDescriptor

GitHubidescriptor/idescriptor

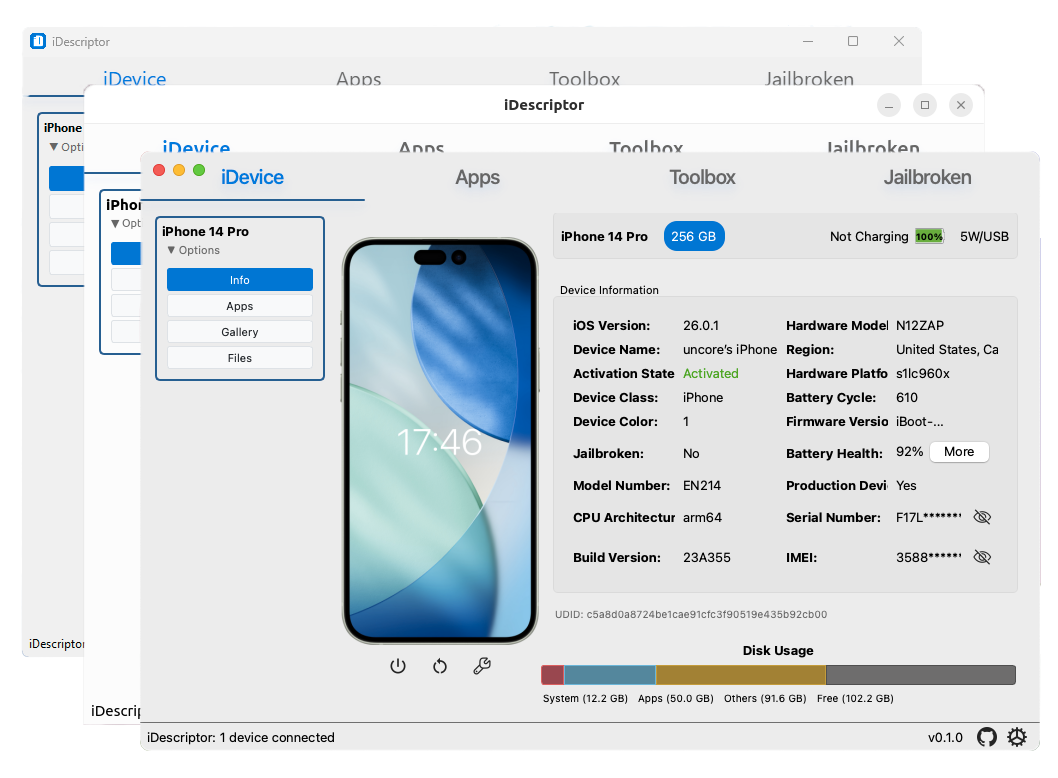
privacy-first, open-source and free idevice management tool written in Rust and Qt

digital-forensicsforensicsinformation-gathering+6
4.5k5 days ago
Previous1…567…19Next