
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
338 results
the-art-of-pivoting preview

the-art-of-pivoting

GitHubadulau/the-art-of-pivoting

The Art of Pivoting - Techniques for Intelligence Analysts to Discover New Relationships in a Complex World
curated-resourcesdigital-forensicseducation+8
190
4 months ago
cve-2025-24985 preview

cve-2025-24985

GitHubairbus-cert/cve-2025-24985

Detection of malicious VHD files for CVE-2025-24985
binary-analysisdigital-forensicsexploitation+3
21 year ago
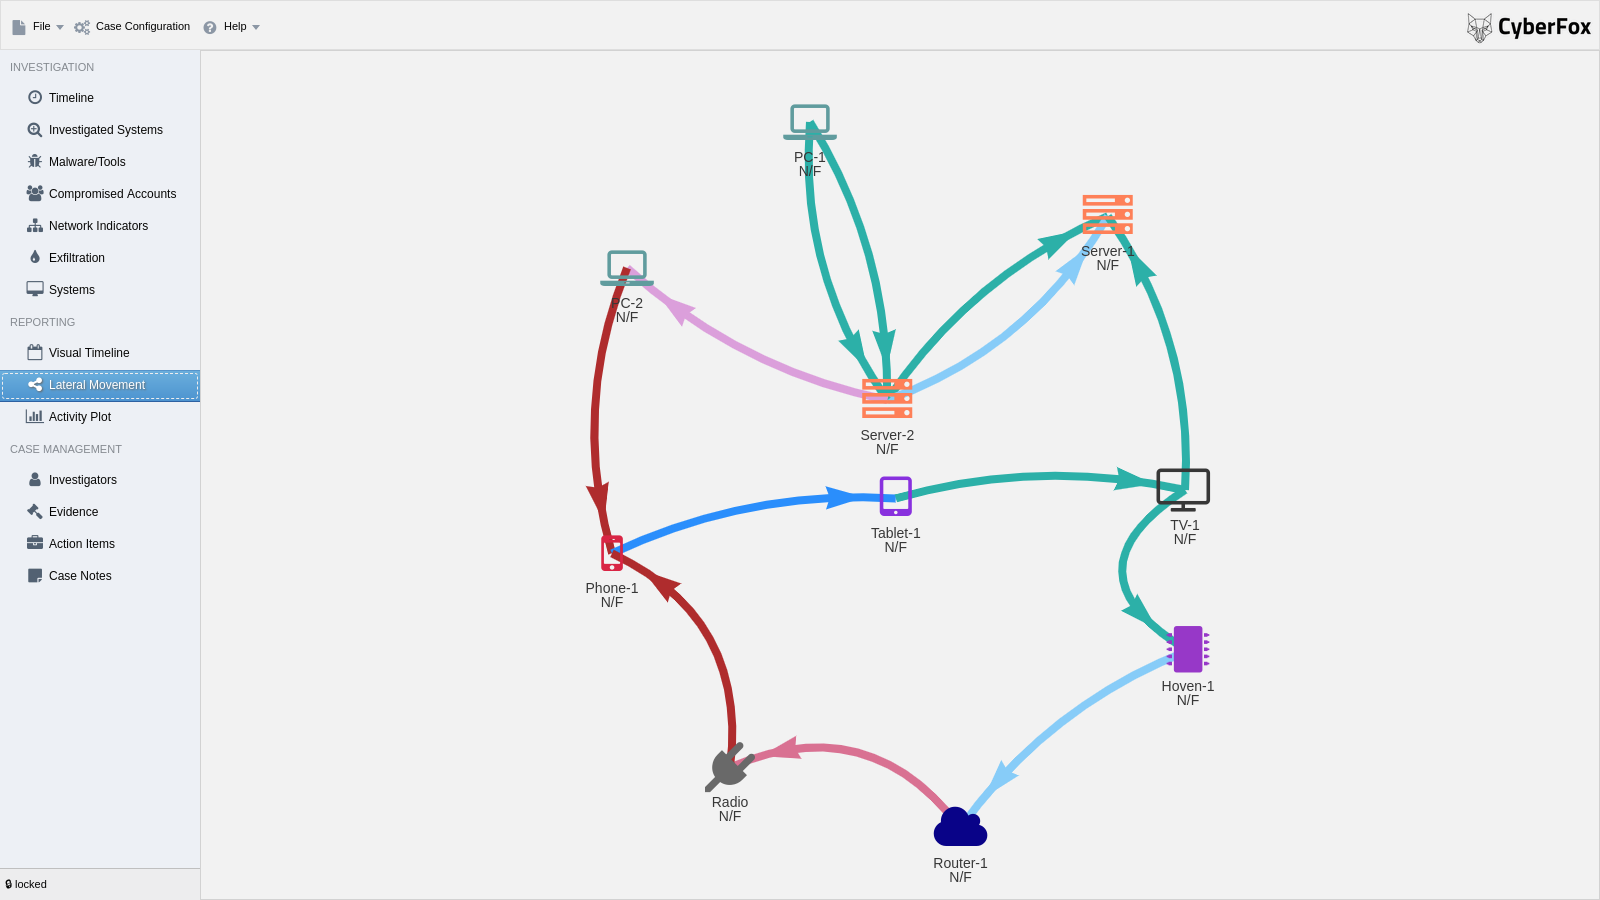
Aurora-Incident-Response preview

Aurora-Incident-Response

GitHubcyb3rfox/aurora-incident-response

Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
digital-forensicsforensicsincident-response+3
1.1k3 years ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
4121 days ago
BareMetal-RAM-Dumper preview

BareMetal-RAM-Dumper

GitHubpiat0n/baremetal-ram-dumper

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
data-recoverydigital-forensicsexploitation+3
1042 months ago
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
1793 days ago
memdumper preview

memdumper

GitHubcenobyte-vincit/memdumper

Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
digital-forensicsids-ips-evasioninformation-gathering+4
128 days ago
CVE-2020-1472-visualizer preview

CVE-2020-1472-visualizer

GitHubmingchen-script/cve-2020-1472-visualizer

PowerShell script to scan Windows Event Logs for CVE-2020-1472 indicators (events 5827-5831), export to CSV, and generate Excel pivot tables for…
digital-forensicsforensicsincident-response+2
15 years ago
dumpzilla preview

dumpzilla

GitHubbusindre/dumpzilla

Extract all forensic interesting information of Firefox, Iceweasel and Seamonkey browsers
digital-forensicsforensicsinformation-gathering+1
1489 months ago
ThreatActors-TTPs preview

ThreatActors-TTPs

GitHubcrocodyli/threatactors-ttps

Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
curated-resourcesdigital-forensicseducation+5
4157 months ago
ThreatActors-TTPs preview

ThreatActors-TTPs

GitHubessexrich/threatactors-ttps

Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
curated-resourcesdigital-forensicseducation+6
481 month ago
ma2tl preview

ma2tl

GitHubmnrkbys/ma2tl

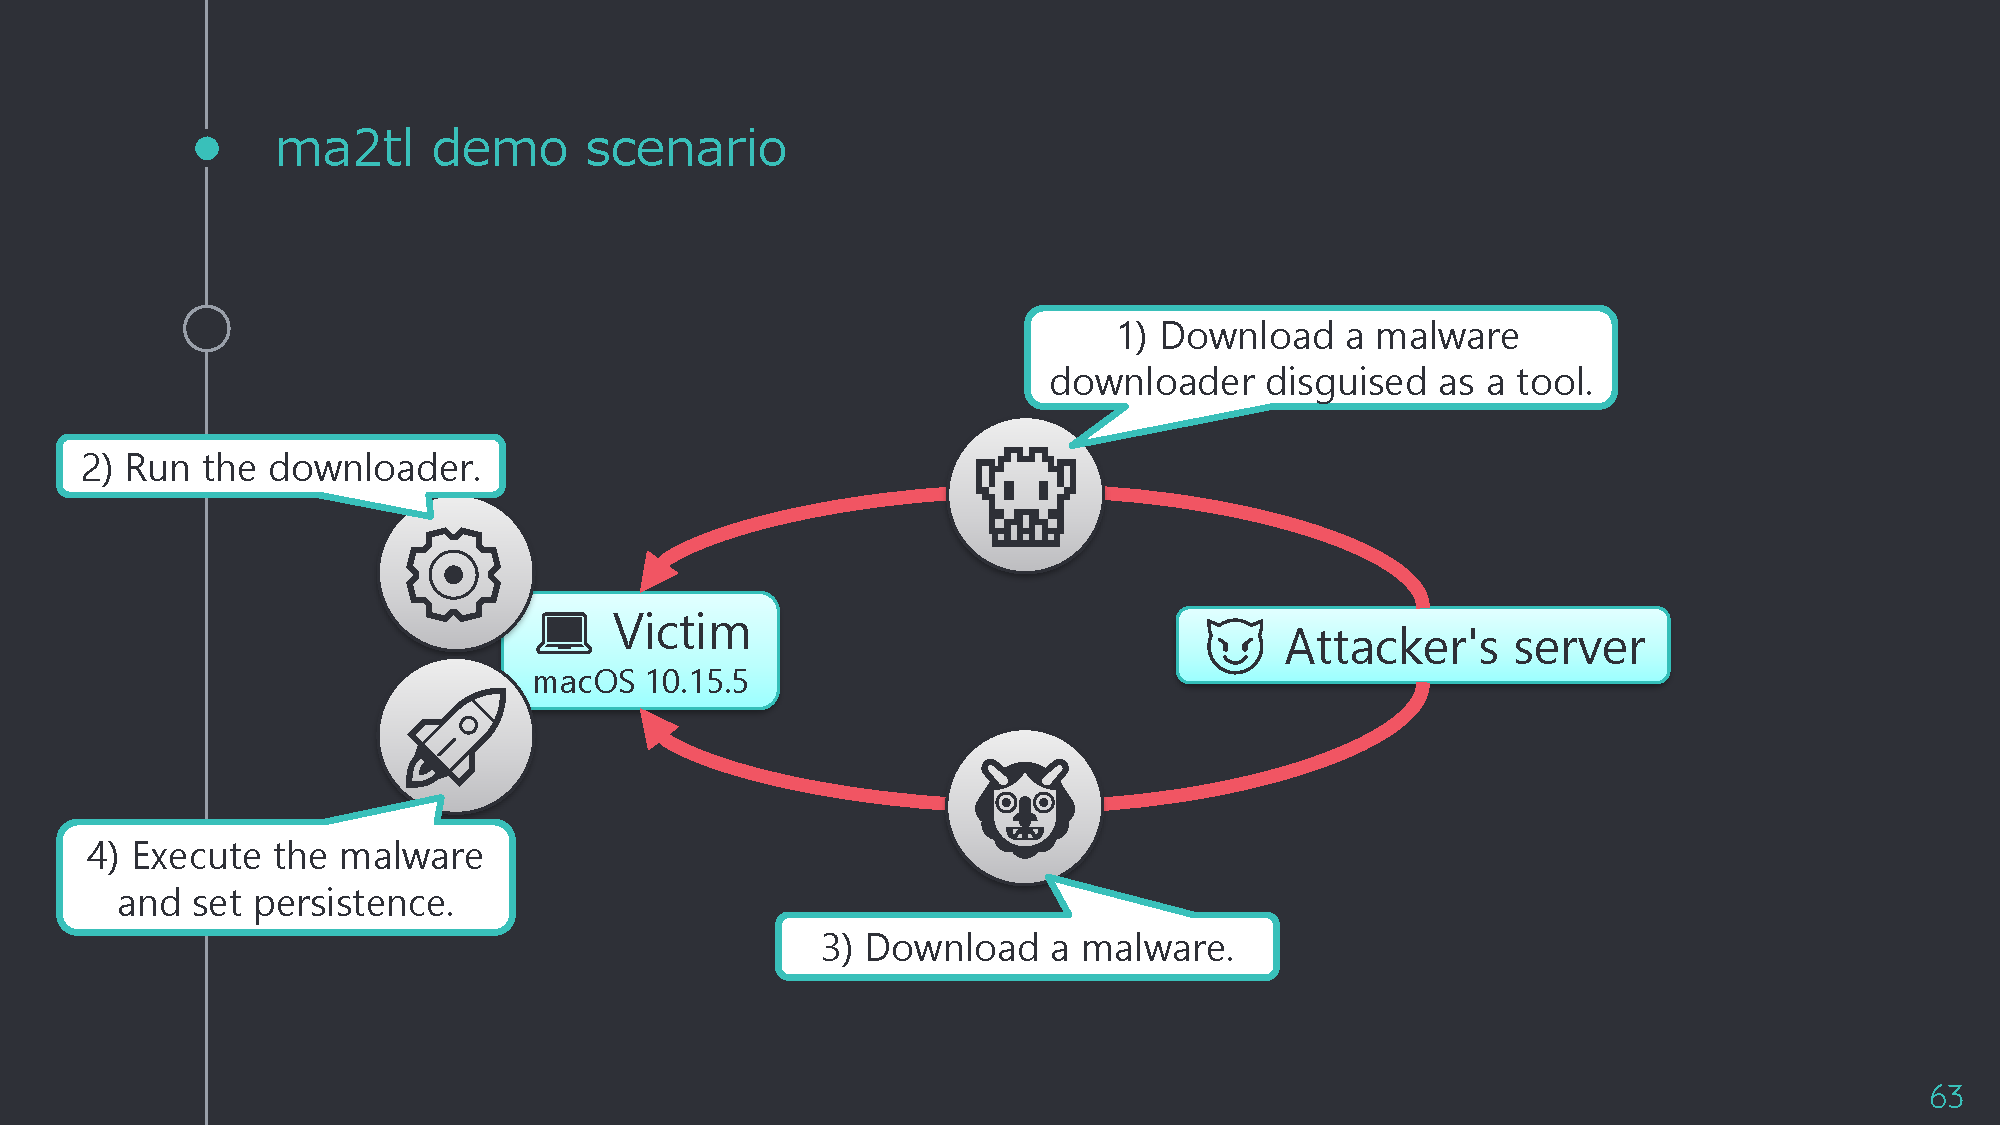
macOS forensic timeline generator using the analysis result DBs of mac_apt

digital-forensicsforensics
953 years ago
An-Integrated-Wireless-Network-Forensic-Analysis-Framework preview

An-Integrated-Wireless-Network-Forensic-Analysis-Framework

GitHubbenadia/an-integrated-wireless-network-forensic-analysis-framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
digital-forensicsforensicsnetwork-forensics+2
68 years ago
LetsDefend-SOC173-Follina-0-Day-Detected preview

LetsDefend-SOC173-Follina-0-Day-Detected

GitHubarkha-corvus/letsdefend-soc173-follina-0-day-detected

We are presented with a security alert indicating the detection of the Follina (CVE-2022-30190) vulnerability. A malicious Word document triggered…
digital-forensicseducationincident-response+5
11 months ago
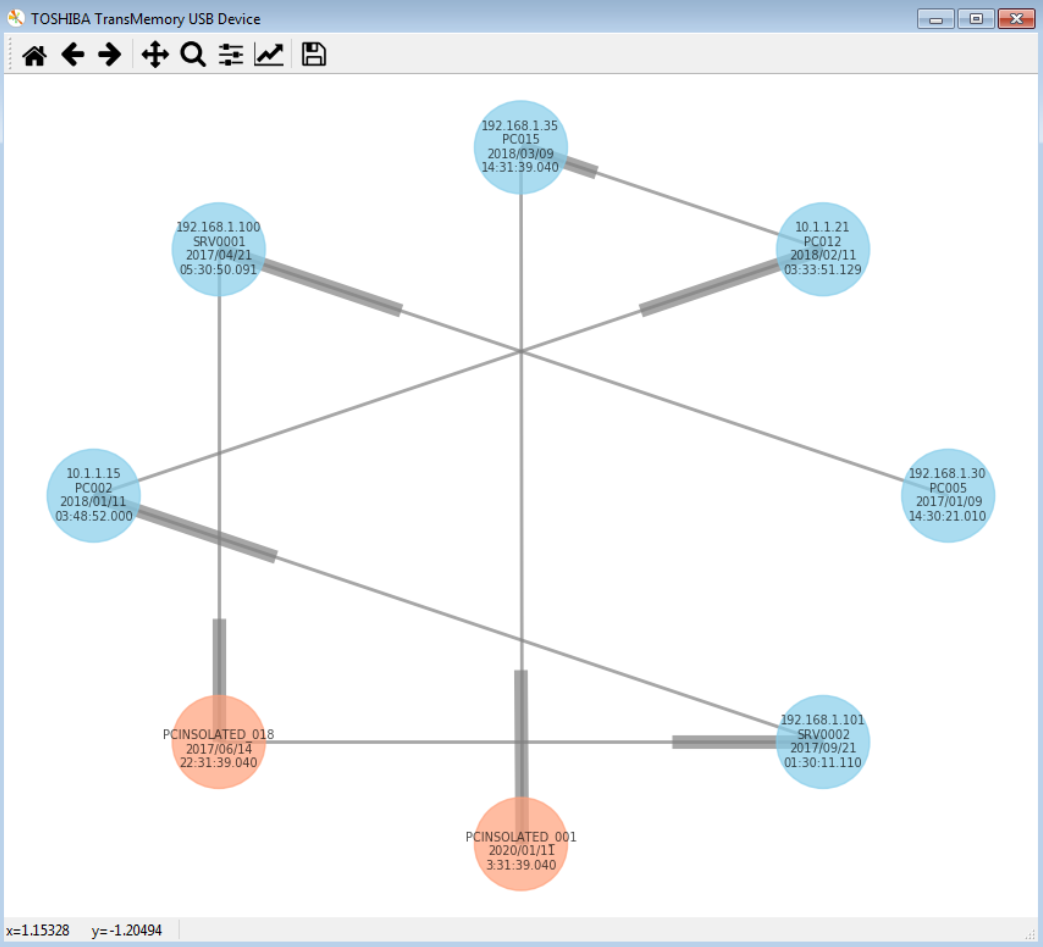
HiddenNetworks-Python preview

HiddenNetworks-Python

GitHubtelefonica/hiddennetworks-python

USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
digital-forensicsforensicsinformation-gathering+2
386 years ago
iPhoneRestrictionsPasscodeBF preview

iPhoneRestrictionsPasscodeBF

GitHubelevenpaths/iphonerestrictionspasscodebf

Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.

data-recoverydigital-forensicsencryption-decryption-tools+4
159 years ago
DesckVB-RAT preview

DesckVB-RAT

GitHubshadowopcode/desckvb-rat

Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
command-and-controldigital-forensicseducation+8
97 months ago
acropalypse-reconstructor preview

acropalypse-reconstructor

GitHubiqbaalilmii/acropalypse-reconstructor

A lightweight CLI tool to detect and reconstruct cropped images vulnerable to Acropalypse (CVE-2023-21036 and CVE-2023-28303) written in Python.

data-recoverydigital-forensicsexploitation+2
3 months ago
Previous1…345…19Next