

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
708 results
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
15.6k5h 29m ago
digital-forensics-lab preview

digital-forensics-lab

GitHubfrankwxu/digital-forensics-lab

Free hands-on digital forensics labs for students and faculty
ai-securityctfdigital-forensics+9
2.9k1 day ago
RecuperaBit preview

RecuperaBit

GitHublazza/recuperabit

A tool for forensic file system reconstruction.
data-recoverydigital-forensicsdisk-forensics+1
6243 months ago
lmg preview

lmg

GitHubhalpomeranz/lmg

Script for automating Linux memory capture and analysis
digital-forensicsforensicsincident-response+1
2756 years ago
awesome-linux-attack-forensics-purplelabs preview

awesome-linux-attack-forensics-purplelabs

GitHubcr0nx/awesome-linux-attack-forensics-purplelabs

This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.

container-securitycurated-resourcesdigital-forensics+8
3423 years ago
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
10.1k8h 22m ago
ALFA preview

ALFA

GitHubinvictus-ir/alfa

Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
cloud-securitydigital-forensicsforensics+3
1836 days ago
persisthunt preview

persisthunt

GitHubraj3shp/persisthunt

Linux Persistence Detection, Hunting and Artifact Collection script
container-securitydigital-forensicsforensics+6
254 days ago
analyzer preview

analyzer

GitHubqeeqbox/analyzer

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
digital-forensicsdynamic-analysis-sandboxingforensics+8
3202 years ago
Judge-Jury-and-Executable preview

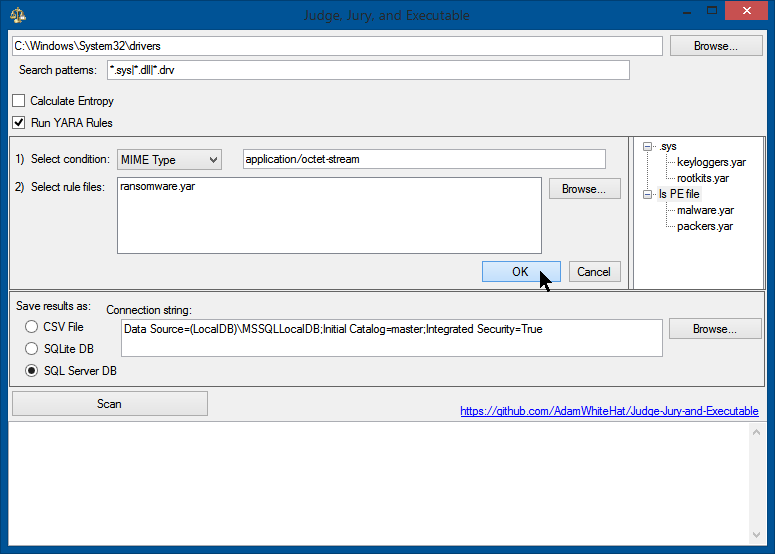
Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
database-securitydigital-forensicsdisk-forensics+8
857 months ago
fim-ebpf preview

fim-ebpf

GitHubharshavmb/fim-ebpf

A lightweight eBPF program to monitor file creation and modification events on Linux. This tool leverages eBPF (Extended Berkeley Packet Filter) to…
defensive-toolsdigital-forensicsforensics+1
710 months ago
CVE-NetScalerFileSystemCheck preview

CVE-NetScalerFileSystemCheck

GitHubdanielwep/cve-netscalerfilesystemcheck

This script checks the Citrix Netscaler if it has been compromised by CVE-2019-19781 attacks and collects all file system information
digital-forensicsforensicsincident-response+3
26 years ago
cve-2026-31431 preview

cve-2026-31431

GitHubvasyapokemon/cve-2026-31431

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…

curated-resourcesdigital-forensicseducation+8
6 months ago
claude-code-backdoor-check preview

claude-code-backdoor-check

GitHubhappyhackingspace/claude-code-backdoor-check

Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…
defensive-toolsdigital-forensicsincident-response+4
15 days ago
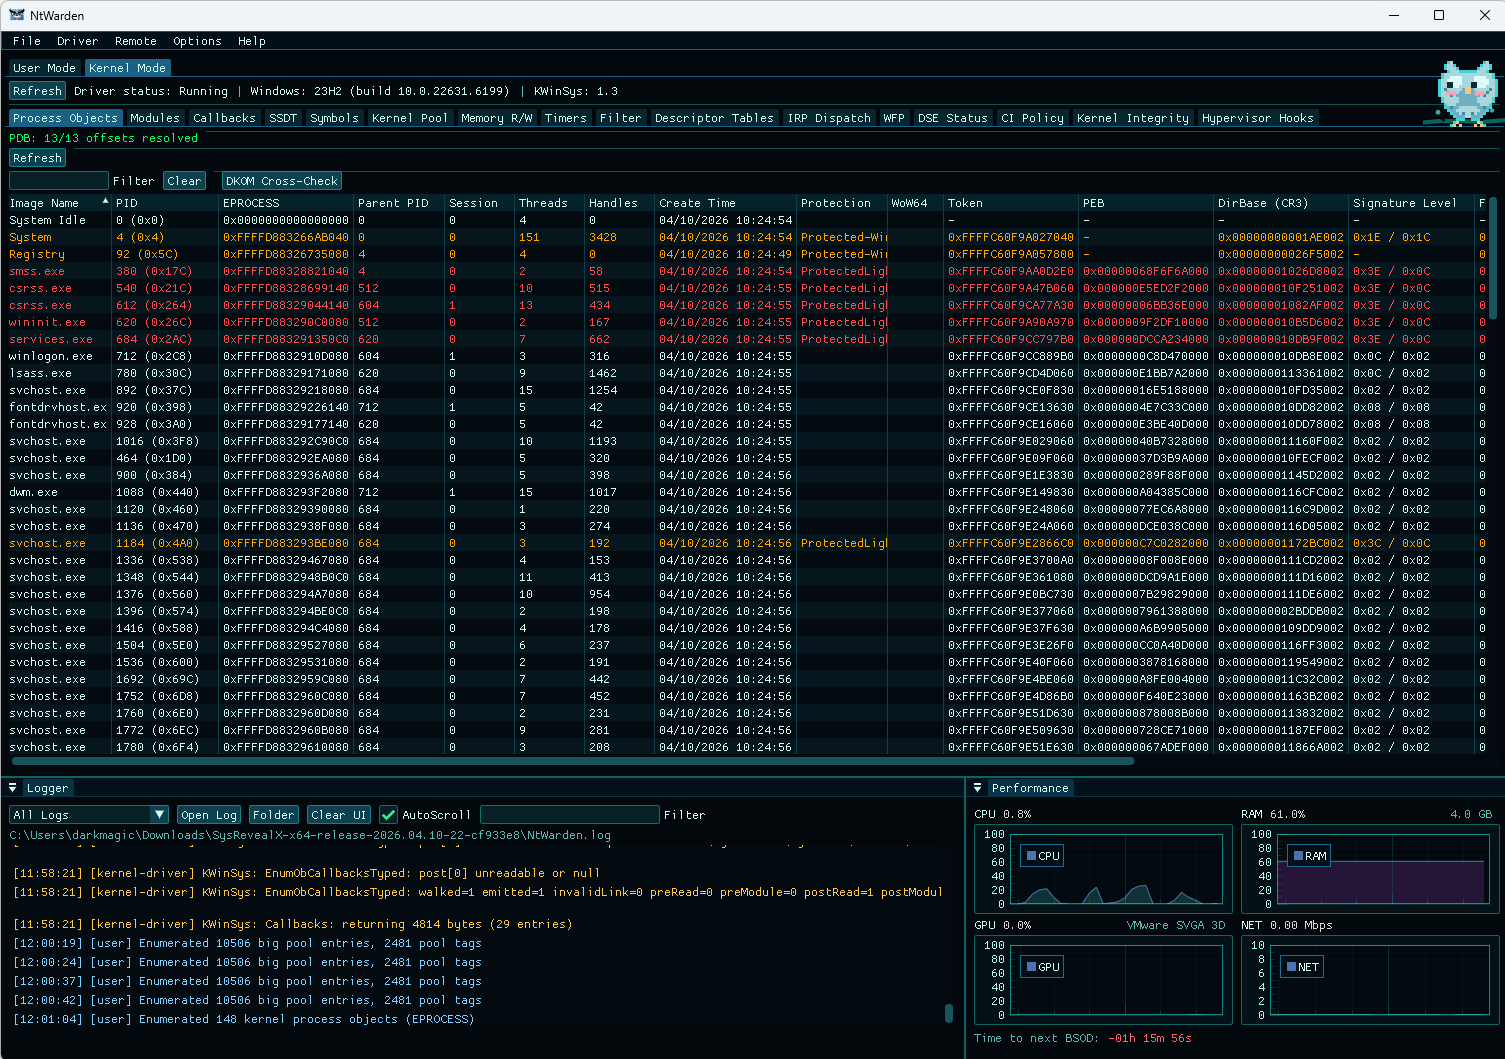
NtWarden preview

NtWarden

GitHubmrt4ntr4/ntwarden

Windows Analysis and Research Toolkit
binary-analysisdefensive-toolsdigital-forensics+4
6766 months ago
UnderlayCopy preview

UnderlayCopy

GitHubkfallahi/underlaycopy

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads

data-recoverydigital-forensicsdisk-forensics+3
2581 year ago
Hayabusa-Bulk-Runner preview

Hayabusa-Bulk-Runner

GitHubrorywag/hayabusa-bulk-runner

Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
defensive-toolsdigital-forensicsforensics+5
191 day ago
MEAT preview

MEAT

GitHubjfarley248/meat

This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices

data-recoverydigital-forensicsforensics+2
1686 years ago
Previous1…345…40Next