
BiBi-Windows-Wiper-Analysis
 knight0x07/bibi-windows-wiper-analysis
Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
binary-analysisdigital-forensicsincident-response+3
8
knight0x07/bibi-windows-wiper-analysisTechnical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
 withsecurelabs/volatility-plugins
Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
 azeemering/cve-2021-44228-dfir-notes
CVE-2021-44228 DFIR Notes
 malgamy/scripts-with-malware-analysis
 rdelasierra-uy/portfolio
Vitrina profesional: writeups de Hack The Box, informes, casos de estudio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), scripts de…
 mo200909/office-malware-forensics-lab-remnux-static-analysis
Static analysis of 2 suspicious Office documents on REMnux using oletools; one matched CVE-2017-11882, the other was inconclusive.
 ledlight33/copyfail-dfir
Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.
 jgoyd/fourteen_endpoints
Shell Companies Inside Apple's Privacy Relay
 haruu77g/phantomprint
Passive hybrid fingerprinting engine — identify hosts without sending a single packet
 gmh5225/memtools
Windows Linux DMA、Dump 、Direct、inject 内存读取、写入工具
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
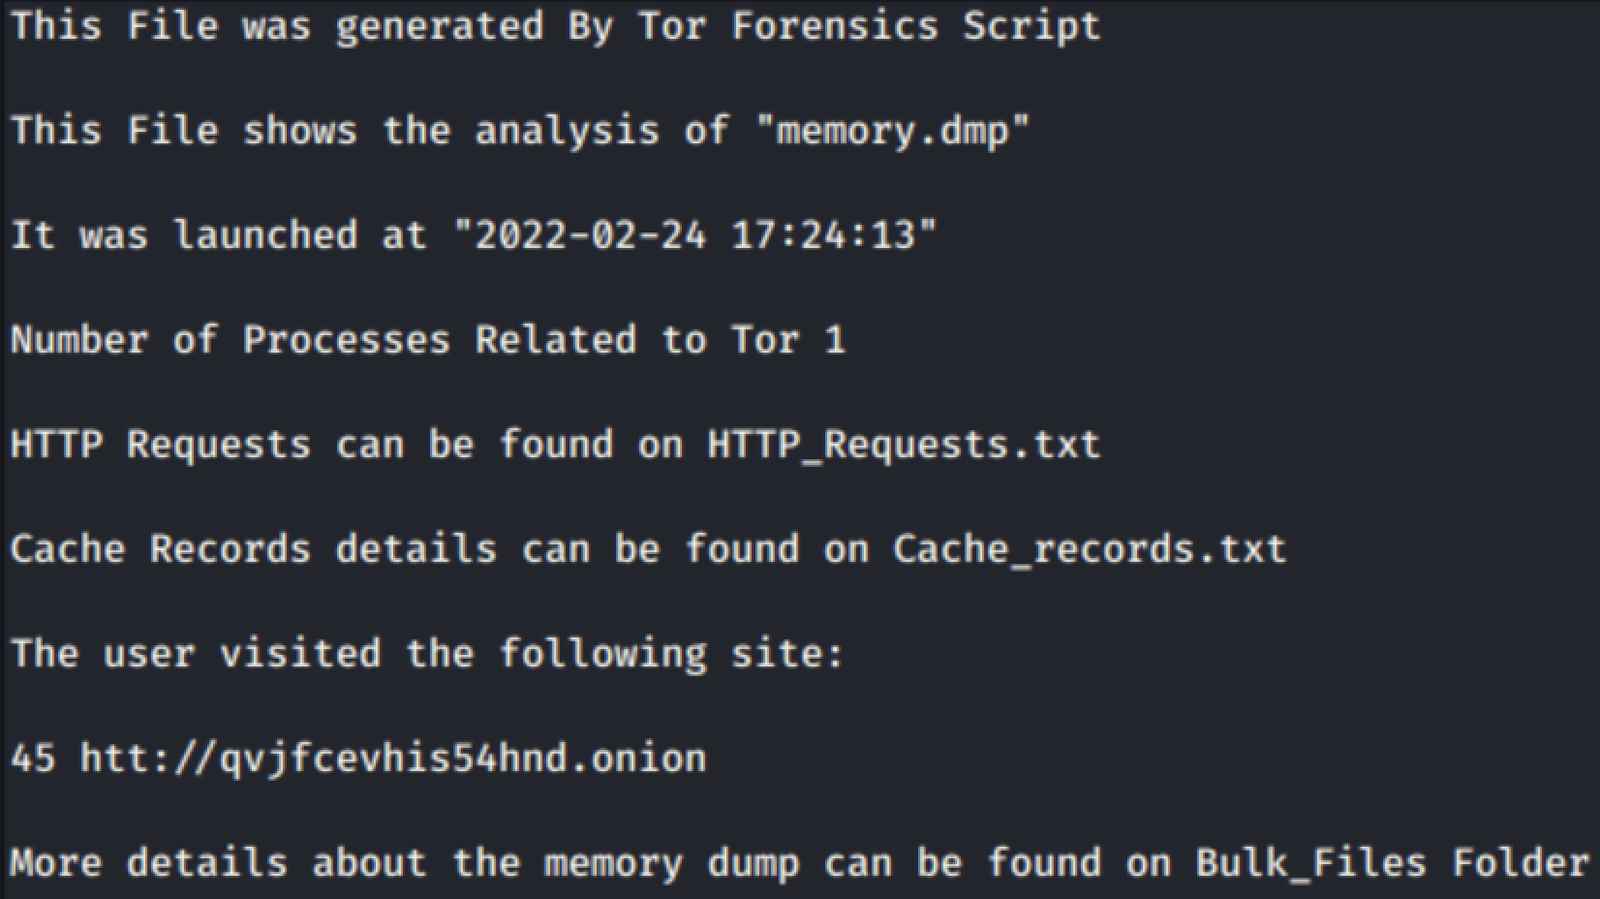 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
 b1tbreaker/cve-2025-48708
Lack of argument sanitization leading to password leakage in Ghostscript PDF versions up to 10.05.0.
 salaheldinfikri/kalim_backdoor
Kalim backdooe Malware Report
 onsec-fr/cve-2019-19781-forensic
Automated forensic script hunting for cve-2019-19781
 airbus-cert/cve-2025-24985
Detection of malicious VHD files for CVE-2025-24985
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…