

Archived
bios_memimage
 dbrant/bios_memimage
RAM imaging utility.
digital-forensicsincident-responsememory-forensics
910 years ago
dbrant/bios_memimageRAM imaging utility.
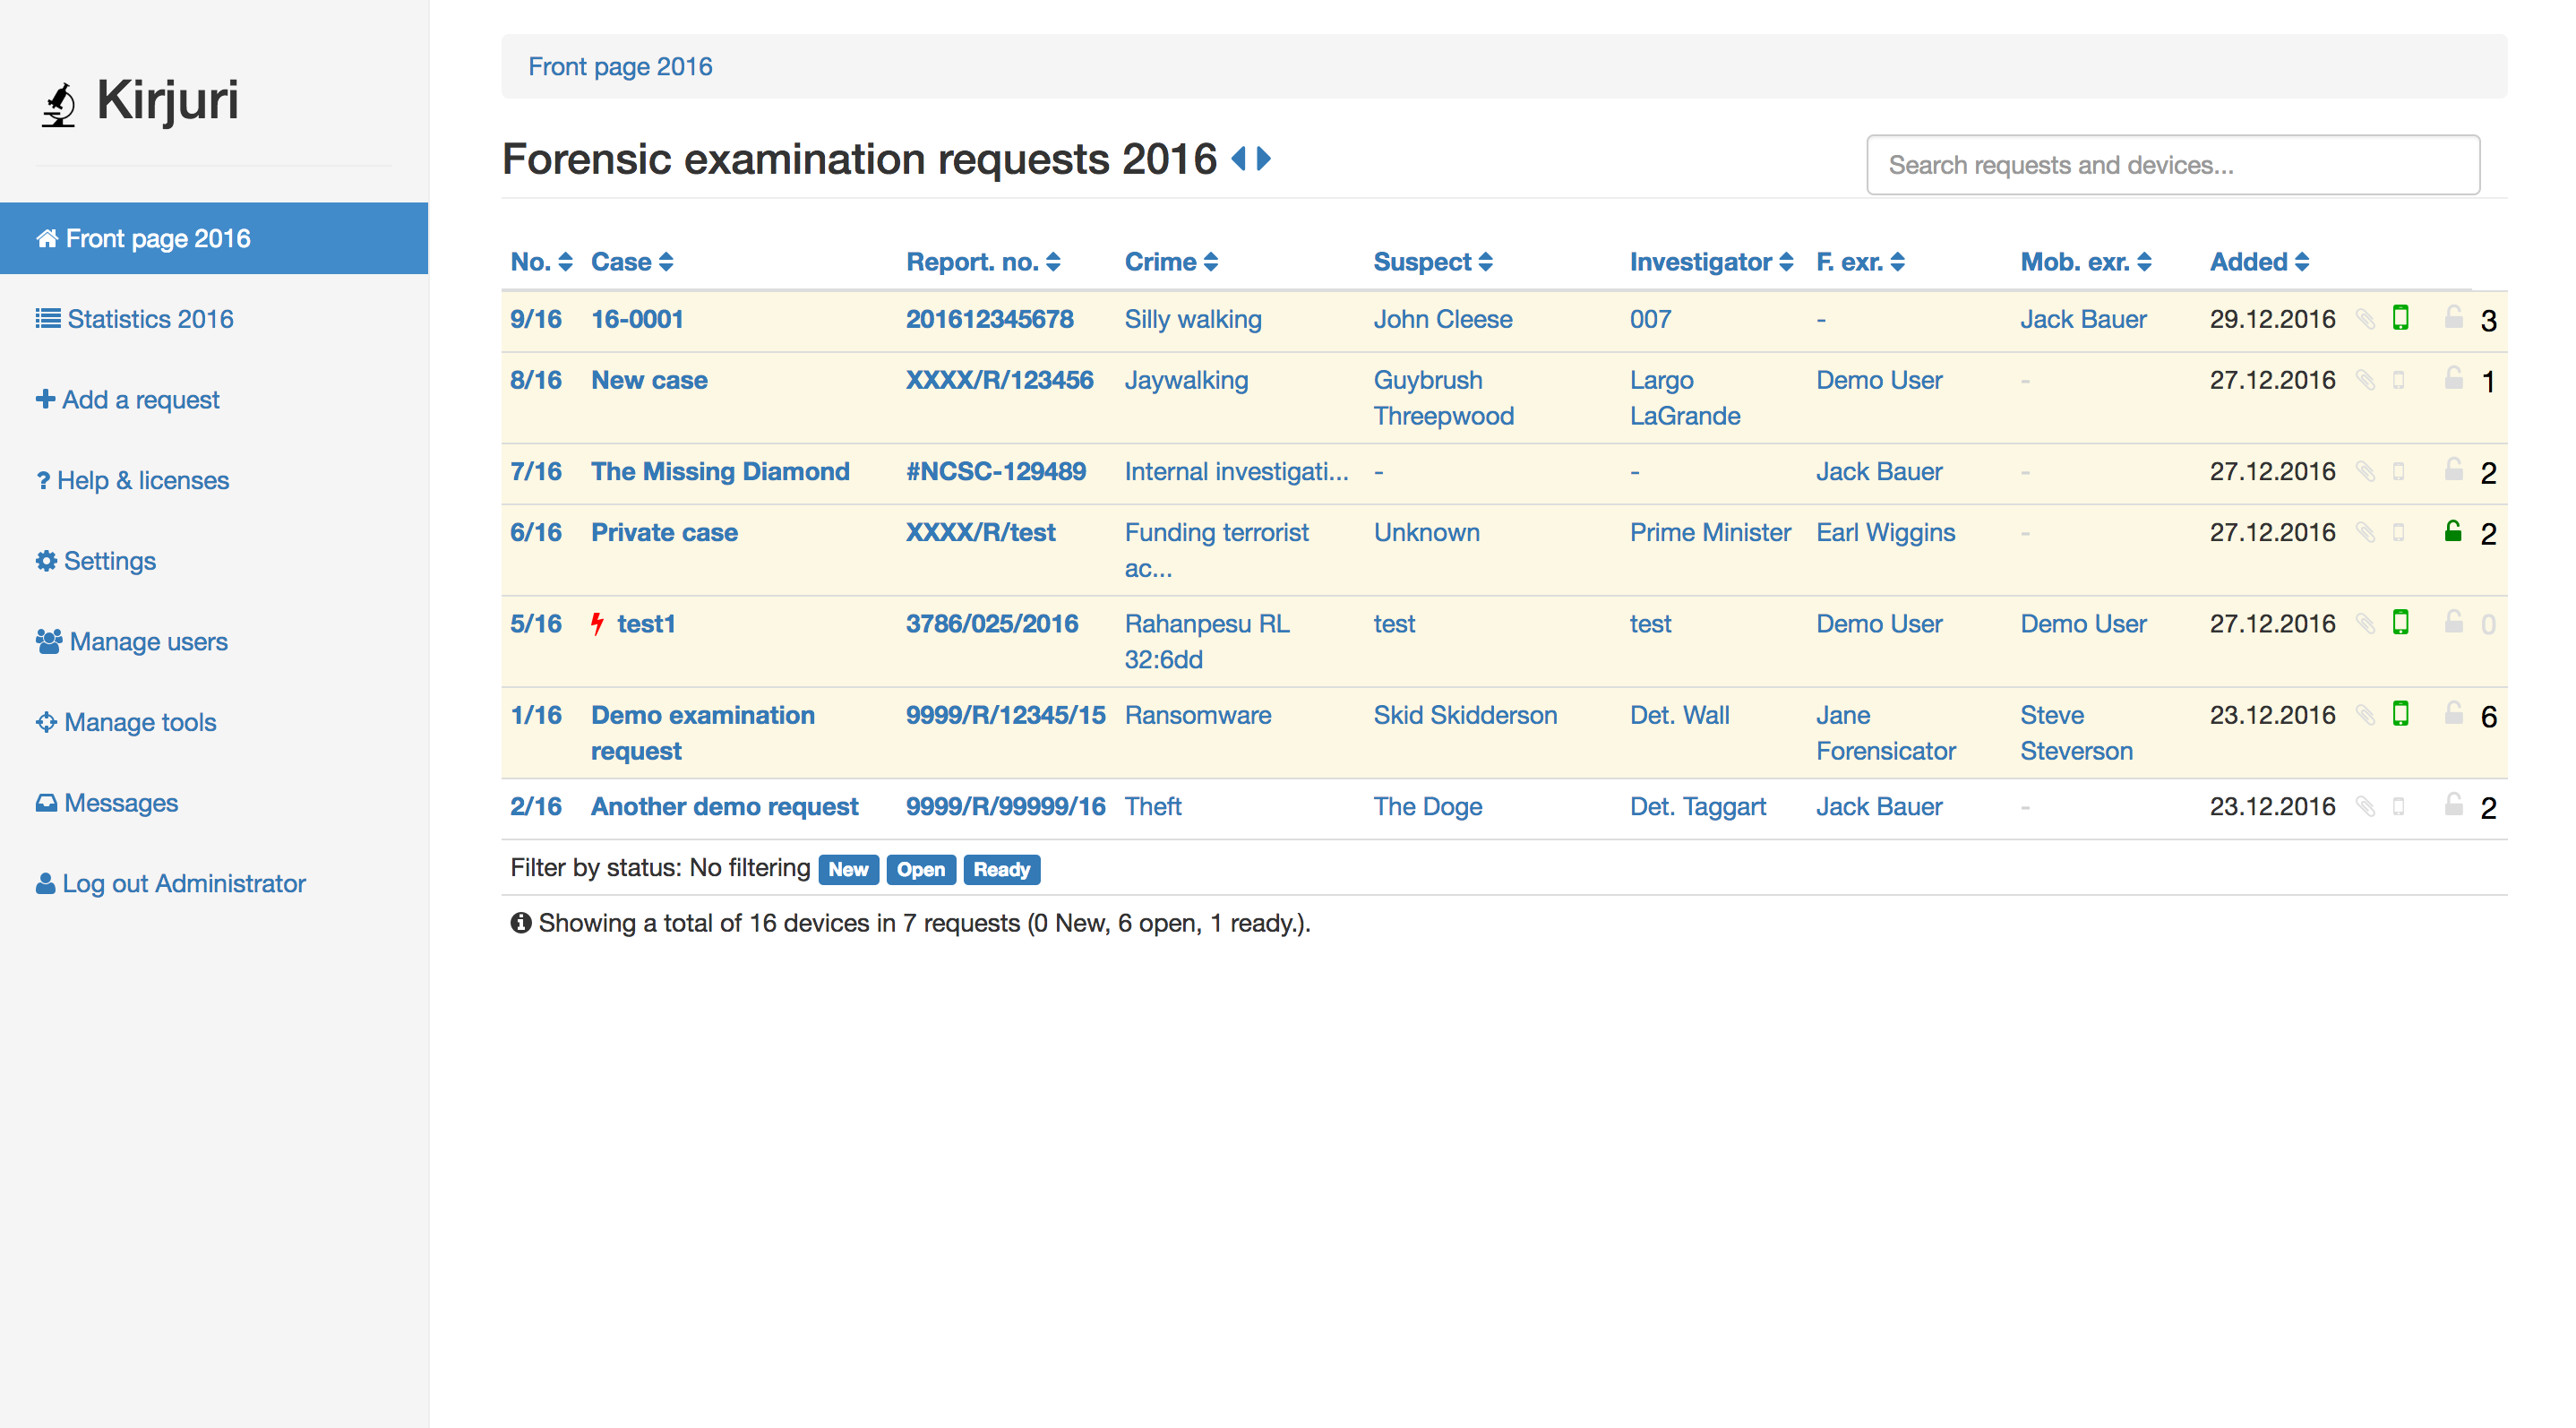 anttikurittu/kirjuri
Kirjuri is a web application for managing cases and physical forensic evidence items.
 certcc/keyfinder
A tool for finding and analyzing private (and public) key files, including support for Android APK files.
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 kowntaewook/mcptrace
Volatility 3 plugin that carves MCP/JSON-RPC message candidates from Windows and Linux memory dumps, preserving raw bytes, addresses, and SHA-256 for…
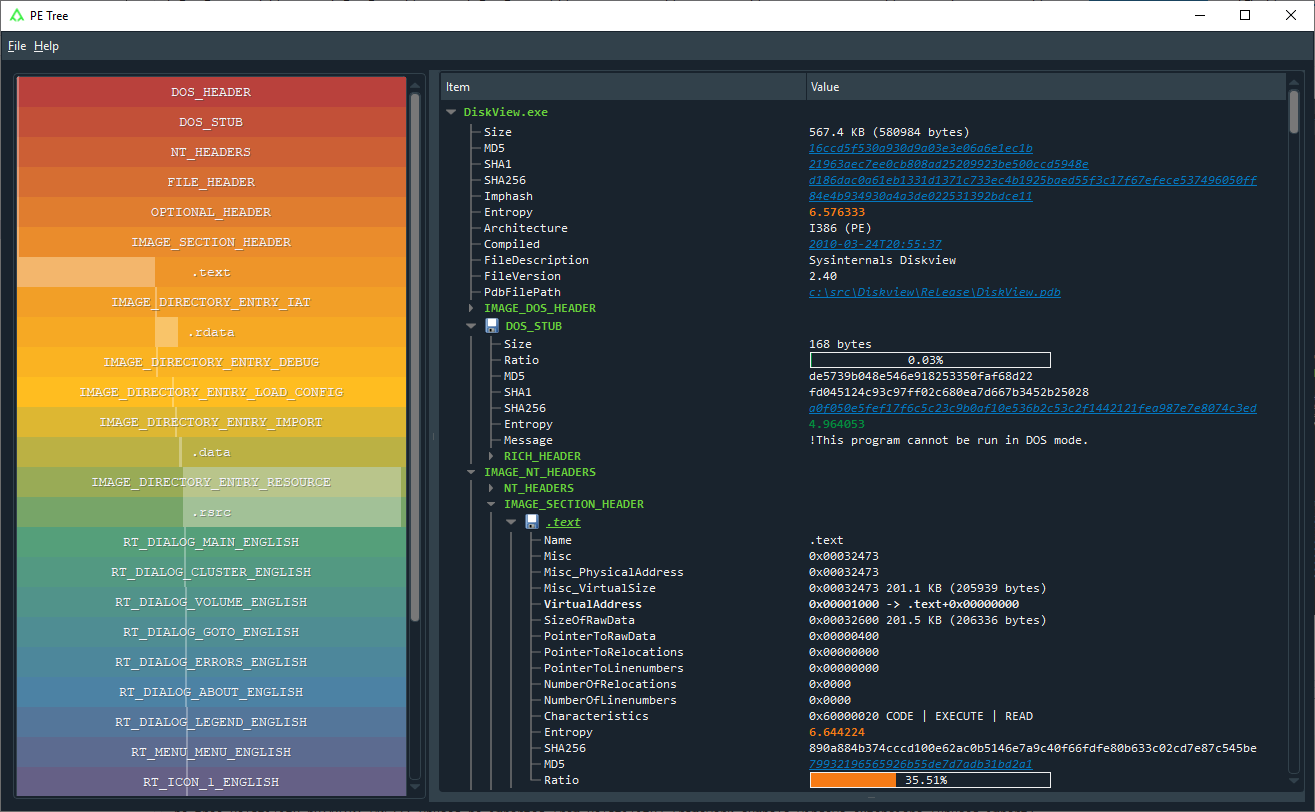 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 snovvcrash/usbrip
Tracking history of USB events on GNU/Linux
 mandiant/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 robindavid/lsb-steganography
Python program to steganography files into images using the Least Significant Bit.
 dfir-dd/dfir-toolkit
CLI tools for forensic investigation of Windows artifacts
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
 grapl-security/grapl
Graph platform for Detection and Response
 sucuri-labs/cve-2025-57819-ioc-check
This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819
 cado-security/varc
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…
 adamrpostjr/cve-2021-27065
Quick One Line Powershell scripts to detect for webshells, possible zips, and logs.
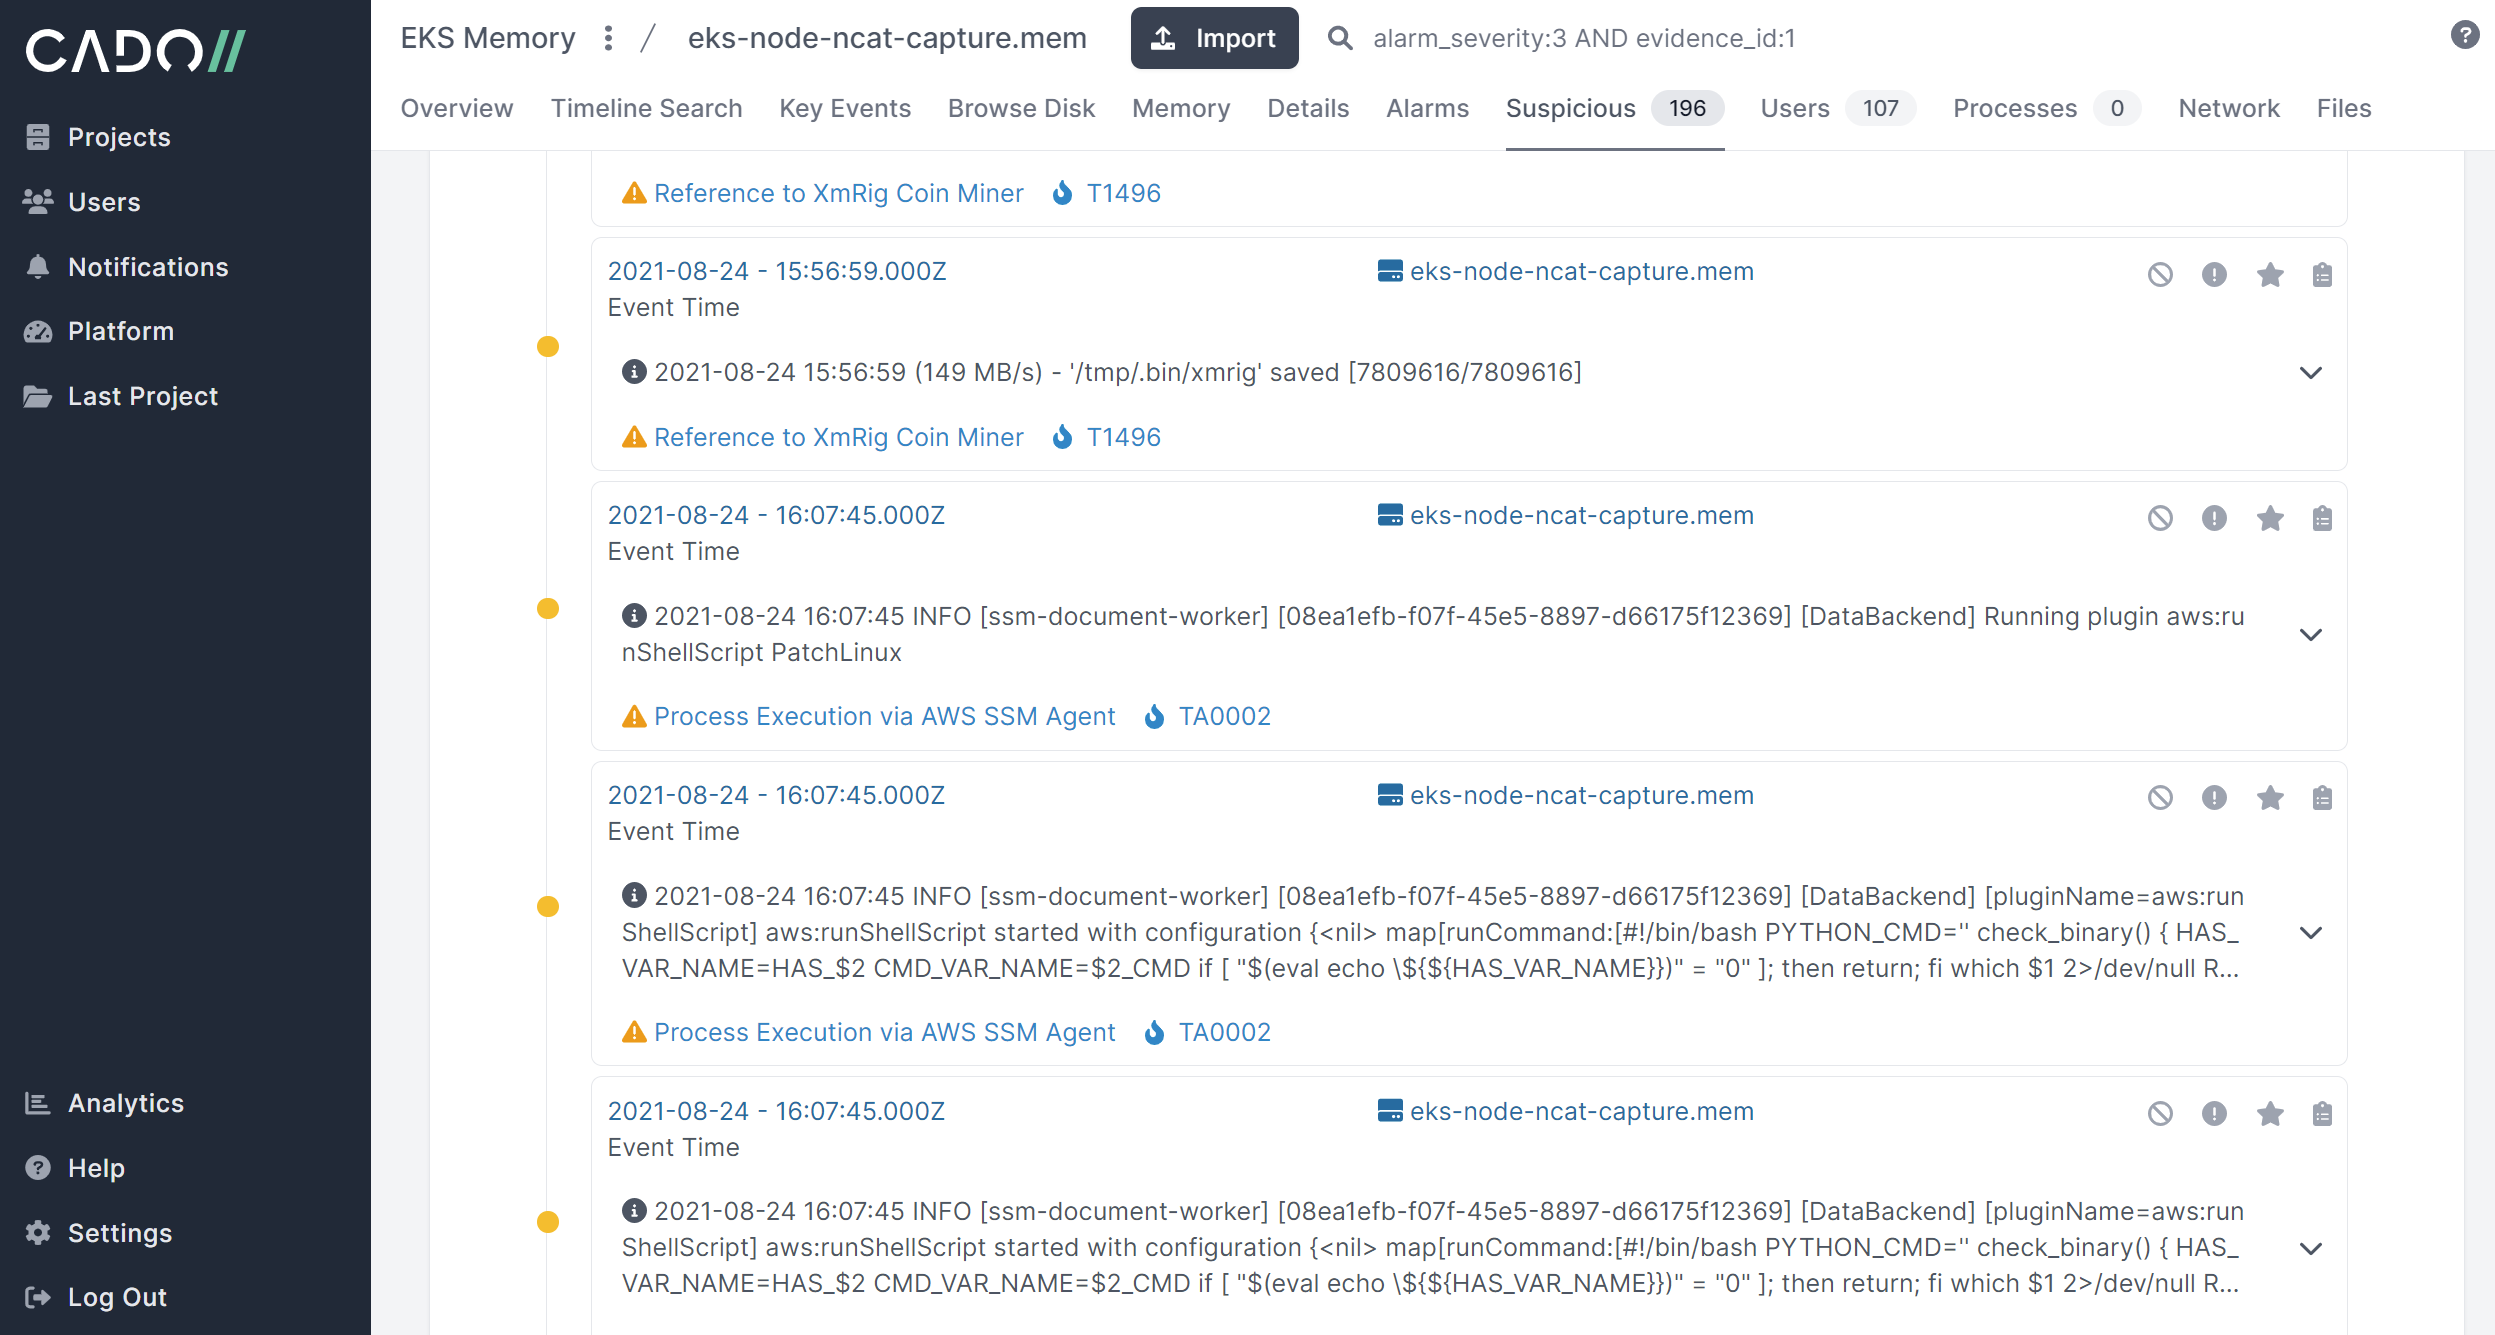 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
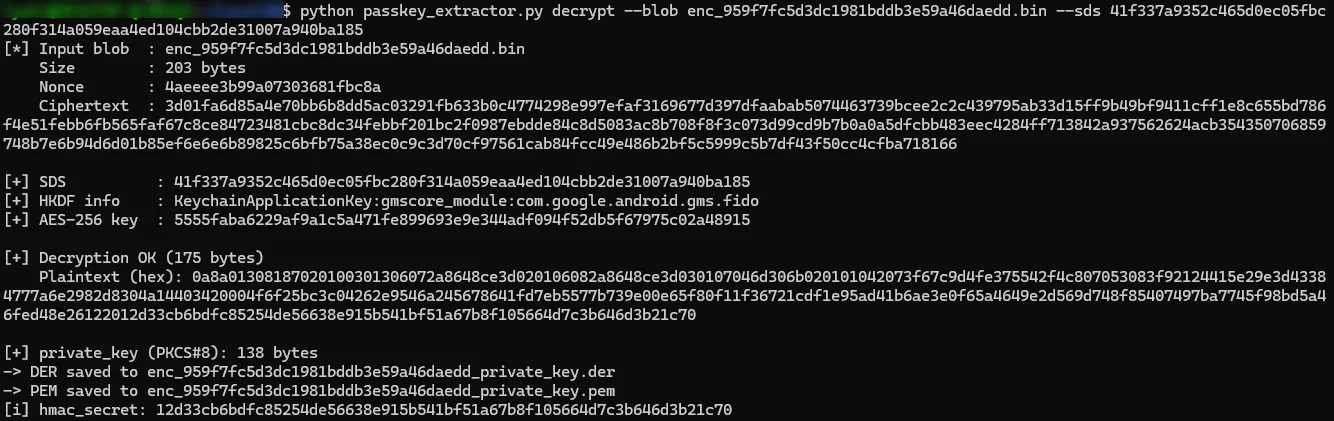 0rcruxe/pass-ta-key
PoC that extracts the Google Password Manager Security Domain Secret from Chrome process memory and decrypts synced GPM passkey ECDSA P-256 private…