
whatfiles
 spieglt/whatfiles
Log what files are accessed by any Linux process
digital-forensicsforensicsgeneral-purpose-utilities
spieglt/whatfilesLog what files are accessed by any Linux process
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 interplains/zero-breach-toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.
 kowntaewook/mcptrace
Volatility 3 plugin that carves MCP/JSON-RPC message candidates from Windows and Linux memory dumps, preserving raw bytes, addresses, and SHA-256 for…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
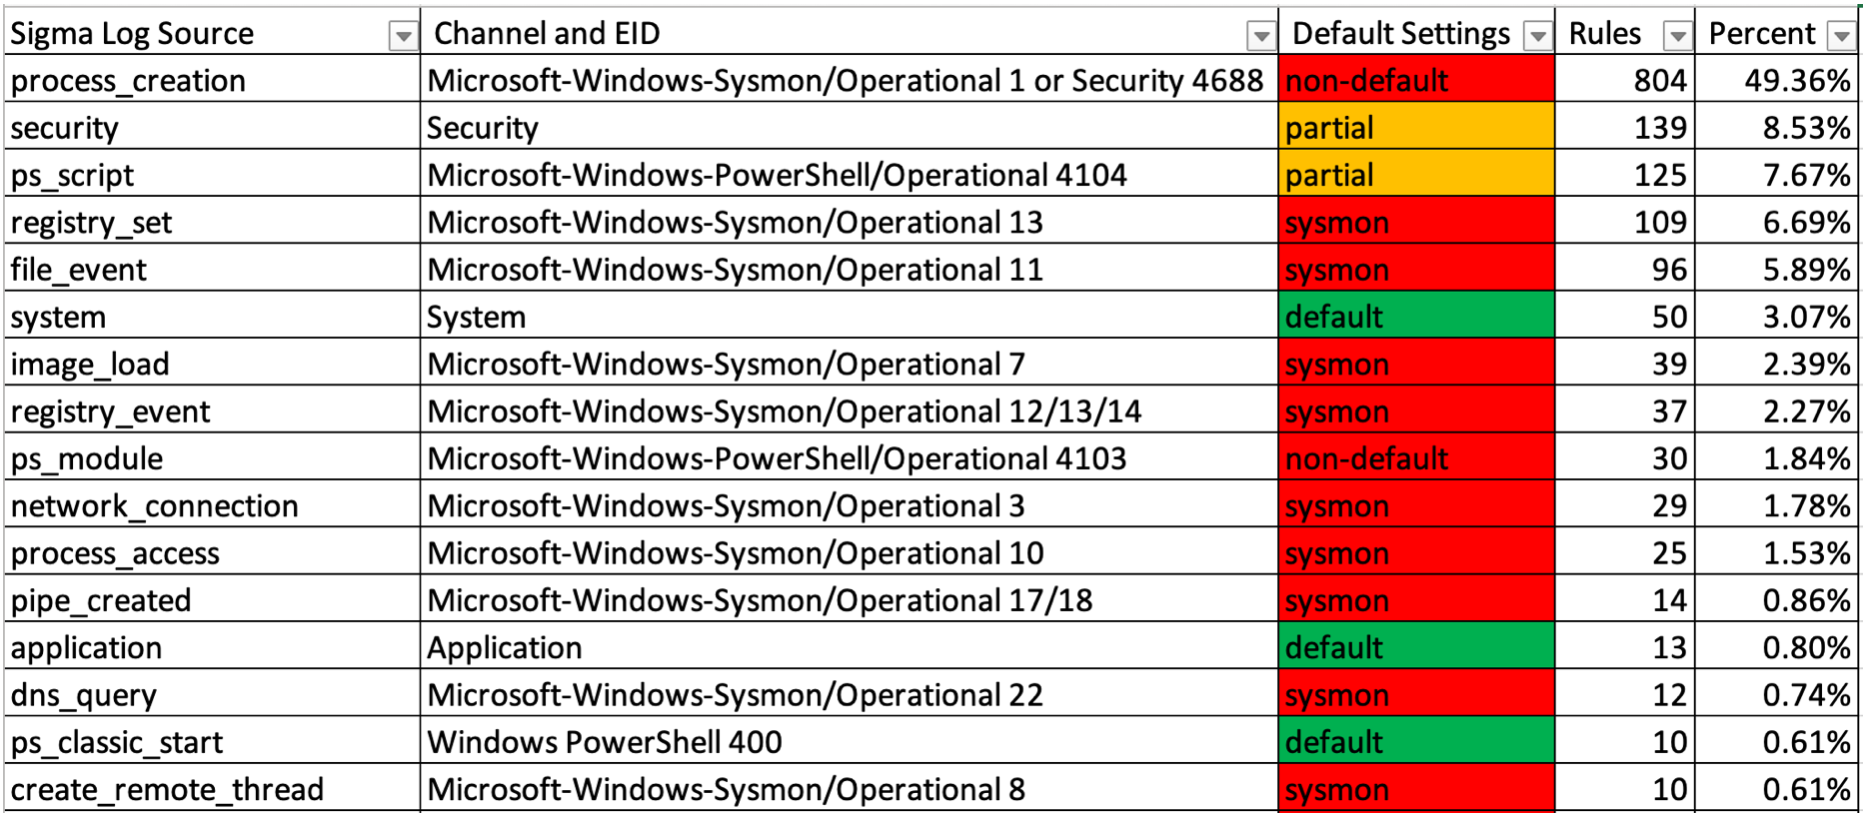 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
 korben00/no-gdid
Read, understand and silence the Windows GDID device identifier (the ID that tracked a hacker through a VPN). Verified on a real Win11 VM. Honest: it…
 yamato-security/wela
Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 twocanoes/audit
Audit Preference Pane and Log Reader for OS X